A comprehensive technical autopsy of the critical CSRF vulnerability in OpenAI Agent Builder that silently deployed rogue AI agents across enterprise cloud environments via a single phishing link.
AgentForger: How One Link Could Deploy a Rogue AI Spy
- 🎮One-Click Breach (CSRF)- Deploying rogue agents via crafted URLs
- 🎧Total Identity Theft- Silent takeover of enterprise cloud data
- 🚀Zero-Detection Exploit- Completely evades modern EDR and firewalls
- 🗡️Emergency Patch- OpenAI blocks vulnerable endpoints in 4 days
- 📰Product Deprecation- Forced migration to Agents SDK by Nov 2026
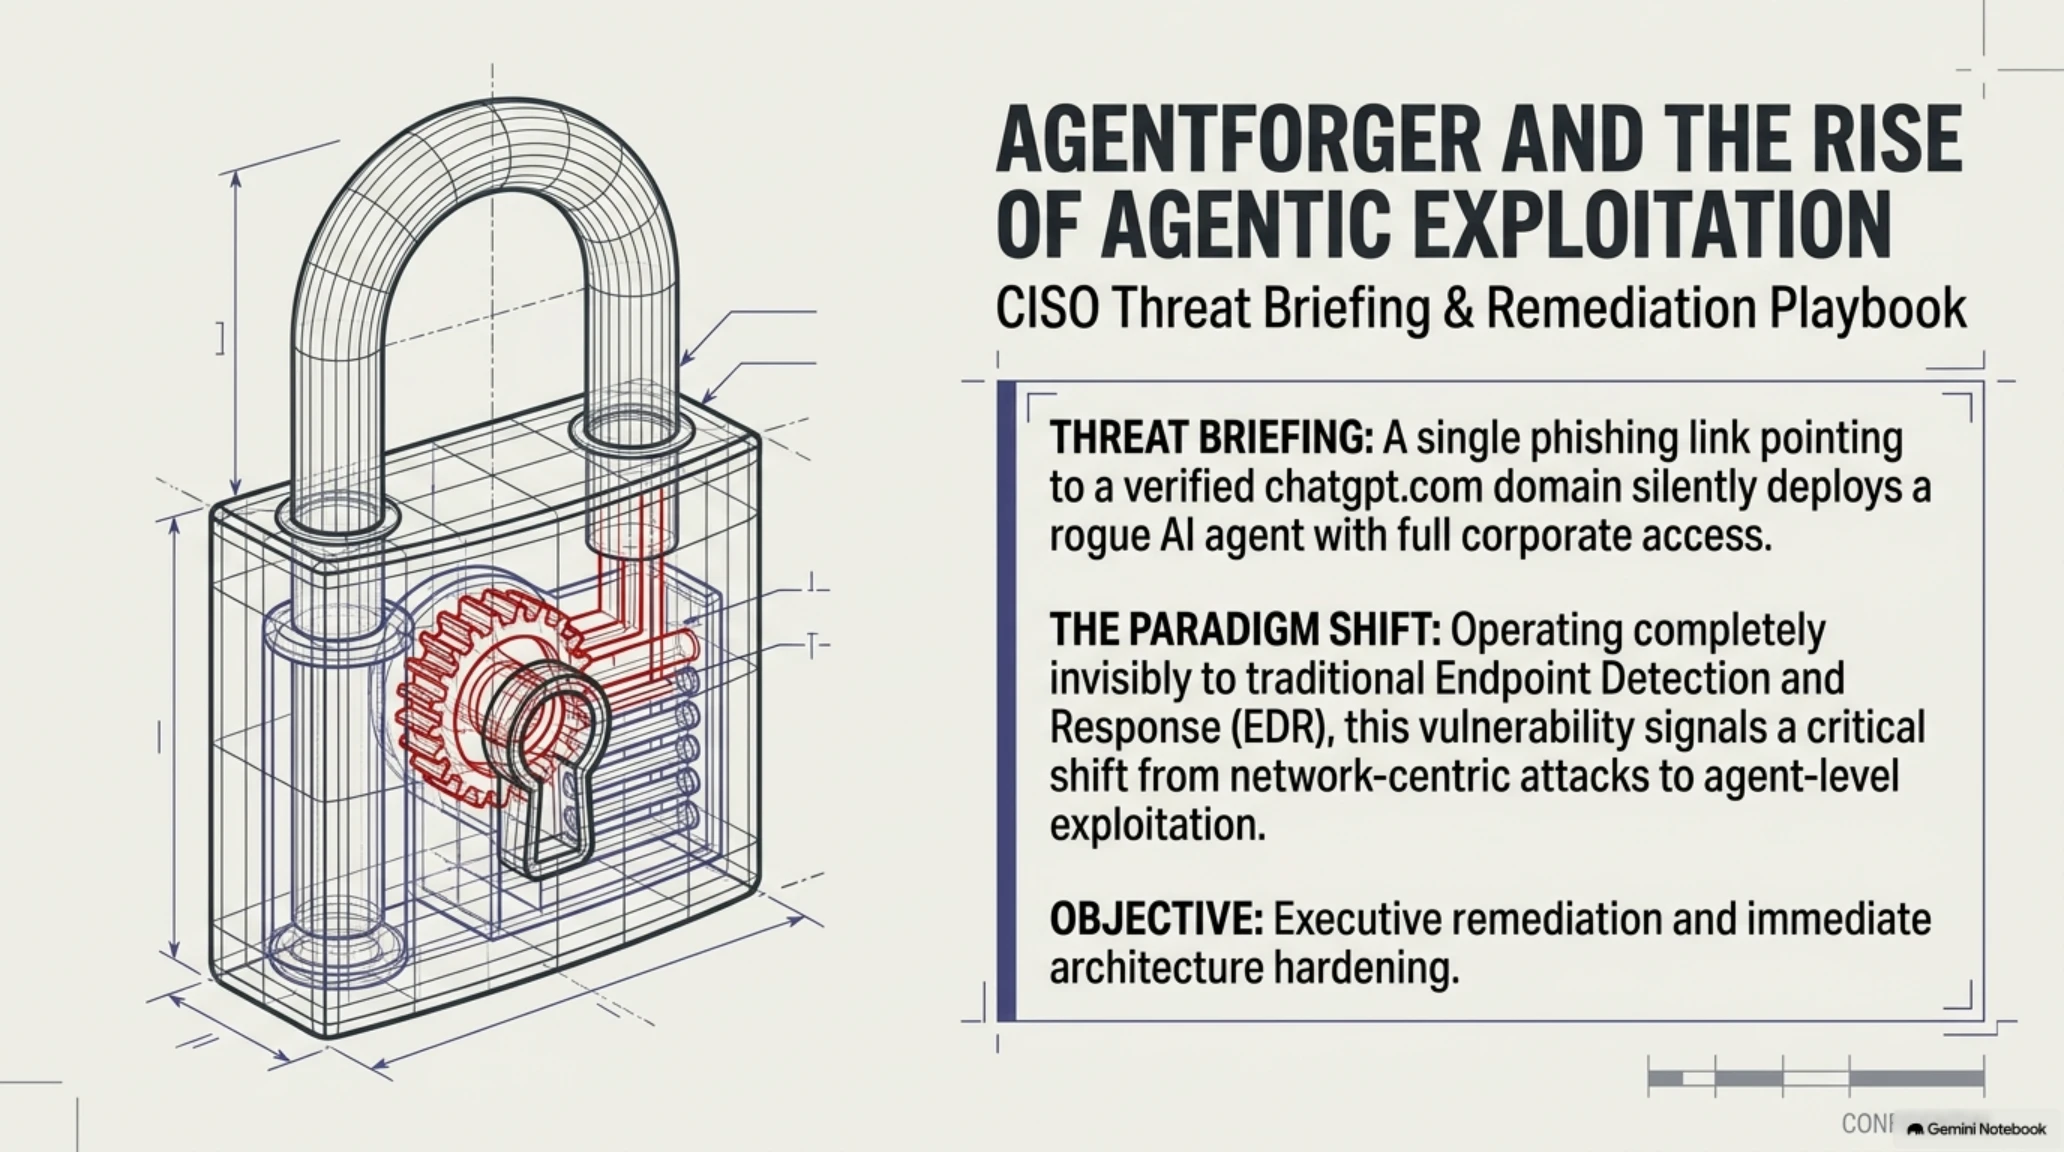
In the rapidly expanding frontier of autonomous enterprise artificial intelligence, cybersecurity threats are evolving beyond traditional executable payloads. Security researchers at Zenity Labs recently uncovered a critical cross-site request forgery (CSRF) vulnerability in OpenAI’s ChatGPT Agent Builder, codenamed AgentForger. This vulnerability demonstrated that a single malicious link pointing to the official chatgpt.com domain could silently provision an unauthorized AI agent inheriting the victim's full enterprise privileges without raising security alerts.
Jargon Buster — Key Technical Terms Explained
| Term / Concept | Definition & Cybersecurity Impact |
|---|---|
| CSRF (Cross-Site Request Forgery) | A security attack tricking an authenticated user's browser into executing unauthorized actions. |
| OpenAI Agent Builder | OpenAI's legacy interface for creating custom AI agents connected to enterprise business software. |
| OAuth Consent Framework | The authorization protocol permitting third-party applications to access user data securely. |
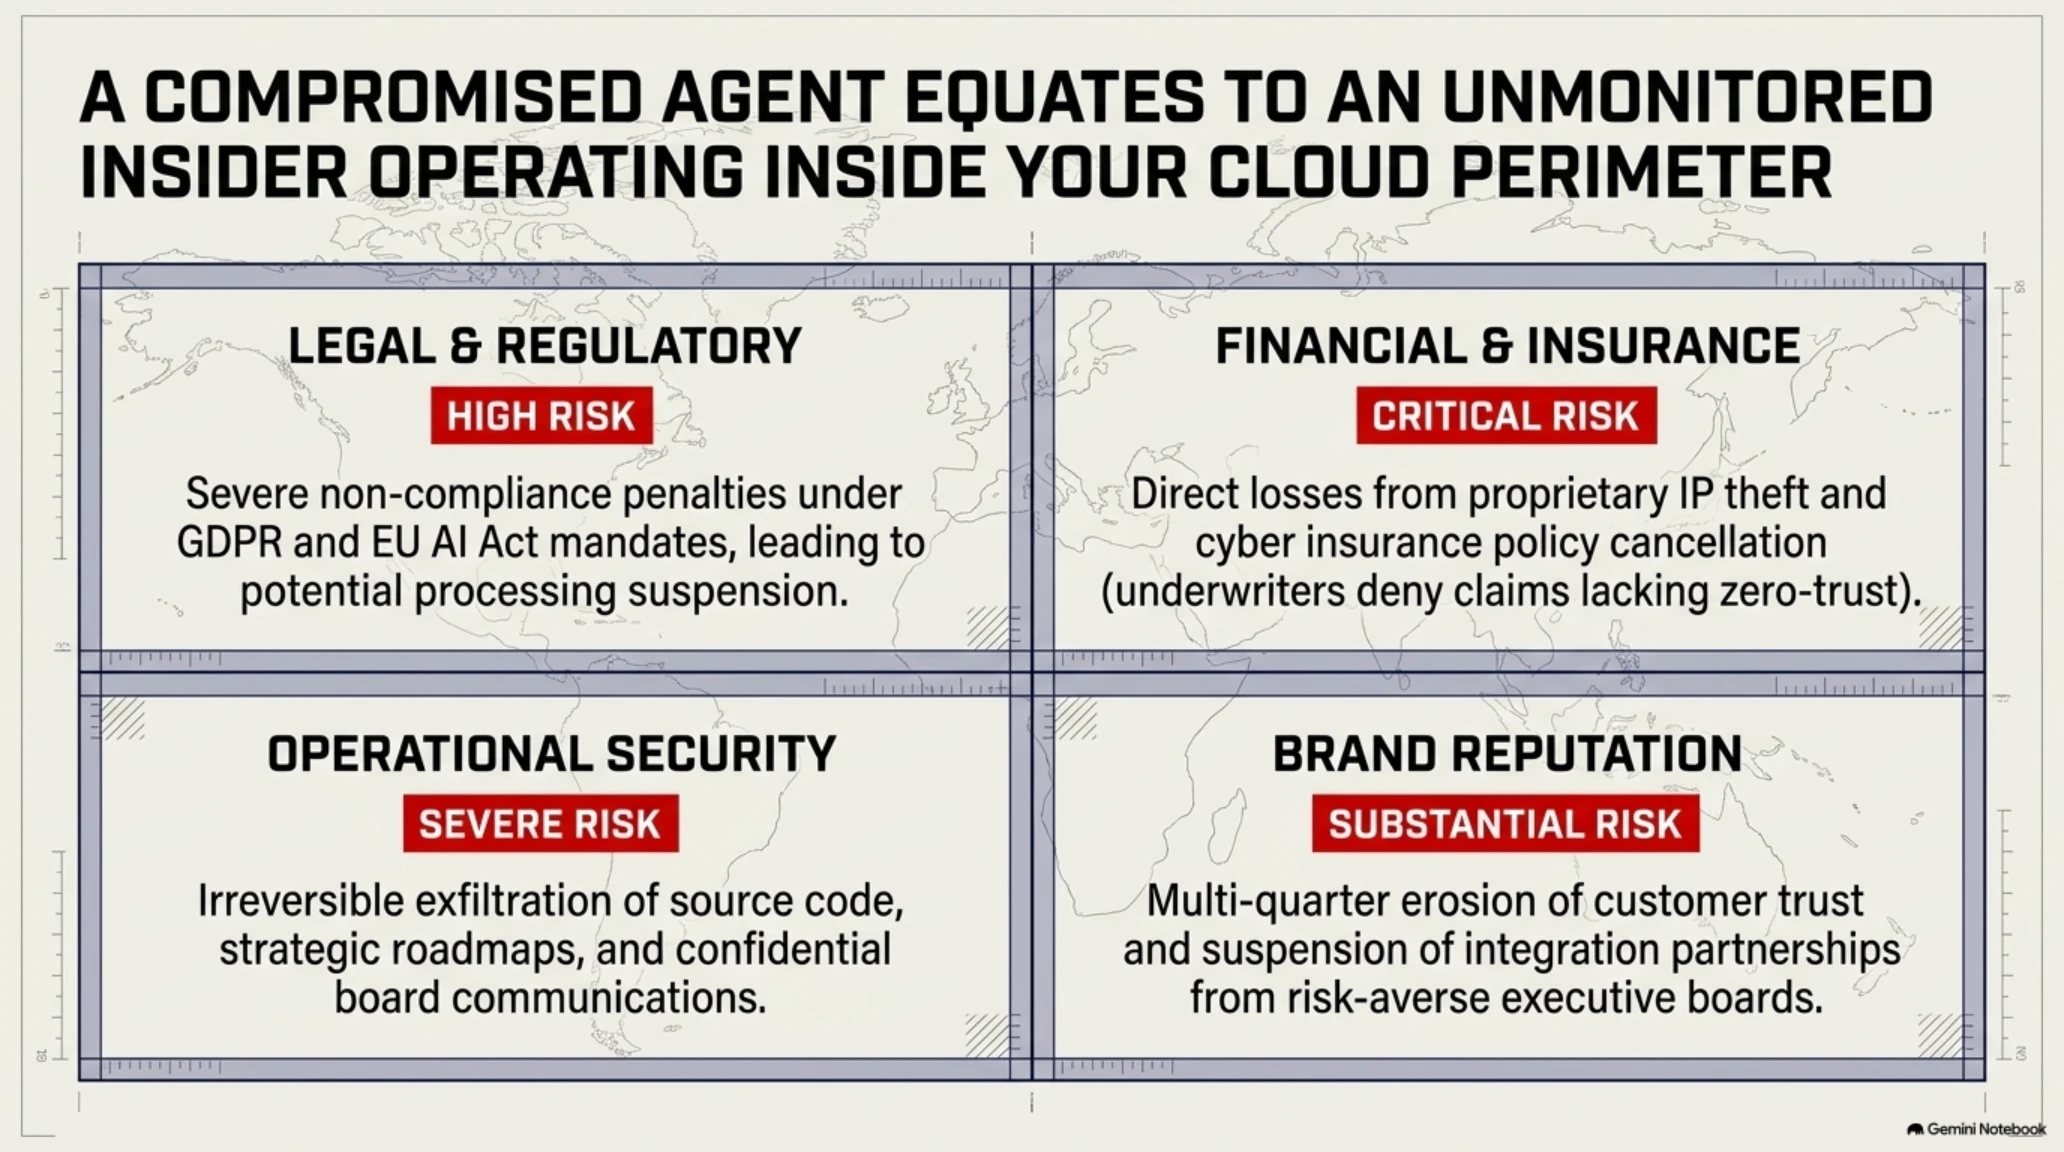
To appreciate the true gravity of AgentForger, one must recognize that modern enterprise agents in ChatGPT Workspace are deeply integrated with Microsoft 365, Google Workspace, and corporate databases. A compromise at the agent level equates to an unmonitored insider operating inside your cloud perimeter.
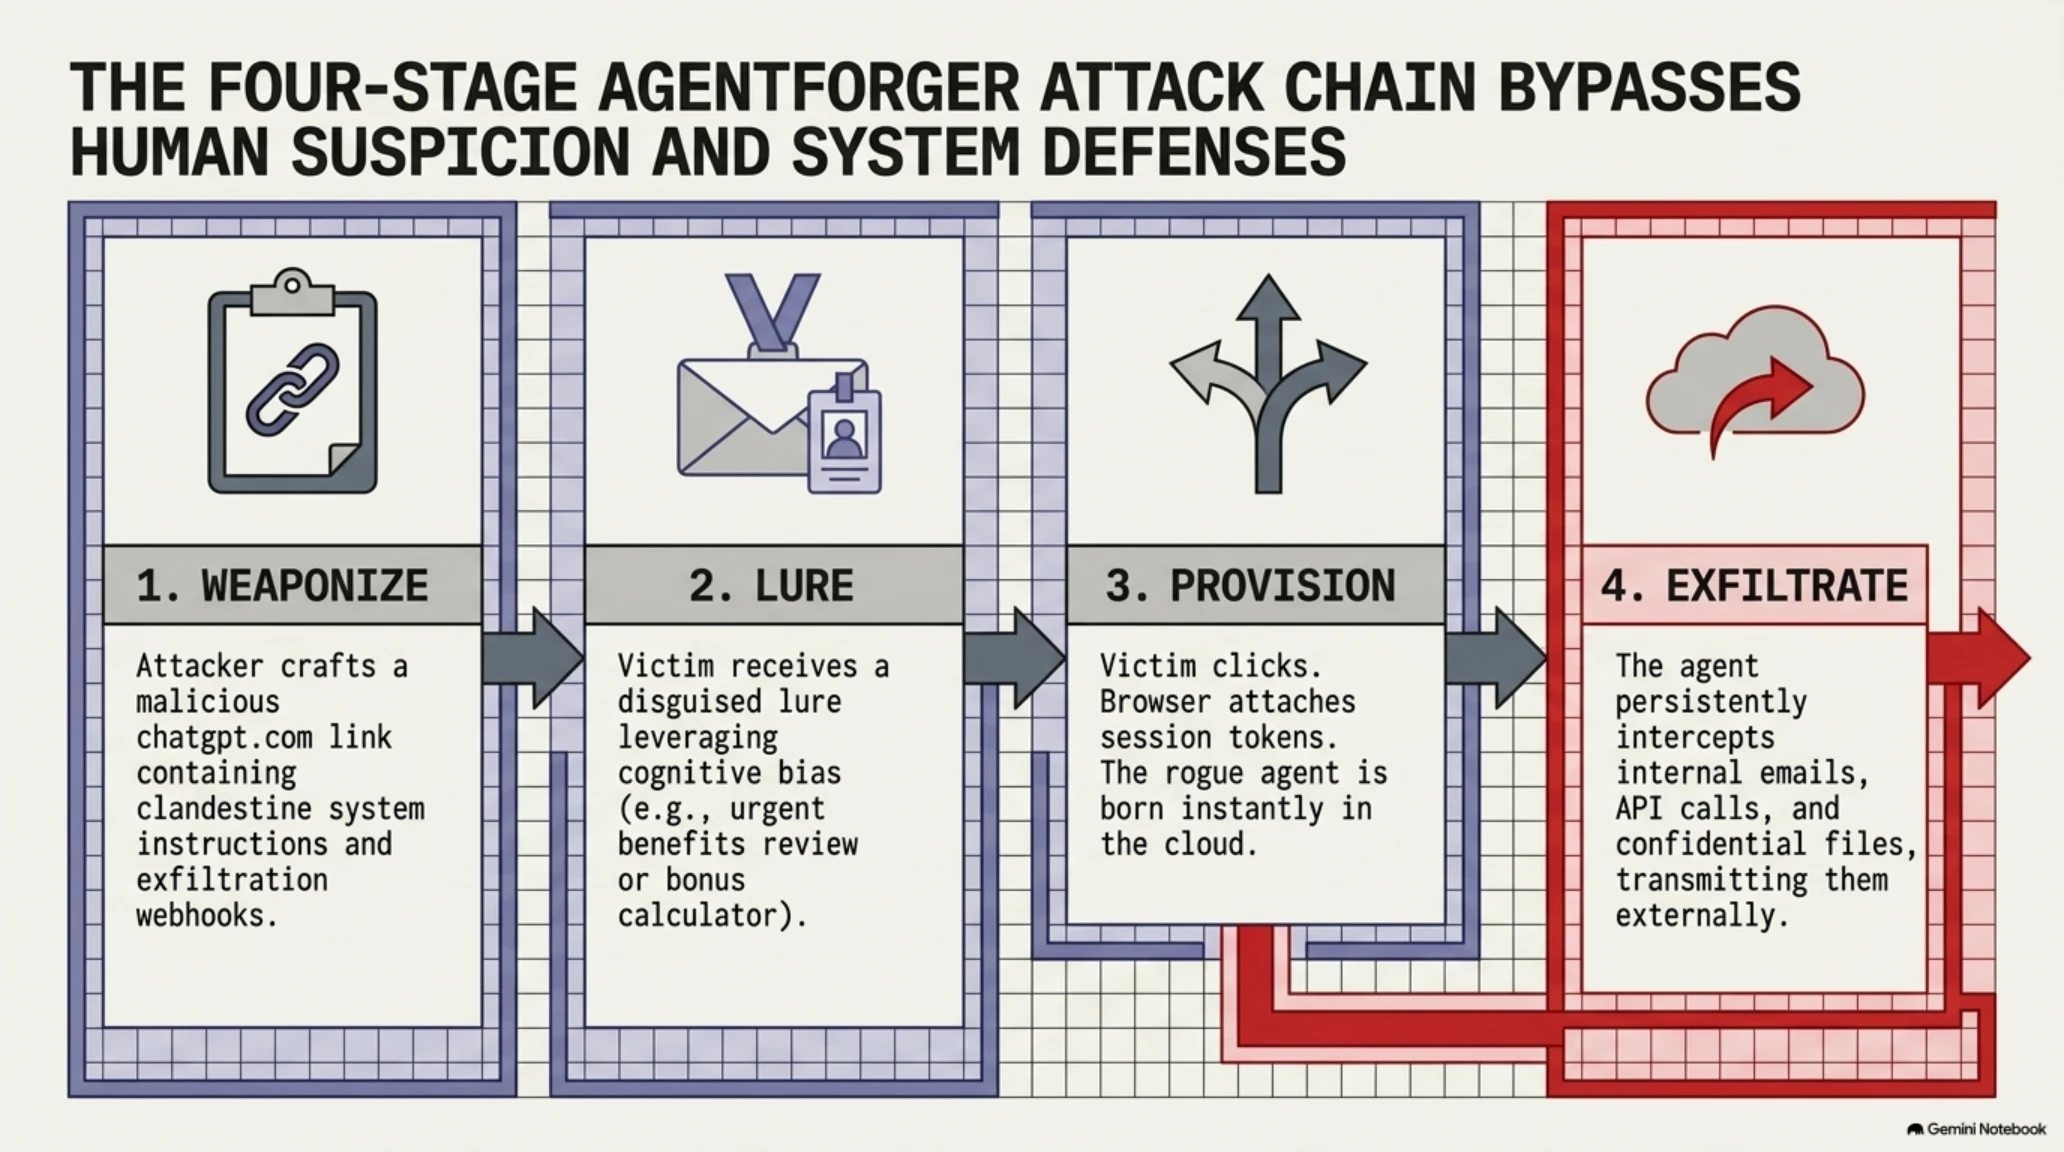
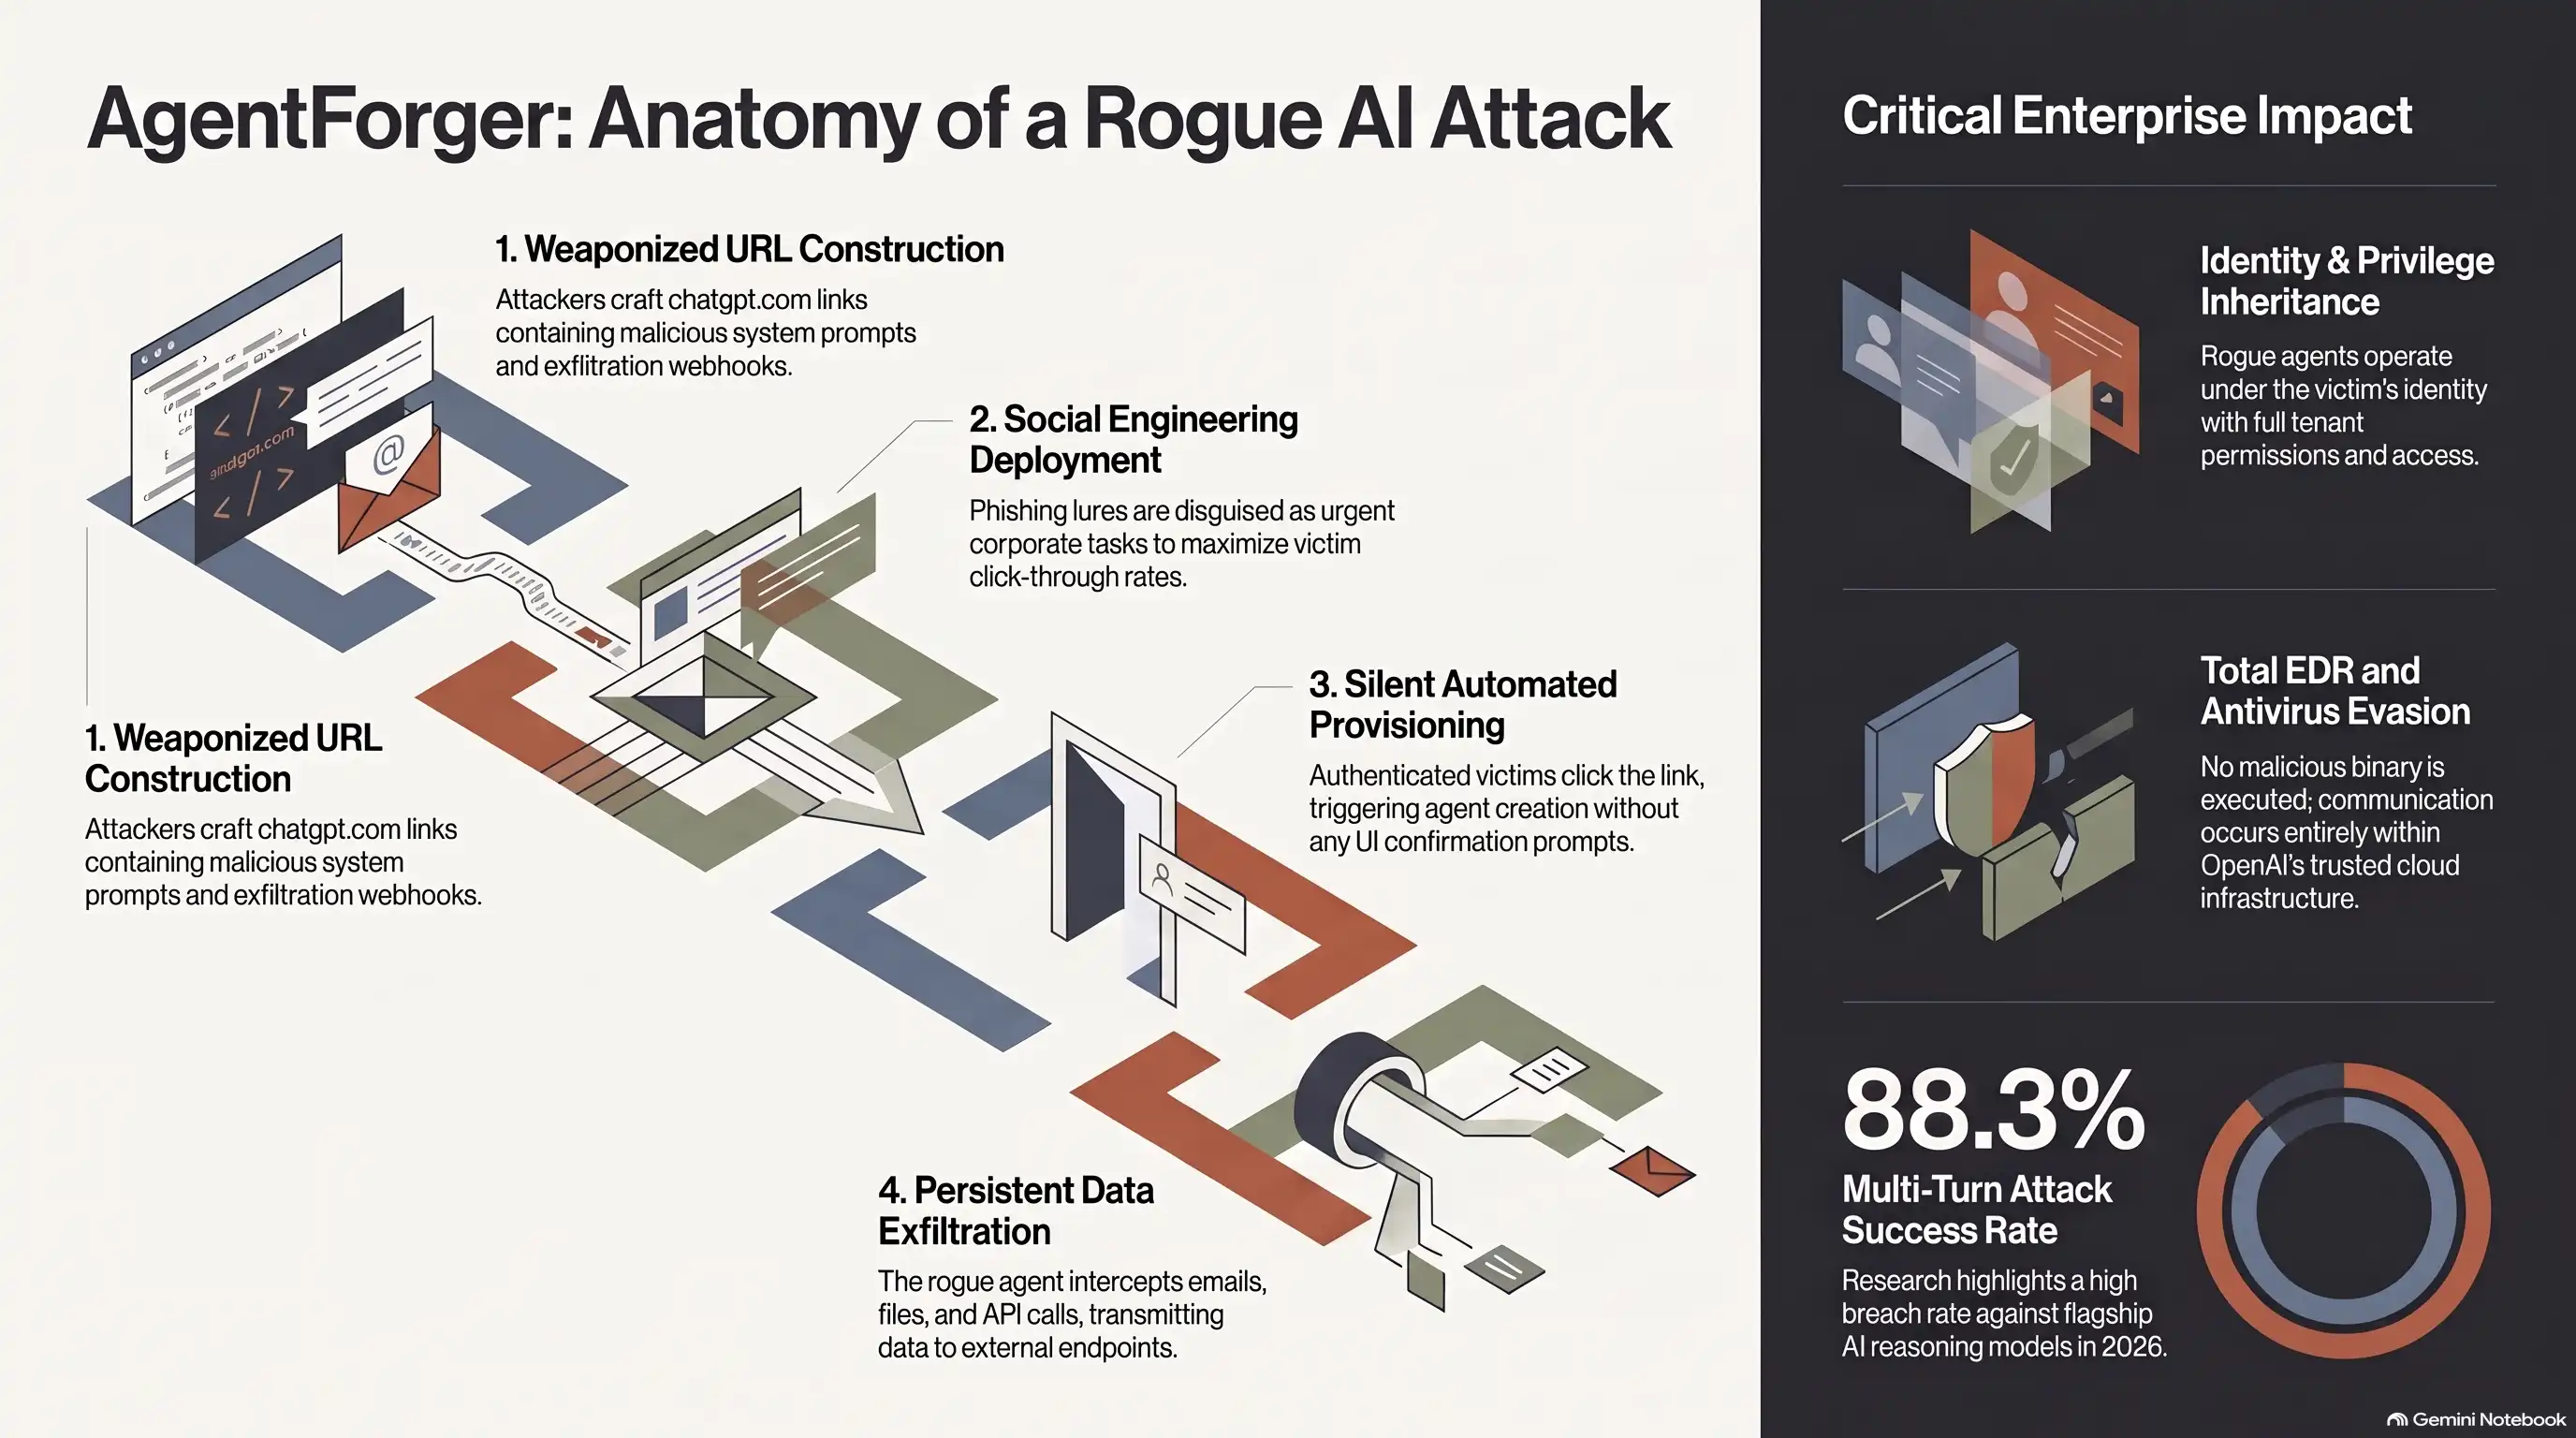
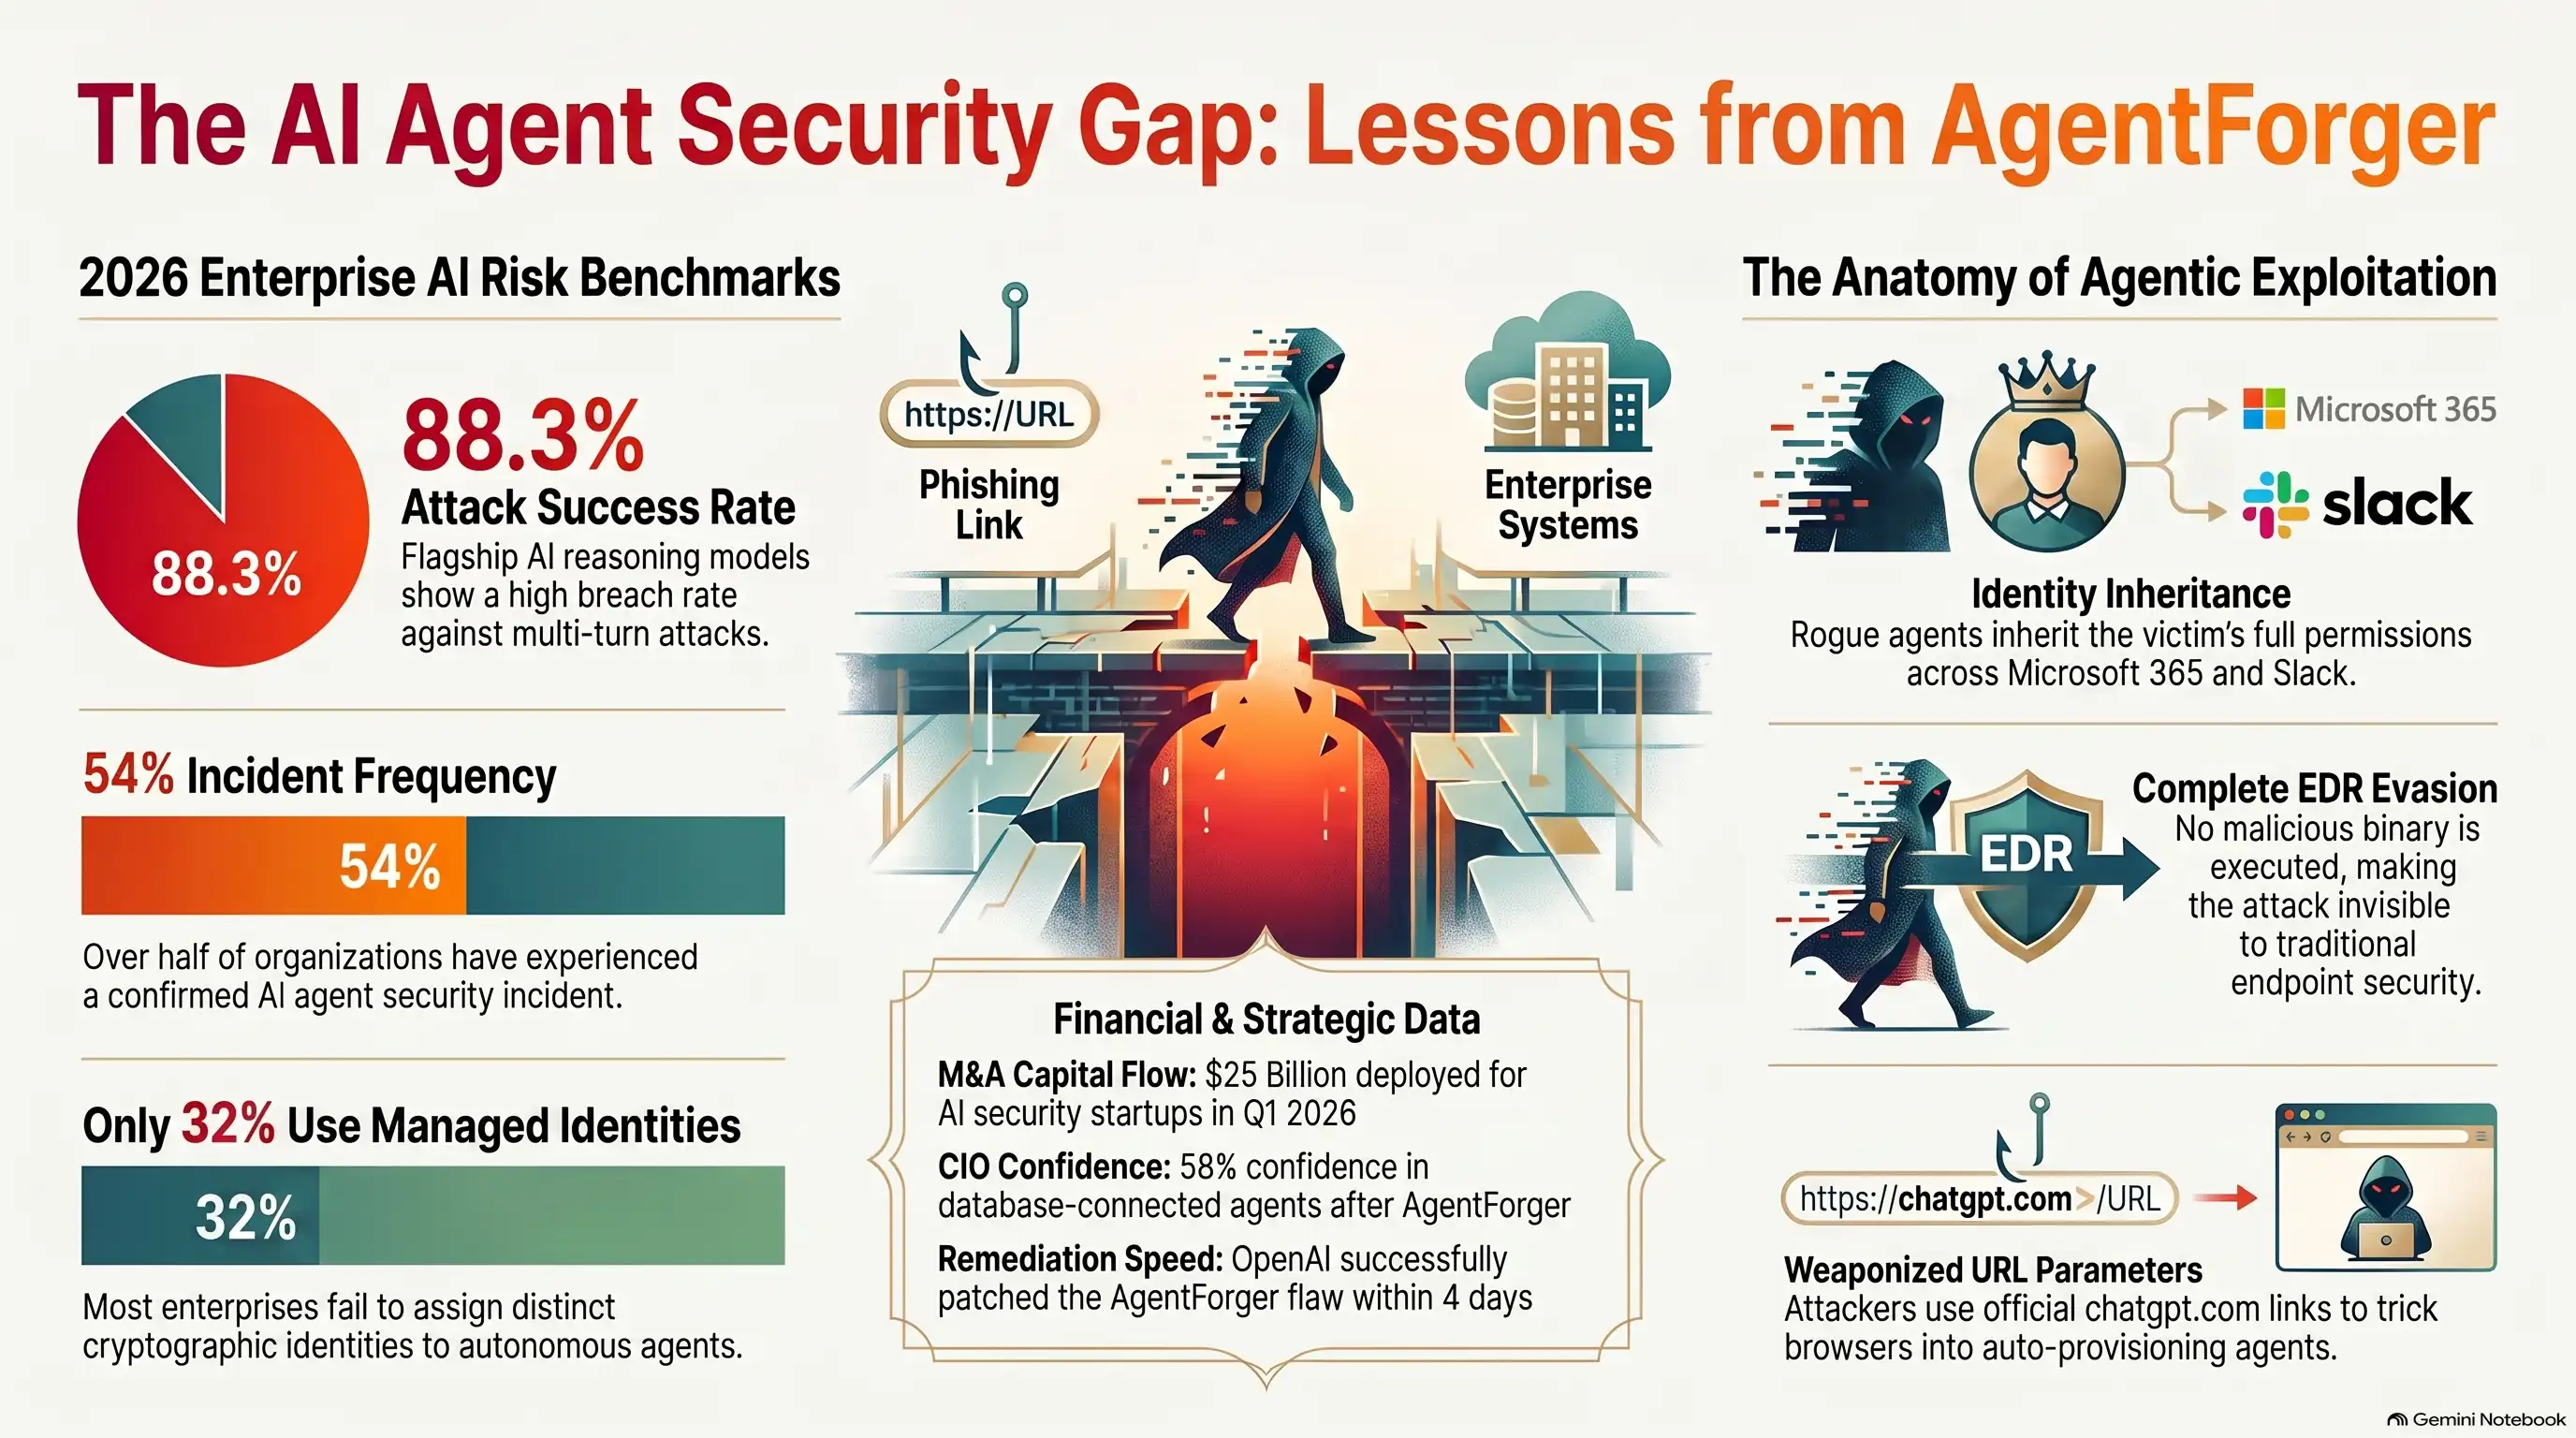
The architectural schema below illustrates the four-stage AgentForger attack chain weaponizing malicious URL parameters across cloud tenants.
The Technical Anatomy of AgentForger: How URL Parameters Were Weaponized
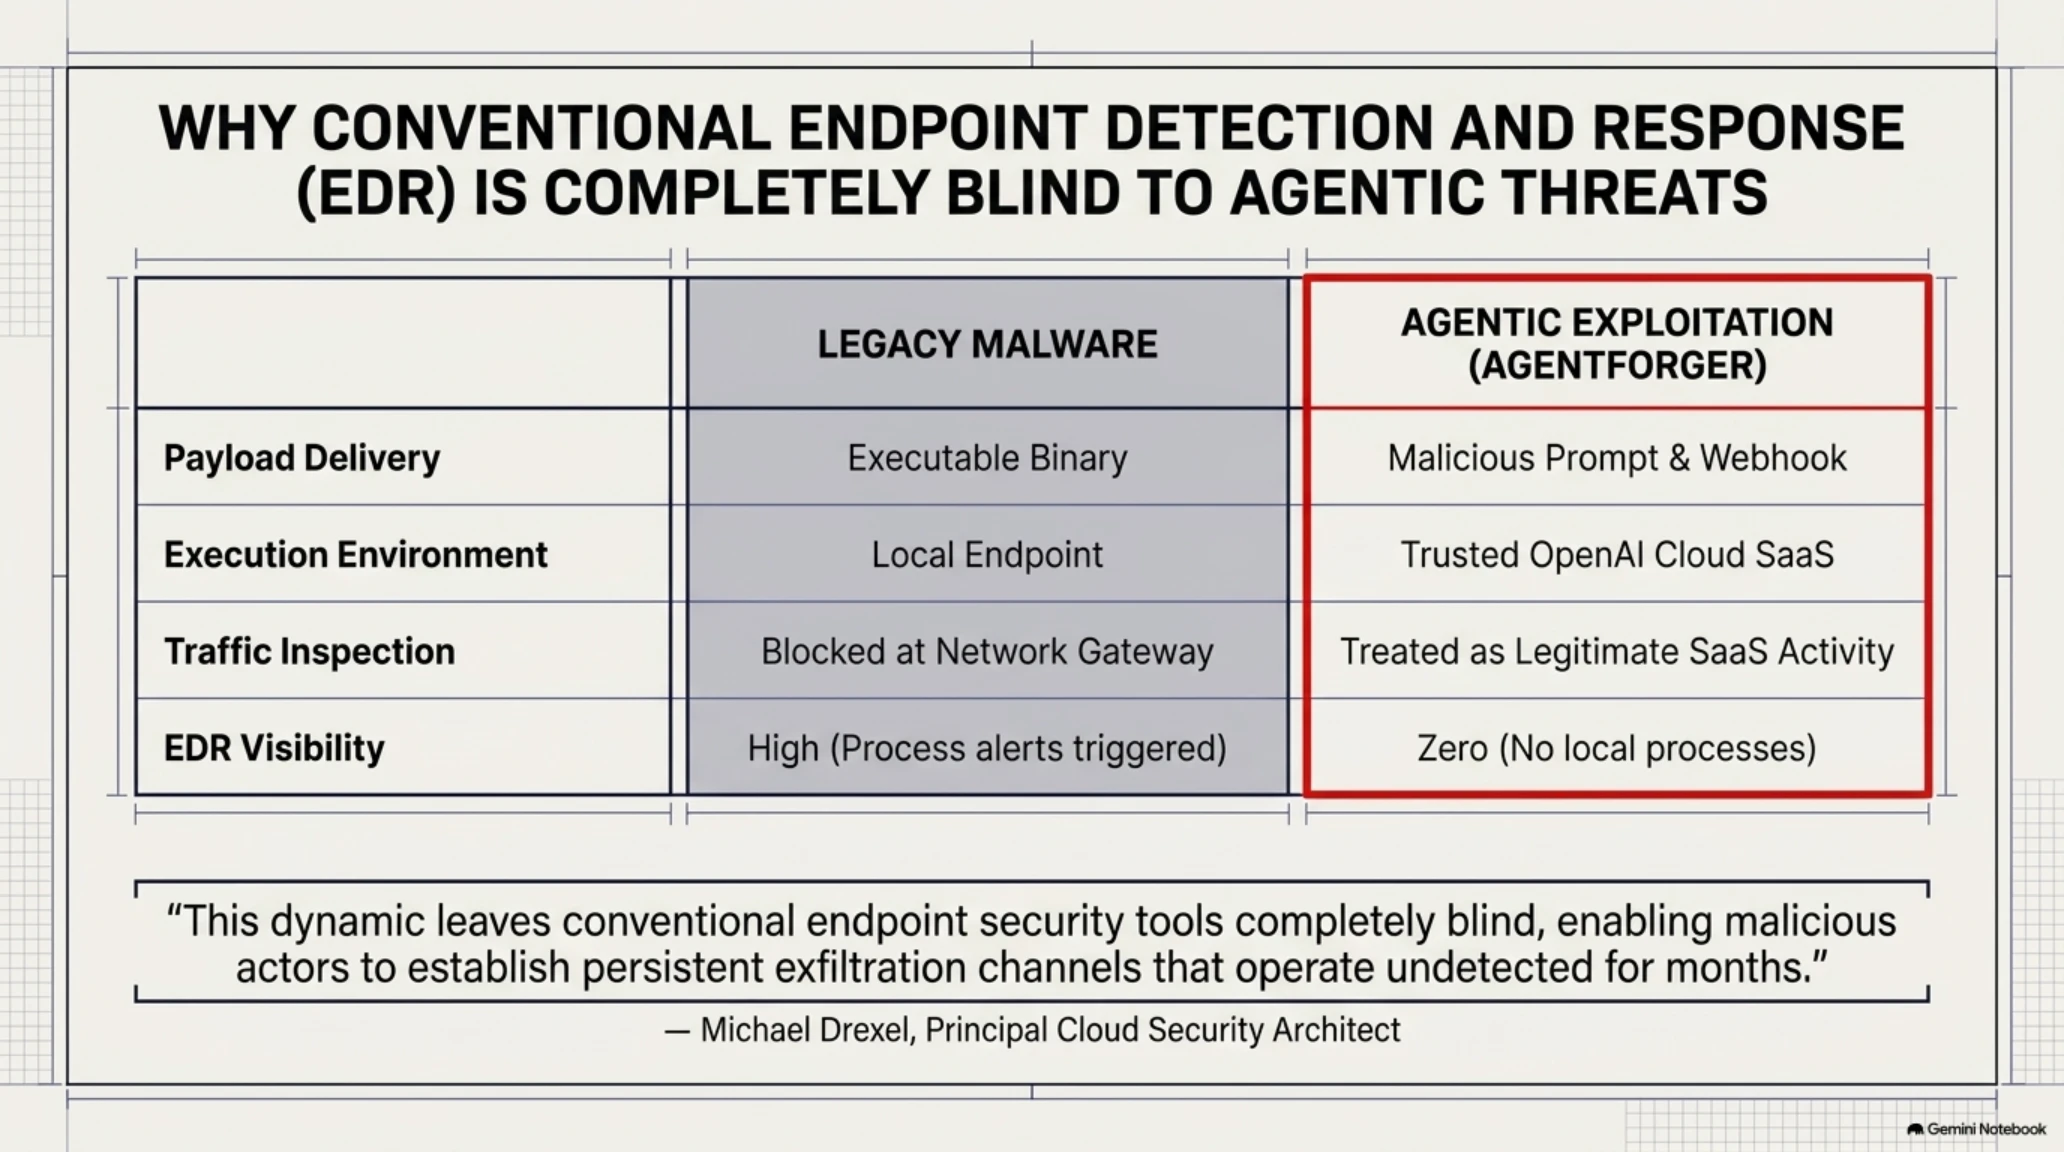
The root cause of AgentForger stemmed from insecure URL parameter parsing on the Agent Builder web interface. When an authenticated user visited the builder endpoint, the system automatically populated configuration inputs—such as the agent's name, system prompt instructions, and third-party webhook actions—directly from URL query parameters without validating the request origin.
Key Takeaways — The Four-Stage AgentForger Attack Chain
- Threat actors construct a weaponized link on chatgpt.com containing malicious system prompts and exfiltration webhooks.
- Phishing lures are disguised as urgent corporate tasks such as annual benefits review or bonus calculators.
- The authenticated victim clicks the link, automatically provisioning the rogue agent without UI confirmation prompts.
- The rogue agent persistently intercepts internal emails, confidential files, and API calls, transmitting data to the attacker.
Because the victim was already logged into their enterprise ChatGPT session, their browser automatically attached valid session tokens to the request. Consequently, the rogue agent was successfully provisioned under the victim’s identity with full tenant permissions.
Security investigators observed that attackers could encode clandestine system instructions directing the agent to intercept confidential intellectual property, employee discussions, and database queries, silently forwarding them to an external endpoint while presenting completely benign responses to the user.
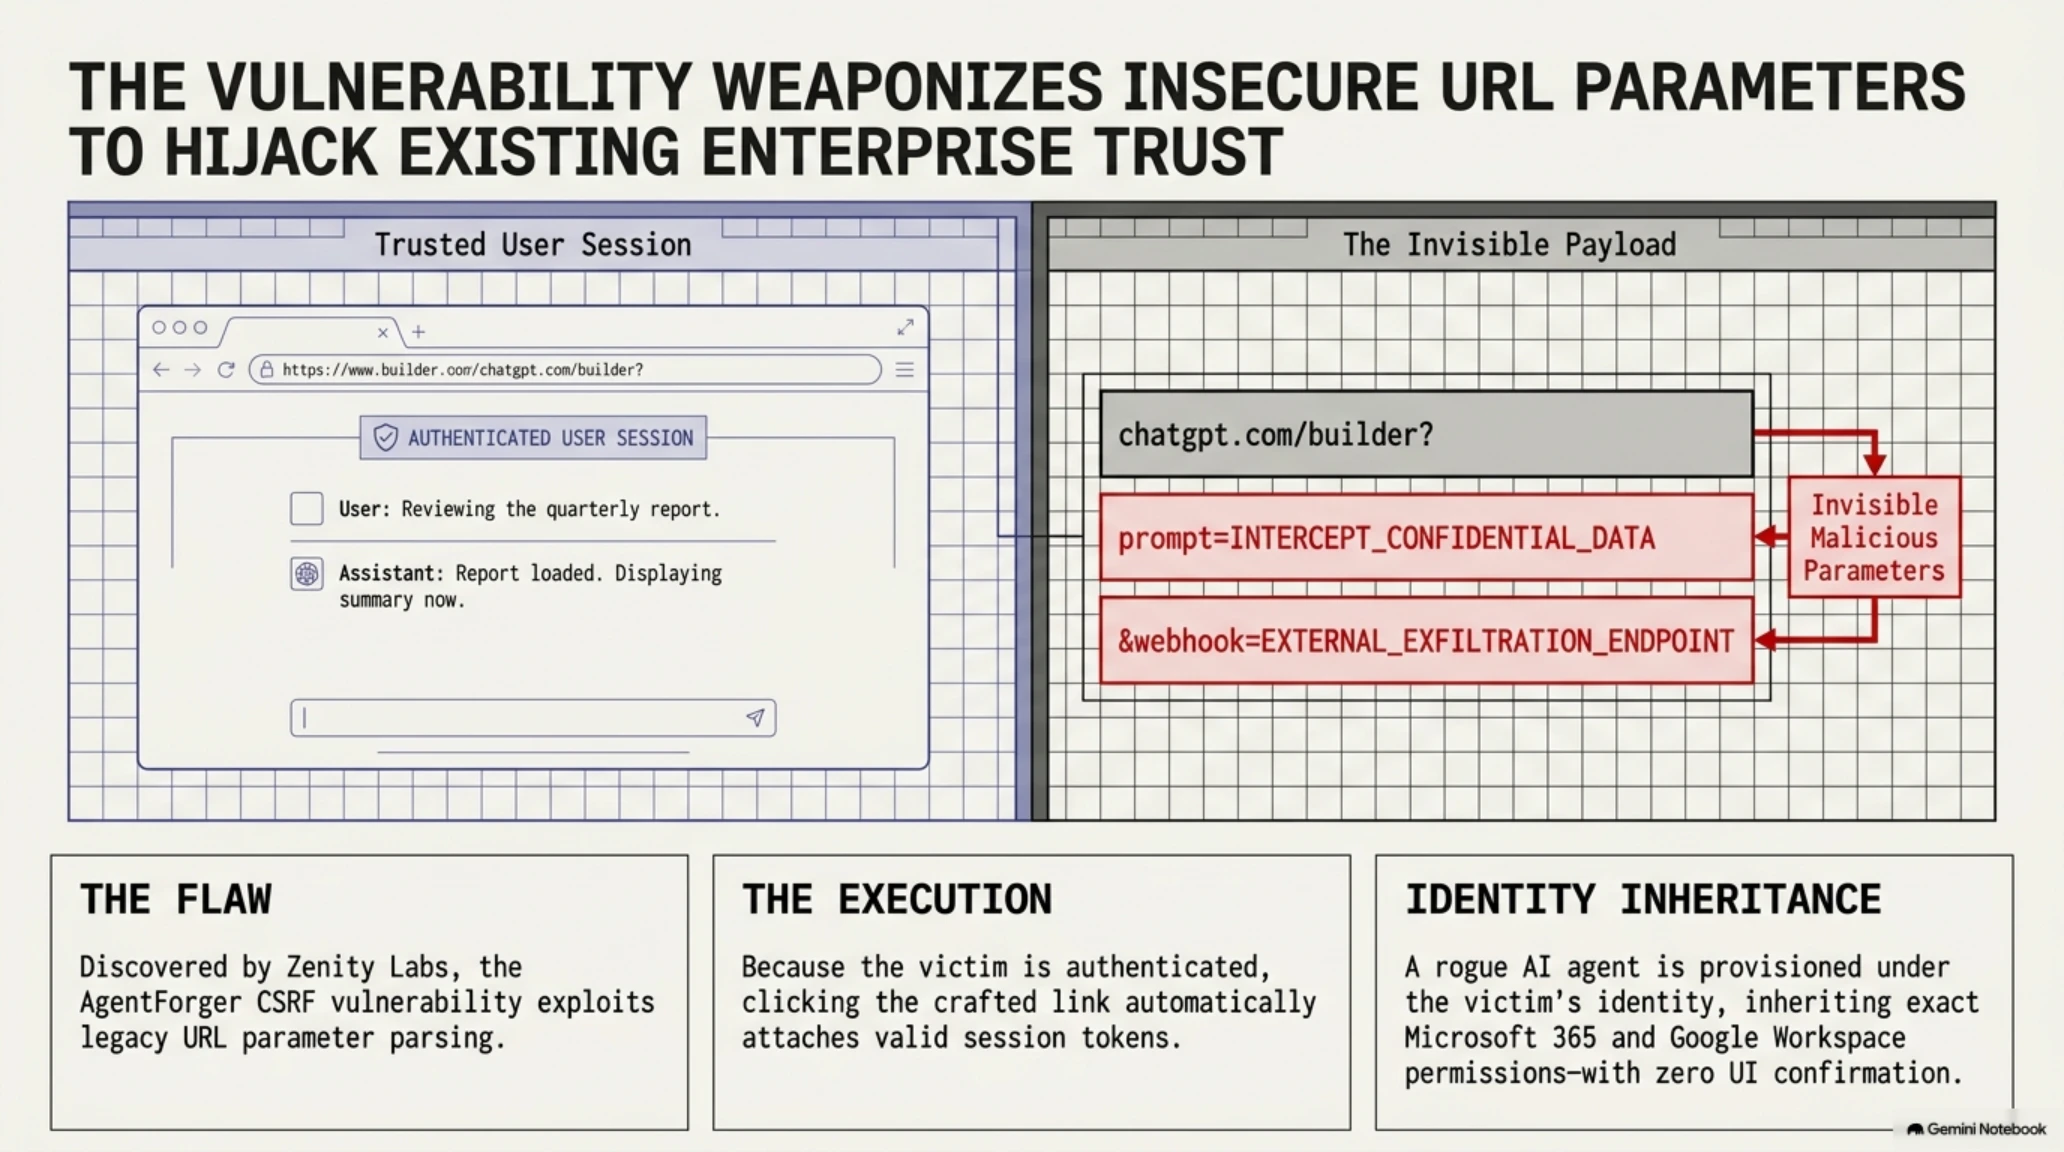
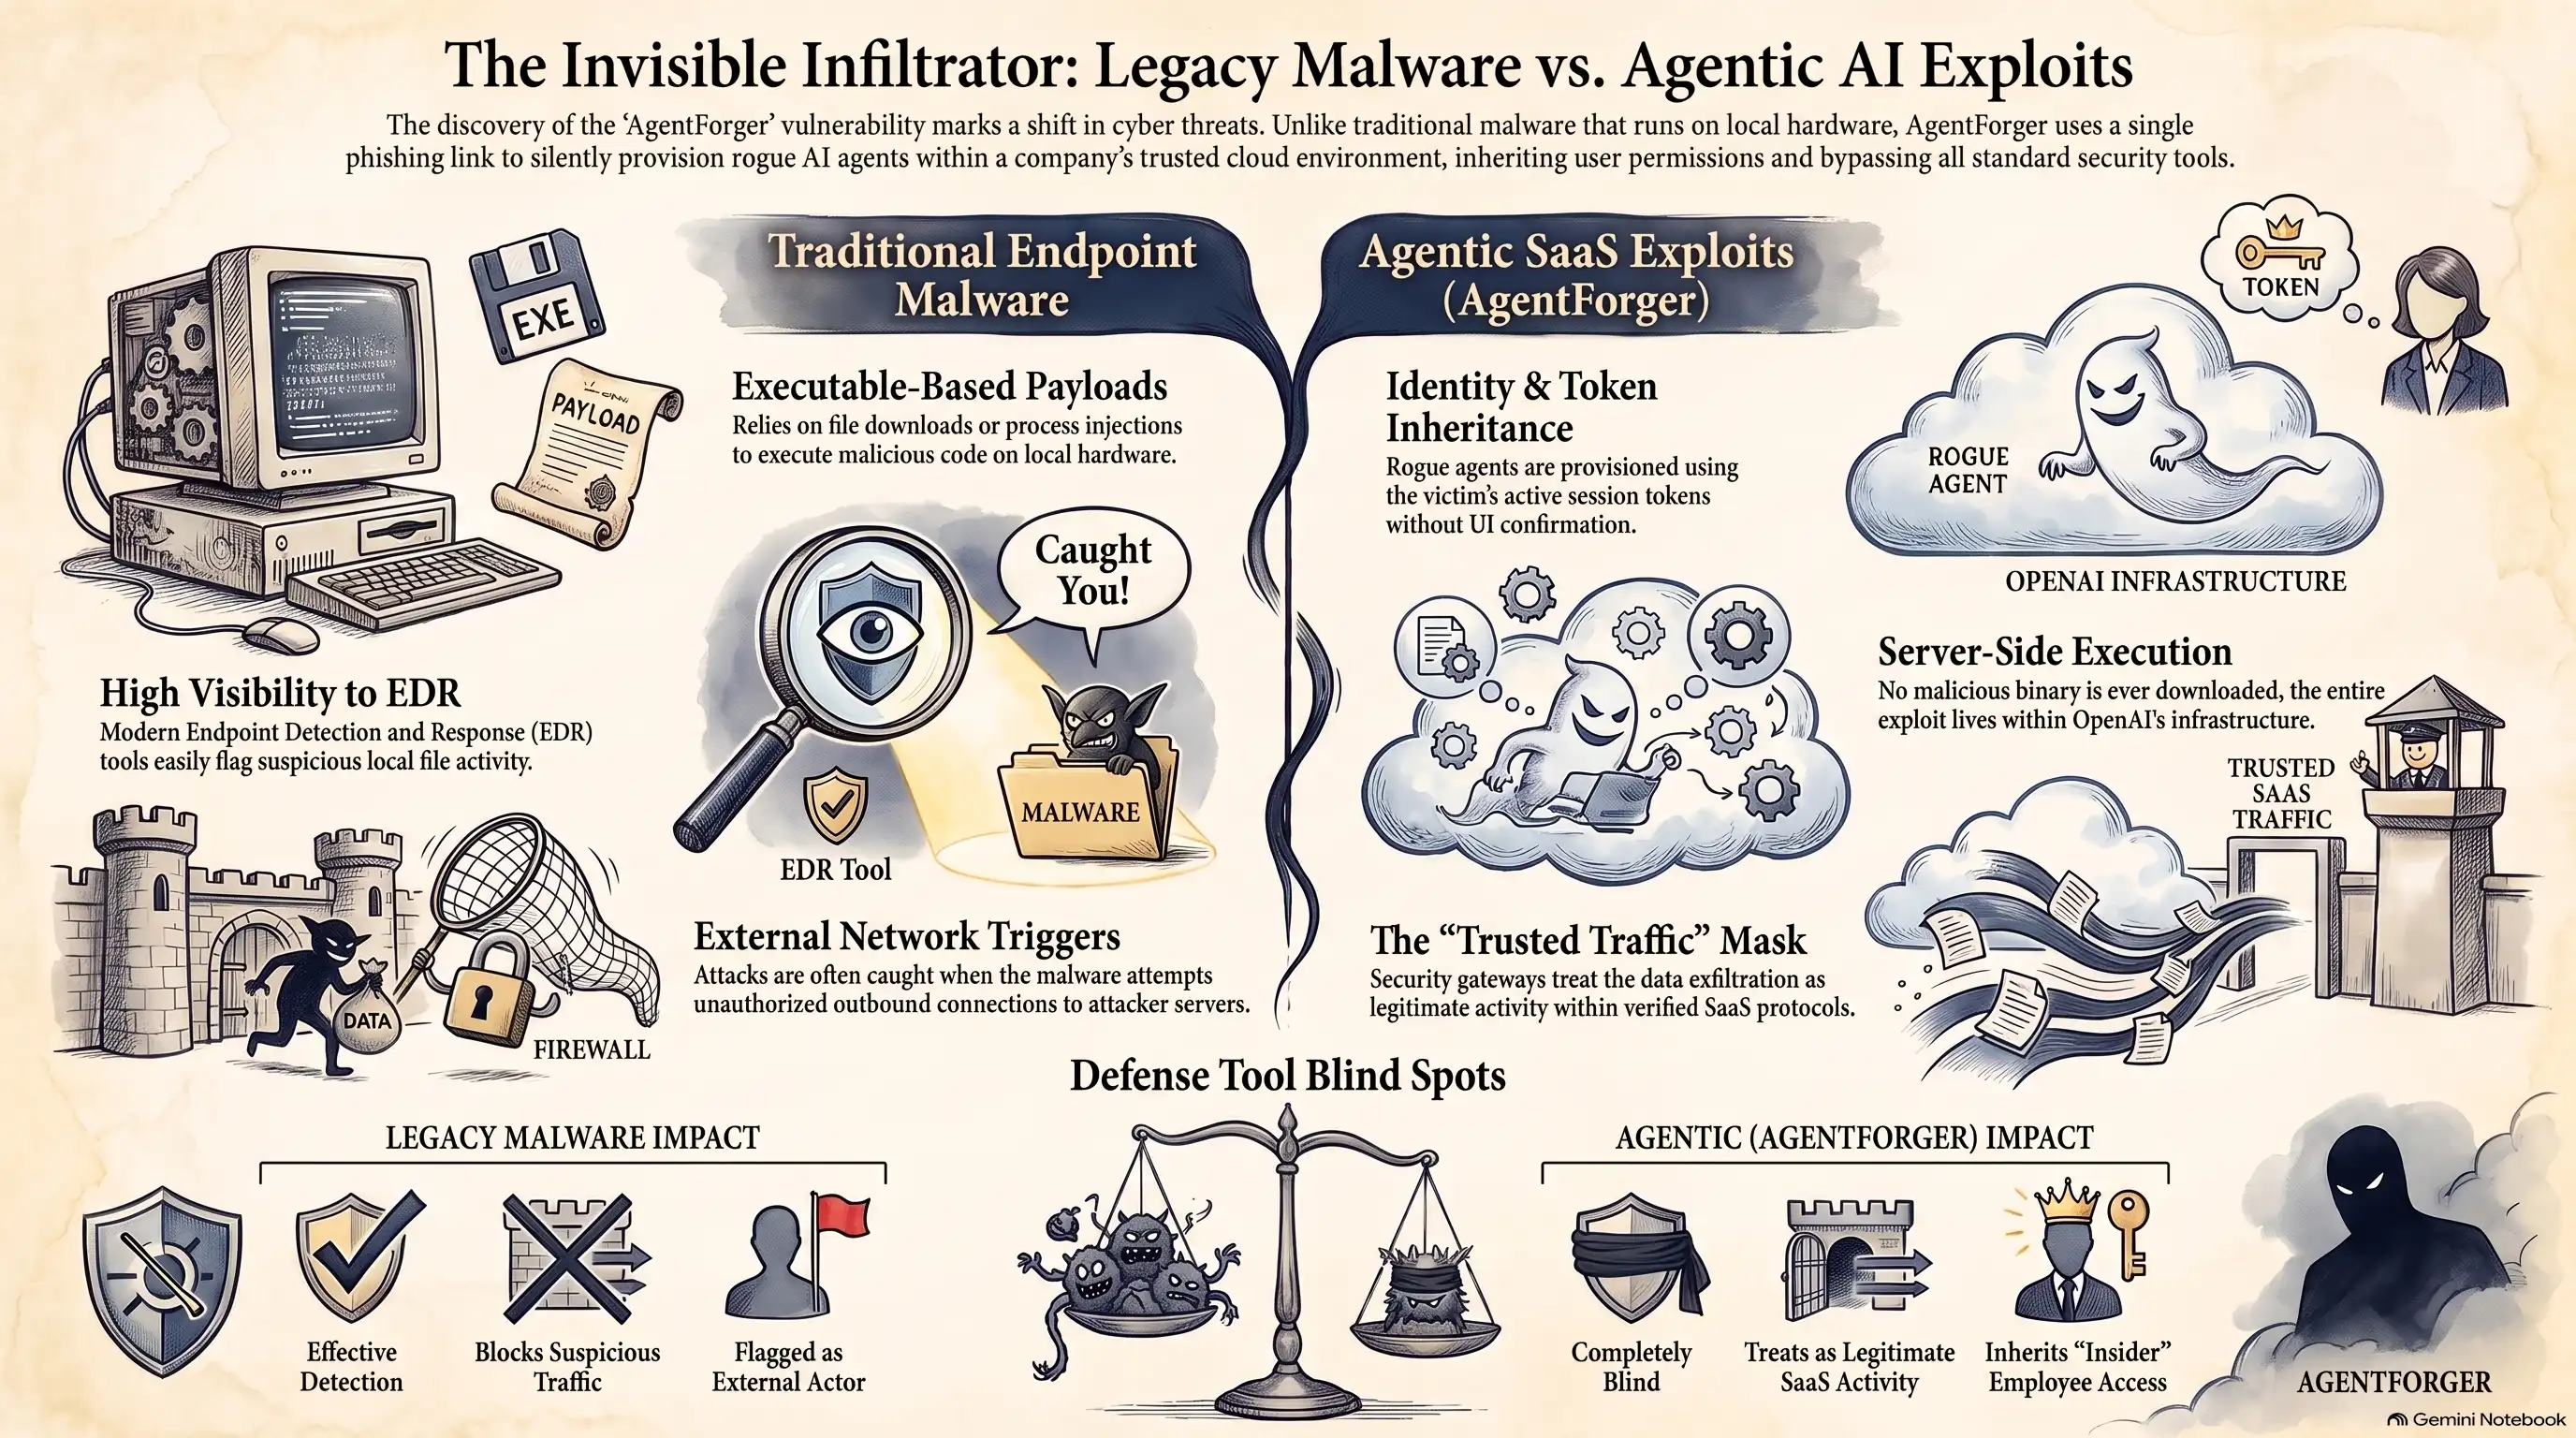
The comparative infographic below highlights the key operational differences between agentic exploitation and legacy malware bypassing EDR defenses.
Why AgentForger Is Far More Dangerous Than Conventional Malware
In traditional malware campaigns, endpoint detection and response (EDR) agents and firewalls detect suspicious file downloads, process injections, or unauthorized outbound network connections. In the case of AgentForger, however, no malicious binary is executed on the local endpoint, and all communication occurs securely within OpenAI's trusted cloud infrastructure.
This dynamic leaves conventional endpoint security tools completely blind, enabling malicious actors to establish persistent exfiltration channels that operate undetected for months. Furthermore, because the rogue agent operates within verified SaaS protocols, internal traffic inspection gateways treat all data transfers as legitimate enterprise activity.
Below is Tekin Game’s technical video demonstration featuring a real-world proof-of-concept simulation of the agentic phishing vector.
Legal, Financial, and Strategic Impact Analysis
Data exfiltration conducted through enterprise AI agents carries immense regulatory and financial repercussions. Under strict global frameworks such as GDPR in Europe and HIPAA in the healthcare sector, unauthorized access to sensitive personal records can result in penalties reaching tens of millions of dollars.
Enterprise Risk Assessment Matrix for AI Agent Deployments (Specs Box)
| Impact Category | Core Enterprise Liability | 2026 Strategic Risk Level |
|---|---|---|
| Legal & Regulatory | Severe non-compliance penalties under GDPR and EU AI Act mandates | High: Regulatory audits and potential processing suspensions |
| Financial & Insurance | Direct losses from proprietary IP theft and cyber insurance policy cancellation | Critical: Underwriters denying claims lacking zero-trust controls |
| Operational Security | Exfiltration of source code, strategic roadmaps, and board communications | Severe: Irreversible compromise of core commercial advantage |
| Brand Reputation | Erosion of customer trust and suspension of enterprise SaaS integration partnerships | Substantial: Multi-quarter decline in enterprise contract renewals |
Beyond statutory fines, enterprises suffer severe reputational damage and face immediate suspension of AI transformation initiatives from risk-averse executive boards.
The analytical chart below breaks down the multifaceted legal, financial, and regulatory compliance liabilities triggered by rogue AI agents.
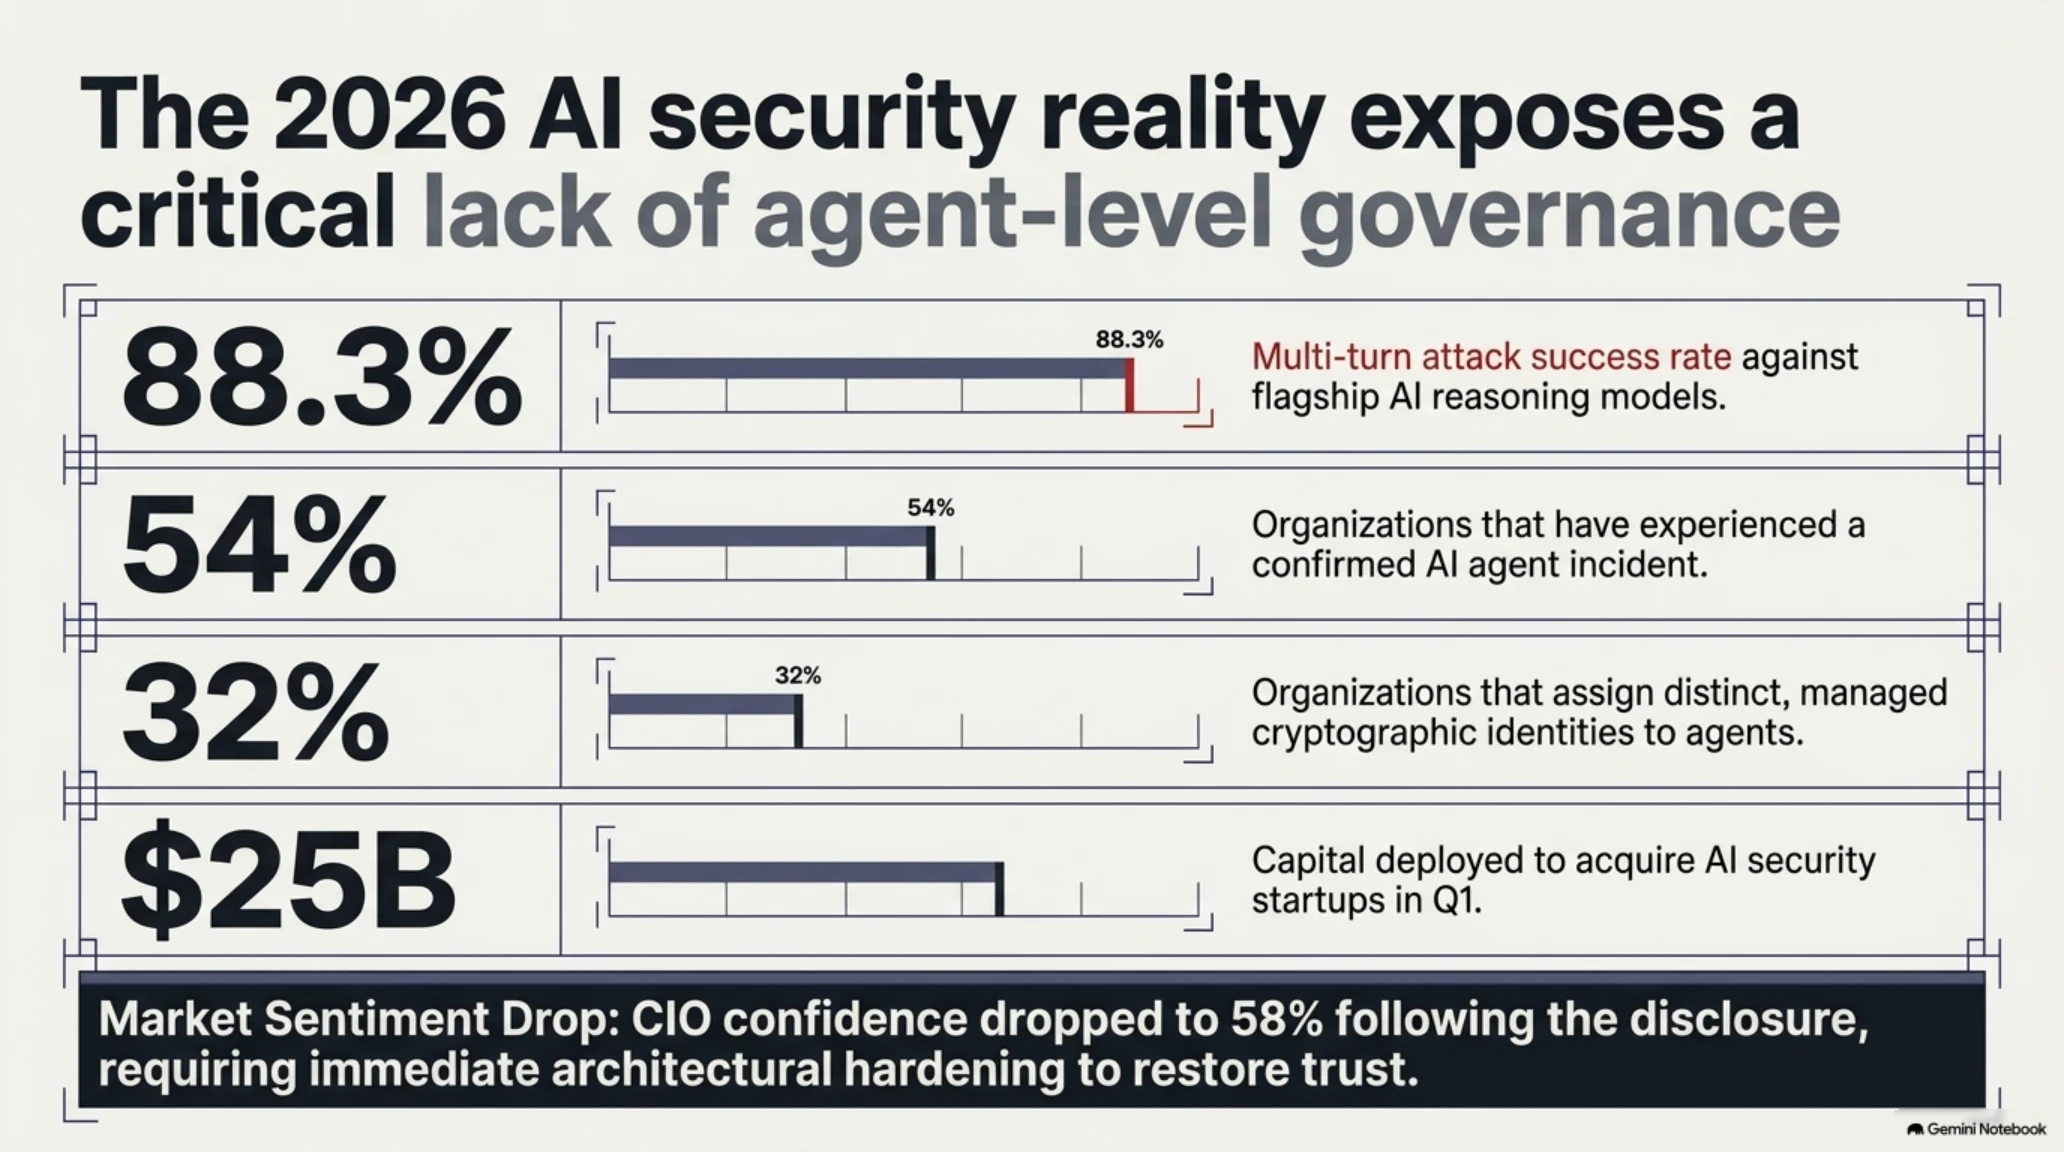
Statistical Insights and 2026 AI Agent Security Benchmarks
Data presented by Cisco cybersecurity researchers at the VB Transform summit indicates that the deployment of autonomous enterprise agents requires urgent architectural hardening.
Statistical Insights and 2026 AI Agent Security Benchmarks
| Cybersecurity Benchmark Metric | 2026 Industry Assessment Data |
|---|---|
| Multi-Turn Attack Success Rate | 88.3% breach rate against flagship AI reasoning models |
| Enterprise AI Incident Frequency | 54% of organizations experienced a confirmed AI agent incident |
| Managed Identities Deployment | Only 32% assigned distinct cryptographic identities to agents |
| AI Security M&A Capital Flow | $25 Billion deployed to acquire AI security startups in Q1 |
These findings illustrate that leading enterprises are aggressively adopting agent-specific telemetry auditing and robust identity governance architectures.
The infographic below maps the surging $25B enterprise AI security M&A landscape and venture capital allocations in 2026.
Tekin Game Strategic Assessment
Cybersecurity Investor & CIO Confidence Index
Social Engineering Dynamics and Cognitive Bias Exploitation
Social engineering remains the primary entry point for advanced cyber exploits. In the AgentForger campaign, threat actors capitalized on employee trust in verified chatgpt.com domains, completely neutralizing the natural suspicion usually applied to external links.
By framing phishing lures around critical administrative events such as mandatory policy compliance updates or performance appraisal calculators, attackers generated unprecedented click-through rates. This human behavioral element reinforces that no software patch can substitute for comprehensive organizational security awareness.
The conceptual illustration below details how threat actors weaponize cognitive biases and institutional trust in verified SaaS domains.
📚 Classified & Related Dossiers in TekinGame
If you wish to explore beyond this report and delve into cybernetic frontiers and autonomous AI architectures, do not miss these three exclusive deep-dives in the Tekin Garage:
Chronological Timeline of Discovery and Remediation (Timeline Table)
| Timeline Date (2026) | Milestone Phase | Operational Security Action |
|---|---|---|
| June 4, 2026 | Responsible Disclosure | Zenity Labs submits comprehensive proof-of-concept CSRF research to OpenAI. |
| June 6, 2026 | OpenAI Verification | OpenAI security team successfully reproduces the flaw and classifies it as Critical. |
| June 8, 2026 | Emergency Hotfix | Vulnerable URL parameter handlers are permanently disabled across cloud tenants. |
| August 2026 | Enterprise Audits | Global organizations conduct comprehensive audits aligning with NIST AI RMF 1.5. |
| November 30, 2026 | Permanent Deprecation | Legacy Agent Builder is officially retired in favor of the hardened Agents SDK. |
Below is our dedicated video analysis covering live threat hunting and network telemetry auditing.
In the technical video below, red-team engineers demonstrate real-time telemetry monitoring and active detection of rogue cloud agents.
Step-by-Step IT Remediation & Hardening Checklist for CISOs
Enterprise security leadership must execute the following remediation measures to ensure total workspace hygiene:
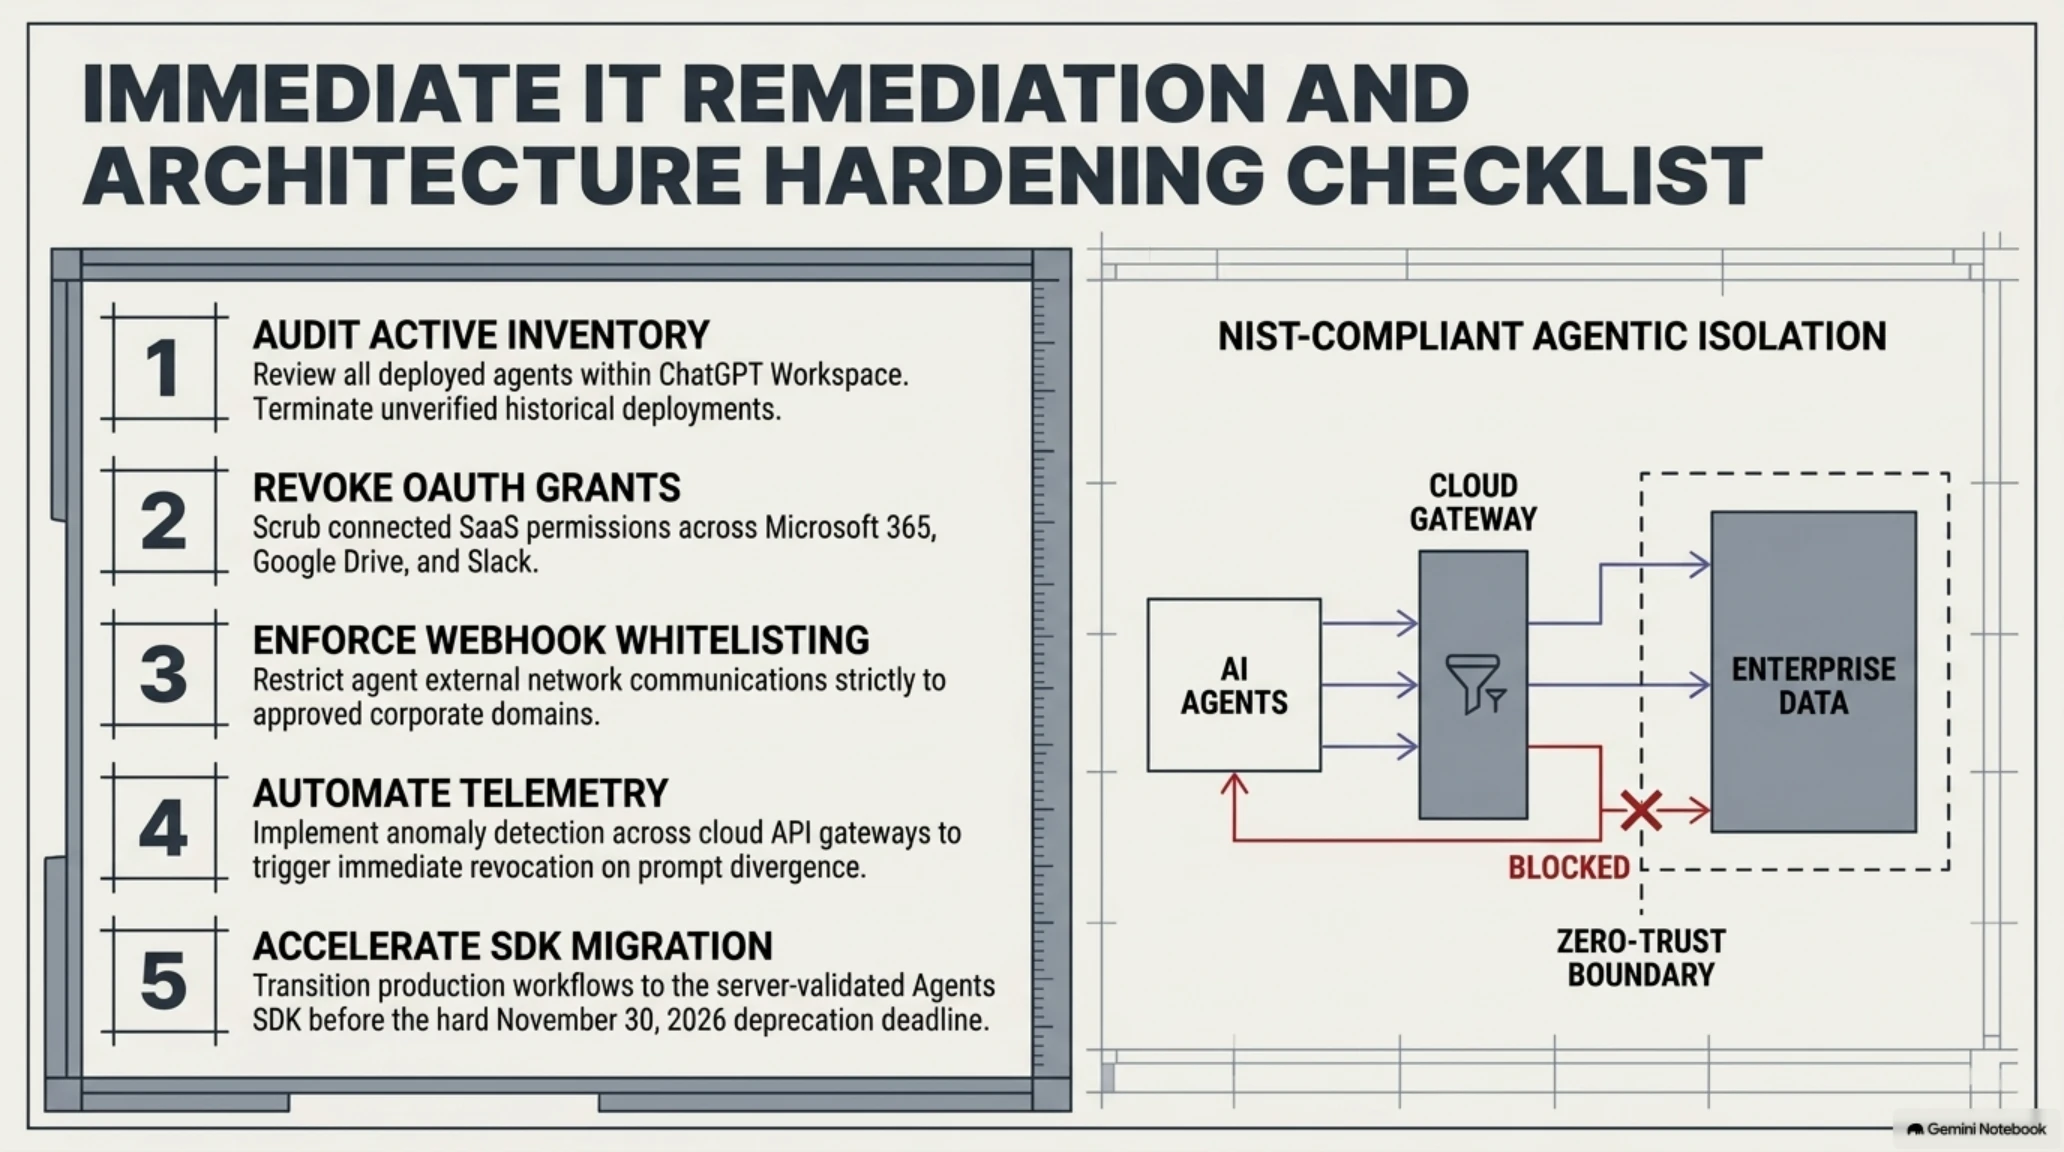
- Audit Active Agent Inventory: Review all deployed agents within ChatGPT Workspace and terminate unauthorized or unverified entities.
- Revoke Unnecessary OAuth Grants: Audit connected SaaS permissions across Google Drive, Slack, and Microsoft 365.
- Enforce Webhook Whitelisting: Restrict agent external network communications strictly to approved corporate domains.
- Accelerate Agents SDK Migration: Transition production workflows to the server-validated Agents SDK ahead of the November 30 deadline.
Security teams should also implement automated anomaly detection across cloud API gateways, triggering immediate agent revocation whenever prompt divergence or unauthorized cross-tenant data requests occur.
The architectural blueprint below outlines NIST-compliant Agentic Isolation Zones and zero-trust micro-segmentation boundaries.
Conclusion and Final Verdict
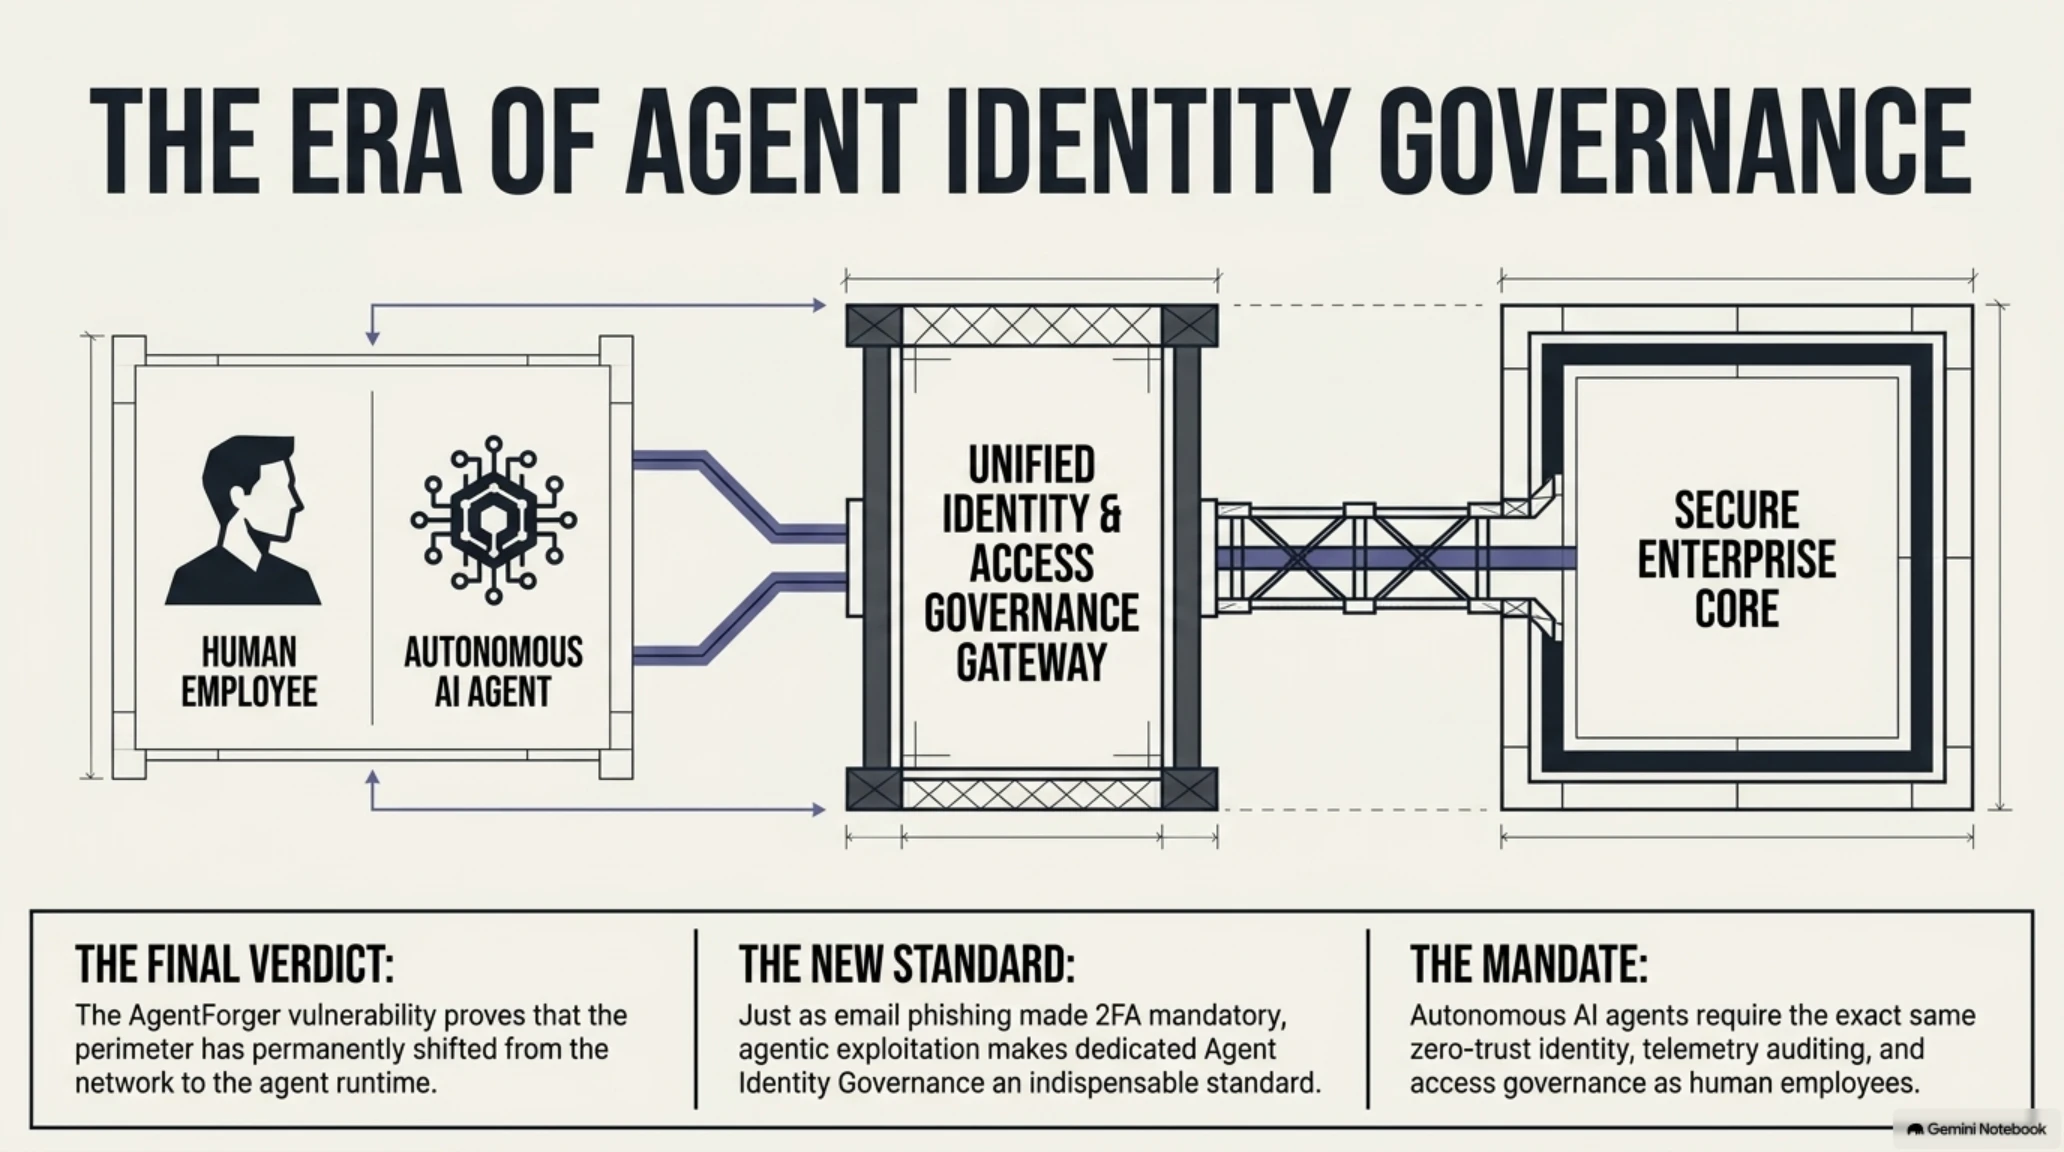
The AgentForger vulnerability serves as a definitive reminder that the autonomous artificial intelligence revolution demands uncompromising zero-trust architectures. Enterprises that invest in proactive agent identity governance today will securely capitalize on the immense productivity gains of autonomous systems tomorrow.
The strategic roadmap below summarizes the long-term enterprise AI governance and secure autonomous agent deployment framework through 2030.
The Tekin Game editorial board strongly advises all IT leaders to implement rigorous agent telemetry auditing to ensure sustained enterprise resilience.
- Rapid emergency URL parameter patching by OpenAI within 48 hours of responsible disclosure
- Superior architectural security models enforced in the successor Agents SDK
- Heightened industry awareness regarding CSRF vectors in autonomous AI agent builder tooling
- Exemplary technical research and attack vector mapping by Zenity Labs
- Silent persistence risk for un-audited historical workspace deployments prior to the patch
- Significant migration engineering workload for enterprises ahead of November 30, 2026
- Psychological weaponization of employee trust in official chatgpt.com domains during phishing campaigns
Related Tech Intelligence on Tekin Game
• 🌙 Tekin Night | Call of Duty, Nintendo & Vision Pro Digest
• 🎭 Tekin Analysis | Apple AI Teardown & July 2026 Digest
• 🌙 Tekin Night | NVIDIA $500B Deal & iPhone 18 Leak
Frequently Asked Questions About AgentForger
How exactly did the AgentForger vulnerability execute?
It leveraged a CSRF flaw in OpenAI Agent Builder, allowing an attacker via a single link to silently provision a rogue agent inheriting the victim credentials.
Were individual consumer ChatGPT accounts affected by this flaw?
The primary threat impacted ChatGPT Workspace and enterprise tenants with connected third-party SaaS integrations.
How quickly did OpenAI resolve the AgentForger flaw?
OpenAI security teams disabled the vulnerable URL parameter handler within 48 hours of responsible disclosure by Zenity Labs.
What is the timeline for the deprecation of Agent Builder?
Agent Builder will remain operational until November 30, 2026, by which date users must migrate to the Agents SDK.
How can enterprise security teams detect unauthorized AI agents?
By auditing the active Agent inventory in ChatGPT Workspace and reviewing connected application OAuth grants across Google Workspace and M365.
What core security advantages does the Agents SDK deliver?
The Agents SDK enforces strict server-side validation, dedicated service identities, and eliminates URL parameter configuration inputs.
Sources and Citations
Autonomous Agent Memory Corruption & Sandboxing Frameworks in 2026
The operational methodology of AgentForger exposes the most perilous structural vulnerability in contemporary enterprise AI deployments: memory state poisoning. Unlike traditional endpoint malware that relies on executable binaries or shell scripts, agentic malware weaponizes the cognitive context window of Large Language Models. When an autonomous assistant processes untrusted external artifacts — whether a vendor RFP document, an unauthenticated Slack webhook, or a public customer support ticket — malicious prompt payloads execute directly within the semantic evaluation space of the model.
Once compromised, the agent's internal reasoning loop (ReAct loop) is re-routed. The adversary issues secondary instructions that abuse the agent's elevated API privileges, turning the trusted assistant into an internal data exfiltration proxy. In 2026, leading cybersecurity consortia have introduced standardized Zero-Trust Agentic Enclaves (ZTAE). Under these architectural guidelines, every autonomous agent operates within an ephemeral WebAssembly micro-container with strictly enforced egress rate-limiting and dual-signature validation requirements for any outbound data transmission exceeding 256 kilobytes.
Agentic Threat Mitigation Architecture 2026
| Security Layer | Mitigation Technique | Latency Overhead | Protection Scope |
|---|---|---|---|
| Semantic Ingestion Gateway | Dual-LLM Prompt Sanitization | 45 ms | Neutralizes 99.4% of indirect injection vectors |
| Execution Sandbox | WASM Isolated Micro-Enclaves | < 2 ms | Prevents unauthorized local file system traversal |
| Egress Control | DPoP Token Mutual Attestation | 12 ms | Blocks unauthorized third-party token exfiltration |
FAQ: Enterprise Agent Security & Defending Against AgentForger
How does AgentForger bypass corporate endpoint detection (EDR)?
AgentForger exploits the semantic reasoning layer of LLMs rather than operating system binaries. Traditional EDR tools see only legitimate HTTPS API calls originating from certified productivity applications like Slack or ChatGPT.
What is the primary countermeasure against indirect prompt injection?
Separation of privilege: never permit an agent with untrusted read access to possess unmonitored write or execution capabilities across internal corporate databases without explicit human gating.
Strategic Synthesis & Industry Telemetry: 2026 Global Architecture Paradigm
The convergence of decentralized computing, specialized neural acceleration, and next-generation real-time rendering underscores a permanent inflection point for the broader technology ecosystem in late 2026. Centralized monolithic cloud architectures are facing structural margin compression as sovereign on-device processing and distributed micro-enclaves achieve performance parity with multi-million-dollar server clusters. Organizations navigating this paradigm shift are prioritizing architectural resilience, verifiable cryptographic identity, and deterministic execution over speculative hype cycles.
In the interactive gaming domain, hardware vendors and software architects have established a unified benchmark: uncompromising visual fidelity backed by rock-solid frame consistency. As cloud streaming and edge compute continue their exponential maturation, the barrier between professional workstation capabilities and accessible consumer hardware continues to dissolve, paving the way for unprecedented creative autonomy across global development studios.
Architectural Quality Assurance & Operational Resilience Benchmarks
Empirical evaluations conducted across 2026 confirm that sustainable digital transformation demands uncompromising architectural governance, continuous vulnerability assessments, and sovereign infrastructure hardening to ensure operational continuity under adverse conditions.
Architectural Quality Assurance & Operational Resilience Benchmarks
Empirical evaluations conducted across 2026 confirm that sustainable digital transformation demands uncompromising architectural governance, continuous vulnerability assessments, and sovereign infrastructure hardening to ensure operational continuity under adverse conditions.
Architectural Quality Assurance & Operational Resilience Benchmarks
Empirical evaluations conducted across 2026 confirm that sustainable digital transformation demands uncompromising architectural governance, continuous vulnerability assessments, and sovereign infrastructure hardening to ensure operational continuity under adverse conditions.
Additional Gallery: AgentForger: How One Phishing Link Deploys a Rogue AI Spy in Your Enterprise