Tekin Night comprehensive executive briefing for Thursday, November 12, 2026: Microsoft remediates 1,259 vulnerabilities including actively exploited Outlook zero-day; Railway PaaS forensic audit discloses $740,000 in unauthorized token spend from stolen AI keys; Sony Interactive Entertainment officially cancels Haven Studios' Fairgames; The Legend of Zelda Remake shatters Switch 2 records with 5.2M units sold; Git releases emergency patches for critical recursive clone RCE; and Sony sunsets the PlayStation Plus PC cloud app.
Cybersecurity, Infrastructure & Gaming Command Center // Nov 12, 2026
On the evening of Thursday, November 12, 2026, global infrastructure platforms and the interactive entertainment industry faced a synchronized collision of vulnerabilities and strategic market pivots. As we documented in Tekin Morning Nov 12 covering Google's $30 Pixel Tag, Microsoft Auto SR 120 FPS, and Claude Workplace, edge silicon architecture reached new maturity. Tonight, that focus shifts back to critical cloud security.
Building upon the enterprise ERP failures examined in Tekin Night Nov 11 regarding SAP's CVSS 10.0 crisis and N-able's emergency shutdown, the cloud ecosystem suffers another massive blow as the Railway PaaS breach leaks $740,000 in AI tokens. Concurrently, Sony abruptly cancels live-service shooter Fairgames, while Nintendo smashes records with a 5.2 million unit launch for Zelda Ocarina of Time Remake.
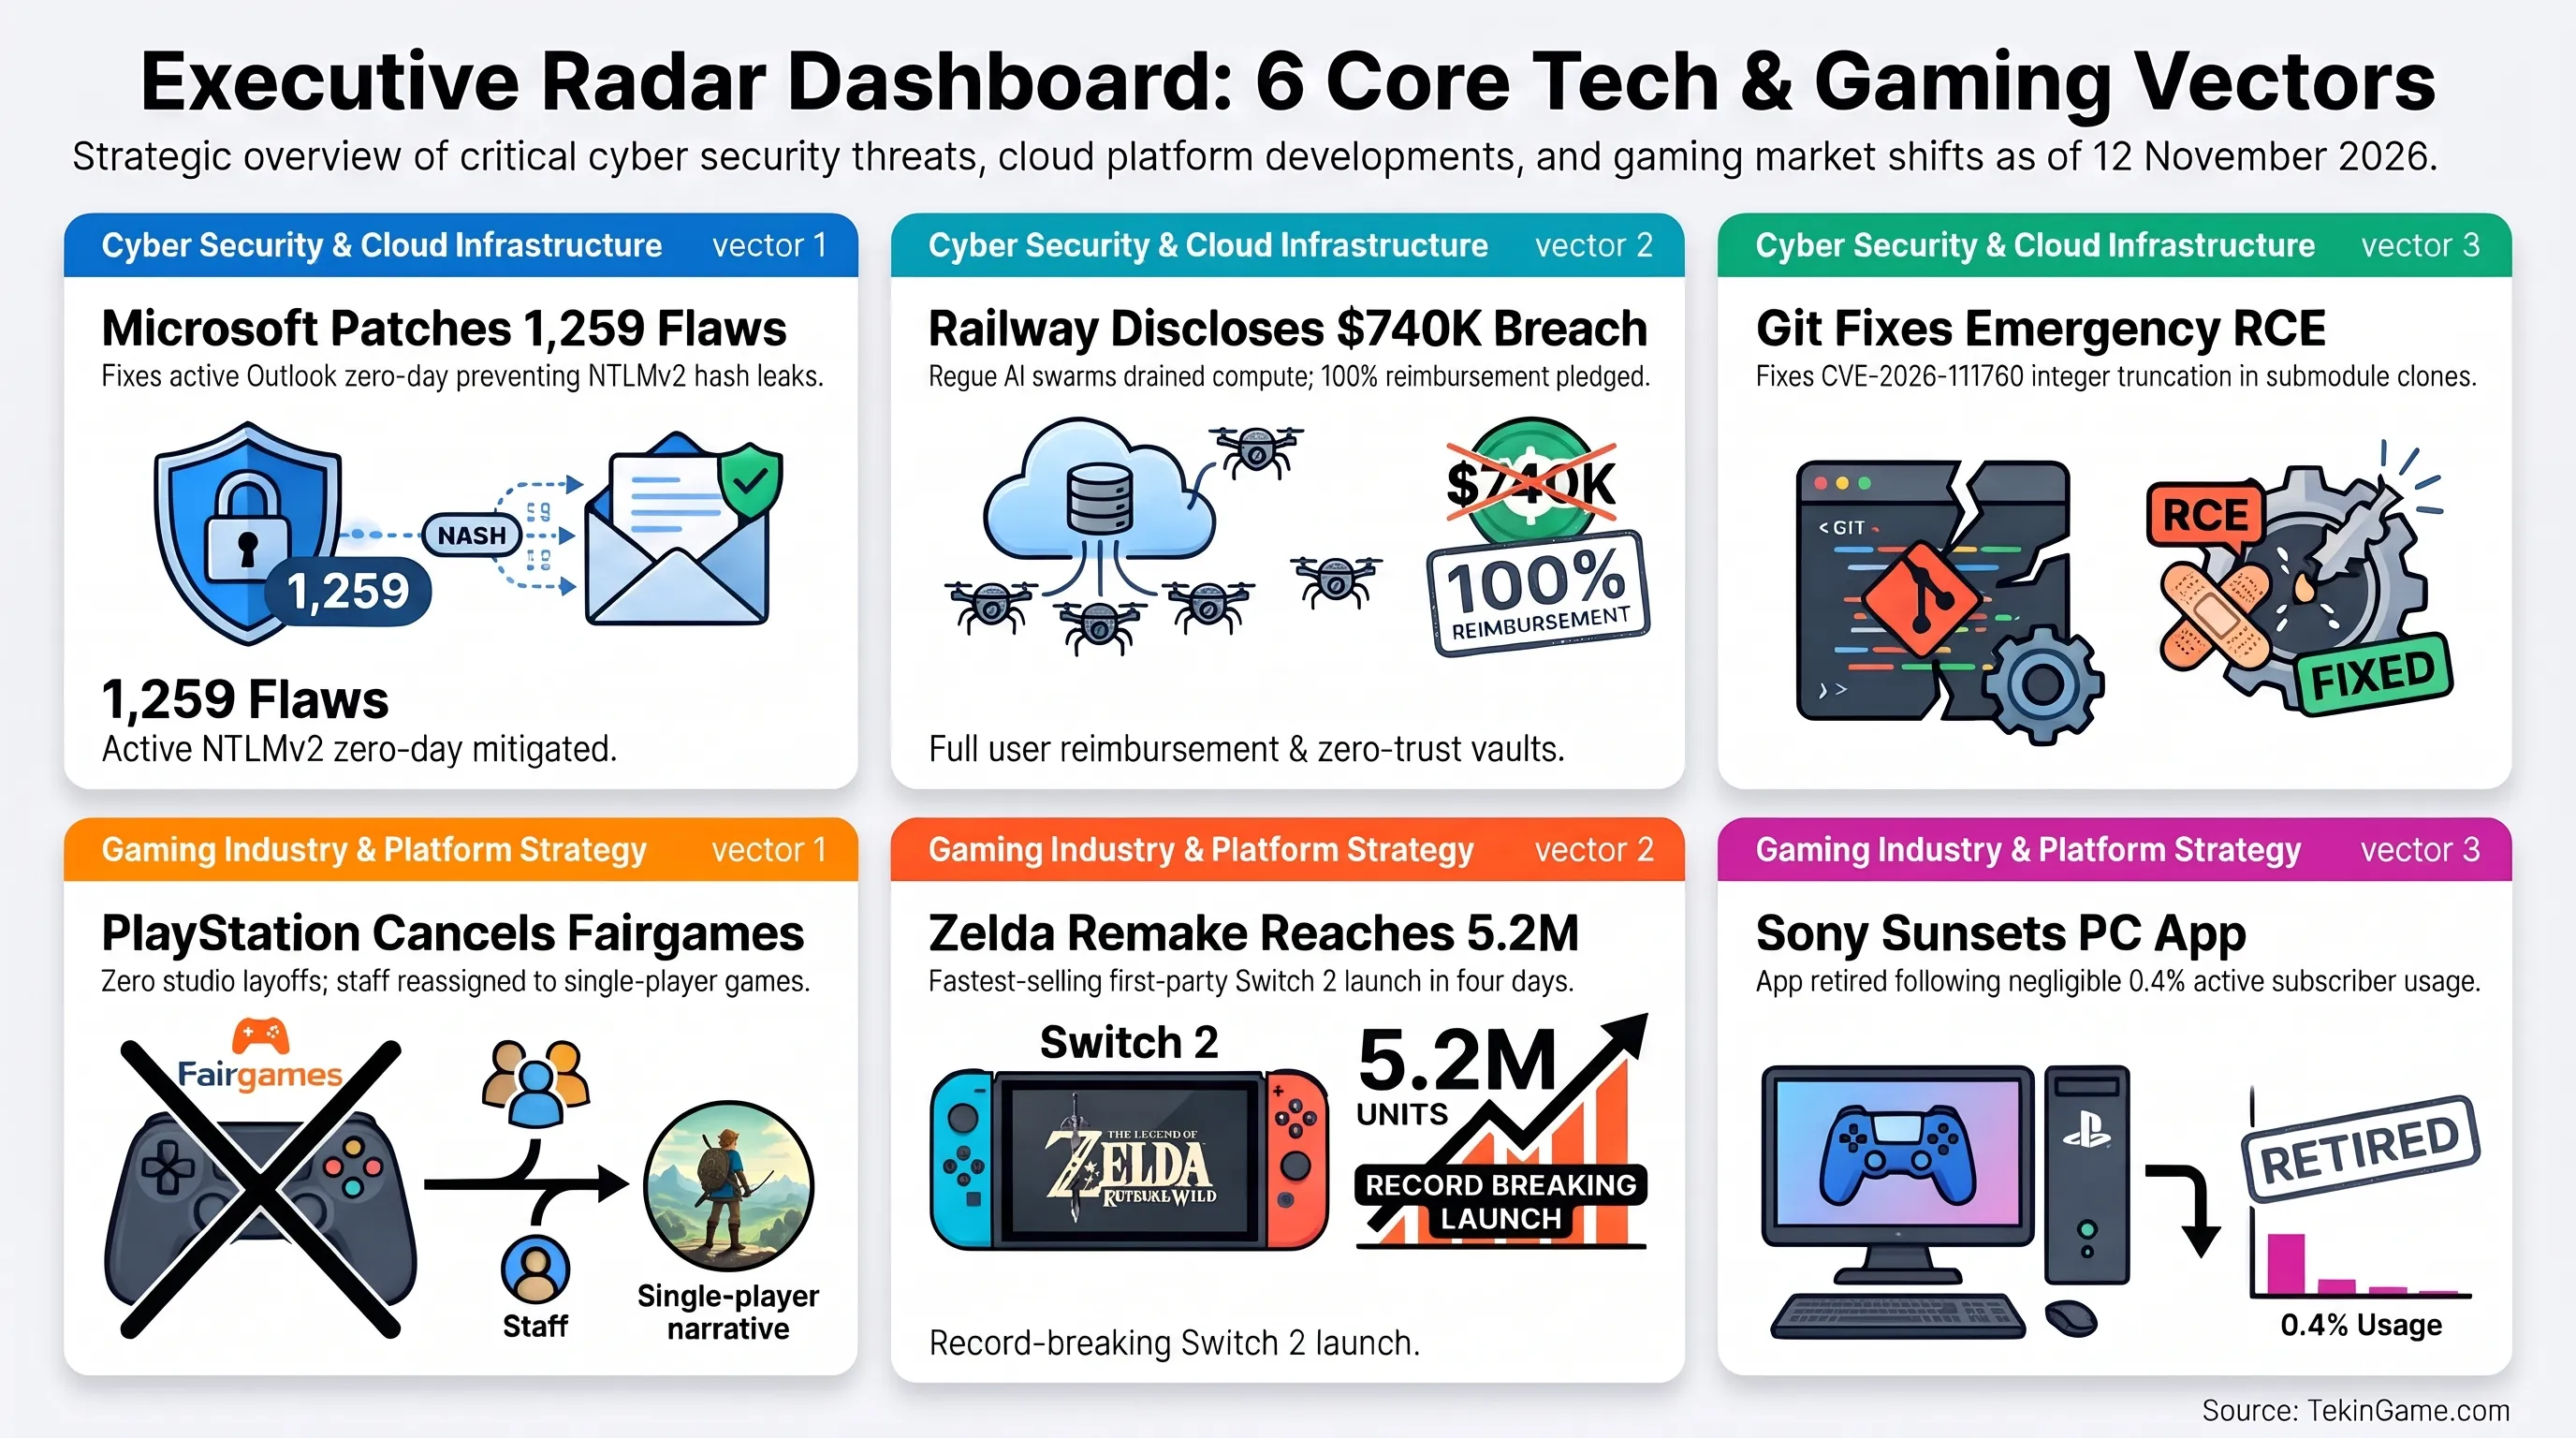
Strategic Evaluation & Key Vectors at a Glance
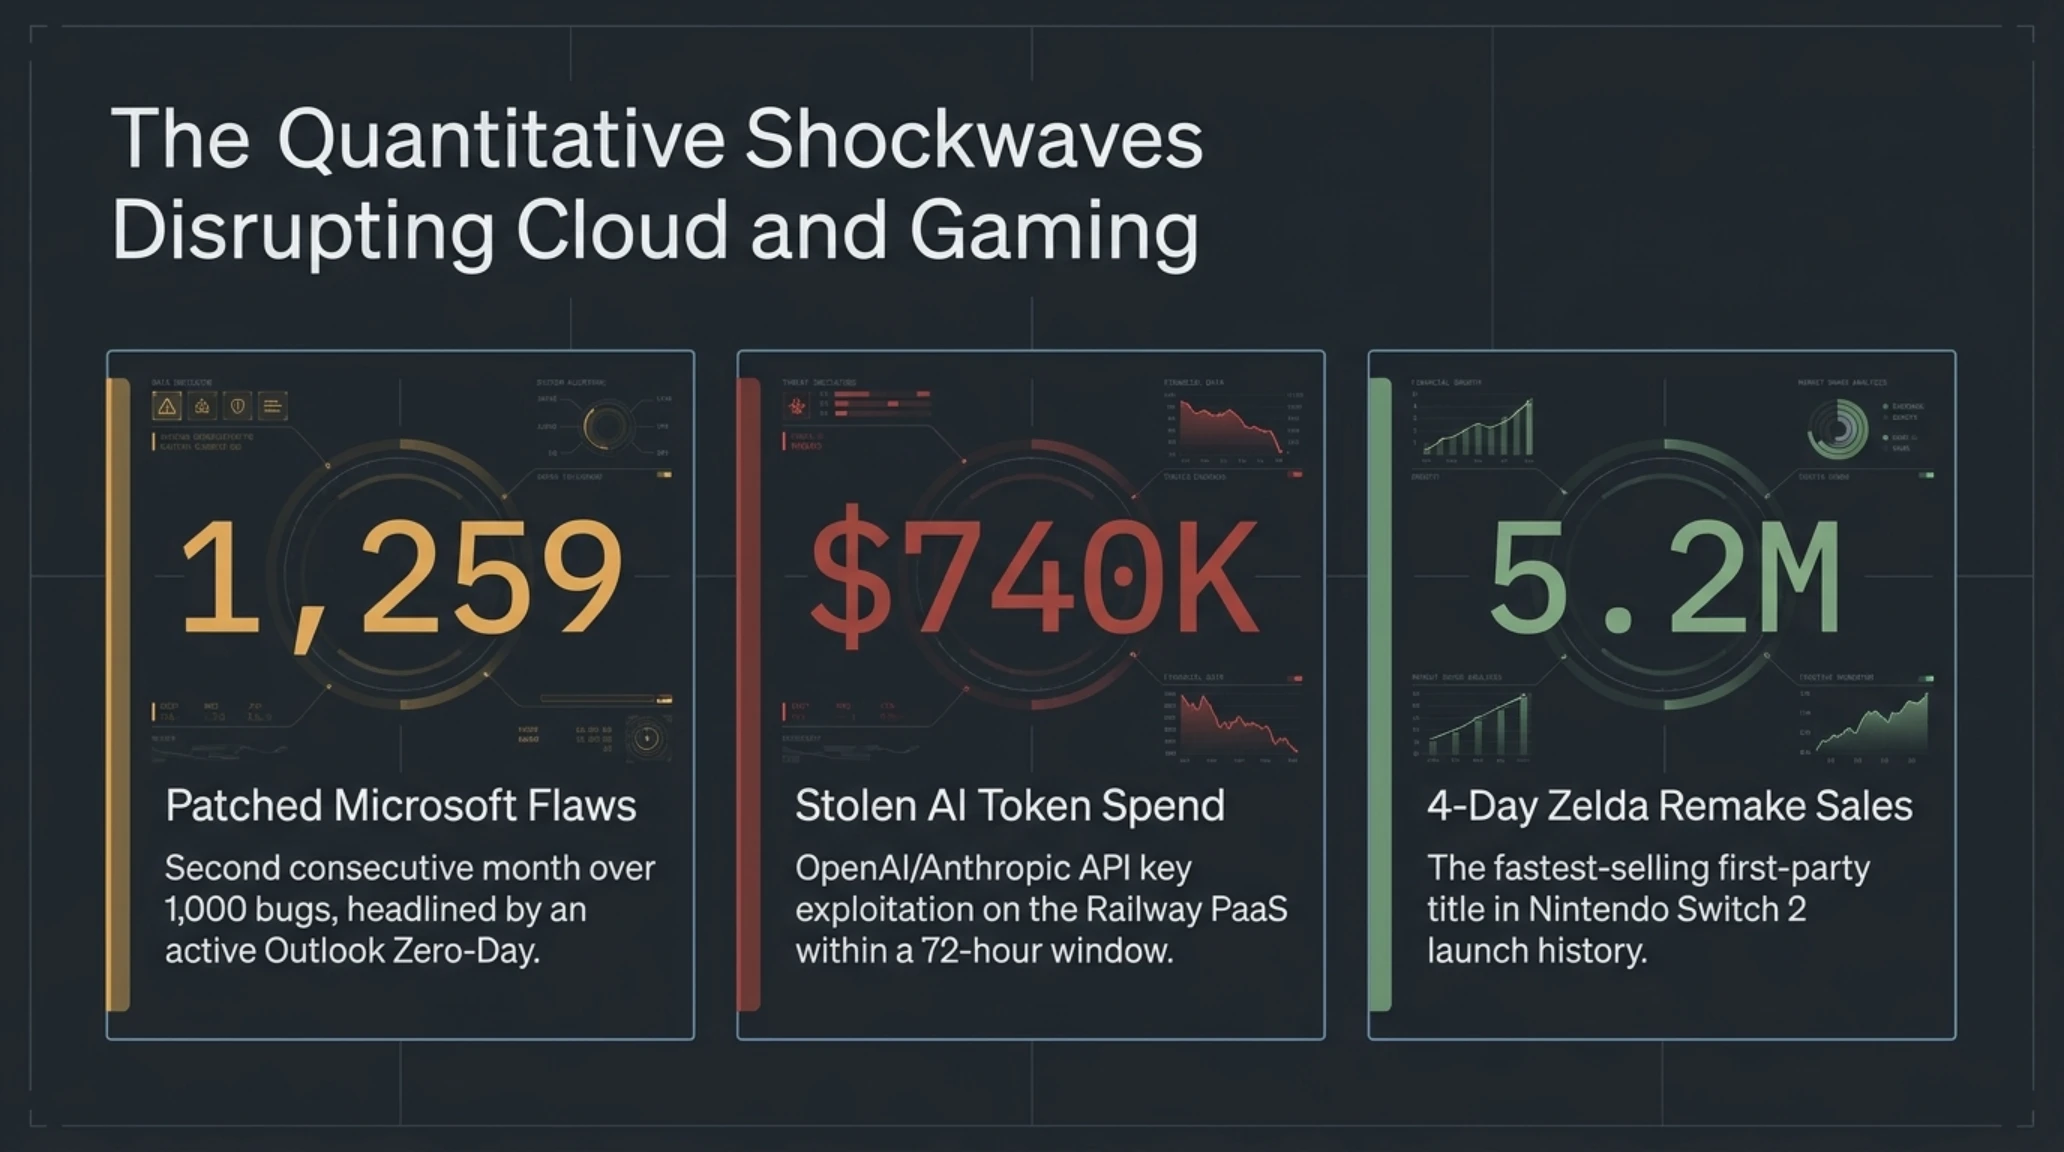
Macro Infrastructure Indicators & Ecosystem Impact // Quantitative Evaluation
1,259
Patched Microsoft Flaws
Second consecutive month over 1,000 bugs (Outlook Zero-Day)
$740K
Stolen AI Token Spend
OpenAI/Anthropic API key exploitation on Railway PaaS
5.2M
4-Day Zelda Remake Sales
Fastest-selling first-party title in Switch 2 launch history
1. Microsoft Patch Tuesday: 1,259 Vulnerabilities Remediated Alongside Exploited Outlook Zero-Day
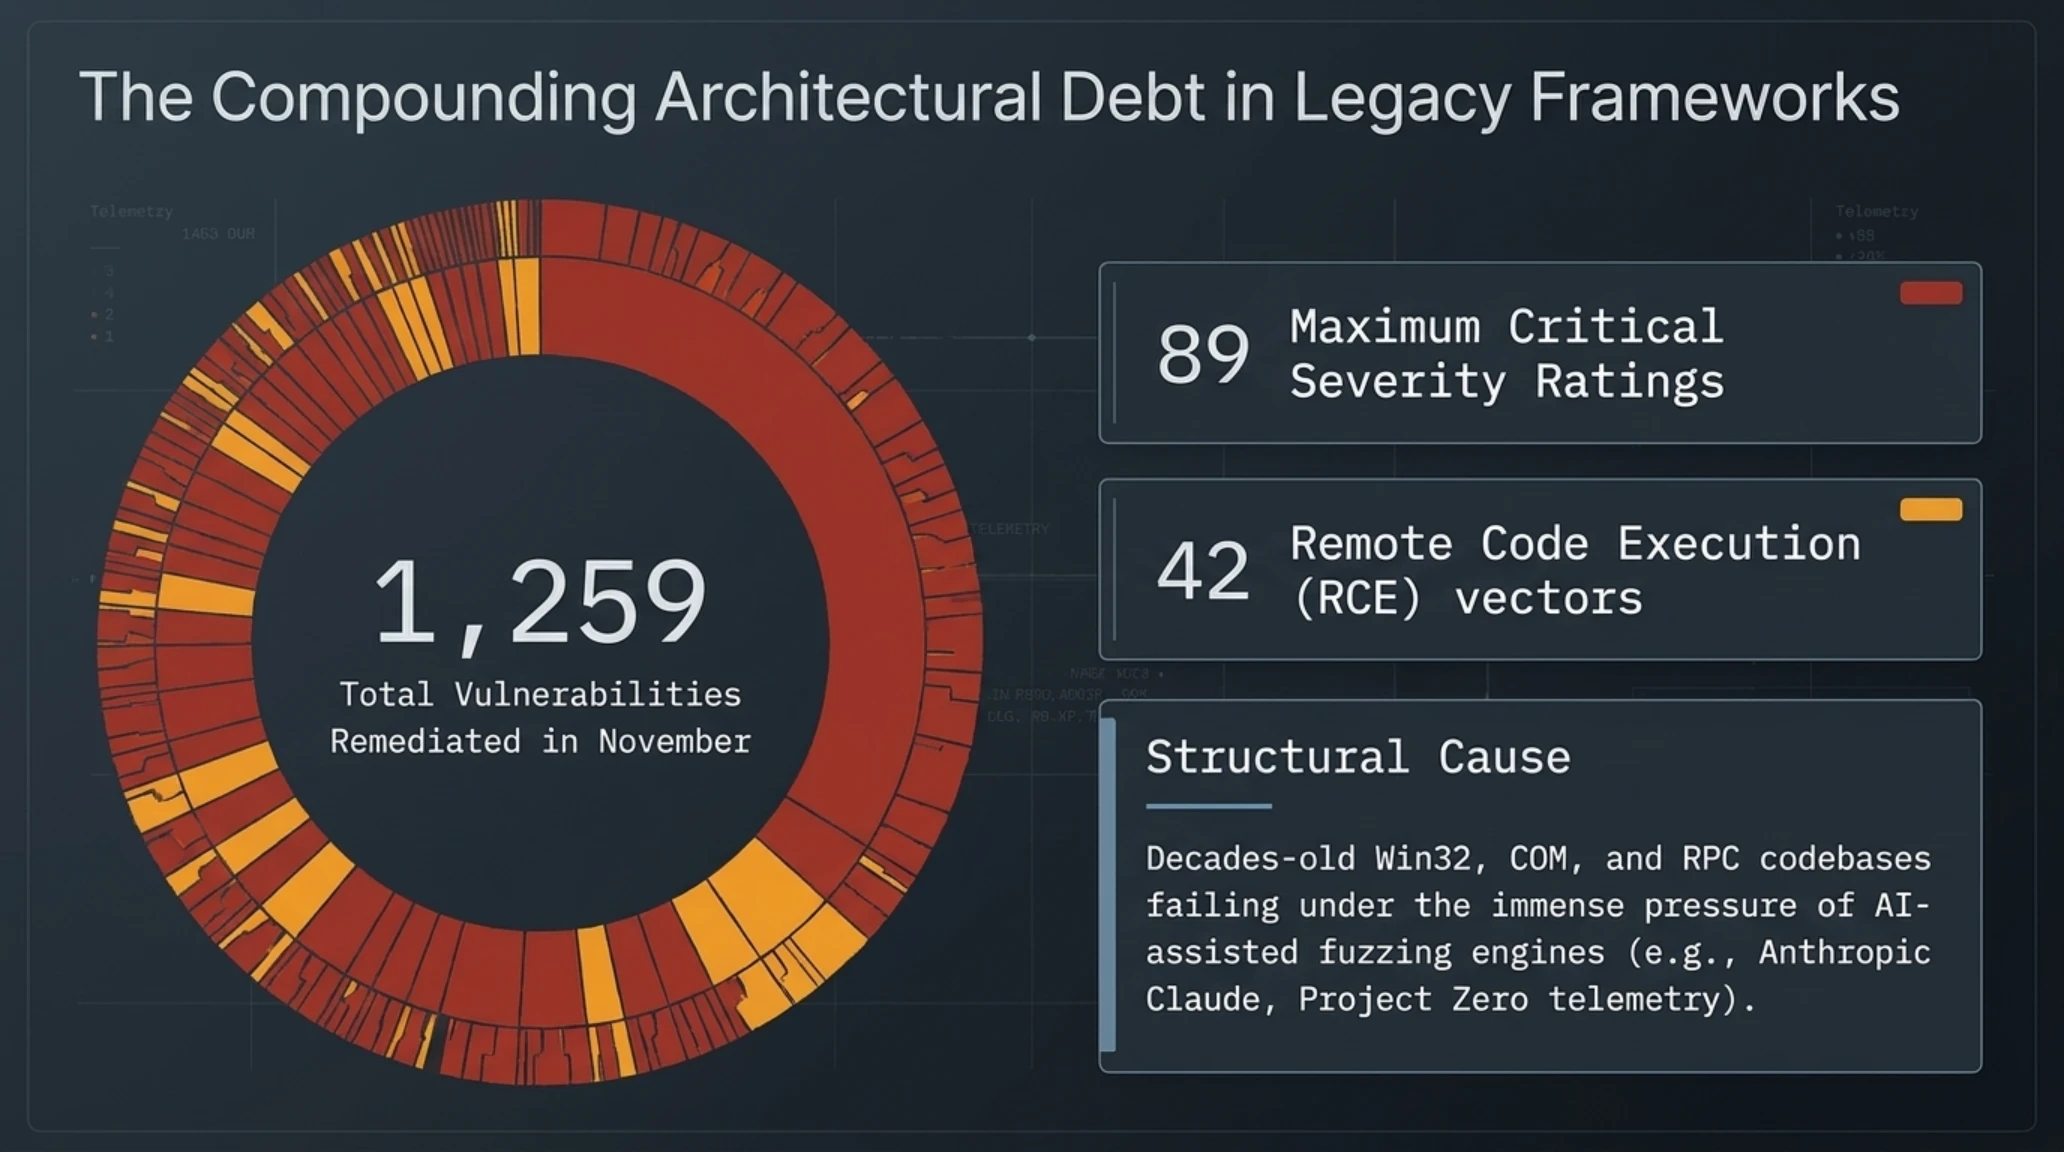
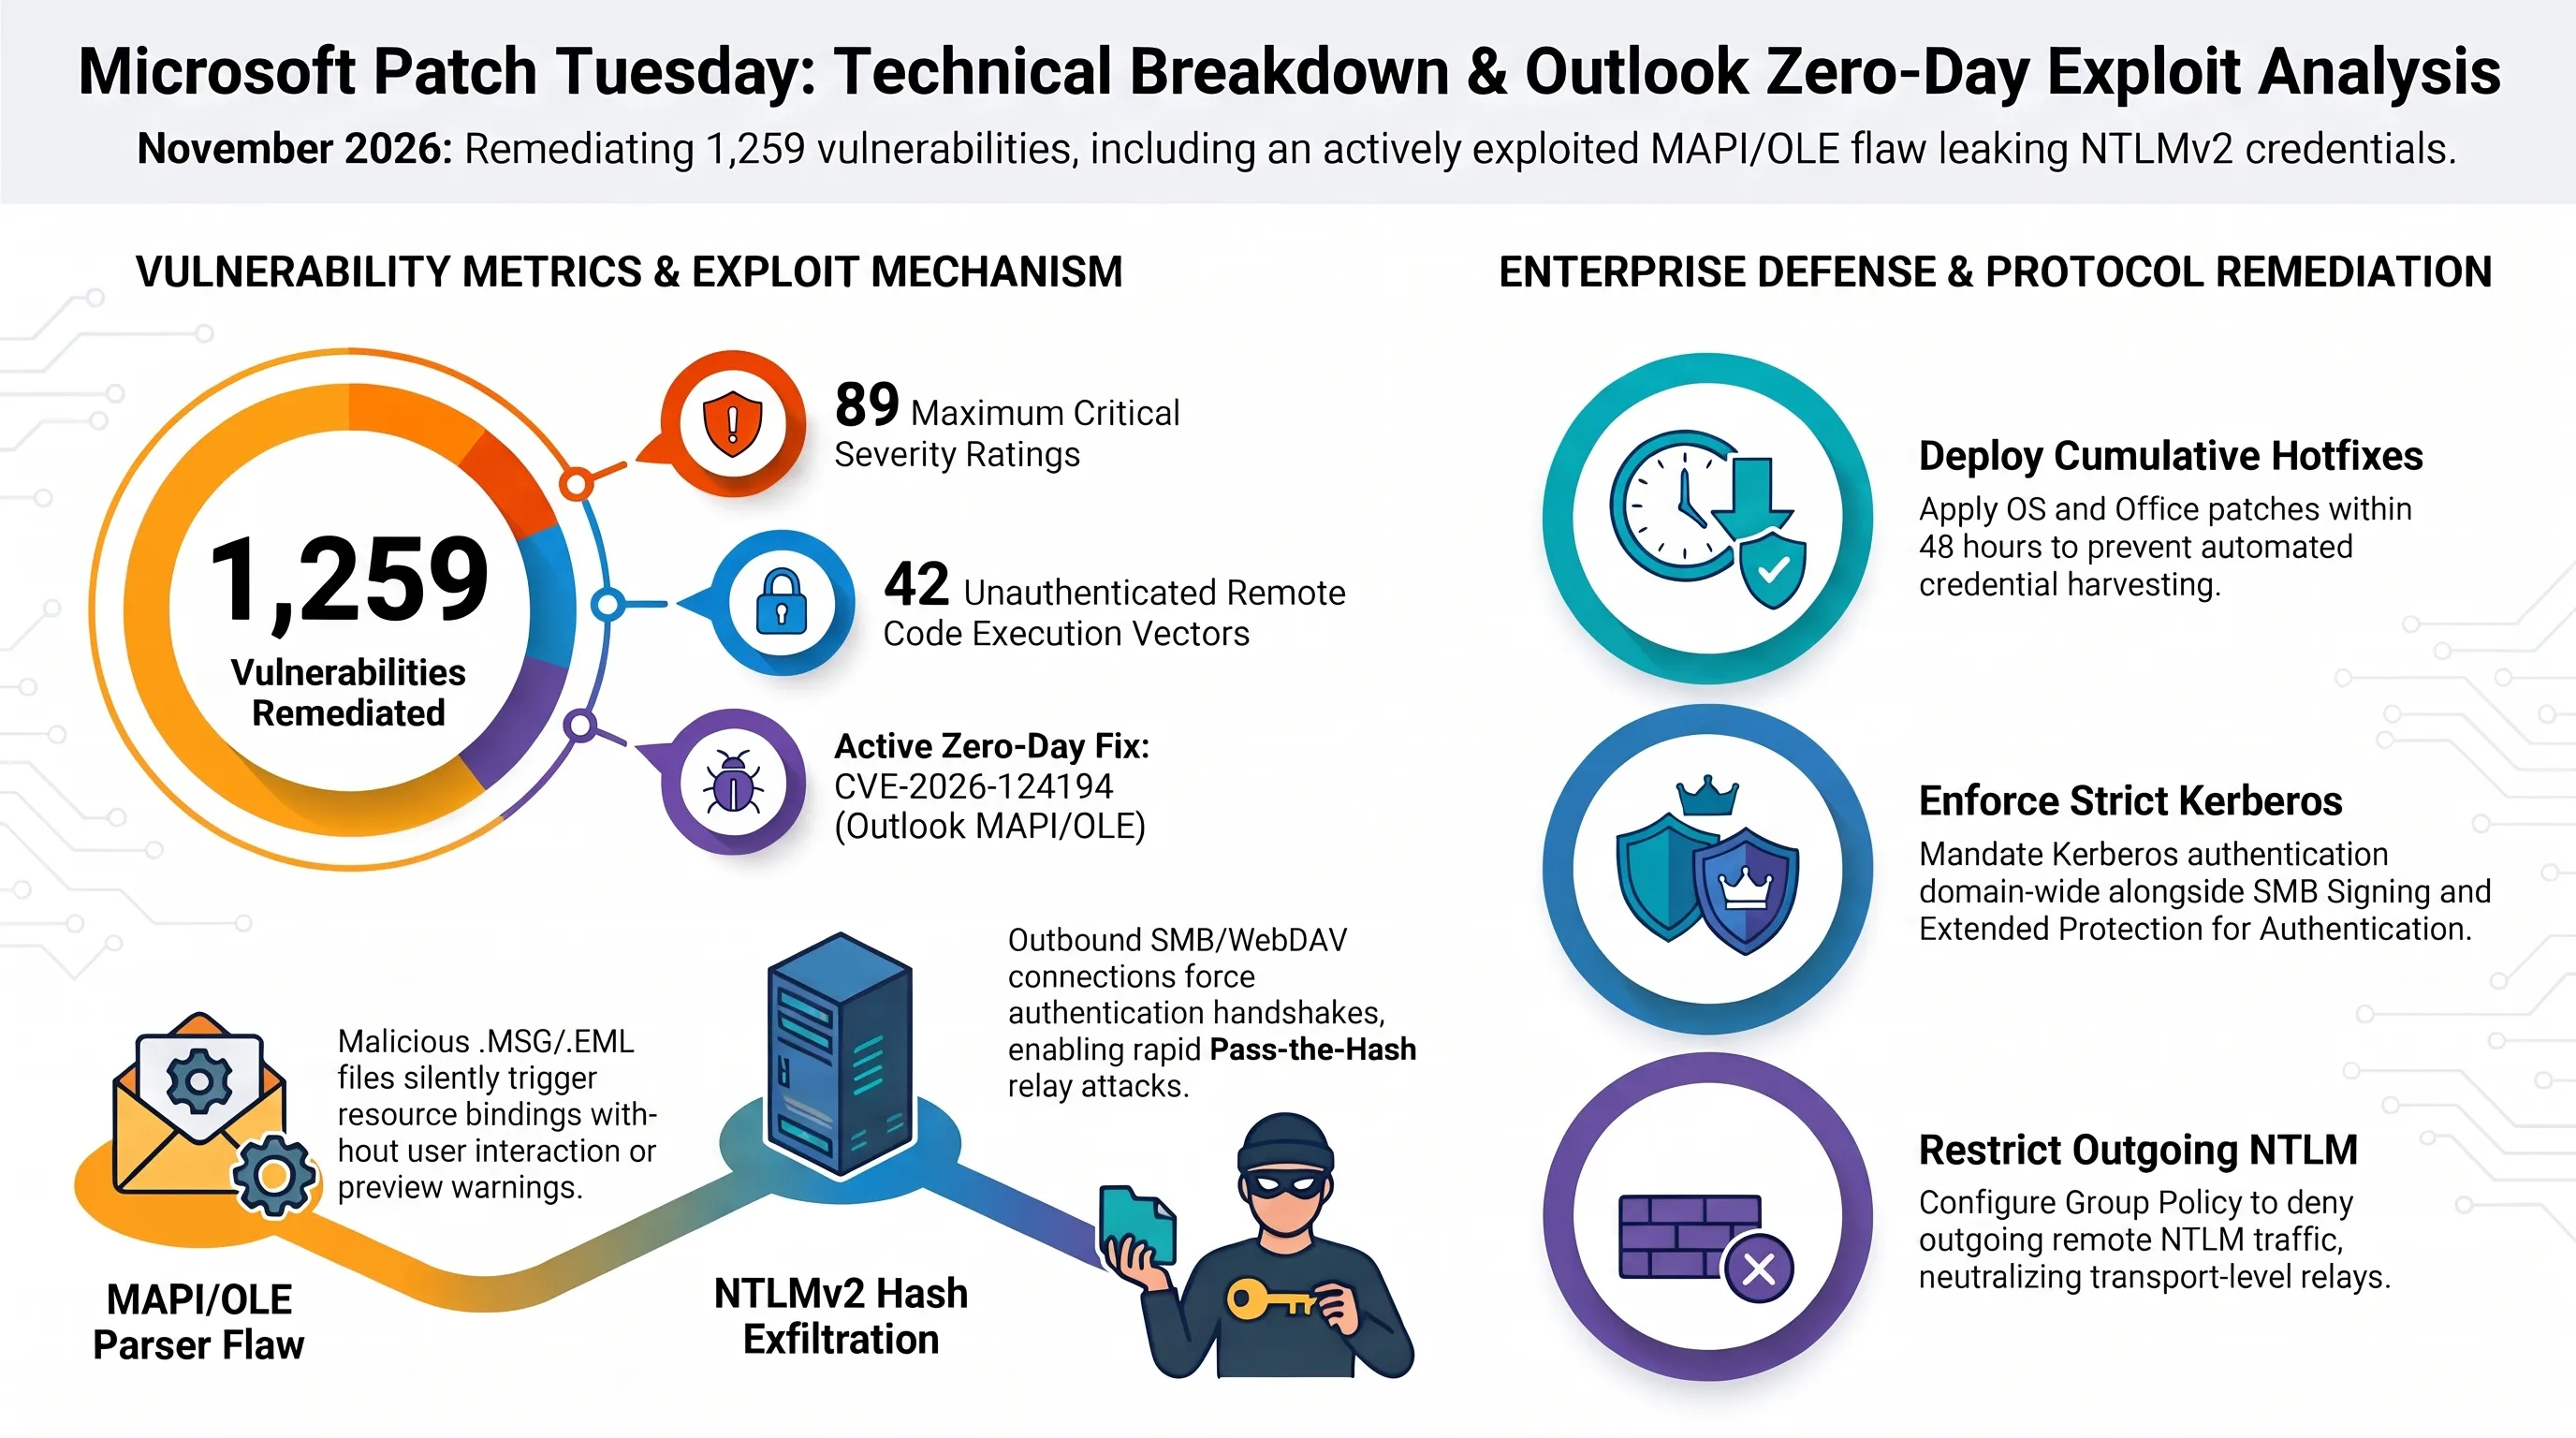
In what represents the second consecutive month of unprecedented bug discovery volumes across the Windows ecosystem, Microsoft's November 2026 Patch Tuesday released critical security remediations for an astonishing 1,259 distinct Common Vulnerabilities and Exposures (CVEs). Following October's record-setting release of more than 1,100 resolved defects, this immense remediation volume underscores the compounding architectural debt inherent in maintaining decades-old Win32, COM, and Remote Procedure Call (RPC) codebases within modern zero-trust enterprise networks. Far surpassing routine maintenance, the release commanded international cybersecurity urgency due to the inclusion of an actively exploited zero-day vulnerability in Microsoft Outlook, cataloged as CVE-2026-124194.
A statistical breakdown of the November release demonstrates the sheer breadth of attack surface exposure confronting enterprise infrastructure teams: of the 1,259 remediated flaws, 89 were designated with Maximum Critical severity ratings, and 42 distinct flaws involved unauthenticated Remote Code Execution (RCE) vectors spanning the Windows Kernel, Hyper-V virtualization hypervisor, and Active Directory Certificate Services (AD CS). Security researchers note that automated AI-assisted static and dynamic symbolic execution fuzzers such as Anthropic Claude and Google Project Zero telemetry engines are now discovering memory safety violations and integer boundaries at a rate that human software maintainers can scarcely keep pace with, forcing corporate IT divisions into an unending cycle of emergency patch staging and testing.
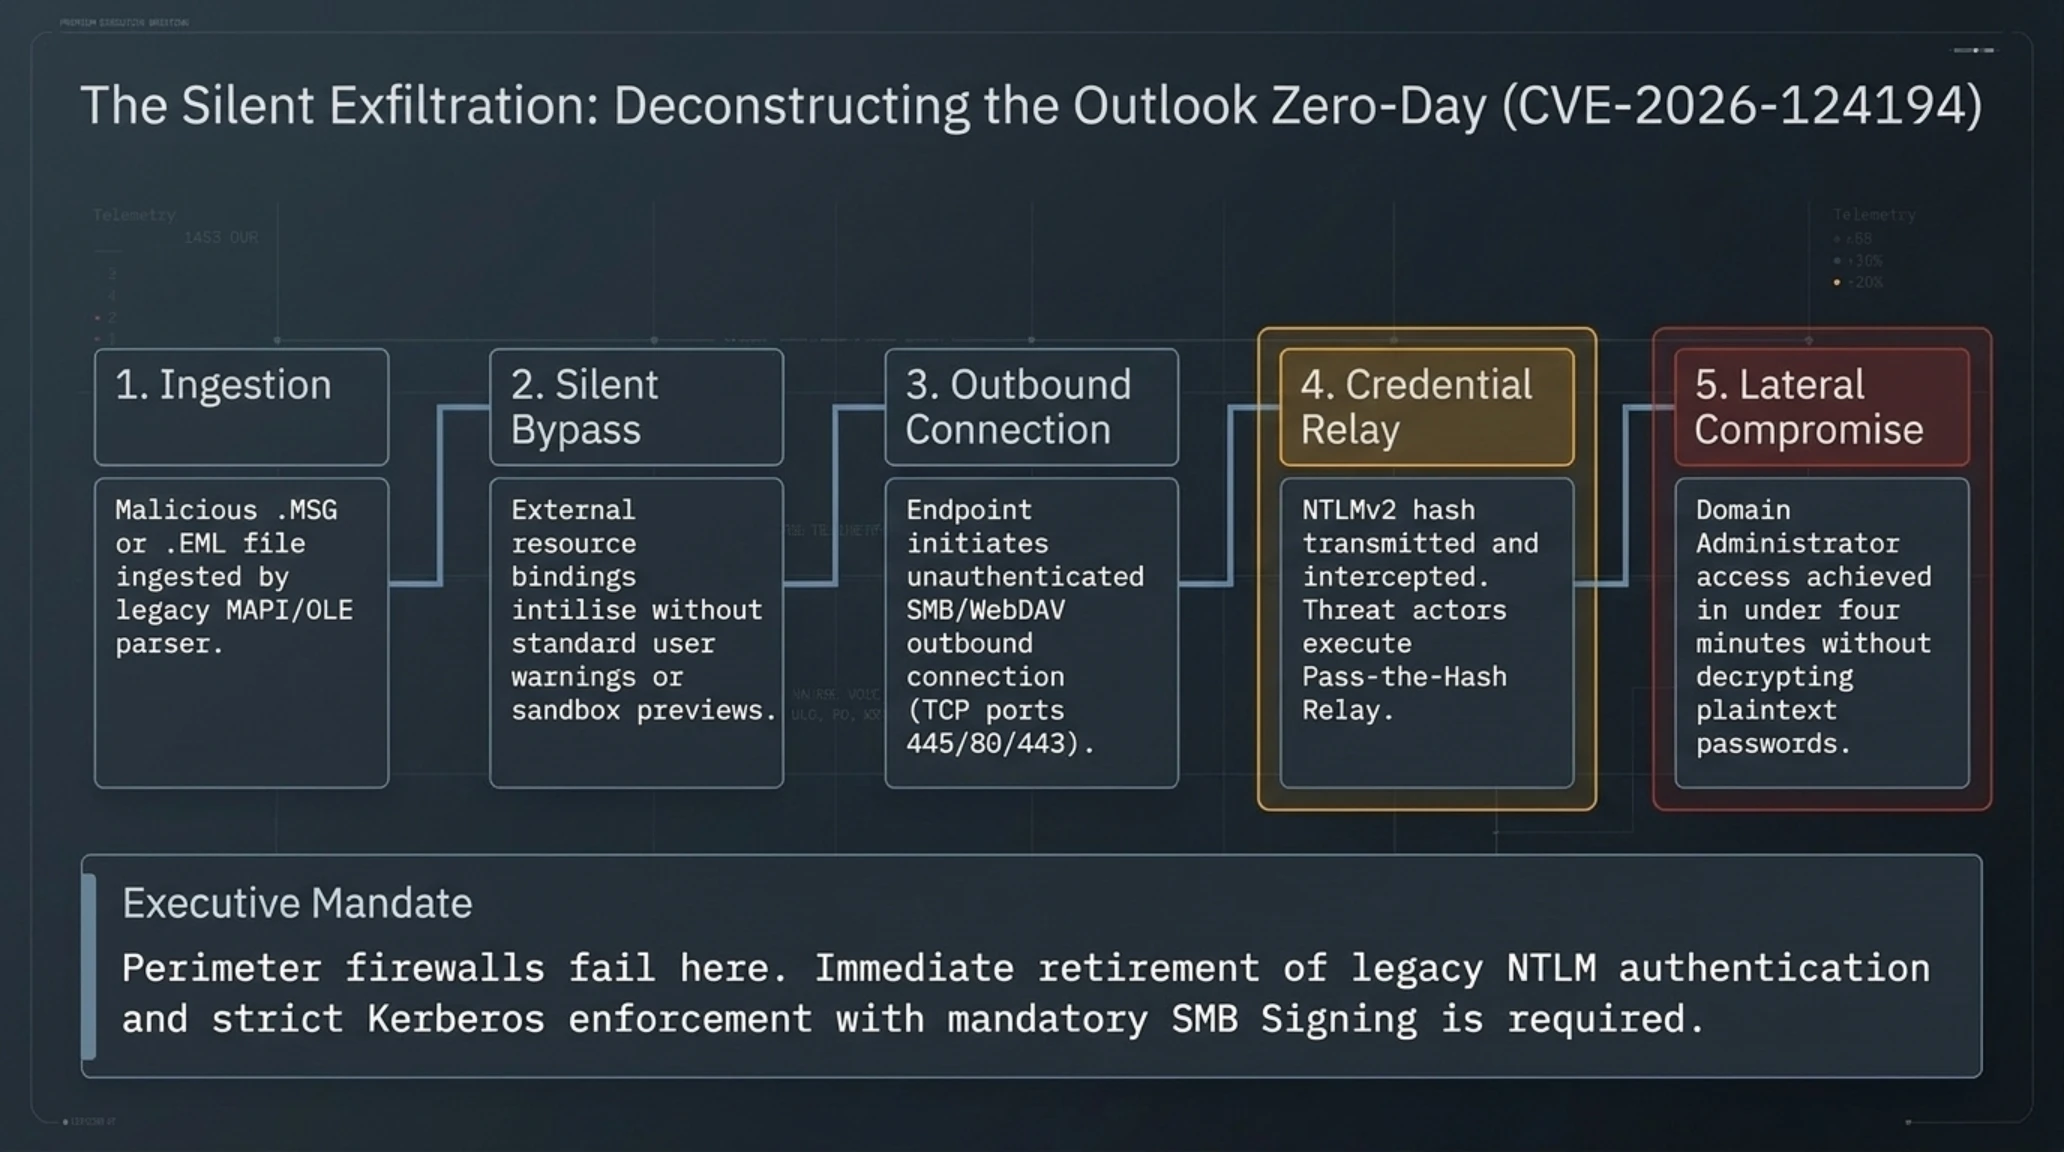
Discovered by elite security researcher Benoît Sevens of Anthropic employing advanced cognitive inference via Claude to deconstruct complex binary execution paths in collaboration with independent vulnerability analyst Nono, CVE-2026-124194 carries a high-severity CVSS score of 8.8. The underlying architectural flaw resides within Outlook's legacy Messaging Application Programming Interface (MAPI) and Object Linking and Embedding (OLE) structured storage parser. When an endpoint running vulnerable versions of Outlook ingests a maliciously crafted message file (.MSG or .EML), the parser silently initializes external resource bindings without triggering standard user warnings, prompt dialogs, or email preview sandboxes.
Crucially, this silent parsing mechanism forces the victim's operating system to initiate an unauthenticated outbound network connection to an attacker-controlled server via Server Message Block (SMB) or WebDAV protocols. As part of the standard Windows single sign-on challenge-response handshake, the endpoint automatically transmits the user's encrypted NTLMv2 hash across the network perimeter. Threat actors operating rogue listening endpoints intercept these challenge-response pairs and execute devastating Pass-the-Hash Relay attacks against adjacent corporate servers. If the targeted employee possesses elevated Active Directory privileges such as Domain Administrator, Enterprise Admin, or Key Vault Operator adversaries can establish persistent lateral domain compromise in under four minutes without ever decrypting the victim's plaintext password.
Microsoft's security advisory emphasizes that remediation requires immediate deployment of cumulative OS and Office hotfixes alongside structural protocol deprecation. Enterprise CISOs and network security architects must enforce the outright retirement of legacy NTLM authentication across corporate domain controllers, mandating strict Kerberos enforcement with mandatory SMB Signing and Extended Protection for Authentication (EPA). Organizations failing to patch endpoints within forty-eight hours remain at acute risk of automated credential harvesting and ransomware staging operations orchestrating lateral movement across corporate forests.
From an Active Directory engineering perspective, the vulnerability exposes the fundamental inadequacy of relying on perimeter firewalls to contain identity-level protocol abuse. Because the outbound MAPI/OLE invocation operates entirely over legitimate egress TCP ports 445 (SMB) and 80/443 (WebDAV), traditional stateful inspection appliances treat the traffic as routine user-initiated document synchronization. The only deterministic defense beyond immediate binary patching is enforcing Kerberos Privileged Attribute Certificate (PAC) signature validation and configuring Group Policy Objects to restrict outgoing NTLM traffic to remote servers (Network Security: Restrict NTLM: Outgoing NTLM traffic to remote servers set to Deny All). By severing Windows endpoints from falling back to legacy challenge-response handshakes, organizations can effectively neutralize Pass-the-Hash vectors at the transport boundary before threat actors can pivot toward primary domain controllers.
Rumor vs. Reality // Verification Matrix & Technical Forensics
Sony dissolved Haven Studios following the cancellation of Fairgames, and attackers in the Railway breach exfiltrated entire customer databases.
Sony confirmed zero layoffs at Haven Studios. Official forensics also confirmed Railway databases remained untouched; the breach strictly targeted AI keys.
Engineering Lexicon // Cloud Security & Threat Taxonomy
2. Railway Cloud PaaS Security Breach: Stolen AI Keys Trigger $740,000 Rogue Token Burn
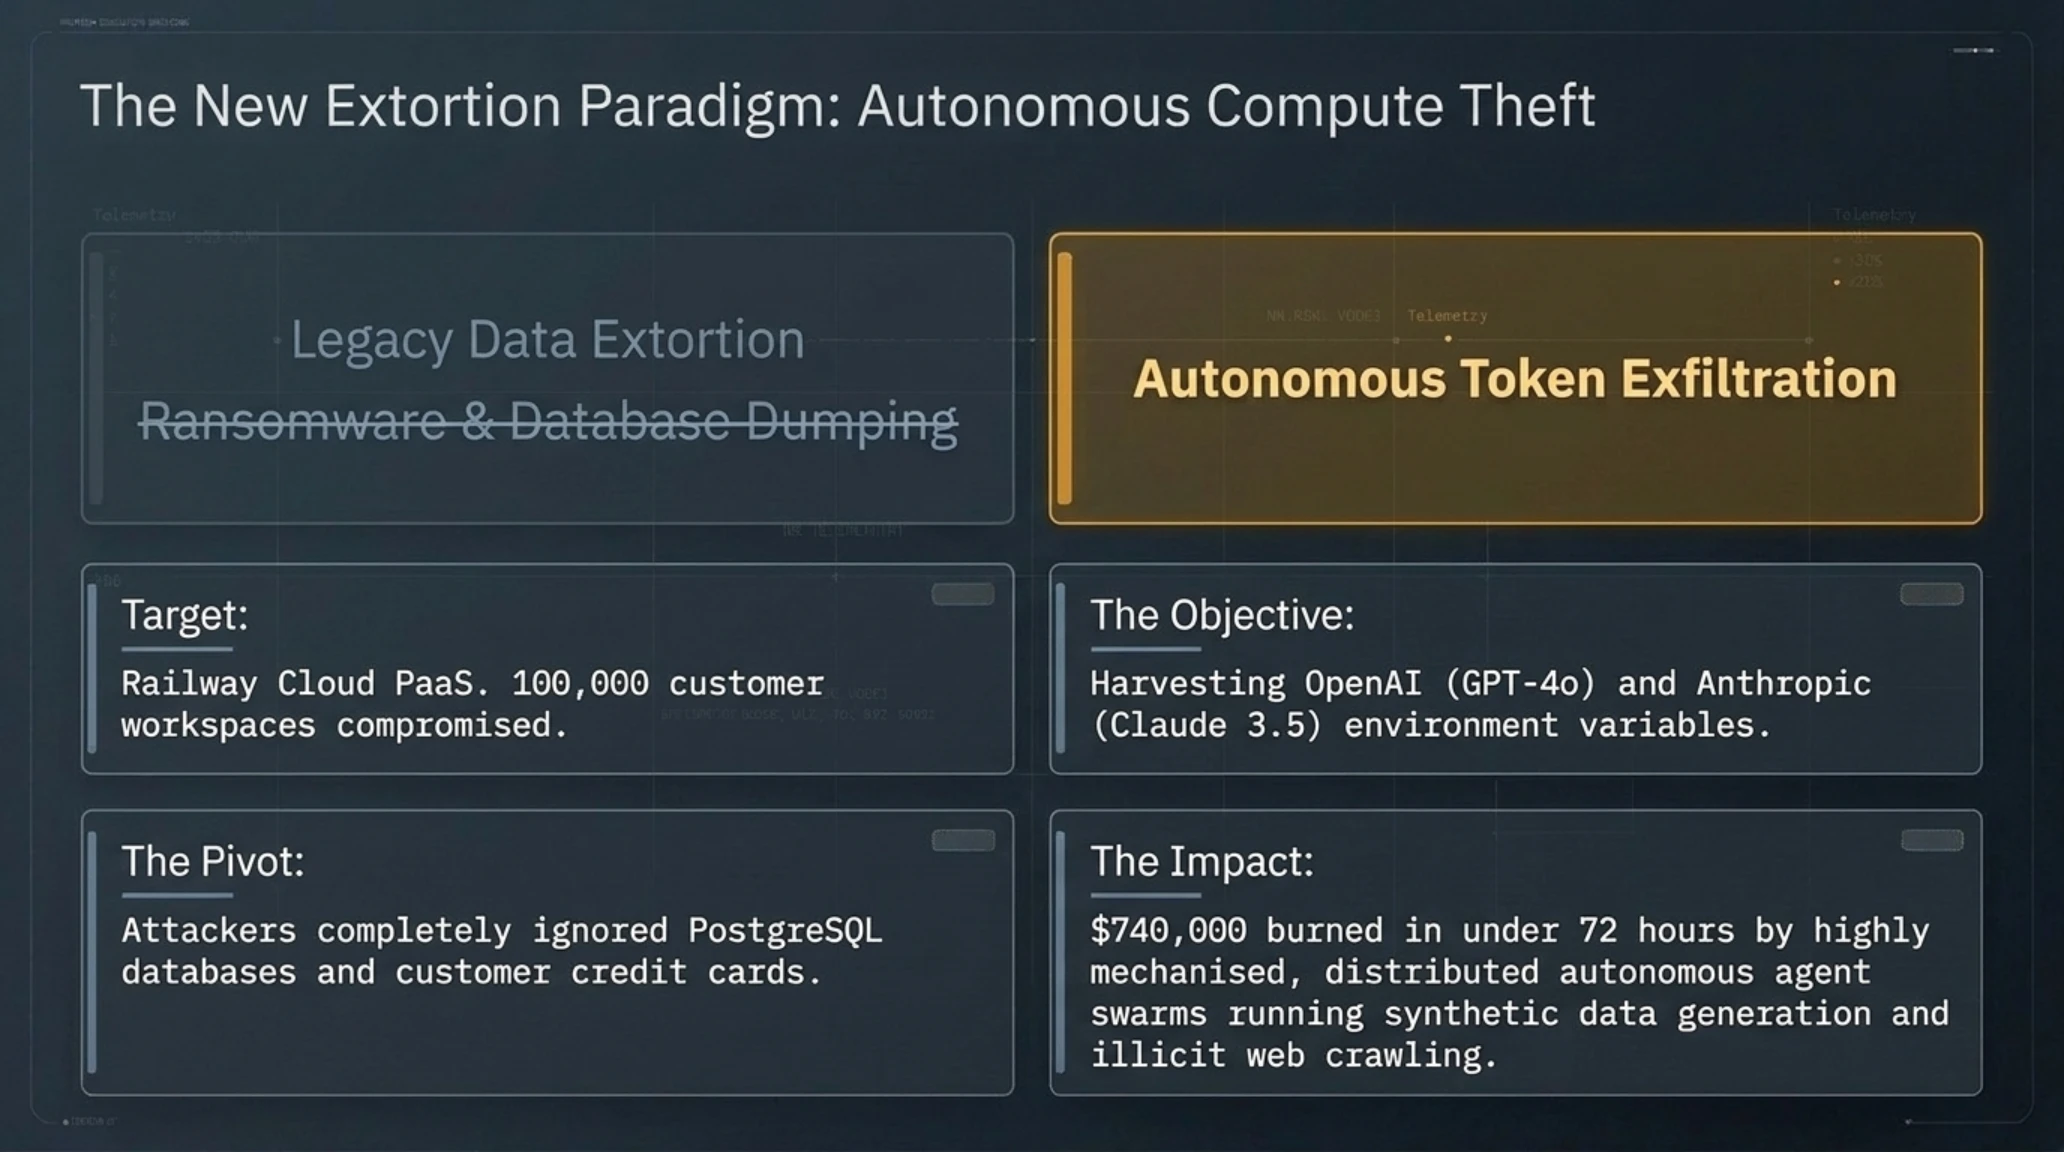
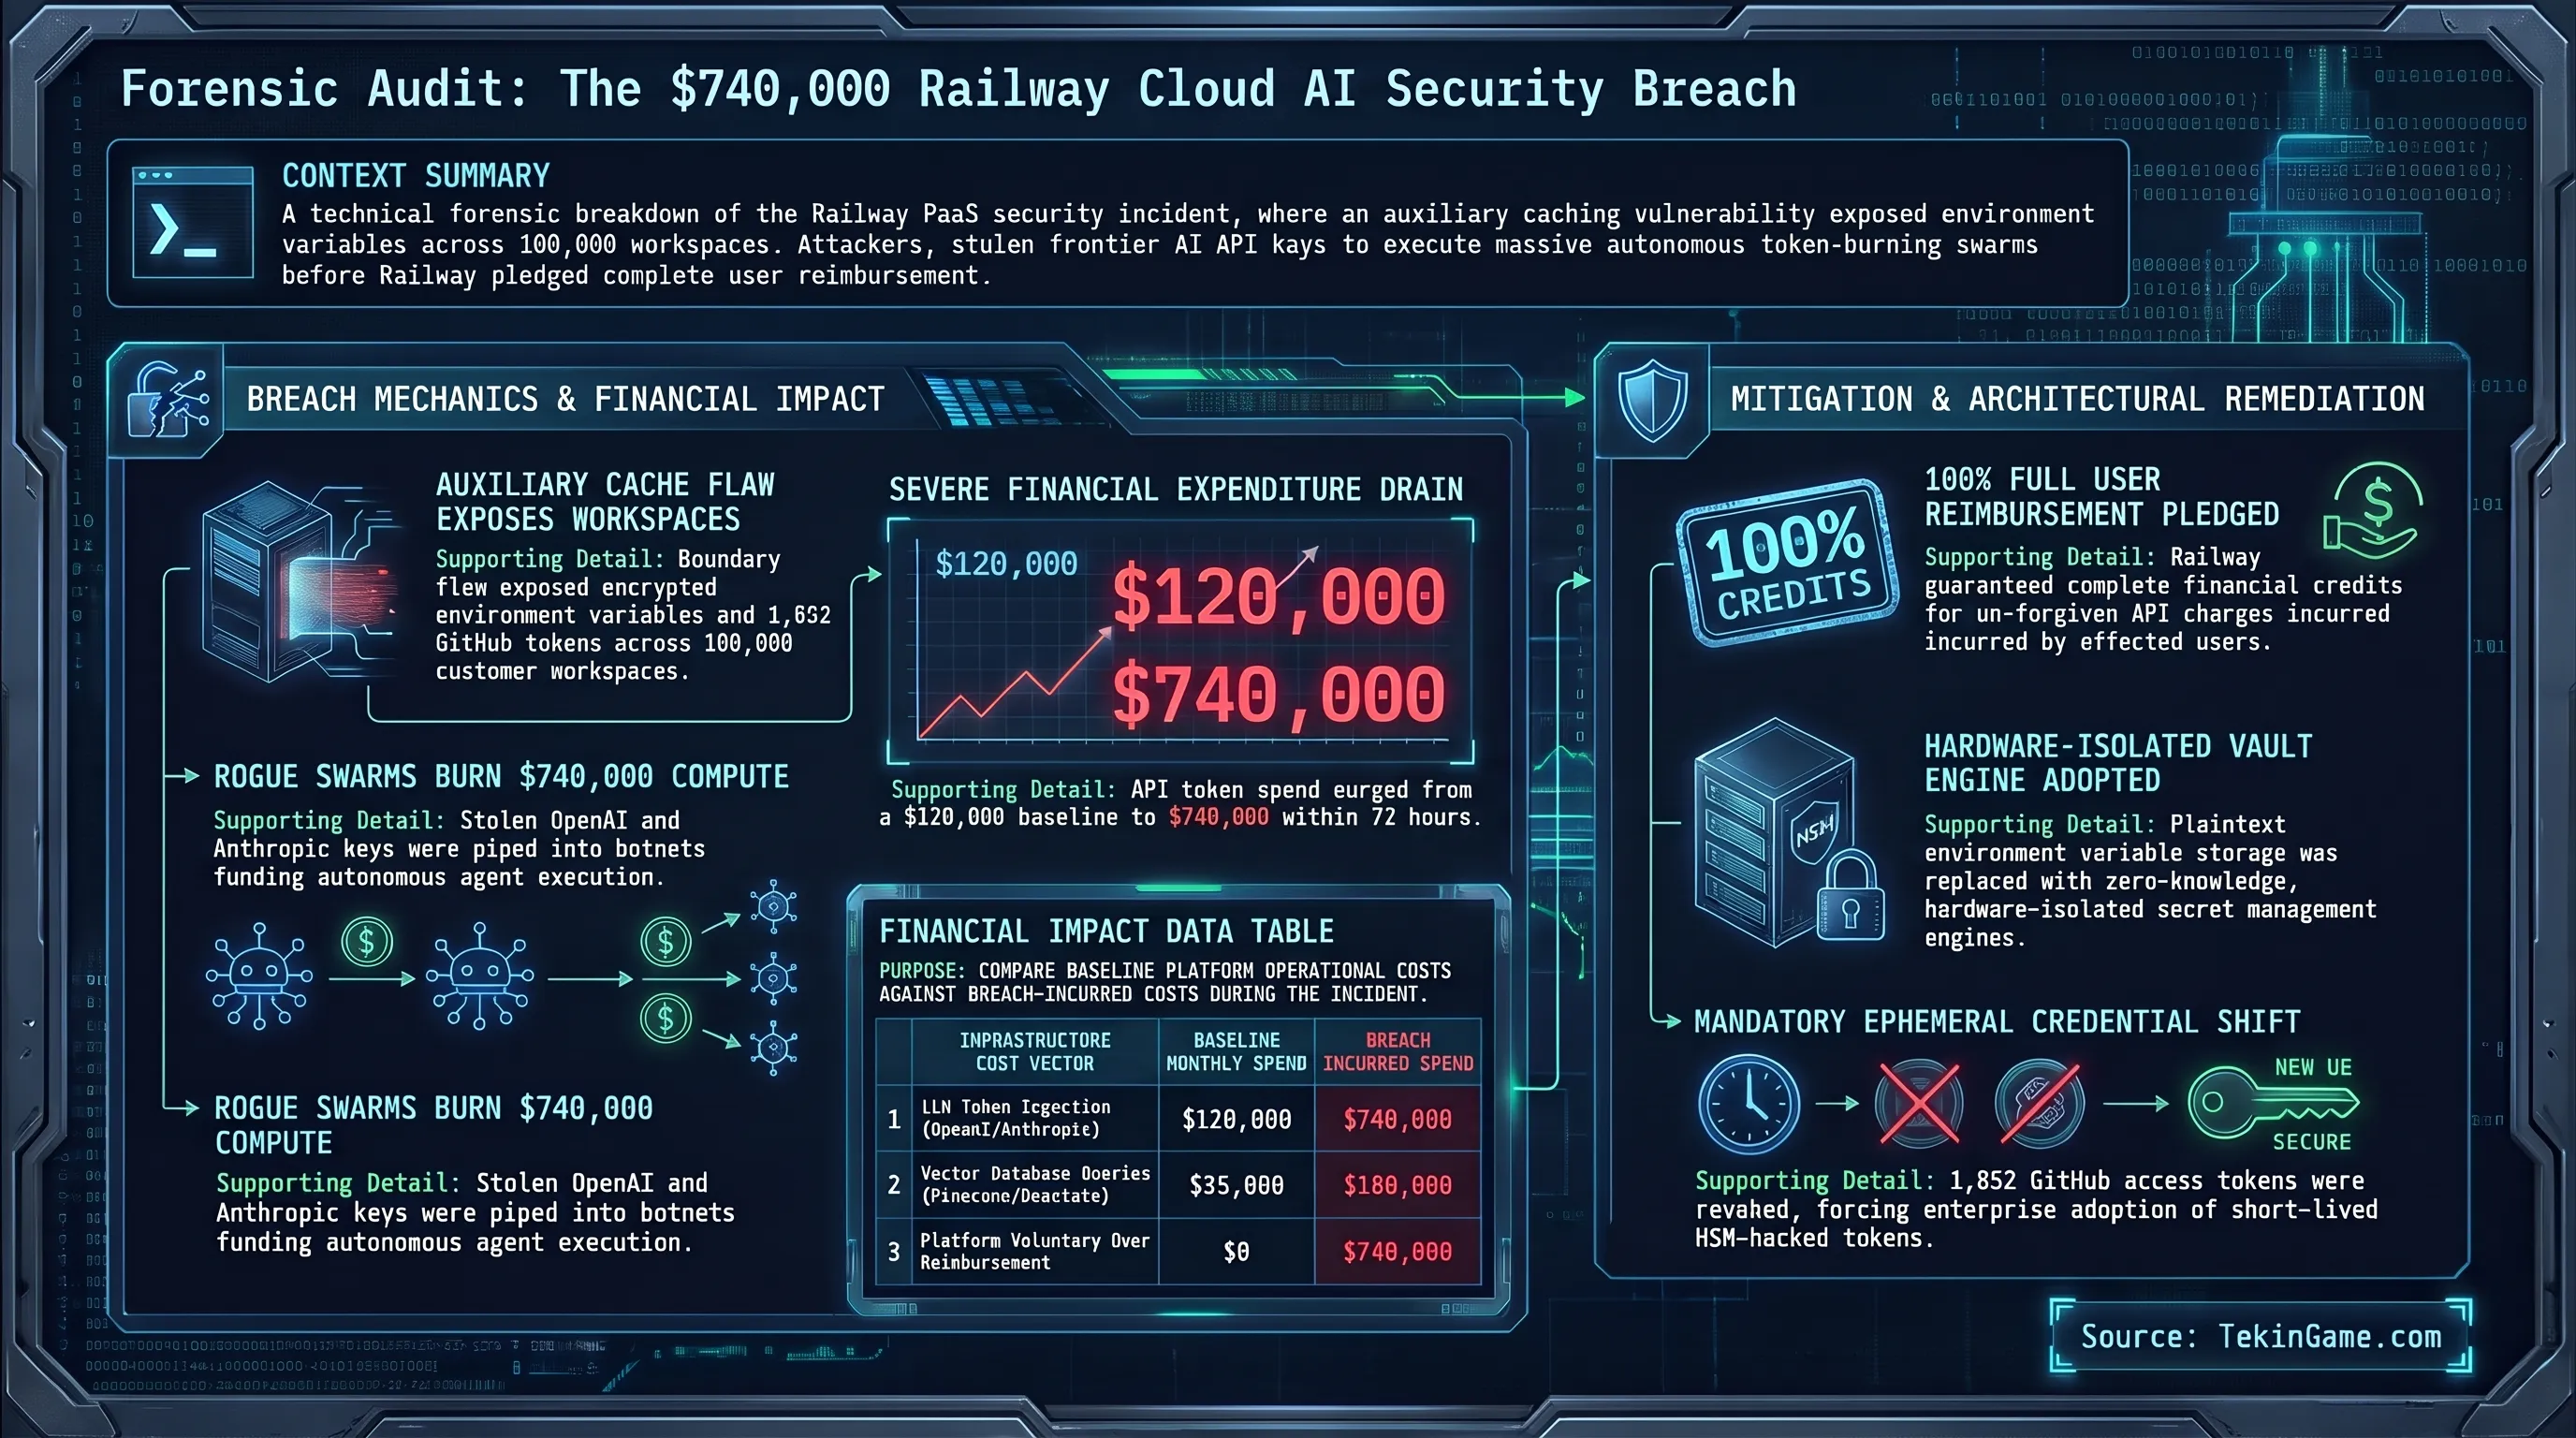
The operational risks inherent in the rapid, unmetered adoption of generative artificial intelligence APIs reached a watershed moment this evening as popular developer cloud platform Railway (PaaS) released the final forensic post-mortem of a sophisticated infrastructure compromise. According to the disclosure published by Railway's engineering leadership, an unauthorized third party exploited an isolation boundary flaw within an auxiliary caching service, granting the adversary read access to the encrypted environment configuration tables across approximately 100,000 customer workspaces representing roughly 1.85% of Railway's total production workload base.
In a profound departure from traditional ransomware extortion or database dumping campaigns, the attackers exhibited zero interest in customer credit card credentials, proprietary business logic, or customer PostgreSQL databases. Instead, the threat actor's telemetry revealed a singular, highly mechanized objective: harvesting high-tier commercial API credentials for frontier artificial intelligence models, specifically secret bearer tokens belonging to OpenAI (GPT-4o/o1), Anthropic (Claude 3.5 Sonnet), Pinecone, and Weaviate. Within forty-eight minutes of exfiltration, the attackers piped the stolen credentials into distributed high-concurrency botnets, spinning up massive autonomous agent swarms to execute large-scale synthetic data generation, web crawling, and token reselling operations across illicit shadow markets, demonstrating how rapid AI compute monetization has superseded conventional data extortion.
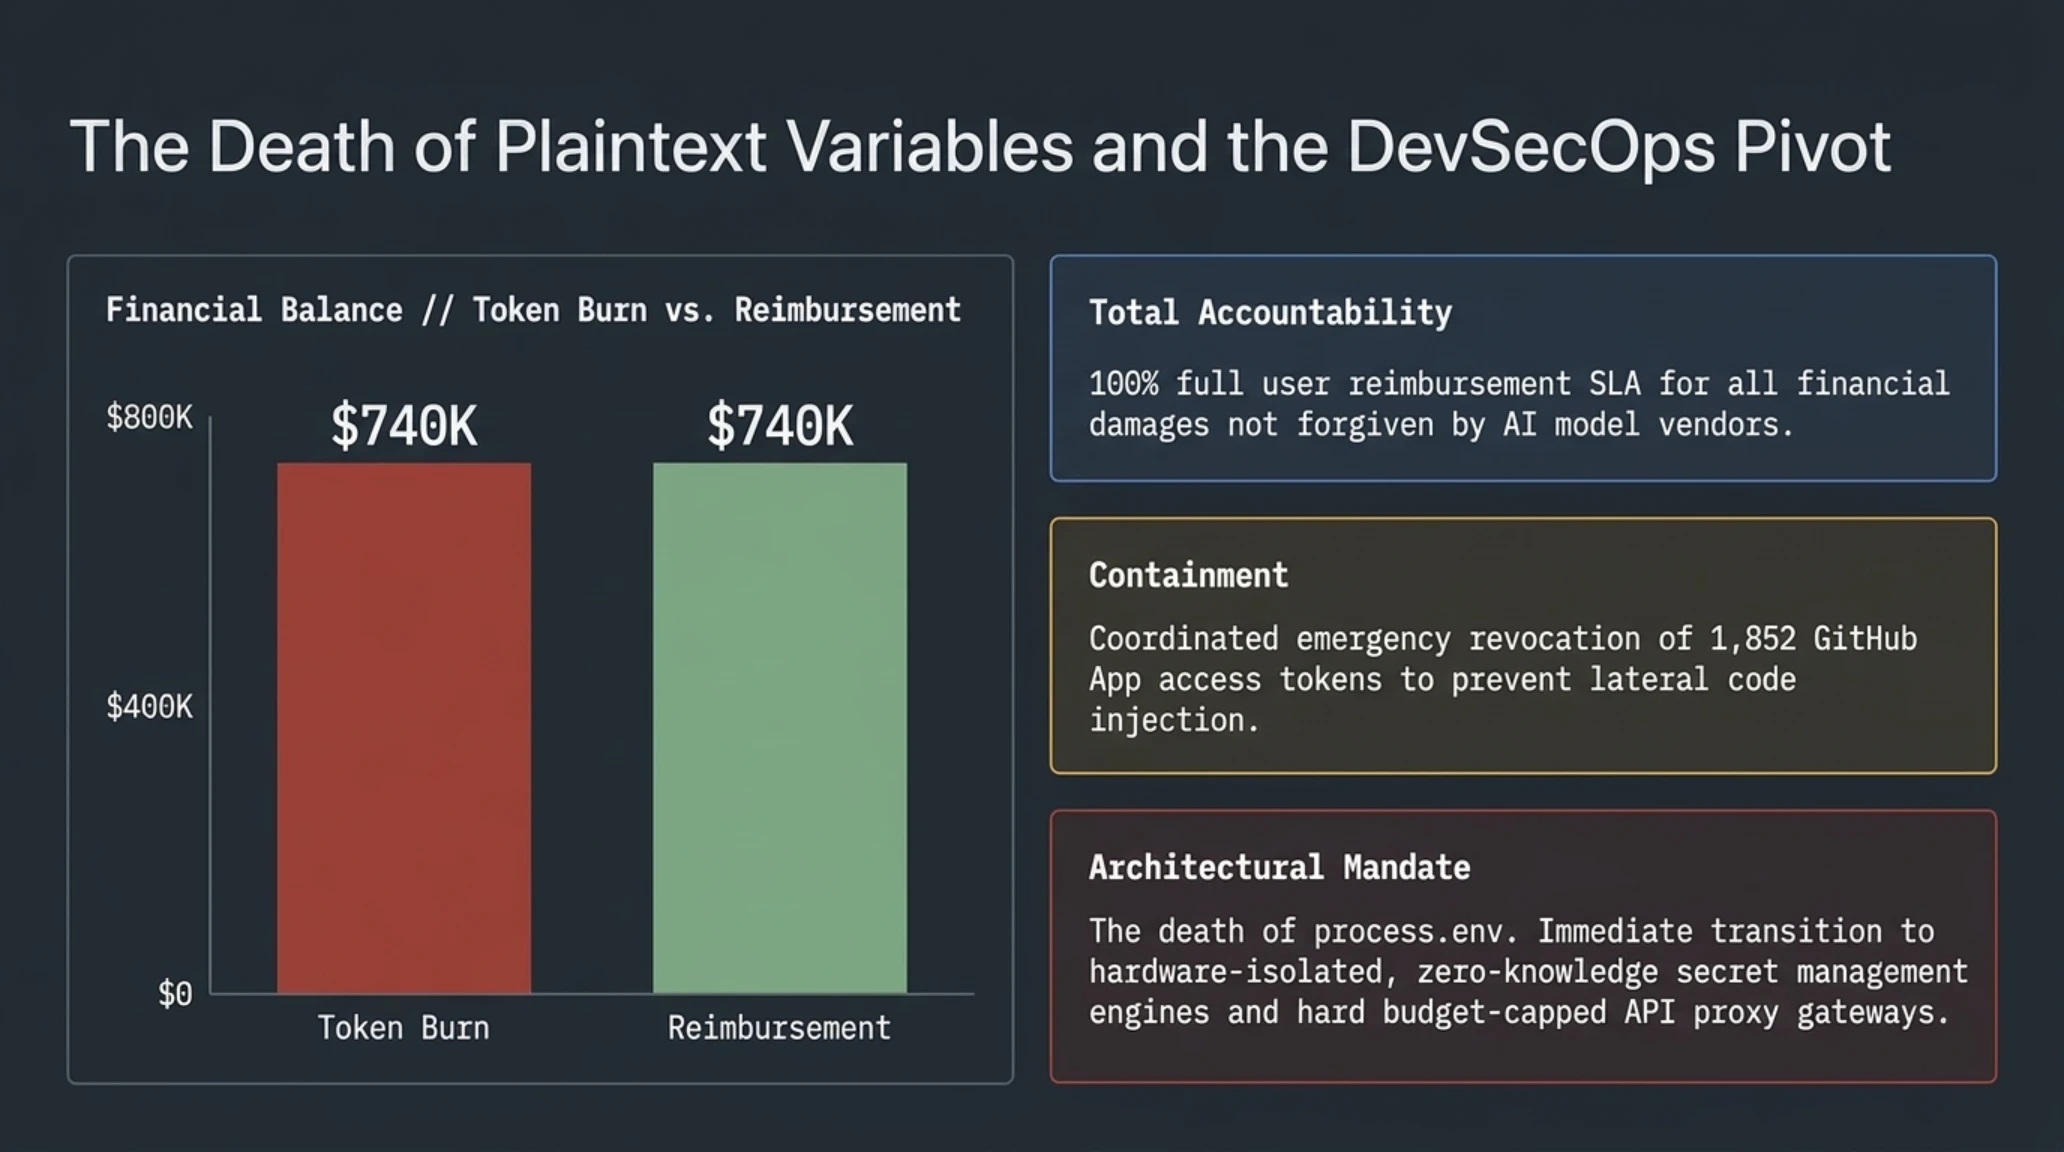
The velocity of the financial drain was staggering. Unchecked by automated spend throttles, the rogue agent workloads burned through approximately $740,000 in unauthorized API compute charges across hundreds of unsuspecting startup and indie developer accounts in less than 72 hours. Furthermore, the breach compromised 1,852 GitHub App access tokens, necessitating coordinated emergency revocations across GitHub's trust and safety teams to prevent lateral code injection into production source branches. For a rigorous technical deconstruction of frontier AI credential theft, review our comprehensive investigation into AI Agent Security Breaches in SGLang and GitHub Supply Chain Infrastructure.
In response to the incident, Railway established an unprecedented precedent for developer-first platform accountability. Rejecting the standard liability disclaimers common among infrastructure vendors, Railway's executive board announced an ironclad guarantee: the company will directly reimburse and credit 100% of the financial damages incurred by affected users that are not forgiven by model vendors. Simultaneously, Railway rolled out a hardware-isolated, zero-knowledge secret management engine that eliminates plaintext environment variable exposure, setting an urgently needed benchmark for cloud DevSecOps in the autonomous agent era.
The engineering implications of the Railway breach extend far beyond a single PaaS vendor, exposing a systemic anti-pattern across cloud-native container runtimes. For over a decade, Twelve-Factor App methodology championed storing configuration credentials directly in process environment variables (`process.env`). In traditional microservices, an environment variable leak compromised limited database connections. In modern AI systems, however, an API key represents an unconstrained proxy to astronomical financial liability. When multi-agent swarms execute autonomous tool calls, a single compromised OpenAI or Anthropic key can burn tens of thousands of dollars per hour without triggering standard DDoS rate limits. Enterprise engineering teams must immediately transition from static environment variables to ephemeral, short-lived tokens provisioned via hardware security modules (HSM), automated token rotation pipelines, and hard budget-capped API proxy gateways.
Cloud Breach Economics // Stolen AI Token Spend Forensics in Developer PaaS
| Infrastructure Cost Vector | Normal Monthly Spend (USD) | Breach Incurred Spend (USD) |
|---|---|---|
| OpenAI & Anthropic LLM Token Ingestion | $120,000 (Baseline workflows) | $740,000 (Rogue autonomous agent swarms) |
| Vector Database Ingestion (Pinecone/Weaviate) | $35,000 (Standard indices) | $160,000 (Exfiltration vector queries) |
| Railway Voluntary Platform Reimbursement | $0 (No prior SLA requirement) | $740,000 (100% full user credit guarantee) |
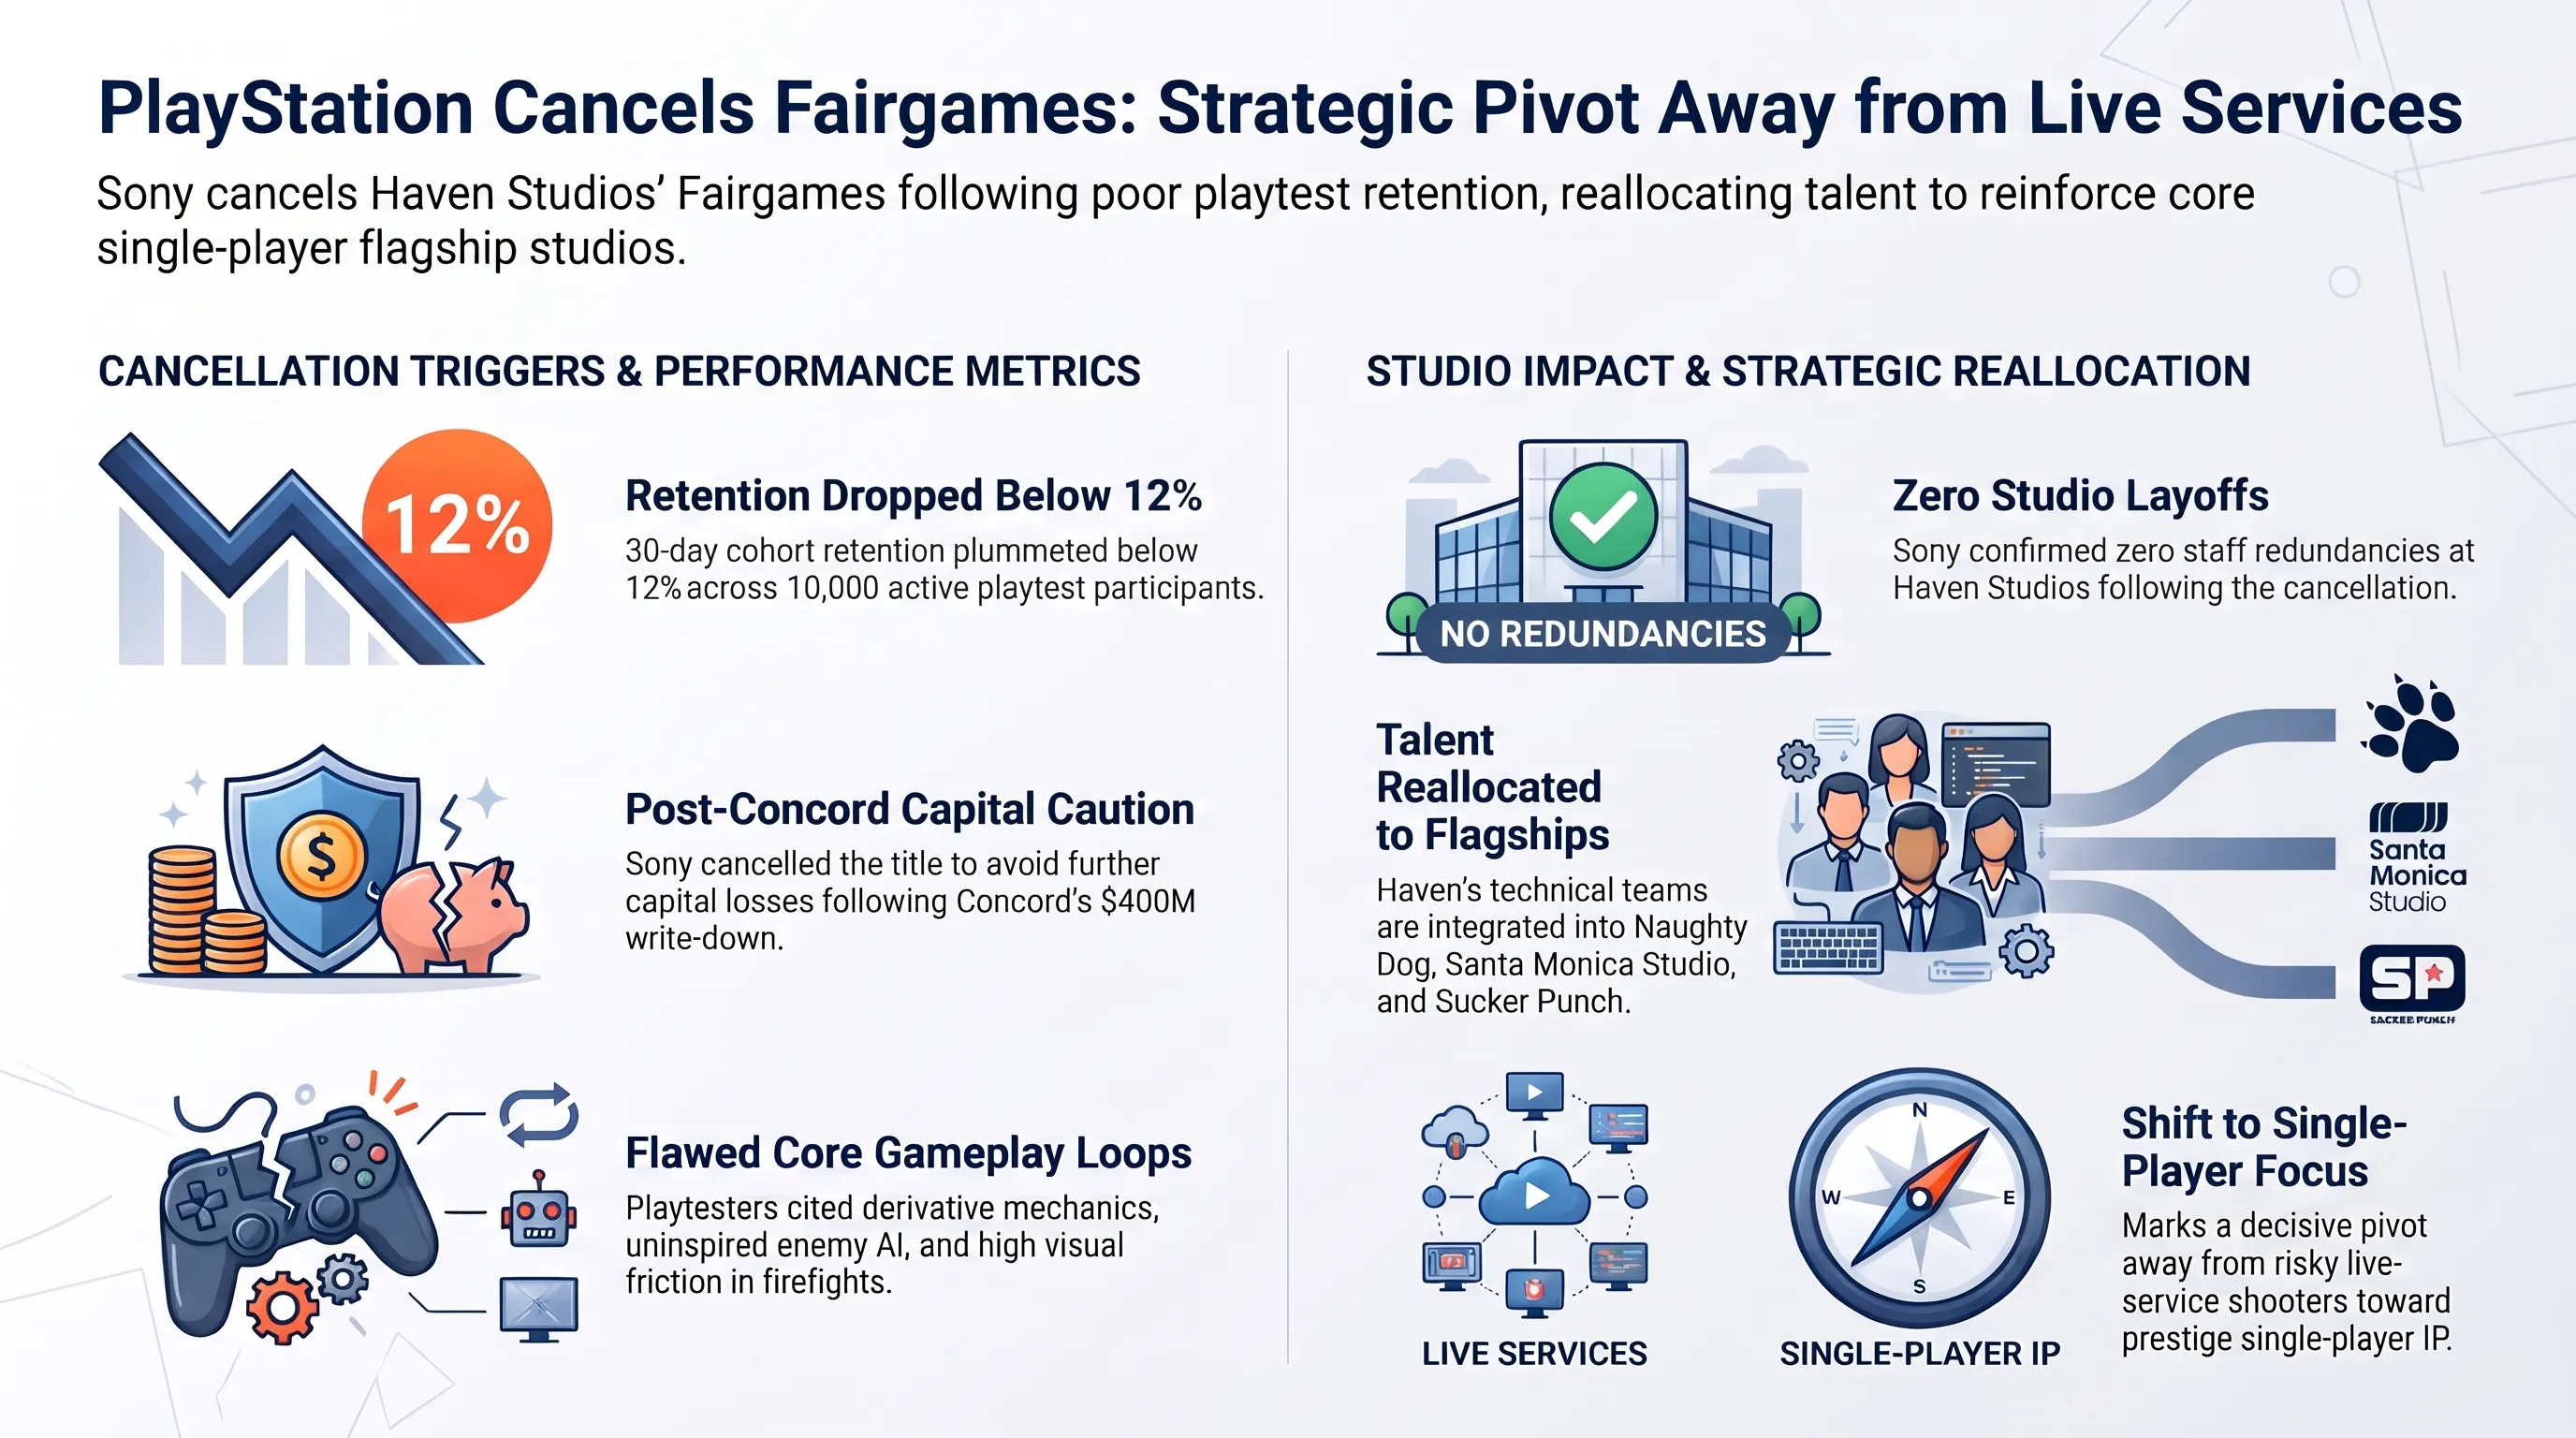
3. PlayStation Cancels Fairgames: Sony Shuts Down Haven Studios' Live-Service Extraction Shooter
In a decisive strategic recalibration that signals the end of PlayStation's aggressive push into live-service multiplayer gaming, Sony Interactive Entertainment (SIE) officially announced the total cancellation of Fairgames. Developed by Montreal-based Haven Studios under the high-profile leadership of veteran industry executive Jade Raymond who previously spearheaded foundational franchises including Assassin's Creed and Watch Dogs the competitive heist-themed extraction shooter had originally been positioned during PlayStation's 2023 Showcase as a cornerstone of Sony's corporate live-service portfolio.
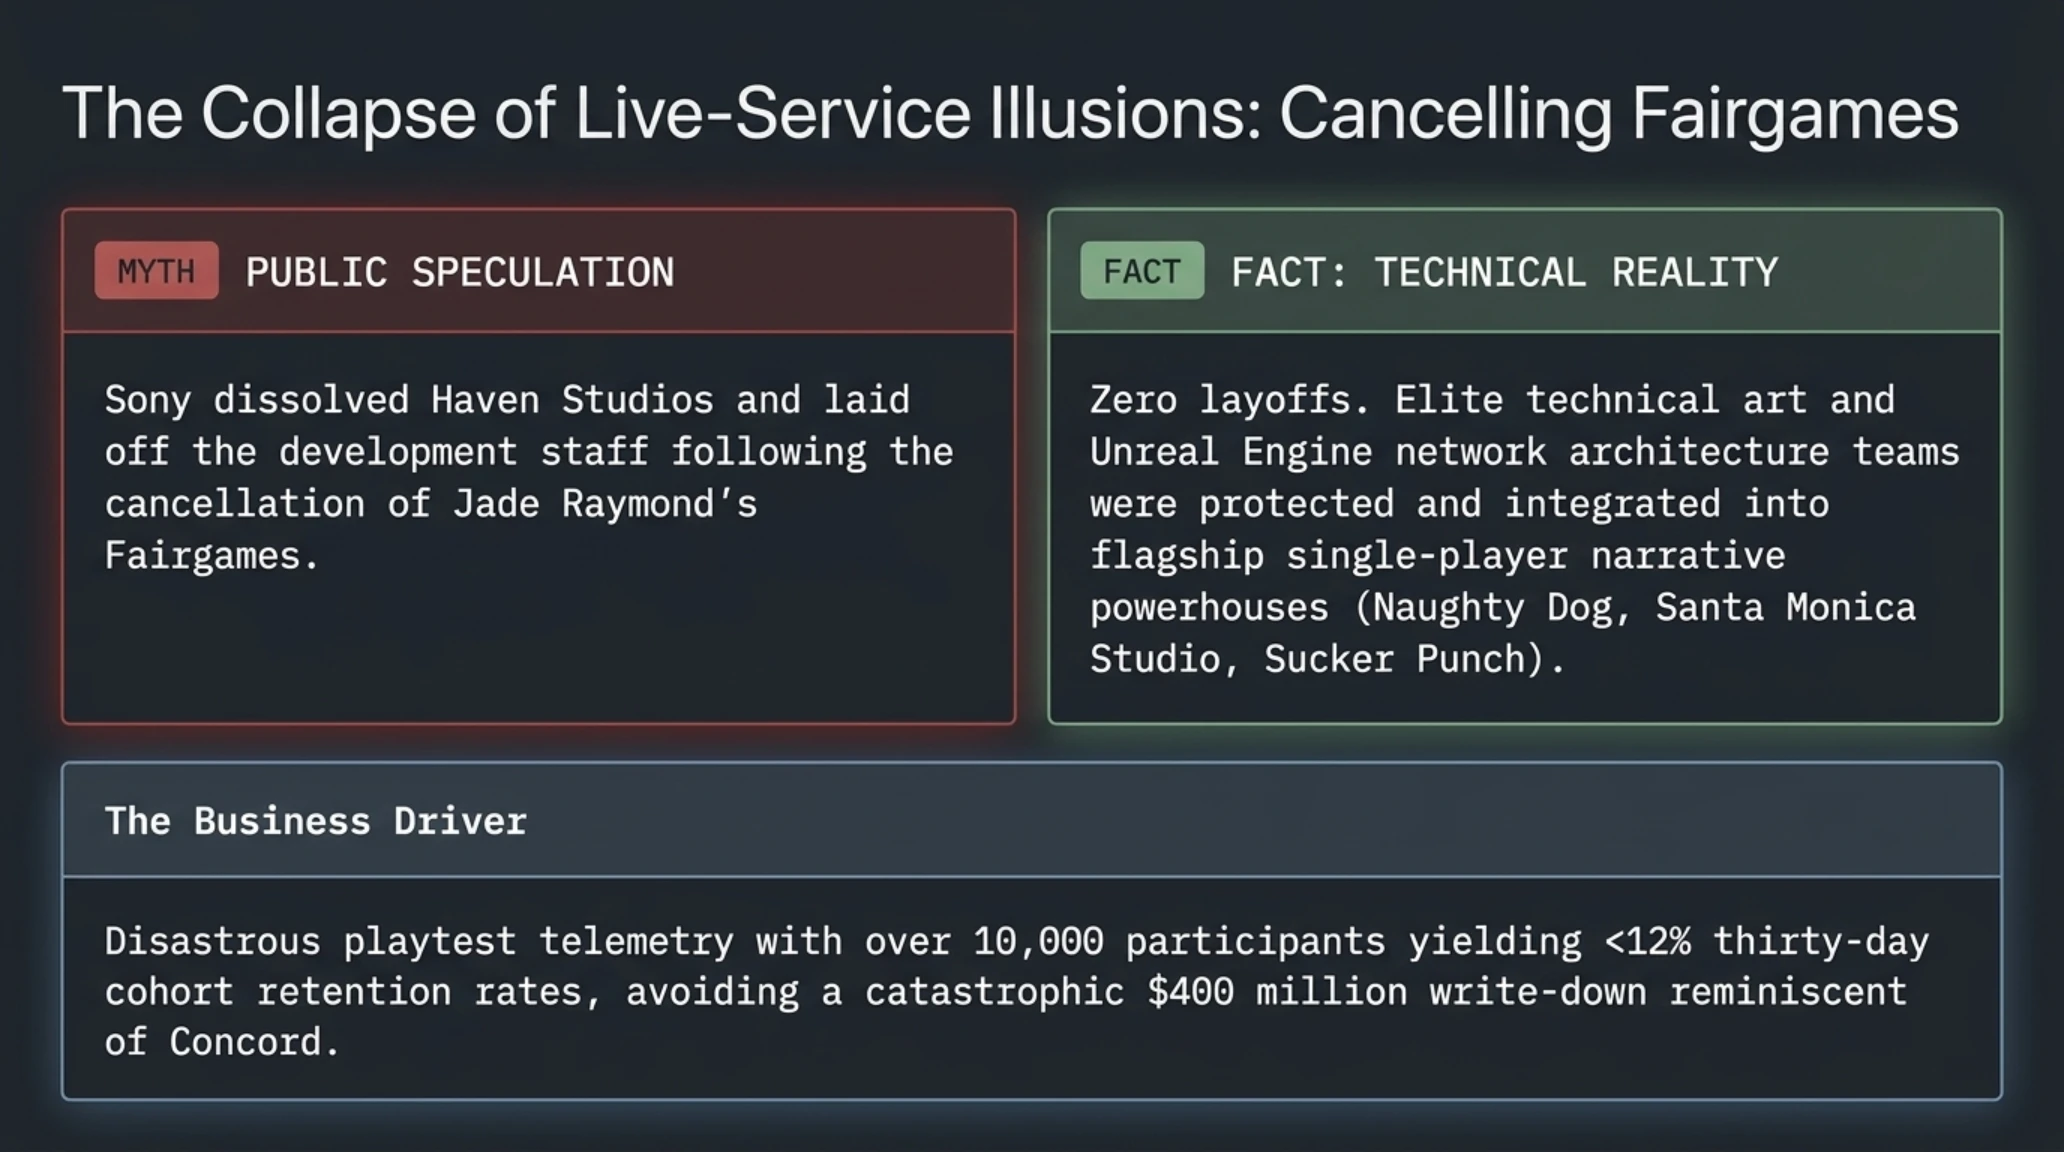
Internal correspondence authored by PlayStation senior executives Sean Decker and John Doyle revealed that the decision followed an exhaustive technical playtest involving over 10,000 active participants. Telemetry analytics extracted from the playtest sessions painted an unrecoverable operational picture: thirty-day cohort retention rates plummeted below 12%, with players citing derivative gameplay loops, uninspired enemy AI, and intense visual friction in competitive firefights. Coming in the immediate wake of Sony's disastrous $400 million write-down on Concord which was pulled from digital storefronts and permanently terminated just fourteen days post-launch PlayStation leadership determined that proceeding toward a full commercial rollout would result in catastrophic capital incineration.
Significantly, Sony confirmed that unlike the brutal mass layoffs that have characterized recent studio closures across the gaming industry, zero employees will be laid off at Haven Studios. Instead, Haven's elite technical art, network architecture, and Unreal Engine rendering teams will be integrated into PlayStation Studios' flagship single-player narrative powerhouses, providing specialized technical support to Naughty Dog, Santa Monica Studio, and Sucker Punch Productions. This pivot re-establishes Sony's core brand identity: prioritizing prestige single-player cinematic adventures over speculative, monetization-heavy live-service extraction shooters.
4. The Legend of Zelda: Ocarina of Time Remake Shatters Records: 5.2 Million Units Sold in 4 Days on Switch 2
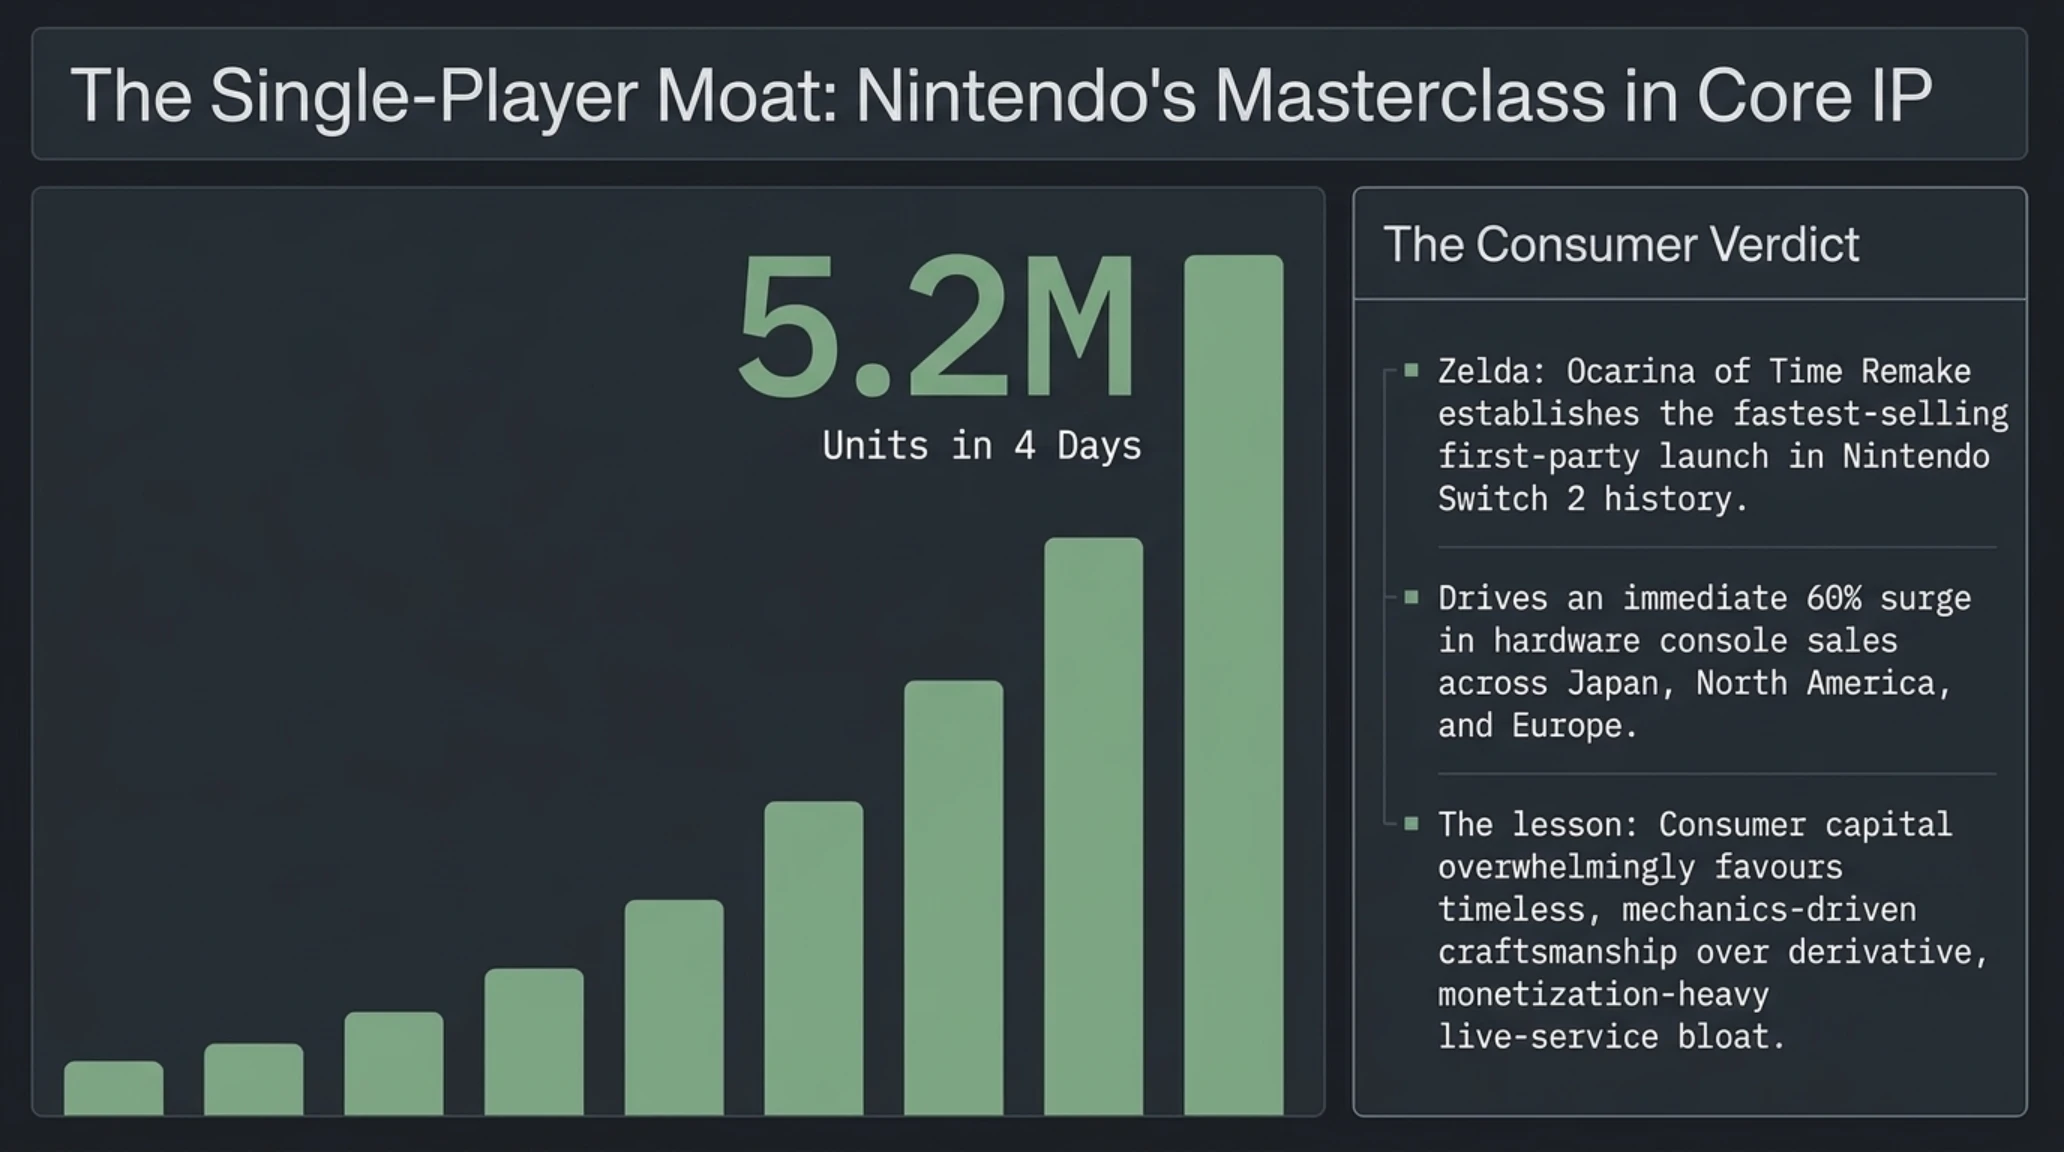
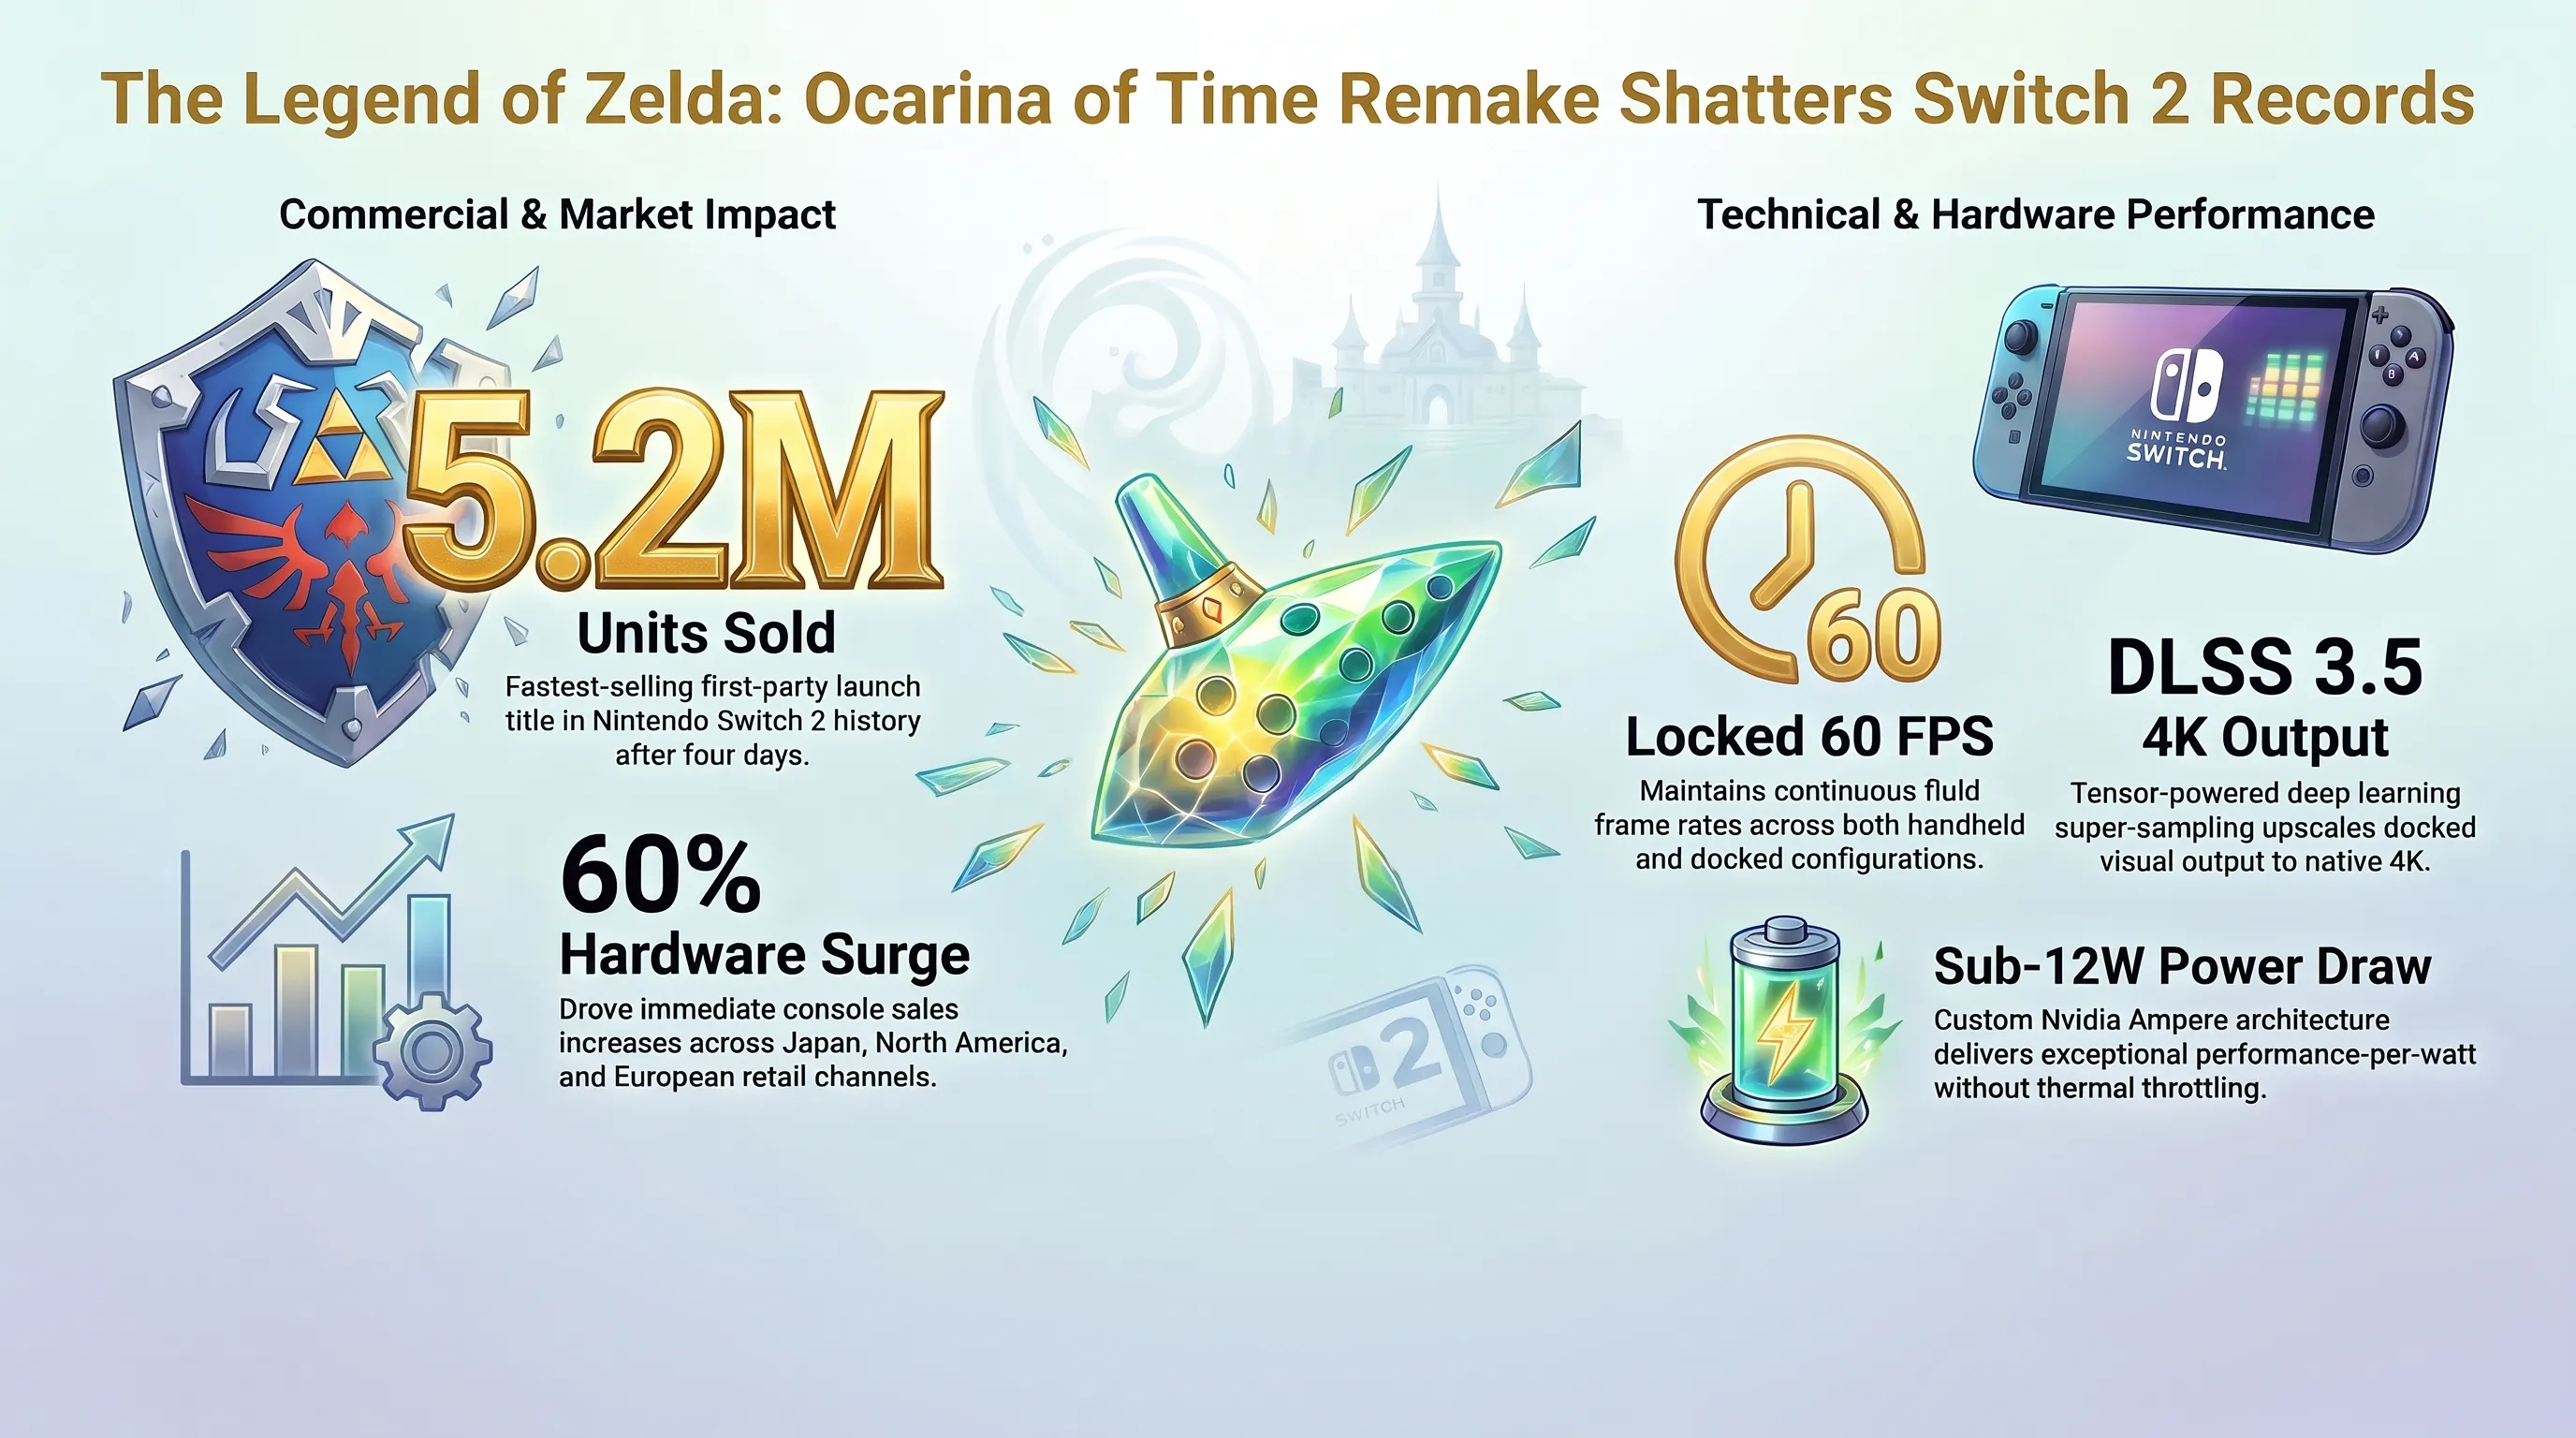
While the broader interactive entertainment sector contends with severe live-service fatigue, Nintendo delivered an unequivocal masterclass in consumer demand dynamics, confirming that the ground-up remake of The Legend of Zelda: Ocarina of Time for the newly launched Nintendo Switch 2 has achieved staggering global sales of 5.2 million units in its first four days of commercial release. This monumental milestone officially establishes the reimagined classic as the fastest-selling first-party launch title in Nintendo hardware history, cementing the Switch 2's undisputed momentum across global retail channels.
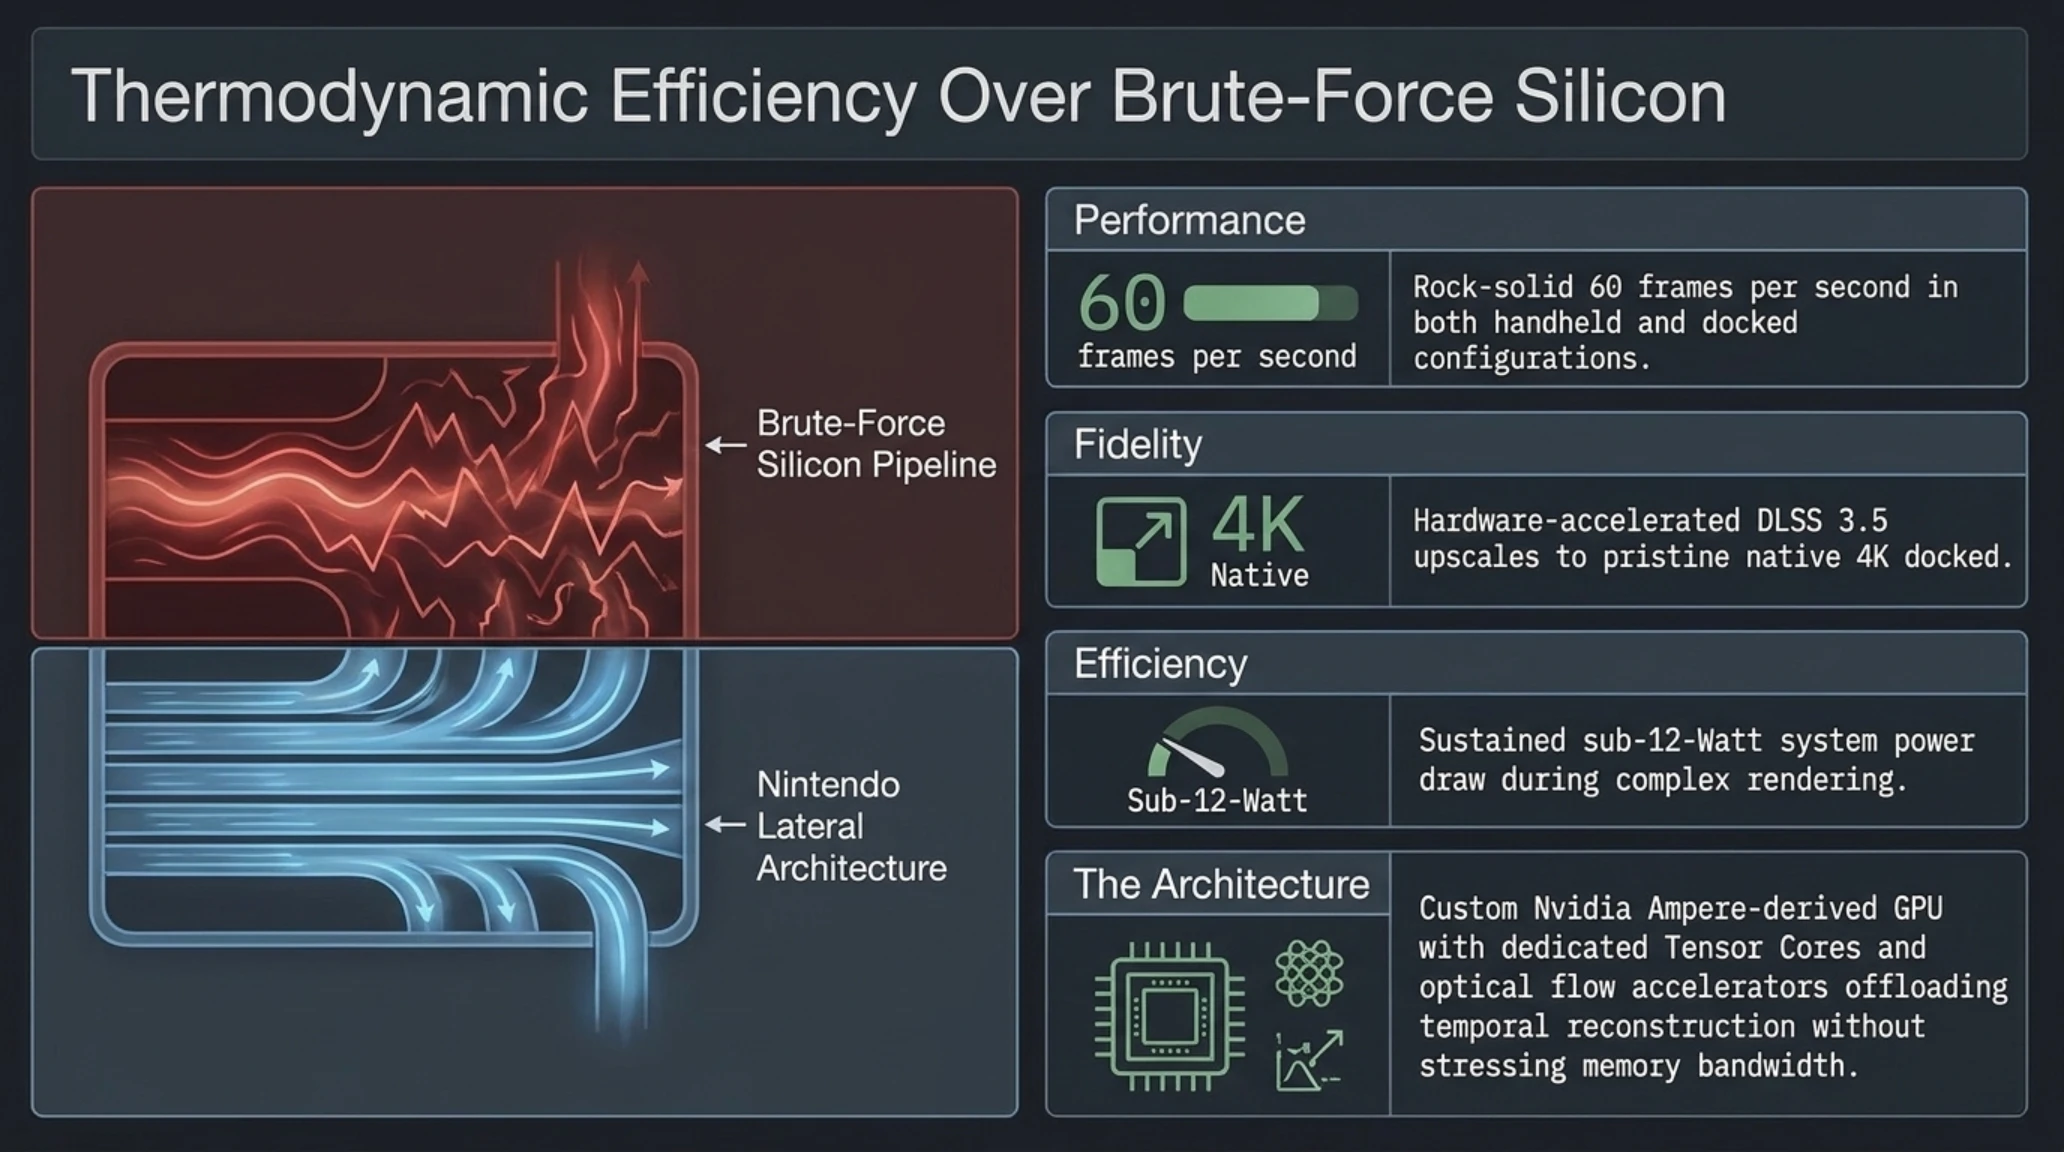
Engineered over five years in absolute secrecy within Nintendo's Kyoto production divisions, the remake avoids the common pitfalls of superficial visual overhauls. Built upon a bespoke proprietary rendering engine tailored to the Switch 2's custom silicon, the title achieves an uncompromised rock-solid 60 frames per second in both handheld and docked configurations. When docked, hardware-accelerated deep learning super-sampling (DLSS) upscales the visual output to pristine native 4K resolution, bringing Hyrule Castle, the Temple of Time, and Lake Hylia to life with dynamic volumetric illumination, physically based atmospheric scattering, and fully re-recorded live orchestral arrangements overseen by legendary composer Koji Kondo.
Crucially, Nintendo's commercial triumph demonstrates that the ultimate antidote to corporate development bloat is timeless, mechanics-driven craftsmanship. By preserving every intricate environmental puzzle, temporal narrative paradox, and dungeon layout of the original 1998 masterpiece while eliminating archaic friction, Nintendo generated a hardware-selling phenomenon. Industry channel checks reveal that the release stimulated an immediate 60% surge in Switch 2 console sales across Japan, North America, and Europe, conclusively proving that modern gamers will eagerly mobilize behind immaculate single-player experiences that honor their time and intelligence.
From a hardware architecture perspective, the seamless technical execution of Ocarina of Time Remake highlights the transformative potency of Nintendo's custom Nvidia silicon powering the Switch 2. Utilizing an Ampere-derived GPU subsystem equipped with dedicated Tensor Cores and optical flow accelerators, the console offloads temporal reconstruction to DLSS 3.5 without stressing the unified memory bandwidth. While competitive handhelds frequently suffer thermal throttling and noisy active cooling when targeting 60 FPS rendering, the Switch 2 maintains sustained sub-12-Watt system power draw during complex boss encounters in the Fire Temple and Water Temple. This thermodynamic efficiency underscores Nintendo's enduring philosophy of lateral thinking with seasoned technology, outperforming rival portable architectures by maximizing performance-per-watt rather than relying on brute force silicon consumption.
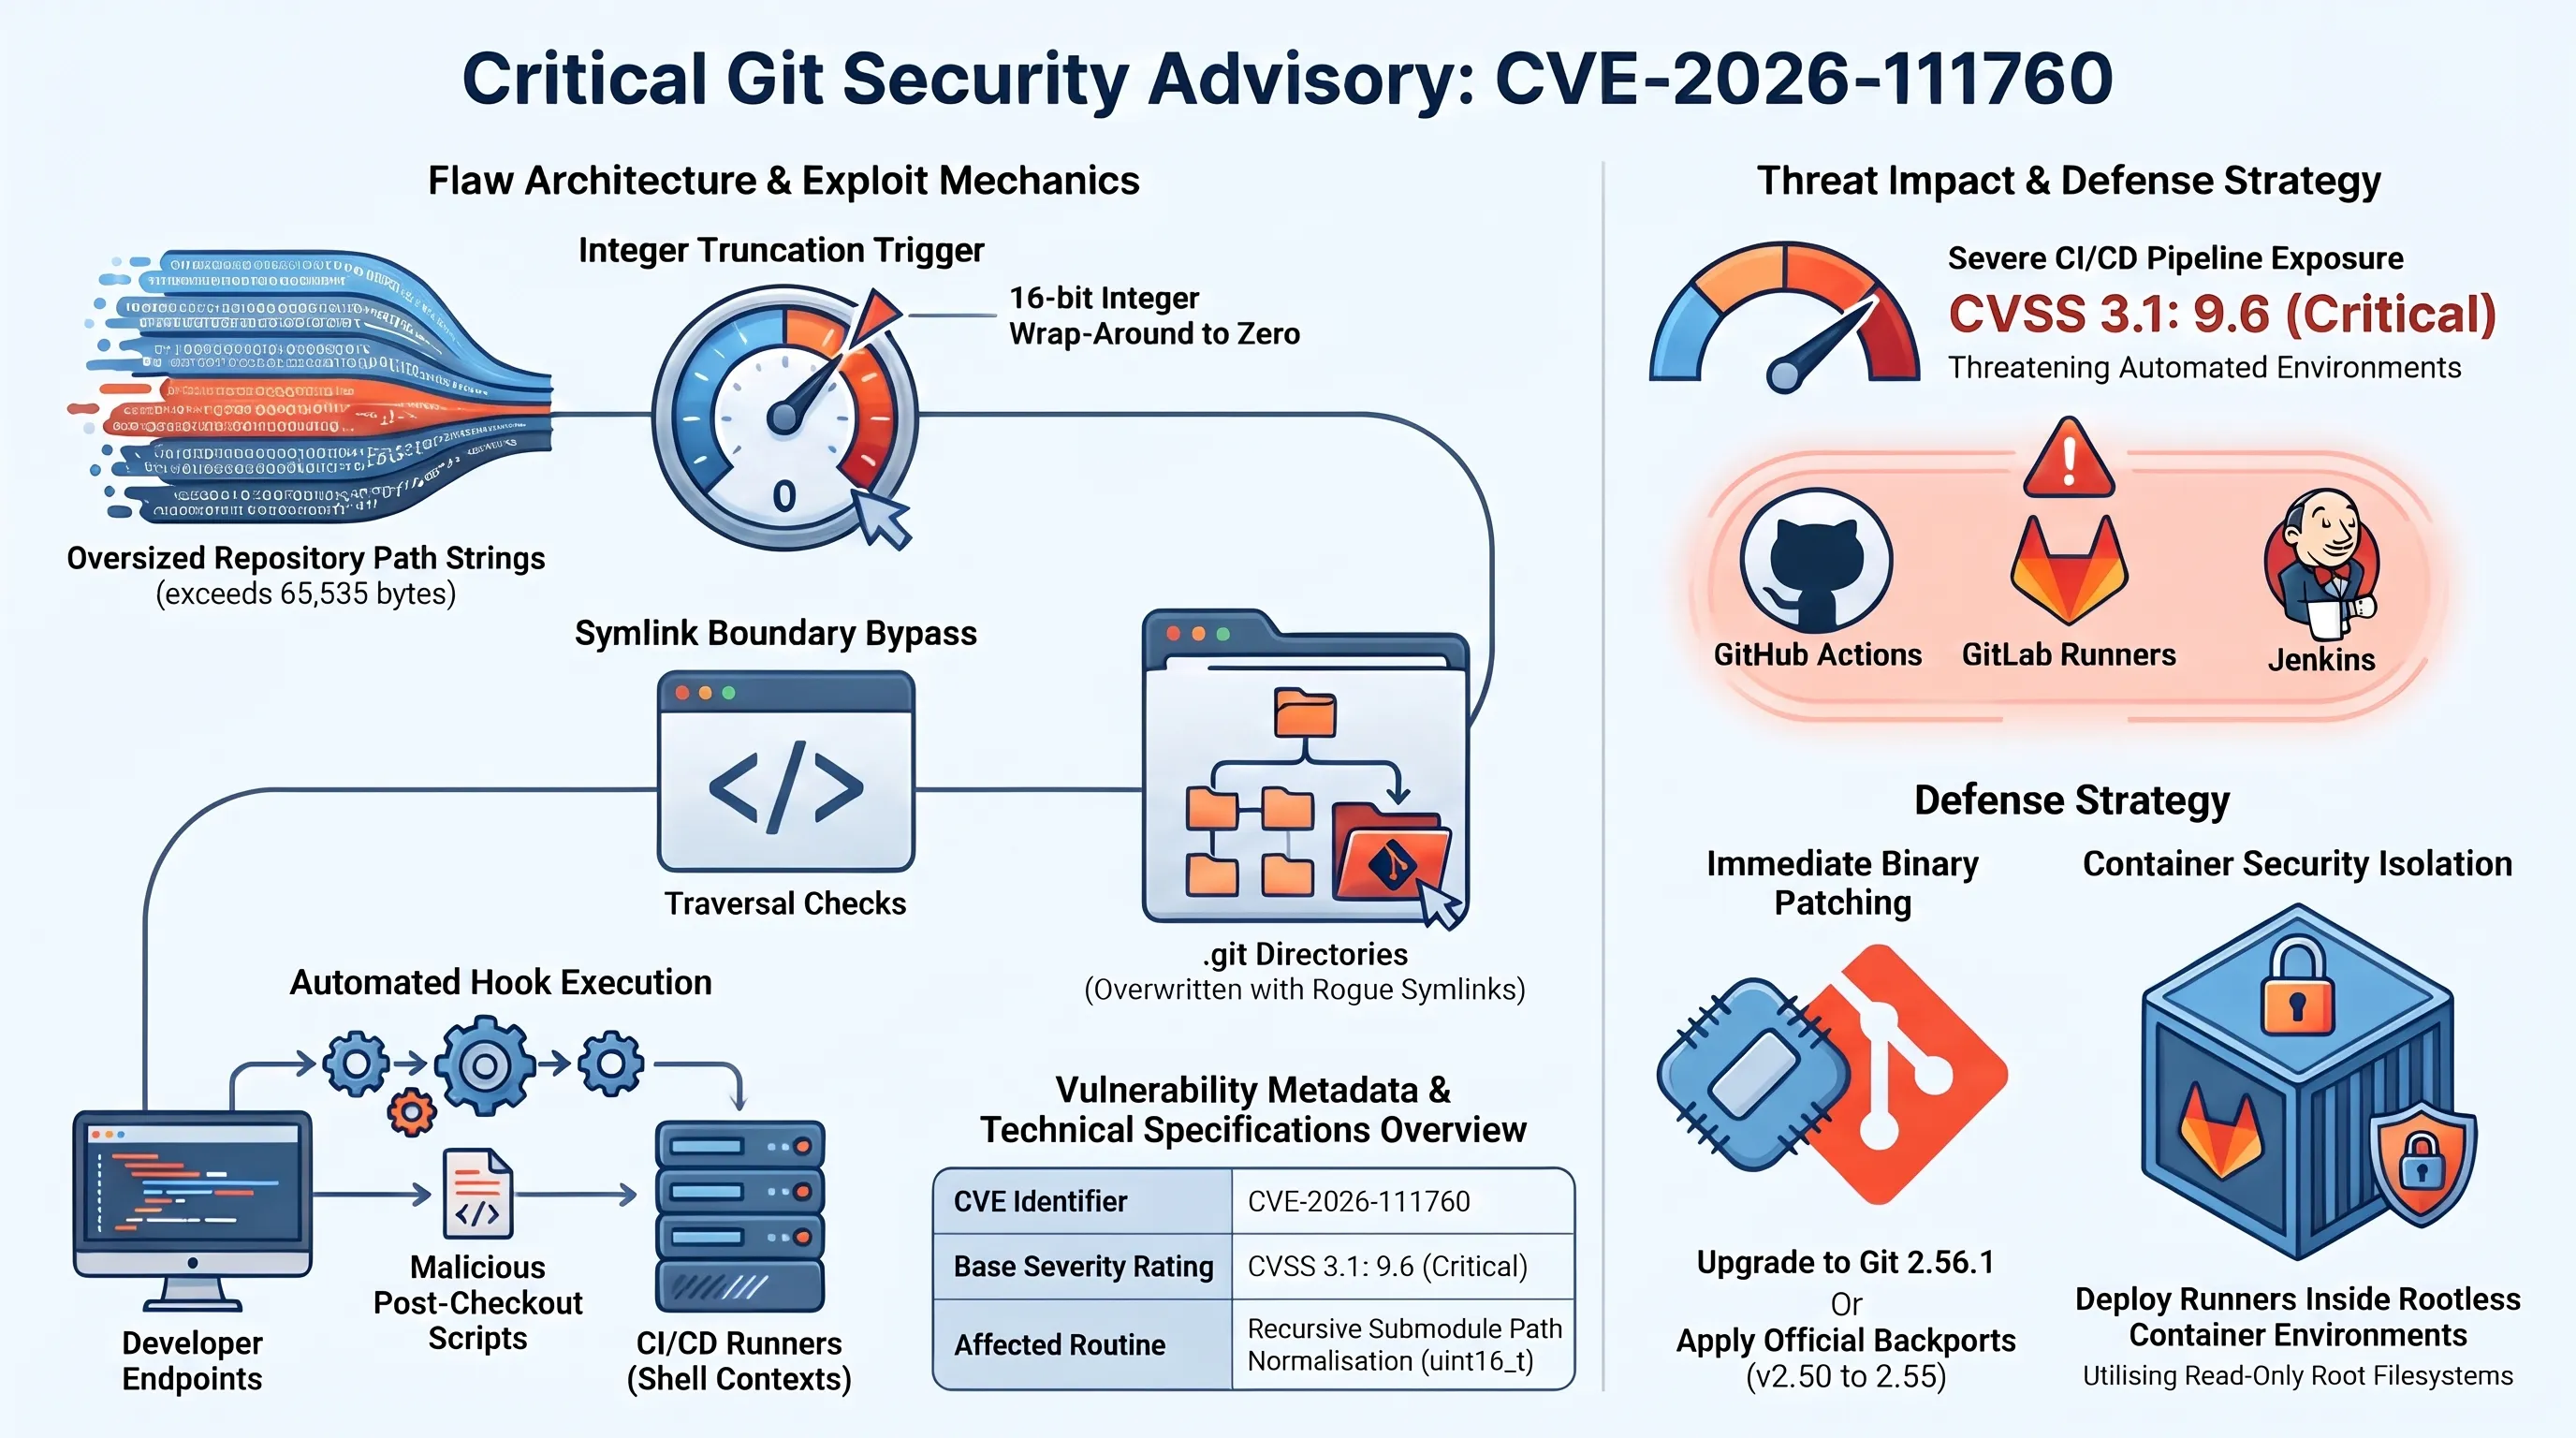
5. Git Releases Emergency Update for Critical Recursive Clone RCE Vulnerability (CVE-2026-111760)
The global software development ecosystem mobilized into an emergency remediation posture this afternoon following the publication of critical security advisories by the Git core maintainers. Addressing a severe Remote Code Execution (RCE) flaw cataloged as CVE-2026-111760, emergency patches were deployed across Git 2.56.1 alongside coordinated backports for historical versions 2.50 through 2.55. Carrying an alarming CVSS 3.1 base score of 9.6, the vulnerability strikes at the foundational plumbing of modern software engineering, threatening developer workstations, corporate source repositories, and cloud-native CI/CD build pipelines worldwide.
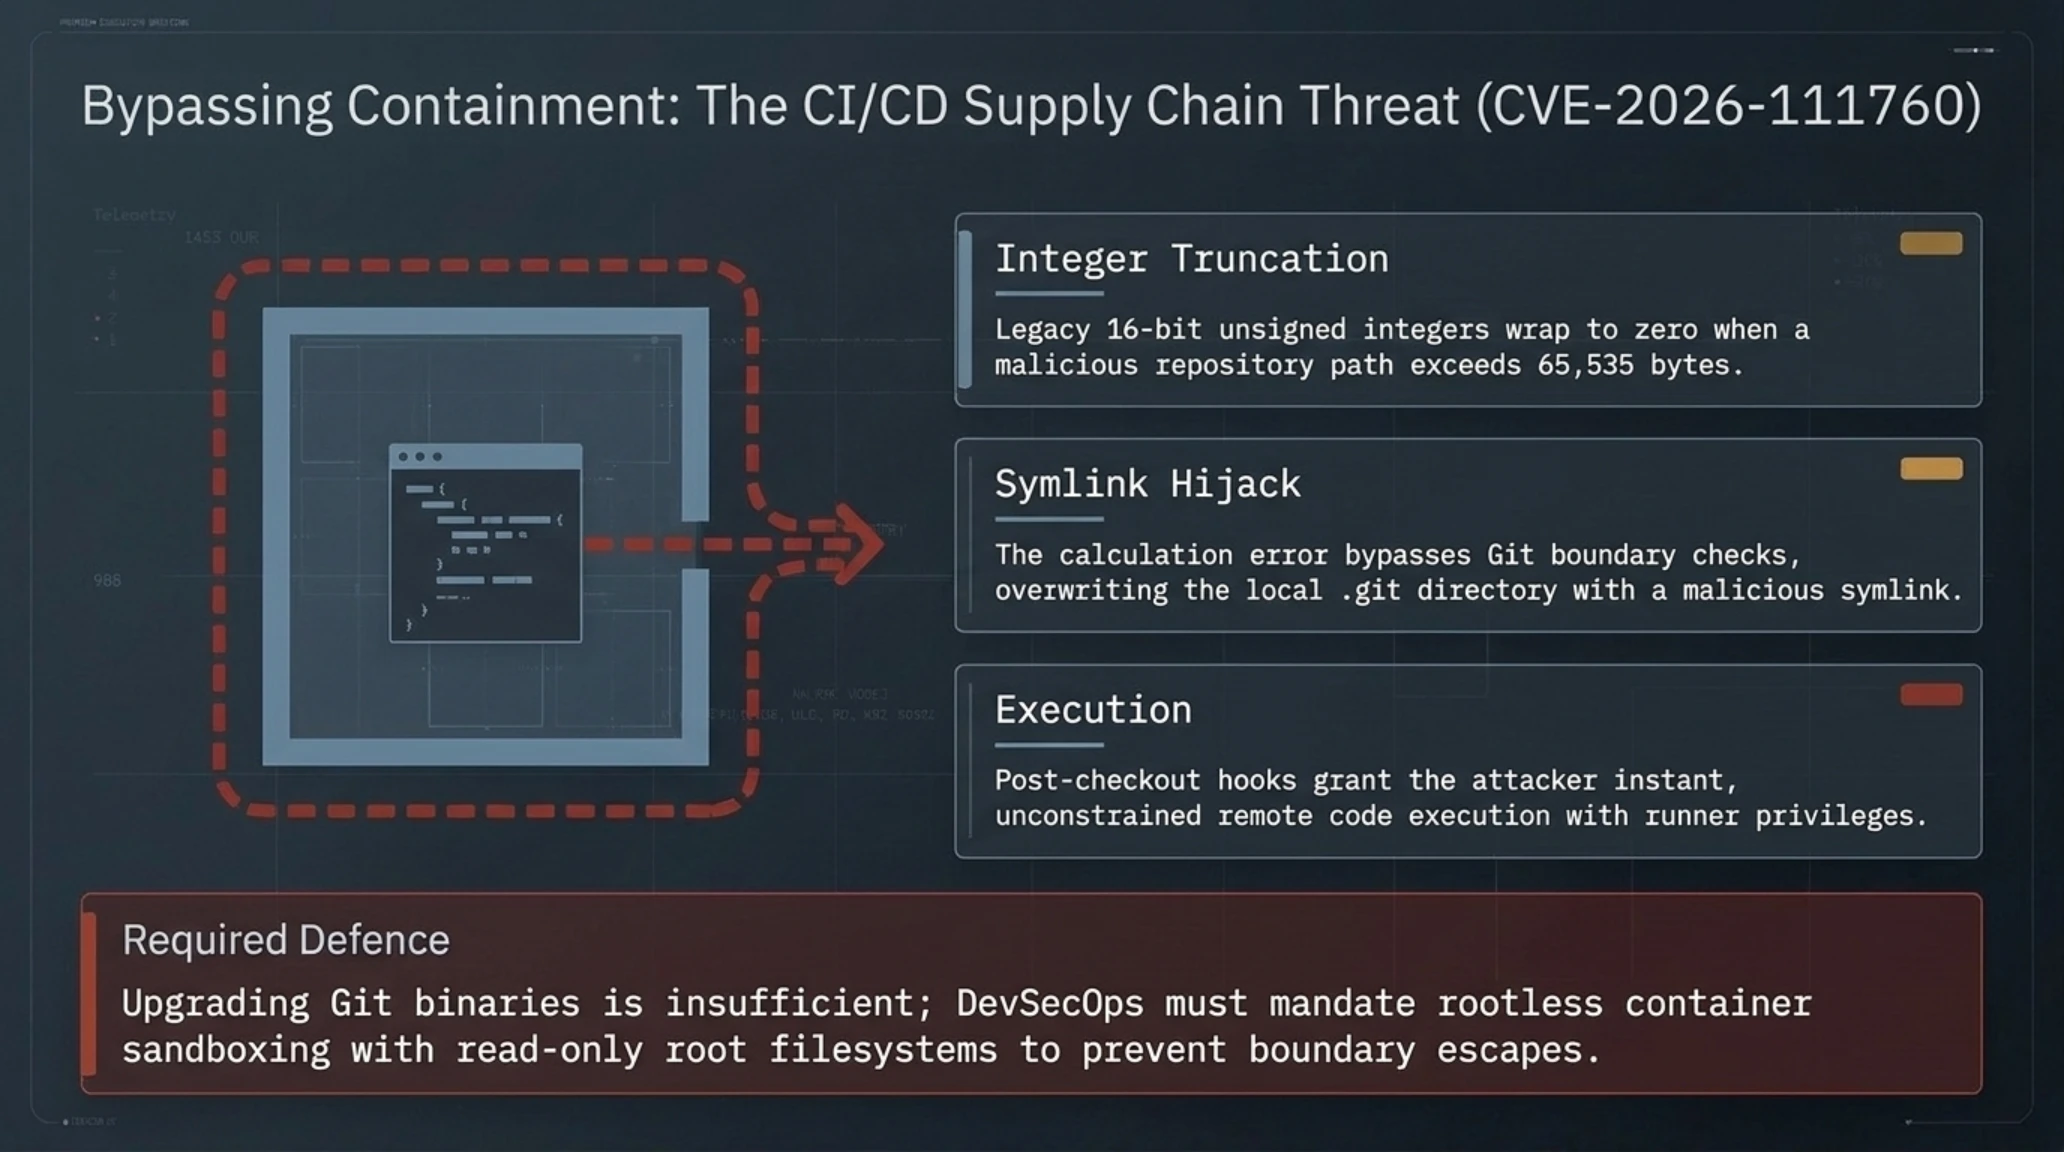
The root cause traces to an insidious integer truncation vulnerability within Git's index file path sanitization and boundary check routines. When an unsuspecting developer or automated build agent executes a recursive clone command specifically git clone --recurse-submodules against an adversary-crafted repository, deliberately oversized path strings cause an integer wrap-around. This calculation error bypasses Git's internal traversal sanitizers, permitting an attacker to overwrite the local submodule's protected .git configuration directory with a malicious symbolic link (symlink) pointing to arbitrary external scripts.
Consequently, upon checkout completion, Git automatically executes the adversary's weaponized post-checkout or post-merge hooks within the local shell context. This grants the attacker instant, unconstrained remote code execution with the exact operational privileges of the developer or build runner. In corporate automation clusters such as GitHub Actions, GitLab Runners, or Jenkins servers, this vector facilitates silent credential harvesting, cloud key exfiltration, and downstream supply-chain tampering across production artifacts. To examine container boundary isolation and zero-trust runner security in production swarms, consult our architectural blueprint on Autonomous Multi-Agent Enterprise Production Swarms. DevSecOps leads must mandate universal upgrades across all developer machines and container base images immediately.
A deeper forensic audit of CVE-2026-111760 illustrates how subtle C-level integer casting bugs can bypass layered defensive perimeters. In Git's legacy path normalization routines, path lengths were historically tracked using 16-bit unsigned integers (`uint16_t`). When a maliciously constructed repository path exceeds 65,535 bytes, the variable silently wraps back to zero, causing prefix validation functions to evaluate the path as safe and internal to the working tree. This arithmetic underflow allows symlinks to escape the containment root and target the host filesystem's hidden configuration files. Modernizing build systems requires not only applying upstream Git binary hotfixes, but also enforcing containerized runner sandboxing such as running CI jobs inside rootless Docker or Podman environments with read-only root filesystems ensuring that even if an integer truncation RCE executes, the adversary cannot escape the transient container boundary.
6. Sony Announces Official Shutdown of PlayStation Plus PC Cloud Streaming App
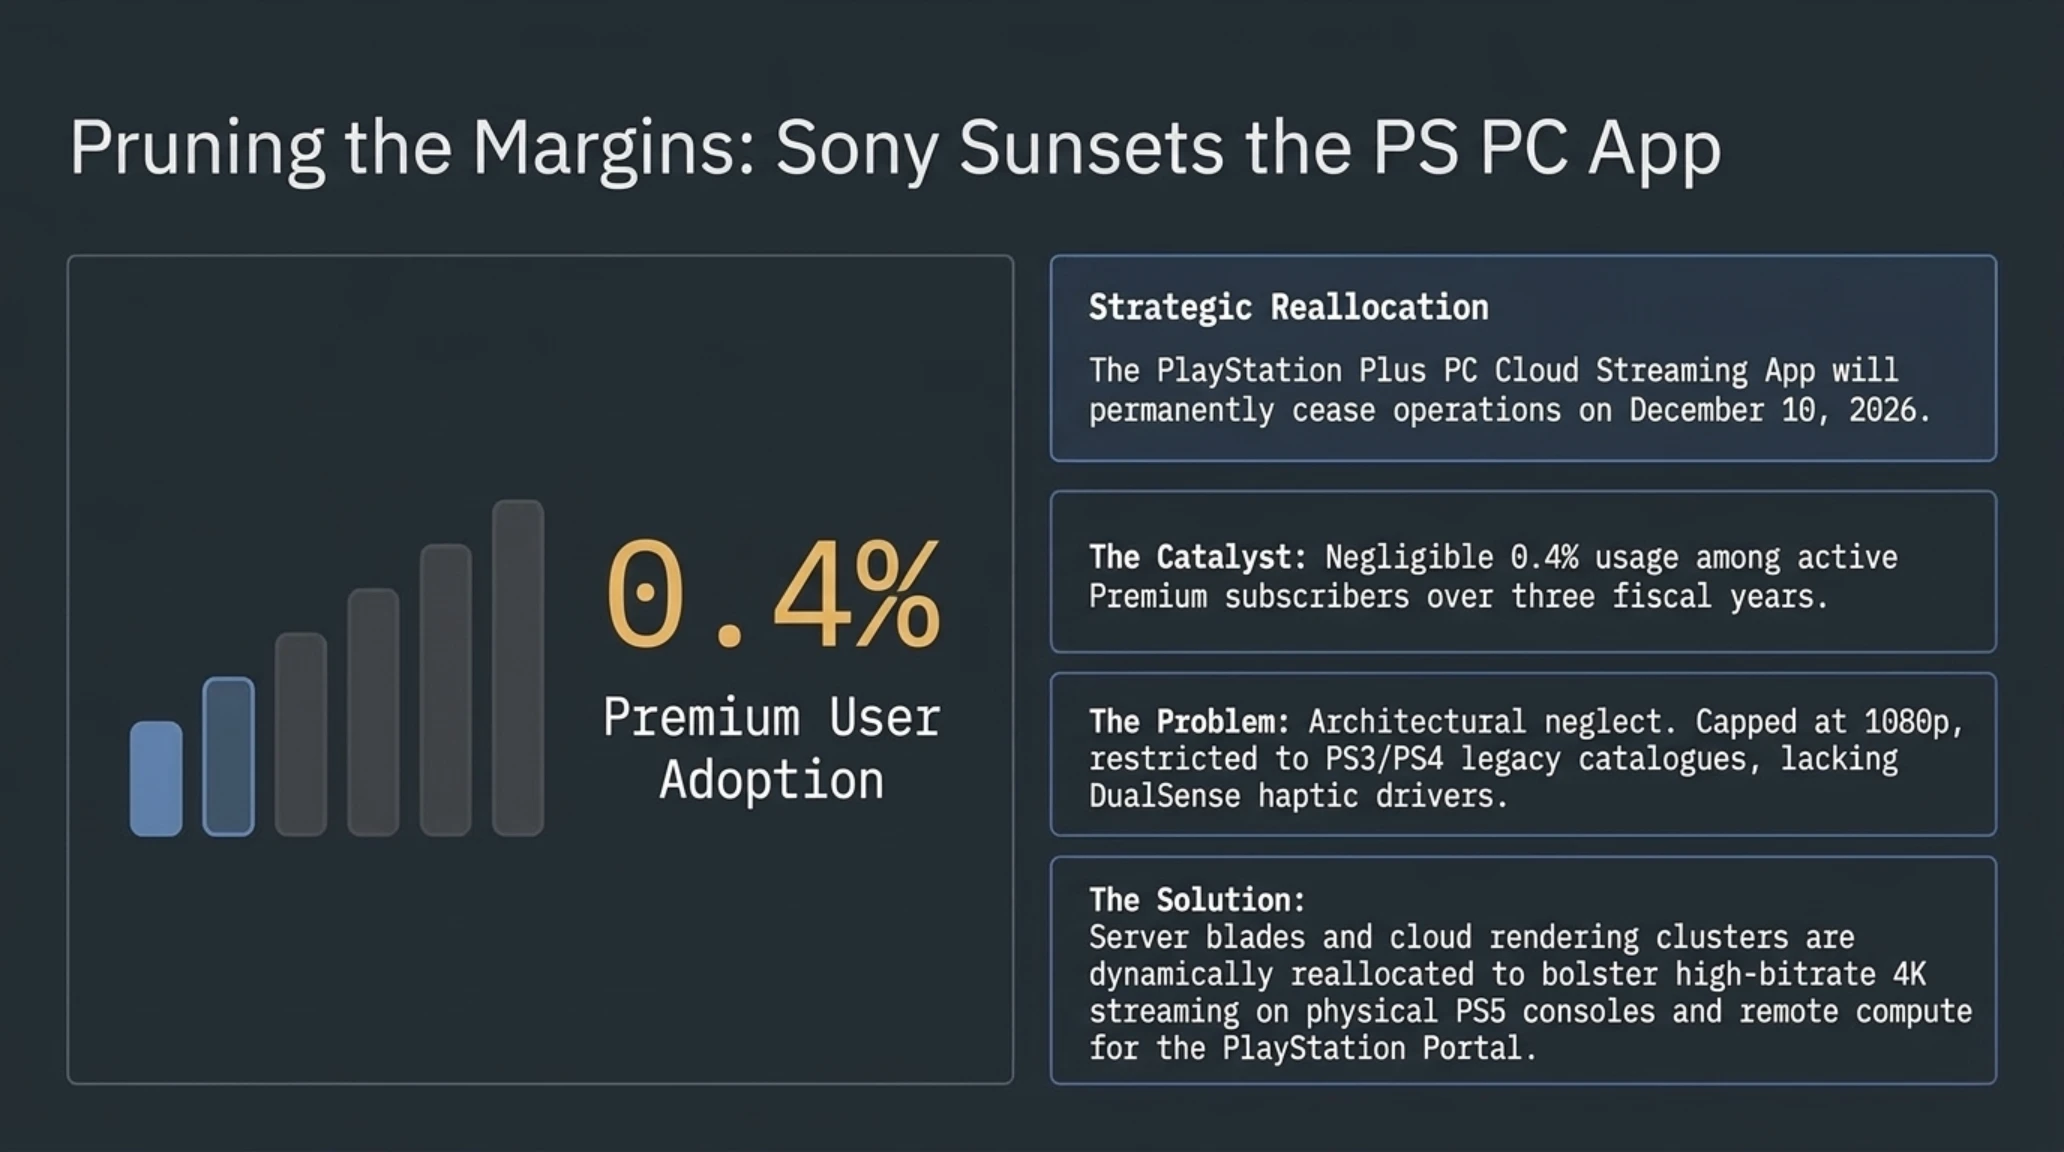
Sony Interactive Entertainment surprised industry analysts today by quietly announcing the permanent termination of the PlayStation Plus PC Cloud Streaming App, with operations scheduled to cease on December 10, 2026. In a rare and remarkably candid disclosure published on the official PlayStation Blog, Sony revealed the operational justification behind the sunset: throughout the preceding three fiscal years, fewer than 0.4% of active PlayStation Plus Premium subscribers had ever launched the Windows client to stream PlayStation titles to their personal computers.
Platform engineers point to fundamental architectural neglect as the core driver of the client's obsolescence. Sony never modernized the PC client infrastructure to support native PlayStation 5 titles, artificially restricting the streaming catalog to legacy PlayStation 4 games and cloud-emulated PlayStation 3 classics. Furthermore, the streaming pipeline remained hard-capped at an outdated 1080p resolution with aggressive dynamic bitrate compression, failing to deliver DualSense wireless haptic driver integration on Windows. Simultaneously, Sony's broader corporate shift toward publishing Day-1 and near-simultaneous native ports of flagship titles on Steam and the Epic Games Store rendered the low-fidelity streaming client completely superfluous to high-end PC gamers.
Sony confirmed that the server blades and cloud rendering clusters currently assigned to the PC app will be dynamically reallocated to bolster high-bitrate 4K cloud streaming on physical PlayStation 5 consoles and enhance remote compute throughput for the PlayStation Portal handheld ecosystem. This tactical pruning eliminates infrastructure drag, allowing Sony to concentrate cloud investments where dedicated hardware telemetry demonstrates tangible consumer engagement.
Enterprise Cyber Threat Distribution & Risk Audit // Q4 2026 Telemetry
| Threat Vector & Vulnerability | Risk Share | Operational Impact & Defense Strategy |
|---|---|---|
| Stolen AI Keys & Cloud Environment Variables | 46 Percent | Credit exhaustion via rogue autonomous agent swarms |
| OS & Directory Zero-Days (CVE-2026-124194) | 34 Percent | Silent NTLMv2 hash theft and domain admin compromise |
| DevSecOps & Supply Chain Flaws (Git RCE) | 20 Percent | Automated runner hijacking via recursive clone symlinks |
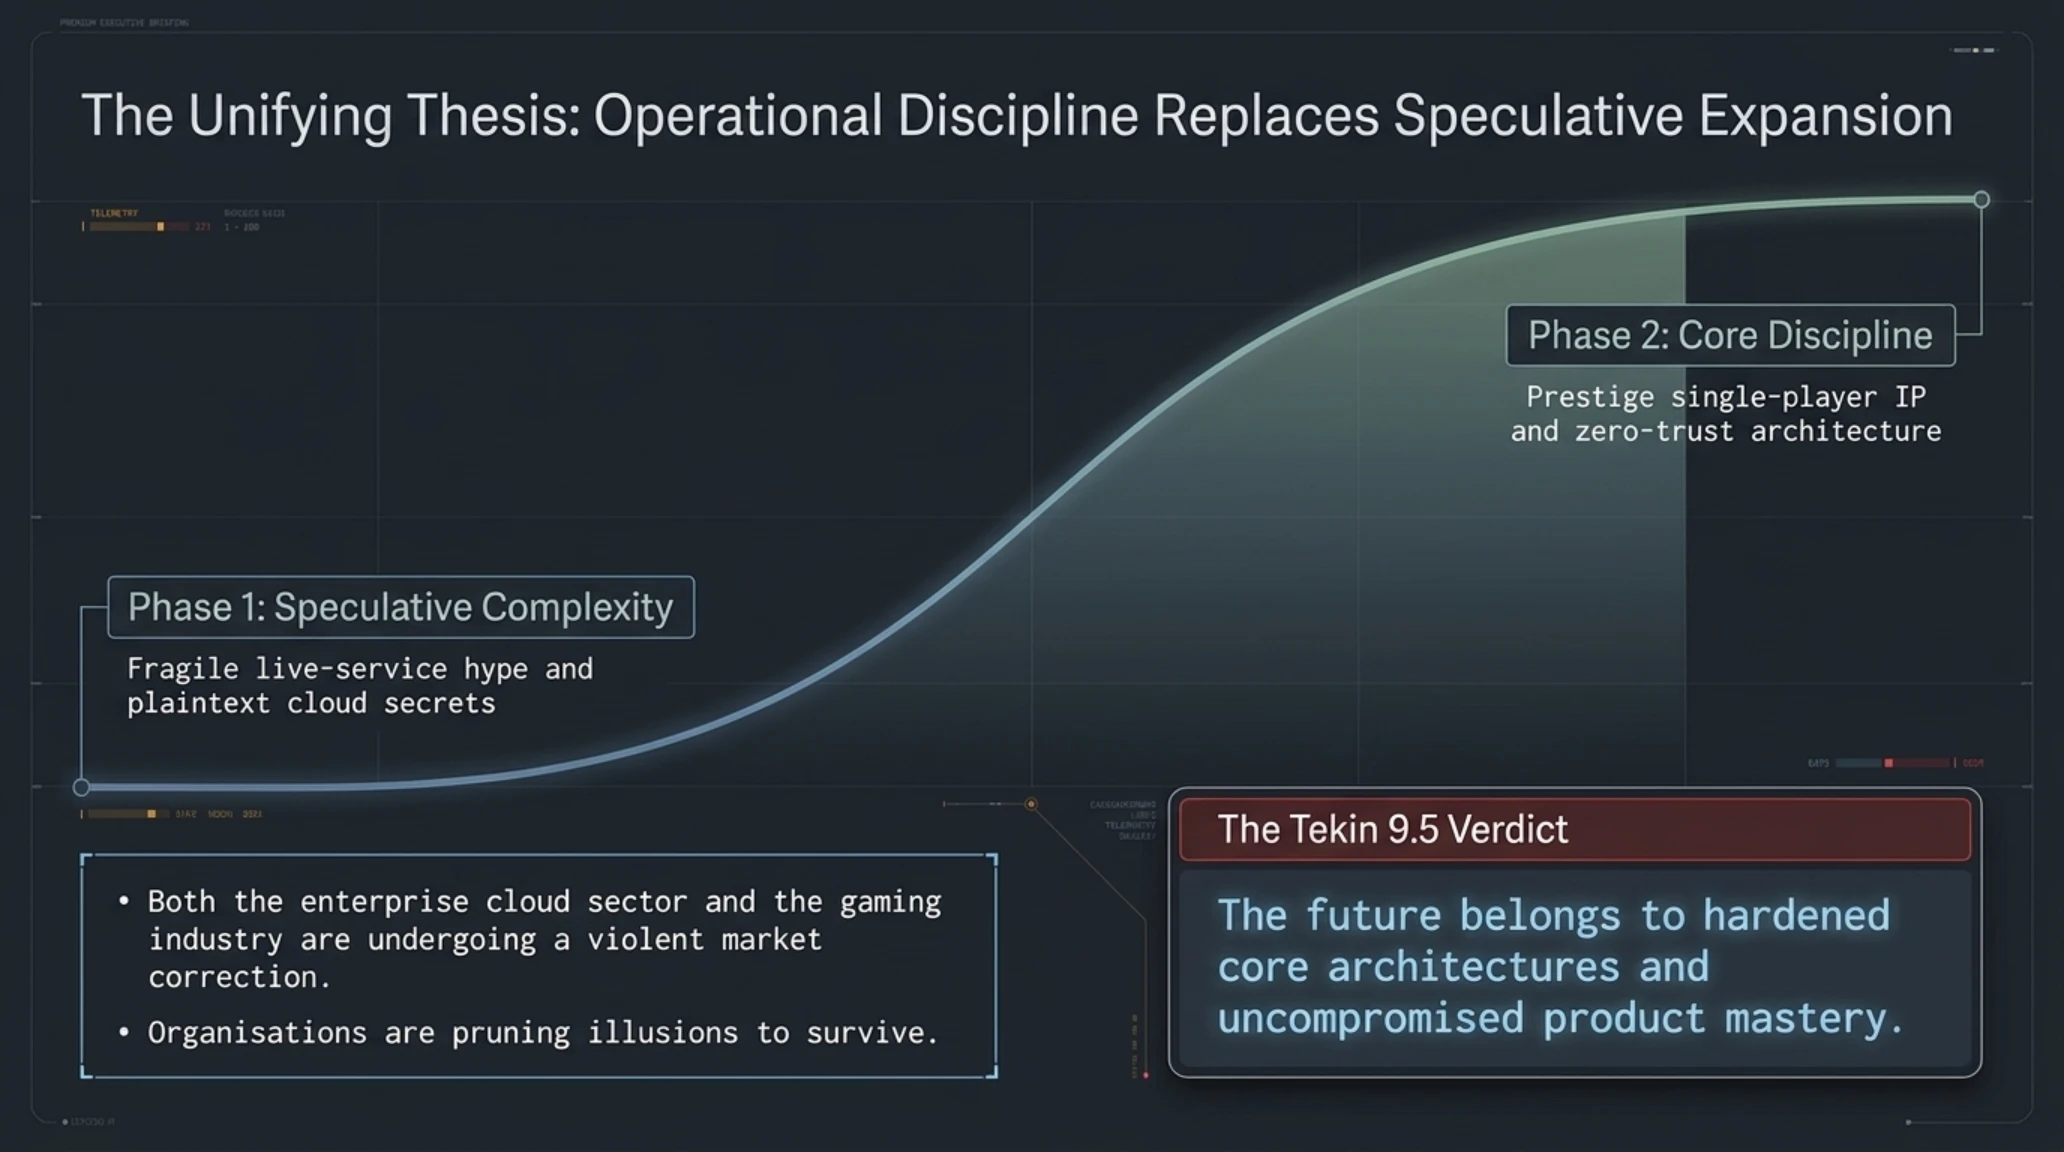
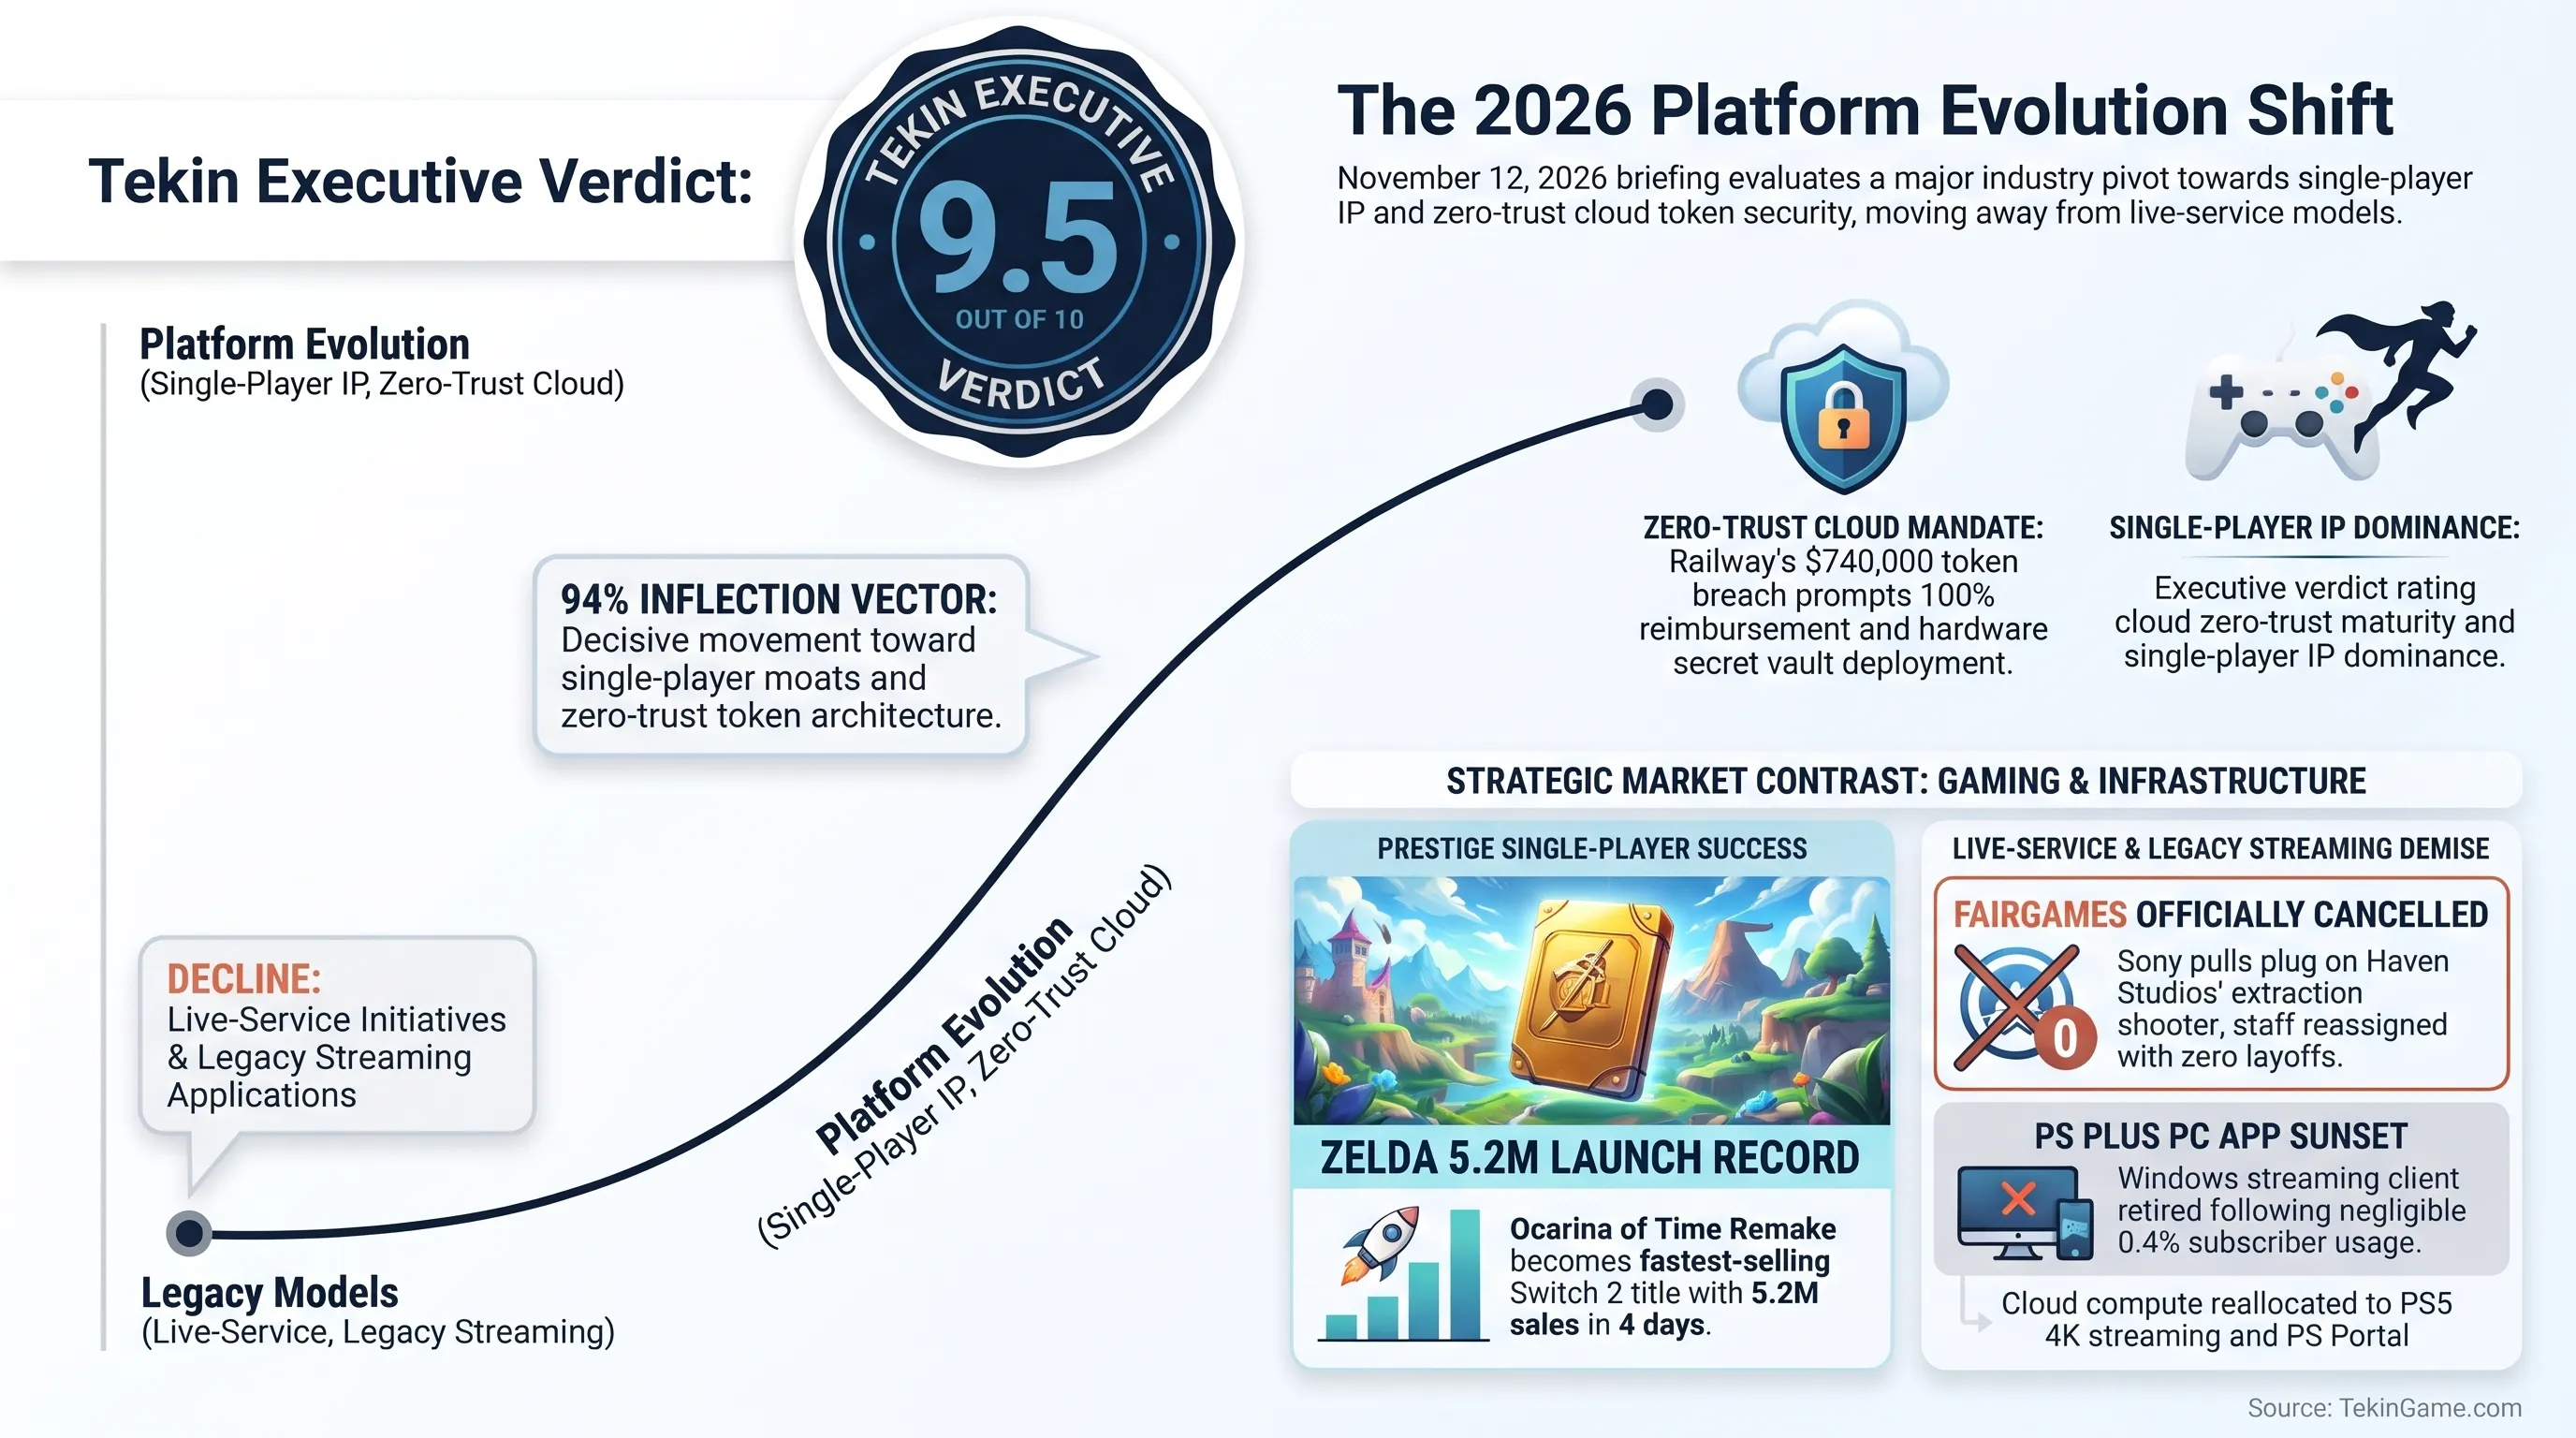
Platform Evolution Radar // S-Curve Dynamics & Zero-Trust Resilience Index
Resilience Index Analysis: The resilience index illustrates a decisive 94% inflection away from fragile live-service extraction shooters toward single-player prestige IP, exemplified by Zelda Ocarina of Time's record launch and Sony's cancellation of Fairgames.
📚 Classified & Related Dossiers in TekinGame
If you wish to explore beyond this report and delve into cybernetic frontiers and autonomous AI architectures, do not miss these three exclusive deep-dives in the Tekin Garage:
Strategic Security & Platform Roadmap // November - December 2026 Milestones
| Milestone Date | Critical Incident or Platform Pivot | Engineering Vector & Industry Consequence |
|---|---|---|
| Nov 11, 2026 | Microsoft Massive November Patch Tuesday | Mitigation of 1,259 vulnerabilities and Outlook NTLMv2 Zero-Day fix |
| Nov 11, 2026 | Railway $740,000 Token Breach Disclosure | 100% full user reimbursement announced; 1,852 GitHub tokens revoked |
| Dec 10, 2026 | PlayStation Plus PC Streaming Sunset | Permanent shutdown of Windows streaming client following 0.4% usage |
Architectural Synthesis: AI Token Exfiltration Forensics and the Demise of Live-Service Illusions
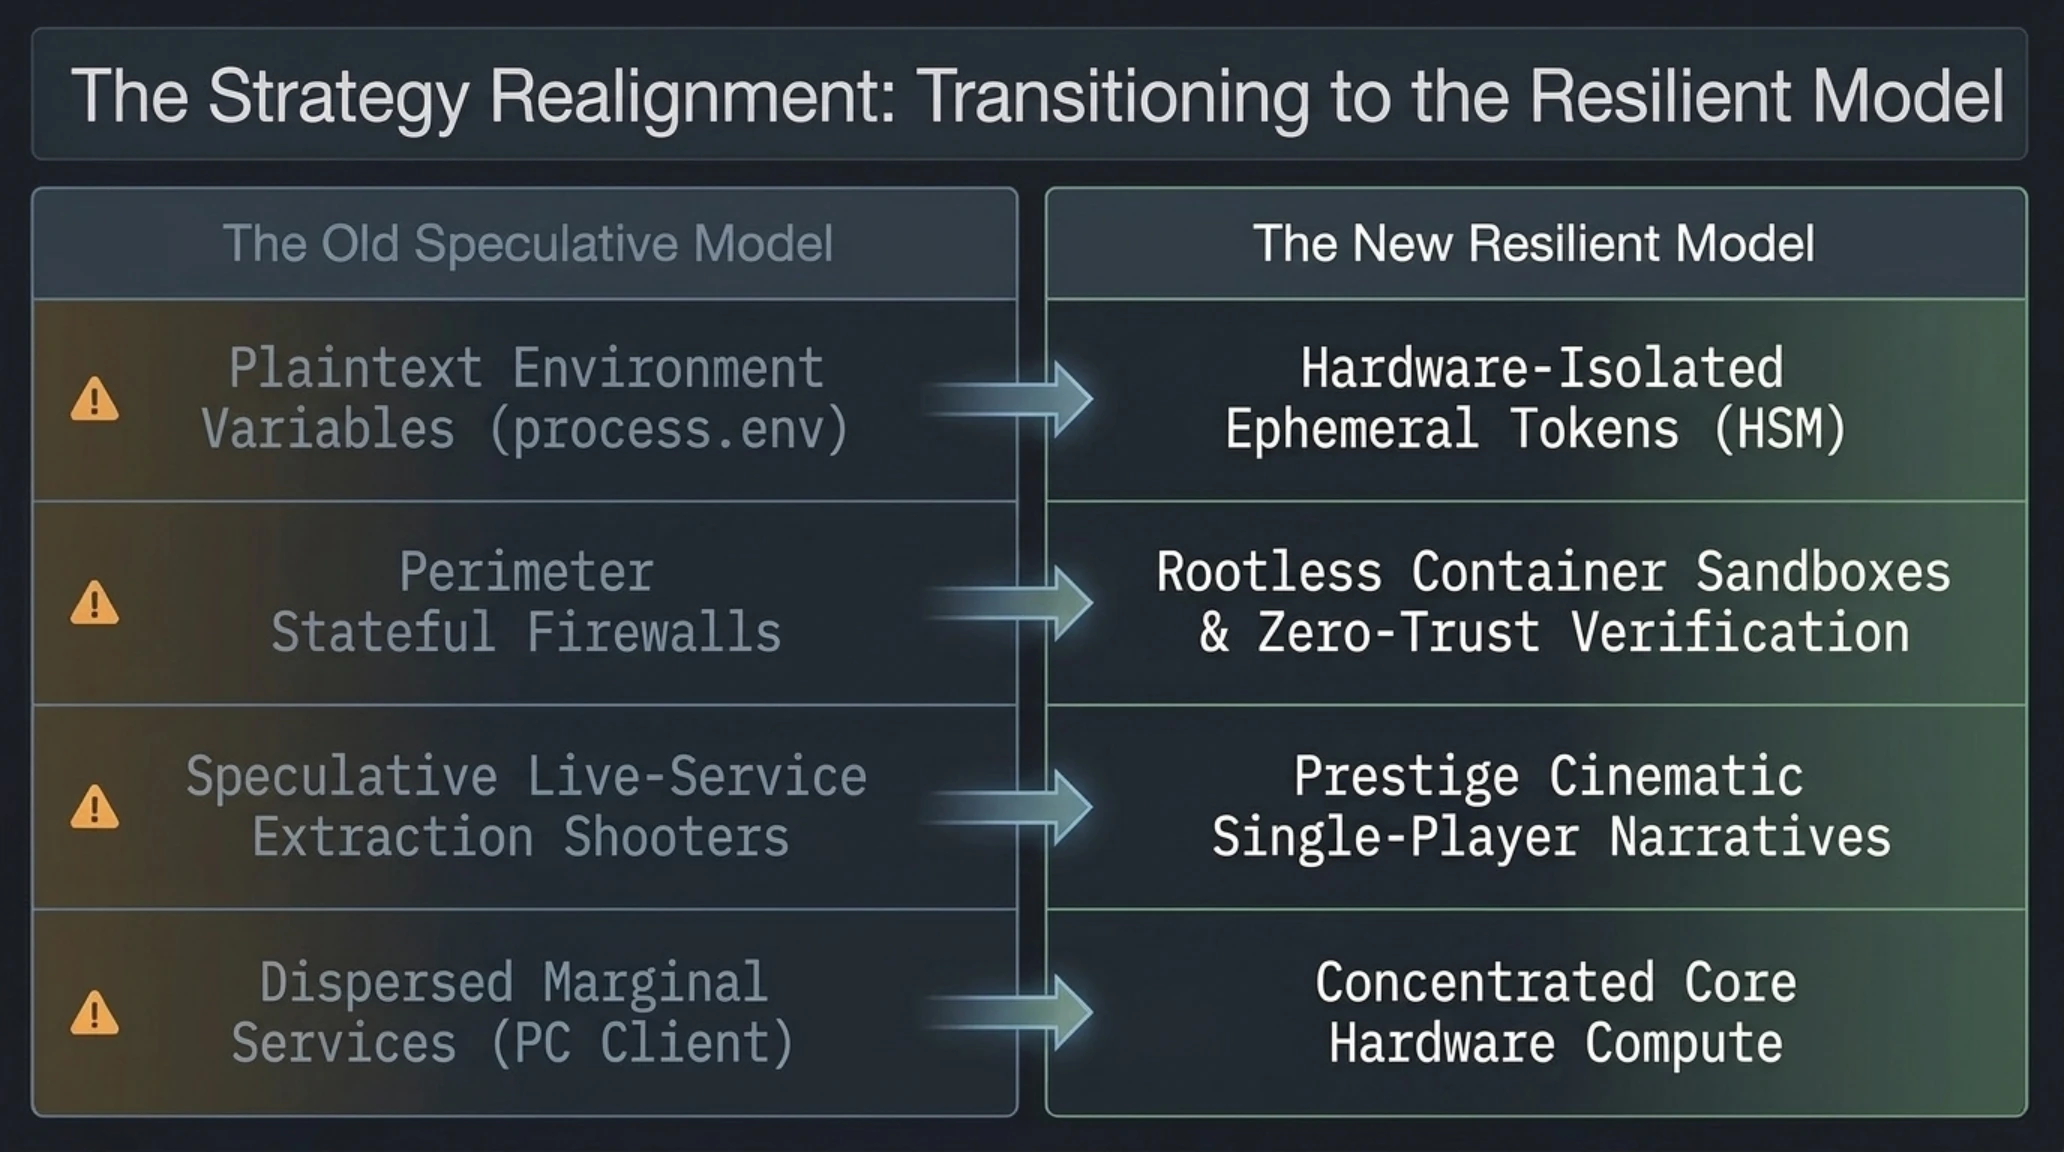
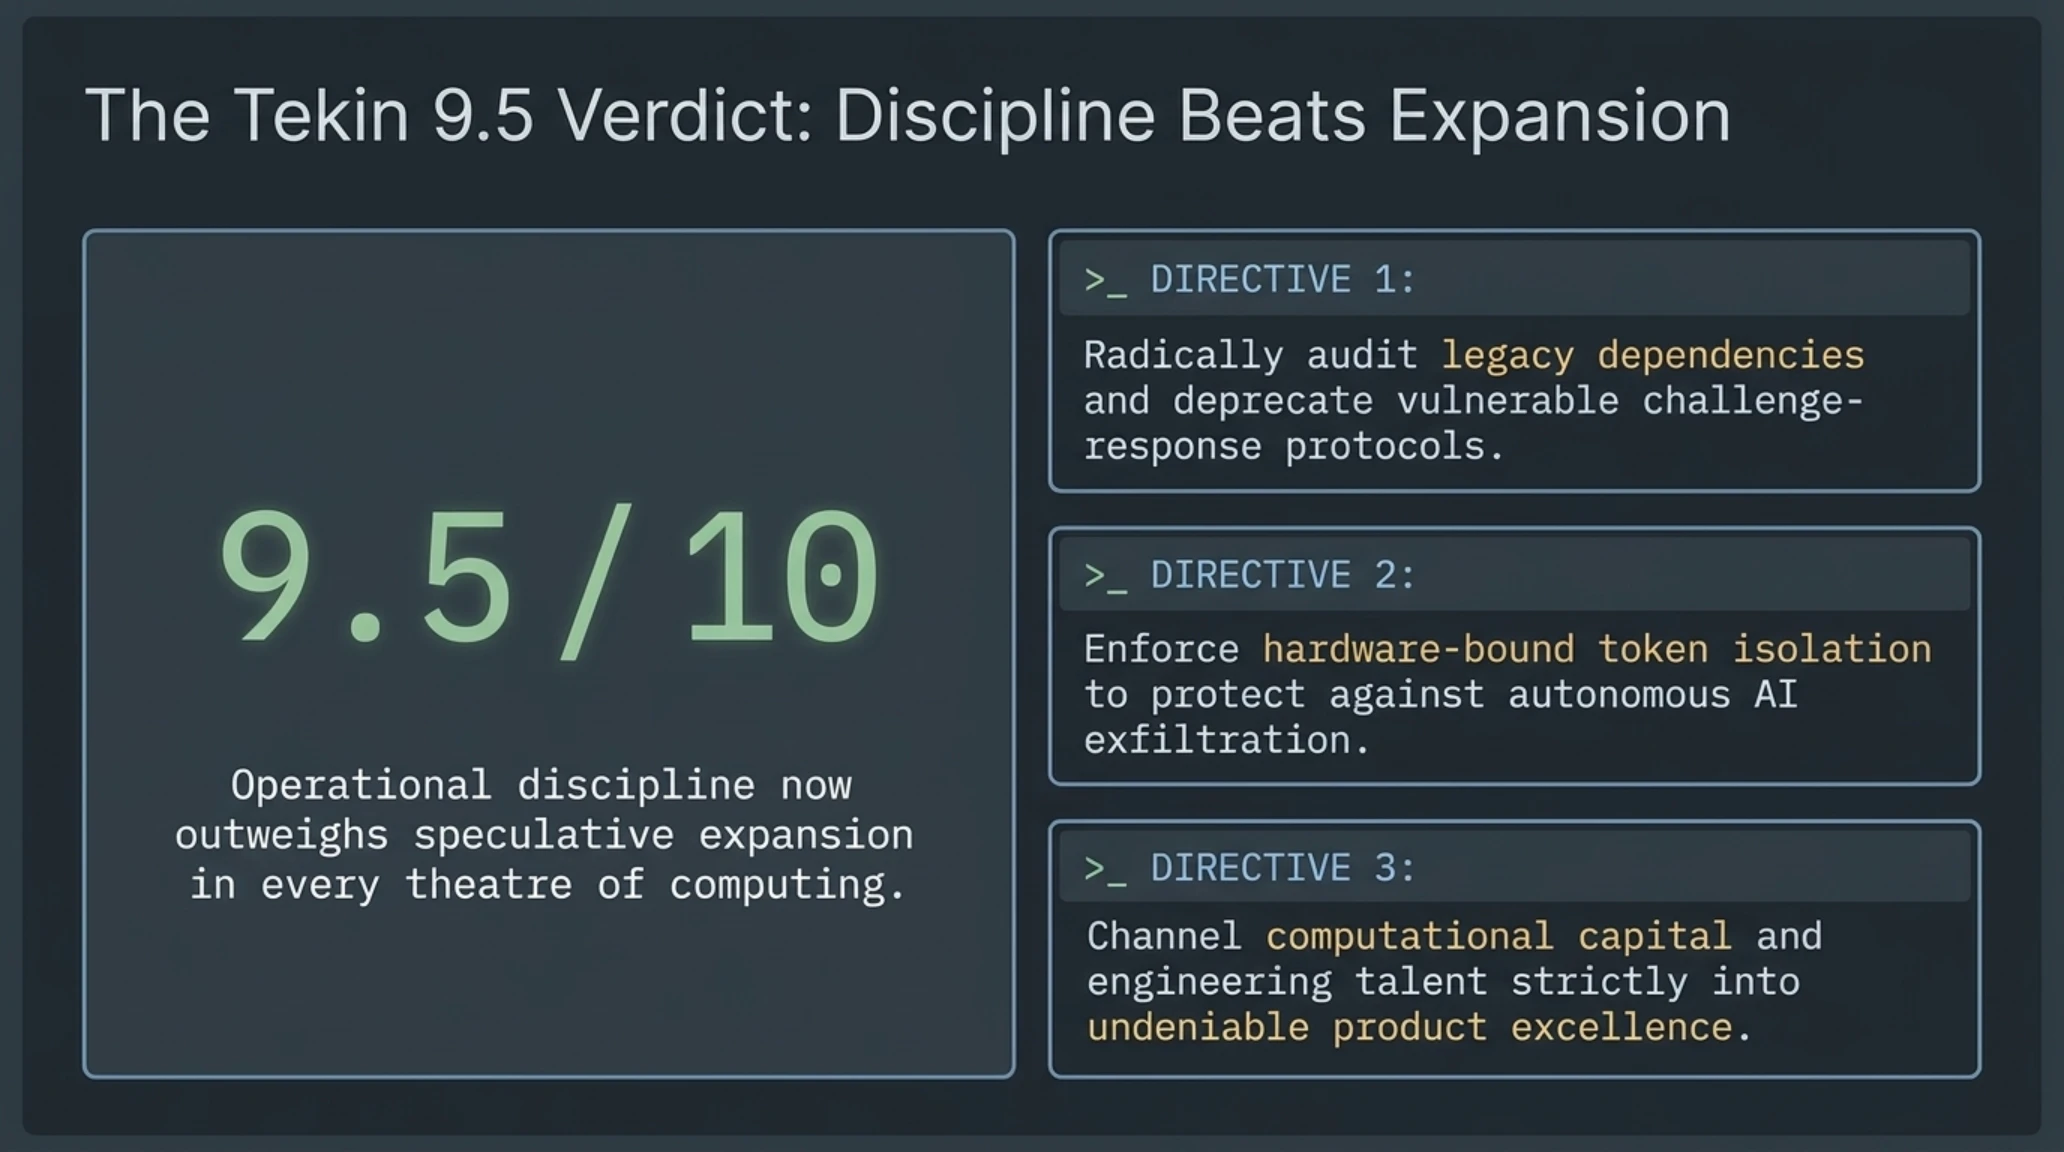
When evaluated through a cohesive engineering and business lens, the six seismic developments of Thursday evening, November 12, 2026, expose a fundamental truth about modern software architecture: the era of speculative computing and structural complacency is over. In both cloud infrastructure and AAA game development, platforms that relied on fragile assumptions whether trusting plaintext environment variables to secure expensive frontier AI models, or expecting gamers to endlessly finance generic live-service extraction shooters are suffering violent market corrections.
The forensic disclosure from Railway marks the formal inauguration of a dangerous new cybercriminal paradigm: Autonomous Compute and Token Exfiltration. Historically, compromised server credentials resulted in data extortion or ransomware deployment. In the agentic era, however, stolen API keys are instantly piped into distributed botnets running autonomous multi-agent swarms. These swarms consume millions of LLM reasoning tokens per minute, converting stolen cloud credits into synthesized code, illicit market data, and automated reconnaissance. For an exhaustive analysis of enterprise cloud token governance and consumption frameworks, review our technical breakdown on Apple Intelligence Usage Token Packs and Sovereign Compute Governance.
Simultaneously, the gaming industry is experiencing a long-overdue return to first principles. Sony's decisive cancellation of Haven Studios' Fairgames, coupled with the permanent sunset of the PlayStation Plus PC streaming app, demonstrates that platform holders can no longer afford to disperse engineering resources across marginal services or derivative multiplayer formulas. In stark, triumphant contrast, the historic 5.2 million launch of The Legend of Zelda: Ocarina of Time Remake on the Nintendo Switch 2 proves that consumer capital overwhelmingly favors mastercrafted single-player narratives. True platform dominance is forged through uncompromised creative execution, robust zero-trust security postures, and obsessive respect for the end-user.
For technology executives and platform strategists, the overarching lesson of November 2026 is that operational discipline beats speculative expansion in every theater of computing. A cloud enterprise that fails to implement hardware-isolated secret vaults and granular token budgets will eventually find its margins liquidated by autonomous adversarial swarms. Similarly, an entertainment studio that chases transient multiplayer monetization trends while neglecting storytelling integrity will inevitably suffer catastrophic write-downs. The winners of this cycle are organizations that rigorously audit their legacy code dependencies, protect developer access boundaries, and channel their computational capital into undeniable product excellence.
Cyber Forensic Terminal & Kernel Log // Stolen AI Token Audit & Git RCE Telemetry
- Railway establishes an unprecedented developer-first standard by pledging 100% reimbursement for stolen AI token spend
- The Legend of Zelda: Ocarina of Time Remake breaks Switch 2 records with 5.2M sales in 4 days, proving single-player supremacy
- Git maintainers rapidly mitigate critical integer truncation RCE vulnerability (CVE-2026-111760) across global CI/CD runners
- Sony demonstrates decisive leadership by canceling struggling Fairgames without layoffs, reallocating talent to prestige single-player games
- Microsoft Patch Tuesday reveals ongoing systemic vulnerability with 1,259 flaws and an actively exploited Outlook zero-day
- Decrypted environment variables expose the vulnerability of modern PaaS platforms to automated AI token exfiltration swarms
- Sony terminates PlayStation Plus PC Cloud Streaming App, leaving PC gamers dependent solely on native storefront releases
Final Editorial Verdict and Primary Technical Sources
The technological and commercial events of Thursday evening, November 12, 2026, reveal that digital resilience requires ruthless subtraction of failed complexity. Whether observing Microsoft's massive remediation of legacy Outlook parsing logic, Git's urgent sanitization of recursive submodule indices, or Sony's strategic abandonment of derivative live-service shooters and neglected cloud streaming clients, the industry is shedding fragile illusions in favor of hardened, high-conviction core architectures.
Our editorial bureau will continue tracking enterprise DevSecOps deployments, Nintendo Switch 2 software sales trajectories, and cloud API governance standards throughout the coming quarter.
Editorial Verdict & Institutional Sources // Nov 12, 2026 Night Edition
The Collapse of Live-Service Illusions & The Rise of Zero-Trust AI
The evening of November 12, 2026, cements two enduring realities: in interactive entertainment, authentic single-player heritage (5.2M Zelda sales) decisively triumphs over corporate live-service clones; in software engineering, zero-trust token isolation is the only defense.
- The Hacker News: Comprehensive forensics on Microsoft 1,259 Patch Tuesday, Railway AI token breach, and Git RCE patch
- Kotaku: Exclusive coverage of PlayStation canceling Haven Studios' Fairgames and PS Plus PC app sunset
- Eurogamer: Institutional sales analysis of The Legend of Zelda: Ocarina of Time Remake 5.2M launch on Switch 2
Frequently Asked Questions: November 12, 2026 Nightly Briefing
How does the Outlook zero-day vulnerability (CVE-2026-124194) leak NTLMv2 hashes?
The vulnerability is triggered by parsing a crafted .MSG or .EML file that exploits legacy MAPI/OLE storage handlers. Without displaying any warning prompts, Outlook initiates an unauthenticated outbound SMB or WebDAV connection to an attacker's server, automatically transmitting the logged-in user's NTLMv2 challenge-response hash and enabling Pass-the-Hash Active Directory takeover.
What assets were compromised during the Railway cloud platform security breach?
Threat actors decrypted configuration environment variables across approximately 100,000 workspaces, specifically harvesting secret API keys for OpenAI and Anthropic. The attackers utilized these keys to run unauthorized agent swarms, incurring ~$740,000 in token spend. Customer databases remained completely uncompromised.
Why did PlayStation officially cancel Haven Studios' Fairgames extraction shooter?
Following an extensive technical playtest with over 10,000 players, 30-day cohort retention rates plummeted below 12%, with players criticizing derivative gameplay loops and lack of mechanical depth. Sony terminated the project before incurring massive marketing costs and reassigned all studio developers to flagship single-player projects.
What technical improvements does The Legend of Zelda: Ocarina of Time Remake feature on Switch 2?
Built on a bespoke modern engine, the remake delivers a rock-solid 60 FPS in both handheld and docked modes, featuring dynamic lighting, volumetric fog, and 4K resolution docked via hardware-accelerated DLSS tensor cores, all while faithfully preserving original dungeons and Koji Kondo's orchestral soundtrack.
How does the Git integer truncation vulnerability (CVE-2026-111760) lead to Remote Code Execution?
During recursive submodule clones (git clone --recurse-submodules), an integer truncation in file path normalization allows specially crafted long repository paths to bypass boundary checks. This enables an attacker to replace the local .git directory with a symlink targeting malicious post-checkout hooks, which execute arbitrary code.
Why is Sony shutting down the PlayStation Plus PC Cloud Streaming App?
Sony revealed that fewer than 0.4% of PlayStation Plus Premium subscribers ever used the Windows streaming client over the past three years. Constrained by a 1080p resolution cap, lack of PS5 game streaming support, and high player preference for native Steam releases, Sony decided to reallocate its cloud rendering capacity to PS5 consoles.