Night Tech Energy Boost
End of a busy day with hot news from security and gaming world.
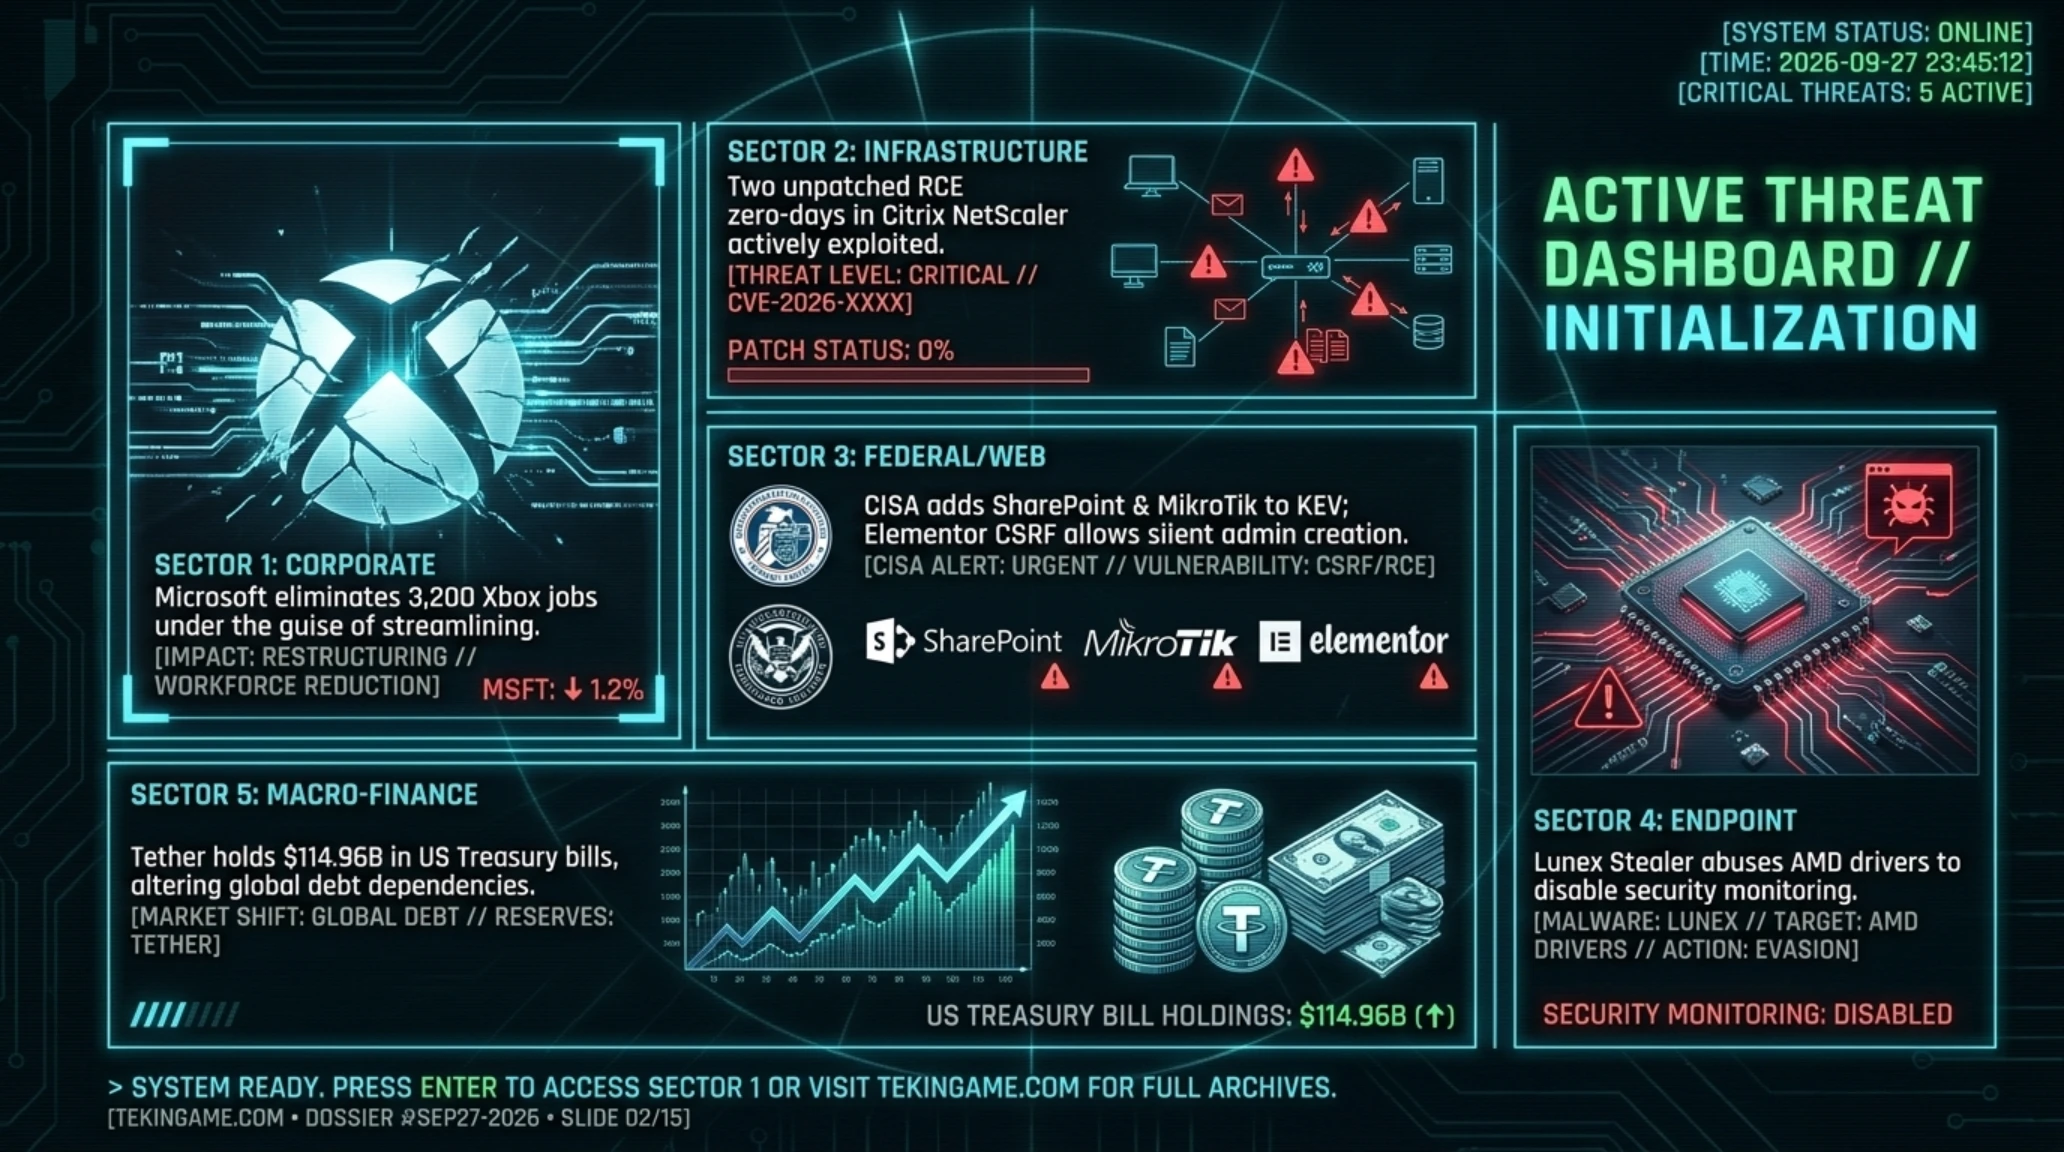
- 🎮Massive Xbox Layoffs- 3200 jobs cut in Microsoft restructuring
- 🎧Citrix Zero-Day Active- Two unpatched RCE under attack
- 🚀CISA Urgent Alert- SharePoint and MikroTik added to KEV
- 🗡️Elementor Under Threat- CSRF allows admin account creation
- 📰Lunex Stealer Emerges- AMD driver abuse technique
- ⚔️Tether Financial Power- $114B US Treasury holdings
A tense night in the tech world unfolds. Microsoft is laying off thousands from Xbox while calling it great streamlining, two critical zero-days in Citrix NetScaler are being actively exploited without patches, CISA added SharePoint and MikroTik vulnerabilities to KEV with urgent warnings, a CSRF flaw in Elementor allows arbitrary admin account creation, Lunex malware abuses AMD drivers to bypass security, and Tether with $114 billion in US Treasury holdings has made Washington dependent.
Quick Look
- Microsoft eliminating 3200 Xbox jobs in streamlining process
- Two unpatched RCE zero-days in Citrix NetScaler actively exploited
- CISA added SharePoint and MikroTik vulnerabilities to KEV
- CSRF flaw in Elementor allows arbitrary admin account creation
- Lunex Stealer uses AMD driver to disable security monitoring
- Tether holds $114.96B in US Treasury bills, one of largest debt holders
Microsoft Praises Xbox Streamlining as Thousands Get Laid Off
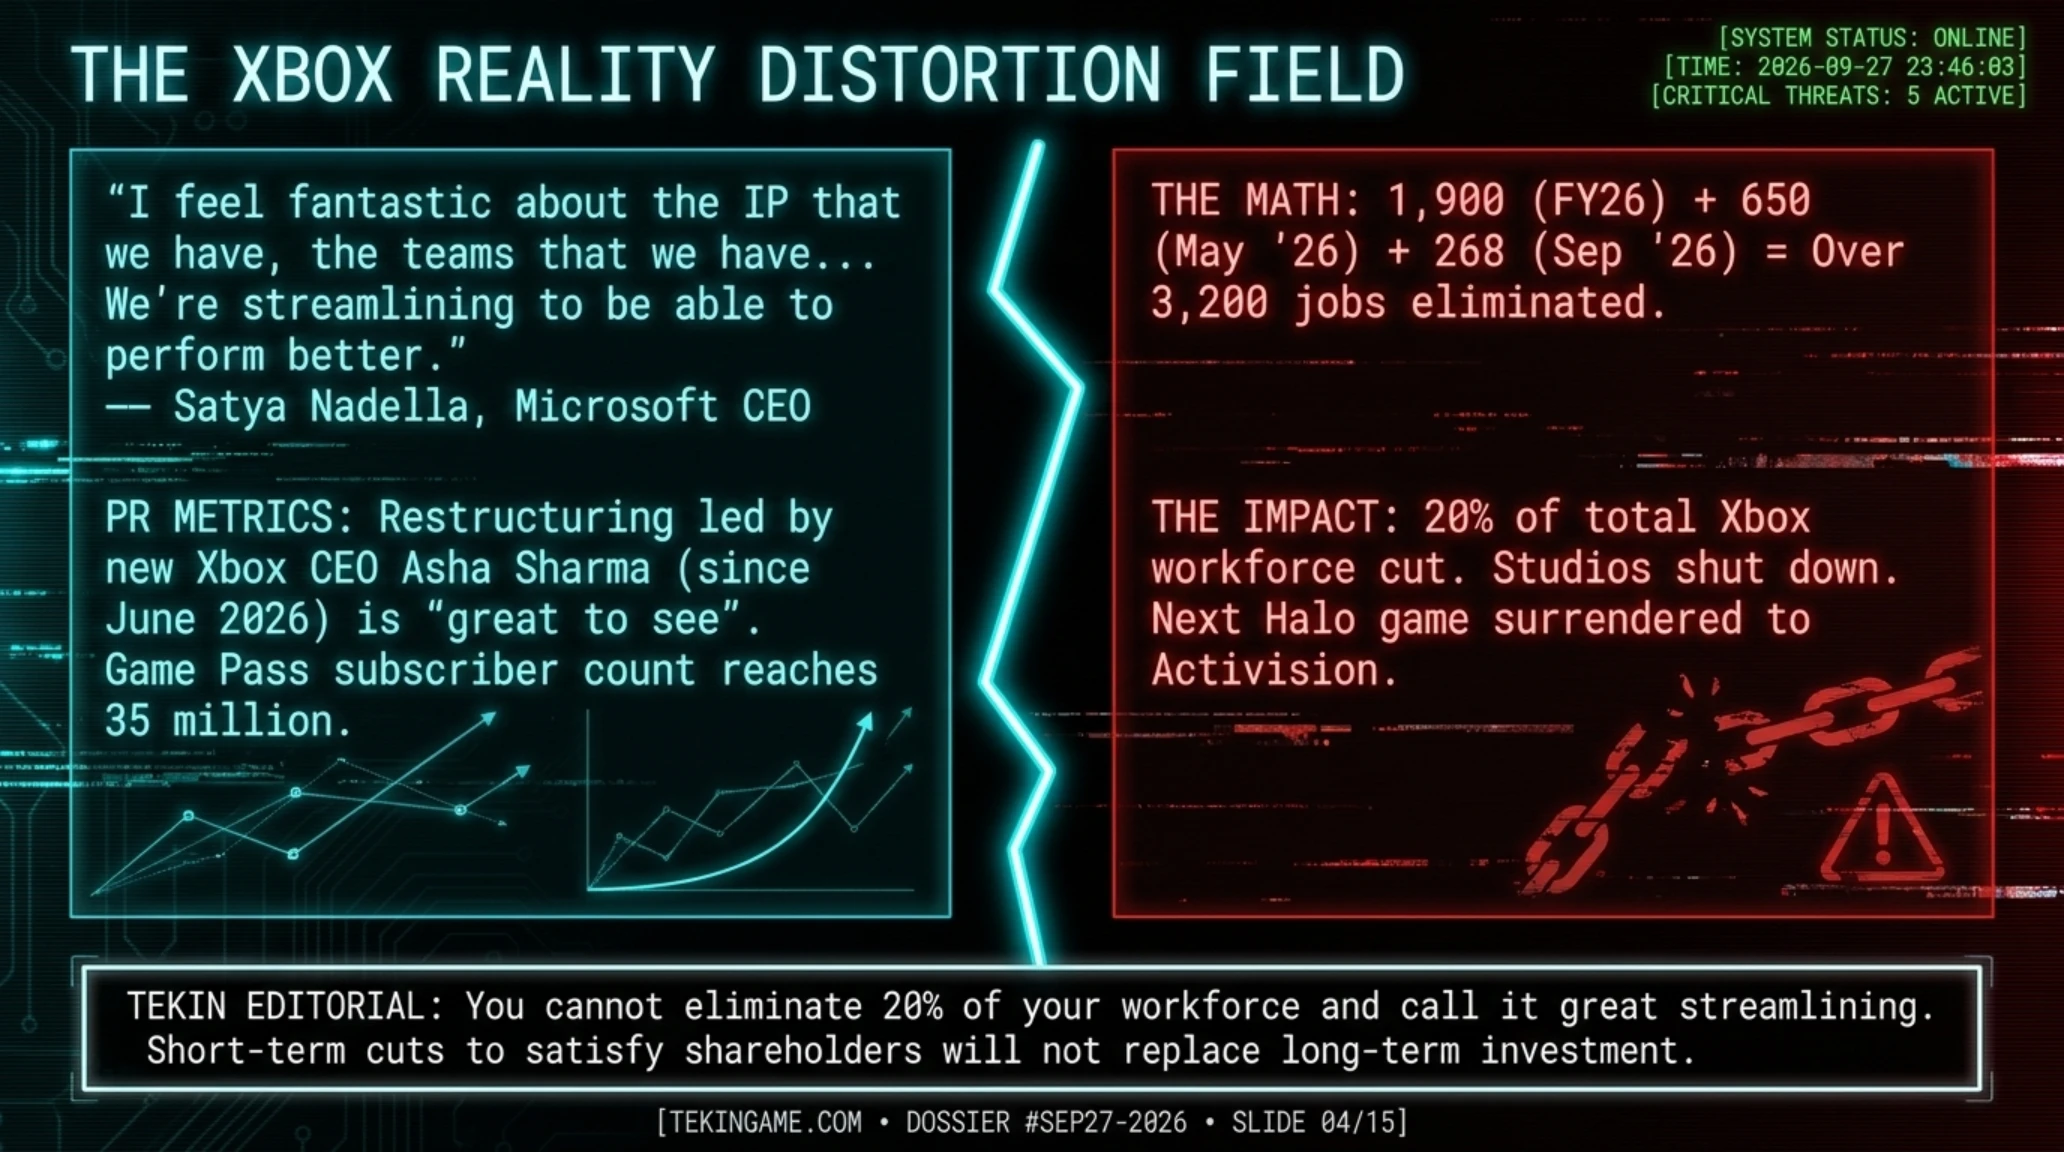
Microsoft CEO Satya Nadella called the restructuring process led by new Xbox CEO Asha Sharma "great to see" during a financial analyst meeting - just days after 268 more Xbox employees were laid off. This latest wave is part of a broader program eliminating 3,200 jobs (about 20% of total Xbox workforce) across fiscal years 2026 and 2027.

Nadella also stated he feels "fantastic" about Xbox IP portfolio and predicts the gaming division will grow in fiscal 2027 (July 2026 through June 2027). However, these statements come as some studios have been shut down and the next Halo game has been moved to Activision.
Xbox Restructuring Details
Since Asha Sharma took over as new Xbox CEO in June 2026, extensive restructuring has begun:
- First wave: Approximately 1,900 people in fiscal 2026
- Second wave: 650 people in May 2026
- Third wave: 268 people in September 2026
- Total: Over 3,200 jobs eliminated
Gaming Community and Employee Reactions
These layoffs have triggered harsh reactions from the gaming community and former employees. Many laid-off workers have stated on social media that these decisions are not only ruthless but also strategically wrong. Some analysts believe Microsoft is destroying the very studios it paid heavily to acquire.
Meanwhile, Nadella emphasized in the financial meeting that Microsoft will continue investing in gaming, but with focus on efficiency and profitability. He also noted that Game Pass continues growing with subscriber count reaching 35 million.
Two Critical Zero-Day RCEs in Citrix NetScaler Under Active Exploitation
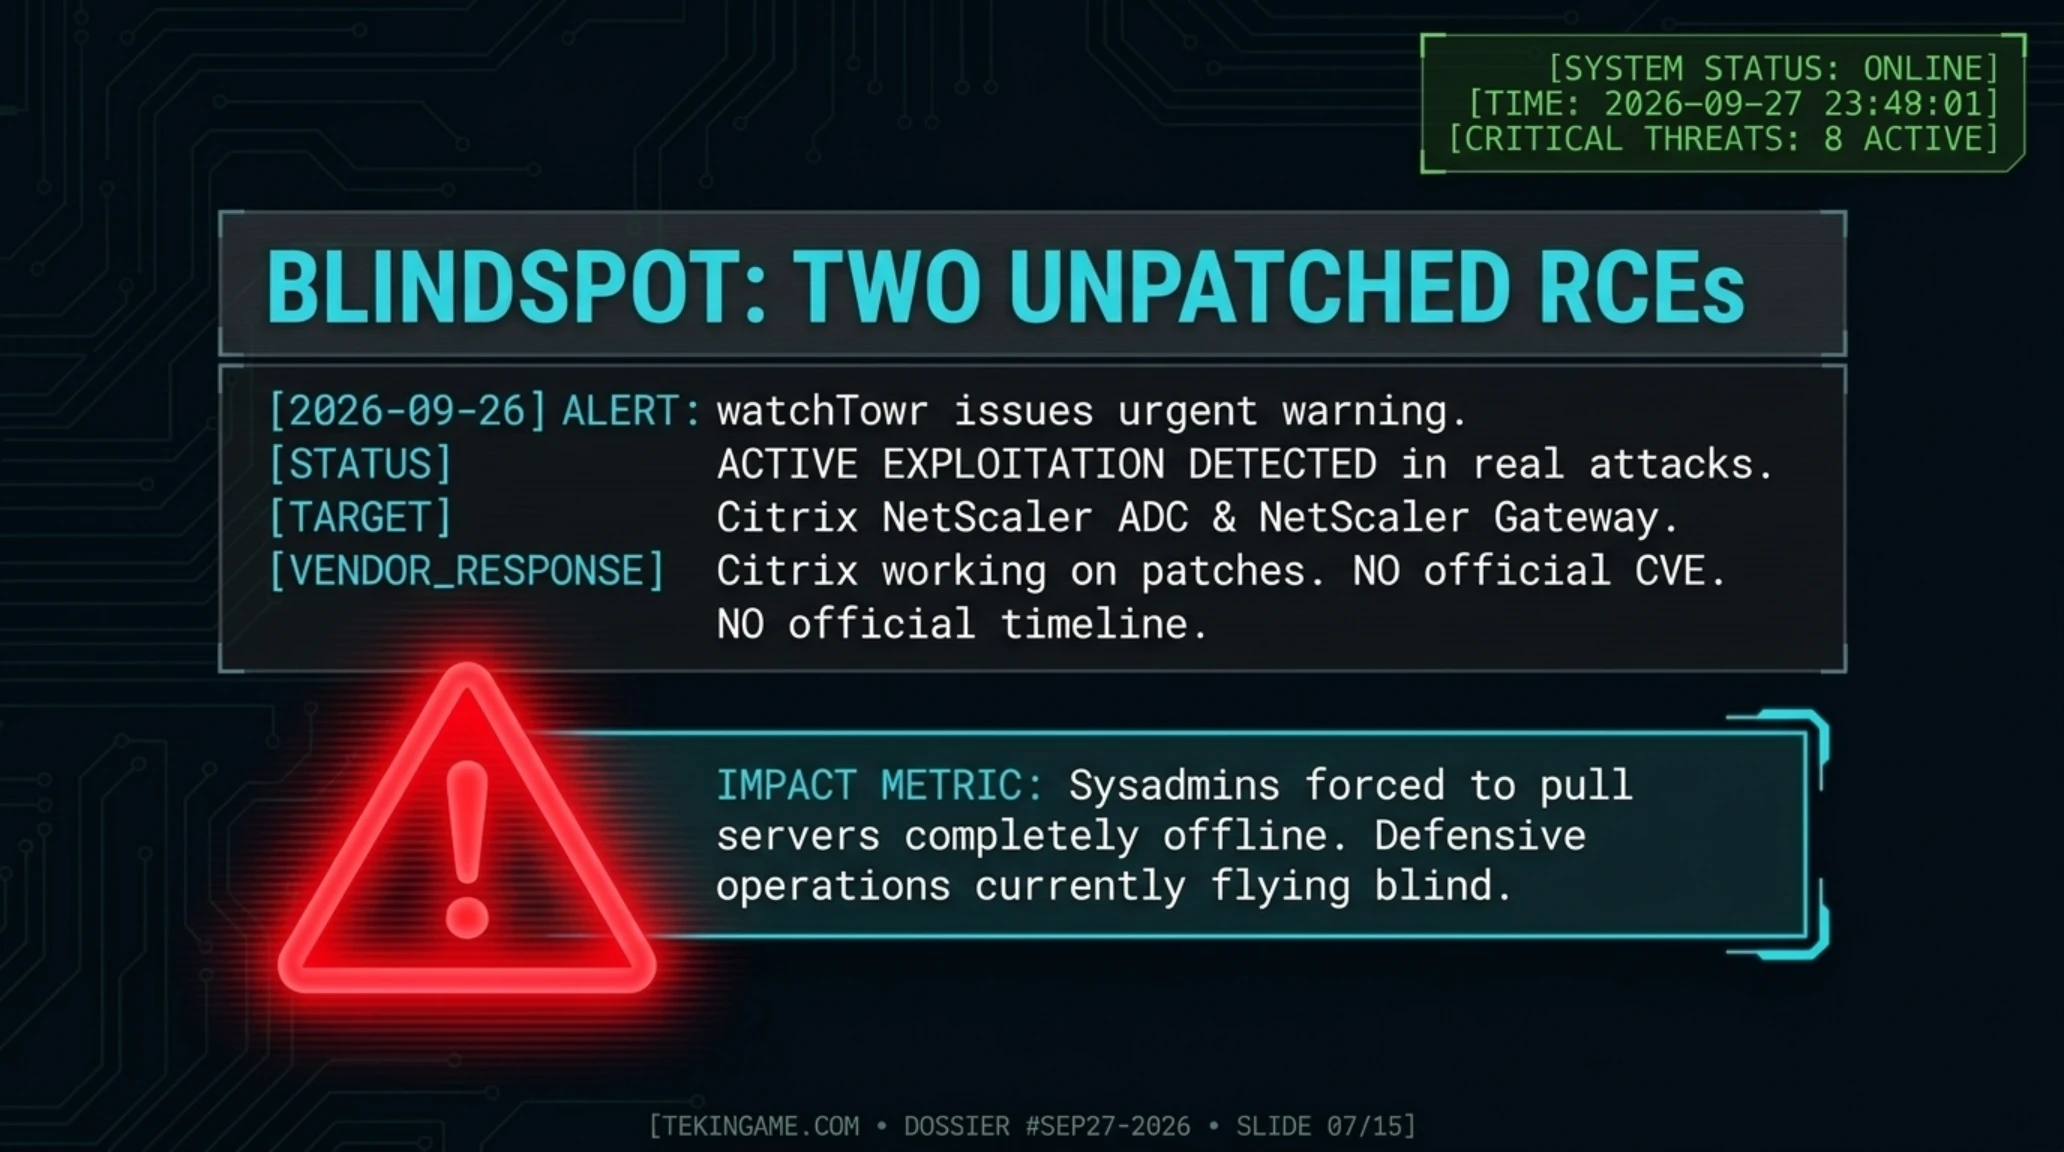
Security firm watchTowr issued an urgent warning on September 26: two unpatched zero-day vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway allowing remote code execution (RCE) are currently being actively exploited in real attacks.

Interestingly, Citrix has not yet officially confirmed these flaws and has not released any patches or security updates. This situation has forced some system administrators who know their systems are at risk to decide to take their NetScaler servers completely offline while waiting for patches.
What Is NetScaler and Why It Matters?
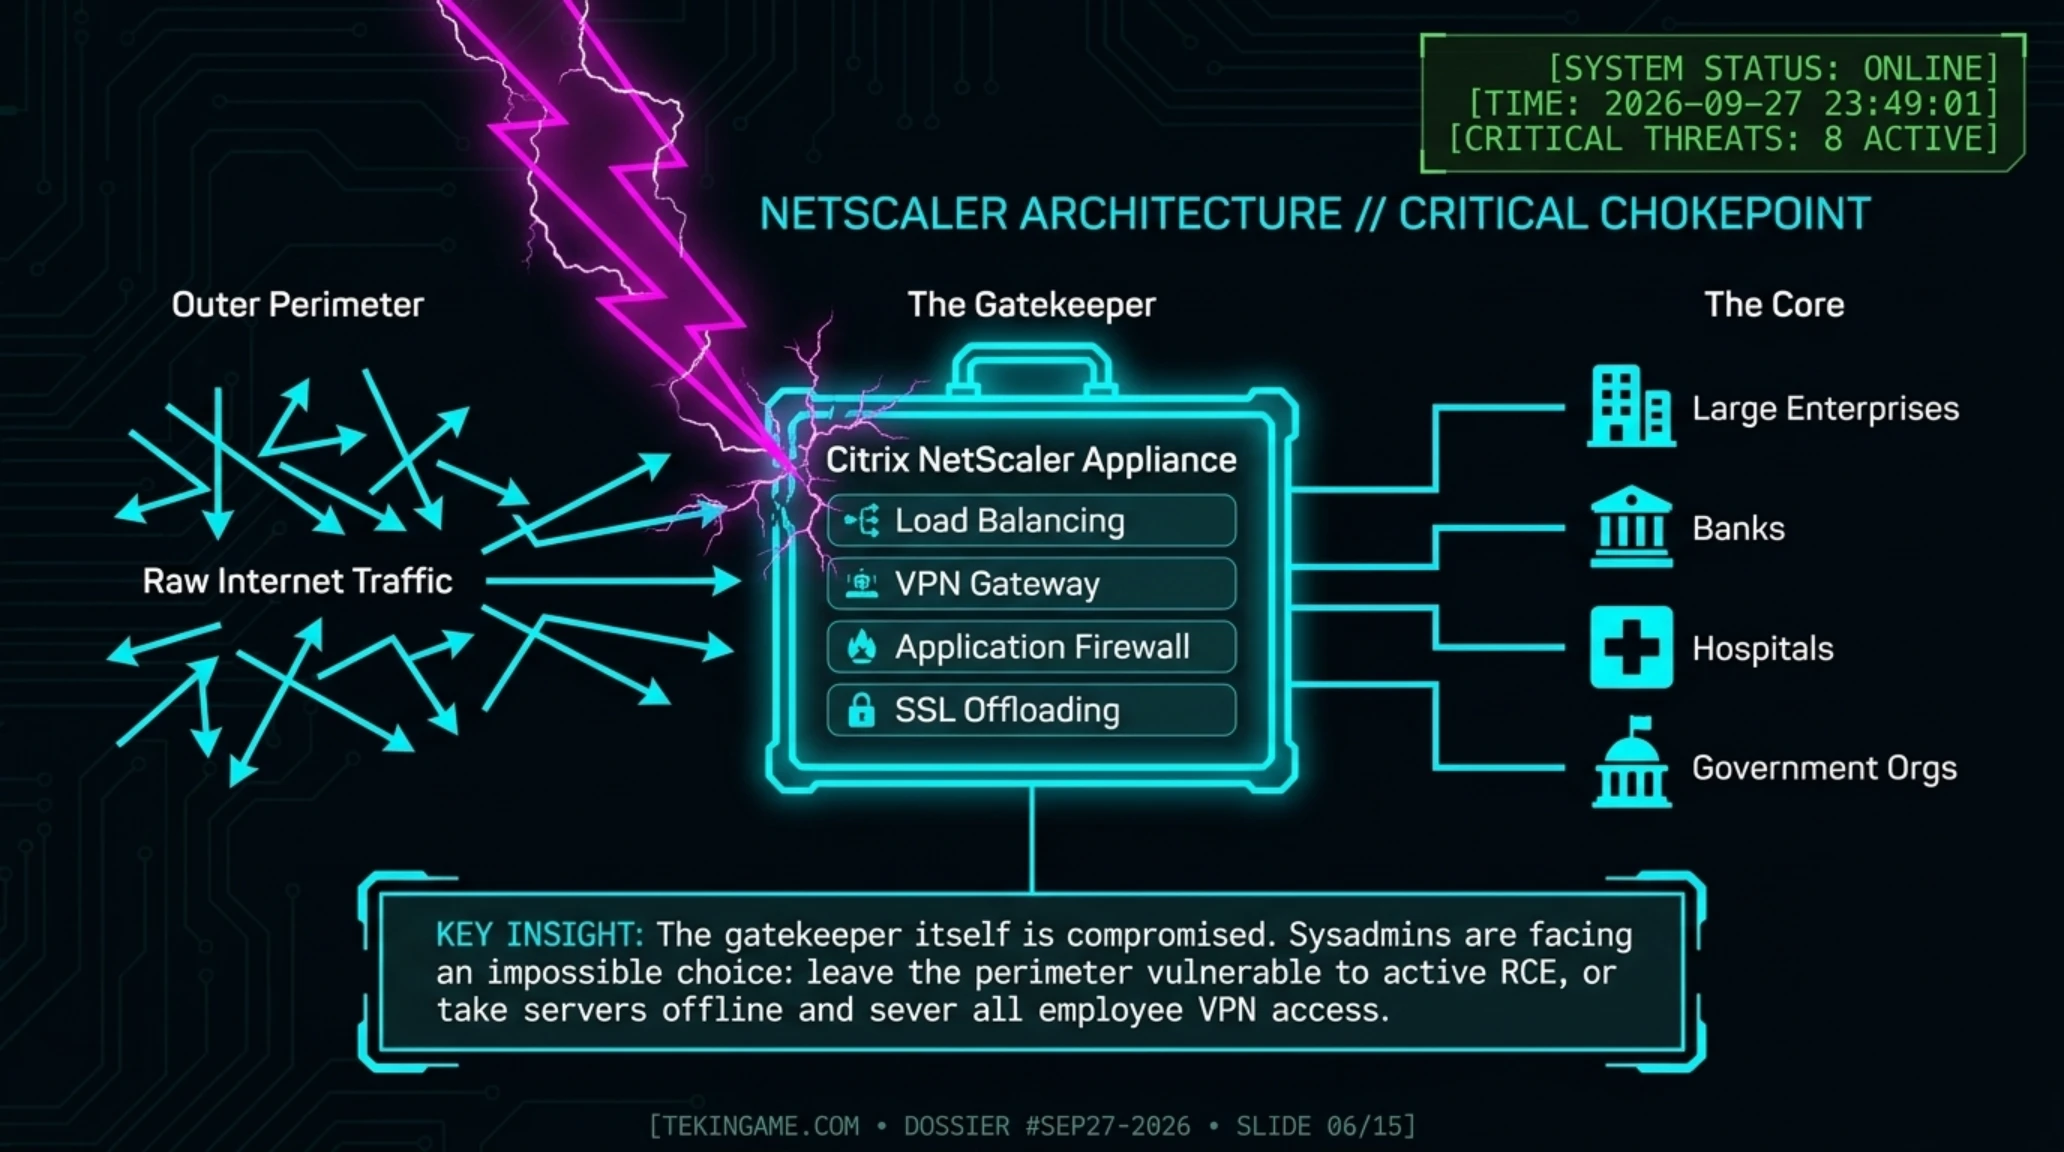
Citrix NetScaler is a highly popular network appliance used for:
- Load balancing: Traffic distribution and optimization
- VPN gateway: Secure remote corporate access
- Application firewall: Deep perimeter inspection
- SSL offloading: Cryptographic acceleration
These appliances are deployed across major enterprise networks, banks, hospitals, and government agencies, making zero-day flaws exceptionally hazardous.
System Administrator Reactions and Attacker Tactics
In security forums and Reddit, system administrators have reported seeing active attempts to breach their NetScaler servers. Some of them, upon observing suspicious logs, decided to shut down the service until patch release - even if it means cutting off employee VPN access.
watchTowr has not published precise technical details of these vulnerabilities to prevent wider exploitation, but stated Citrix is working on patches. However, as of this writing (September 27), no official timeline for patch release has been announced.
CISA Adds SharePoint and MikroTik Vulnerabilities to KEV
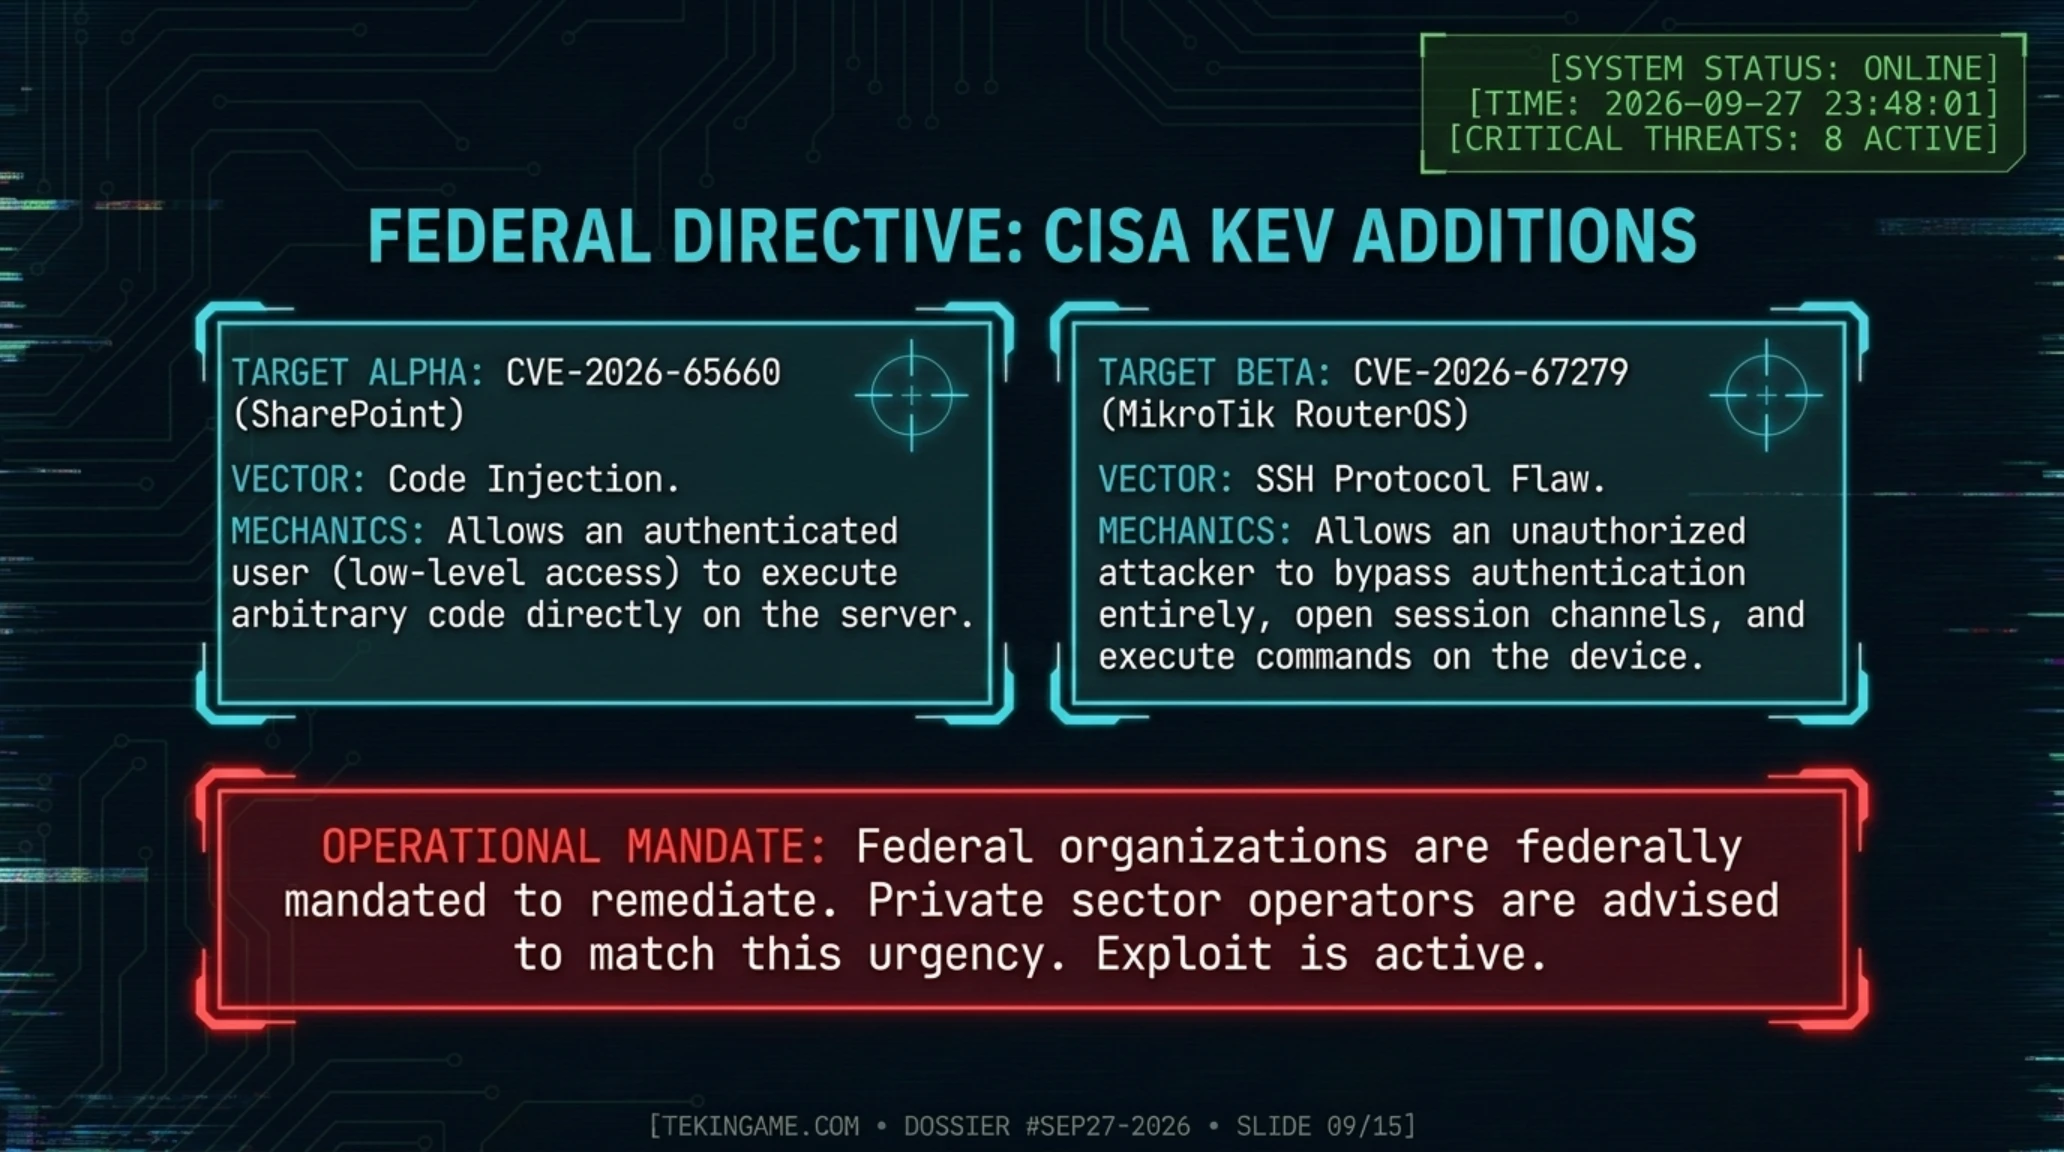
The Cybersecurity and Infrastructure Security Agency (CISA) added two actively exploited security vulnerabilities to the Known Exploited Vulnerabilities (KEV) catalog on September 25, issuing urgent warnings for federal organizations.

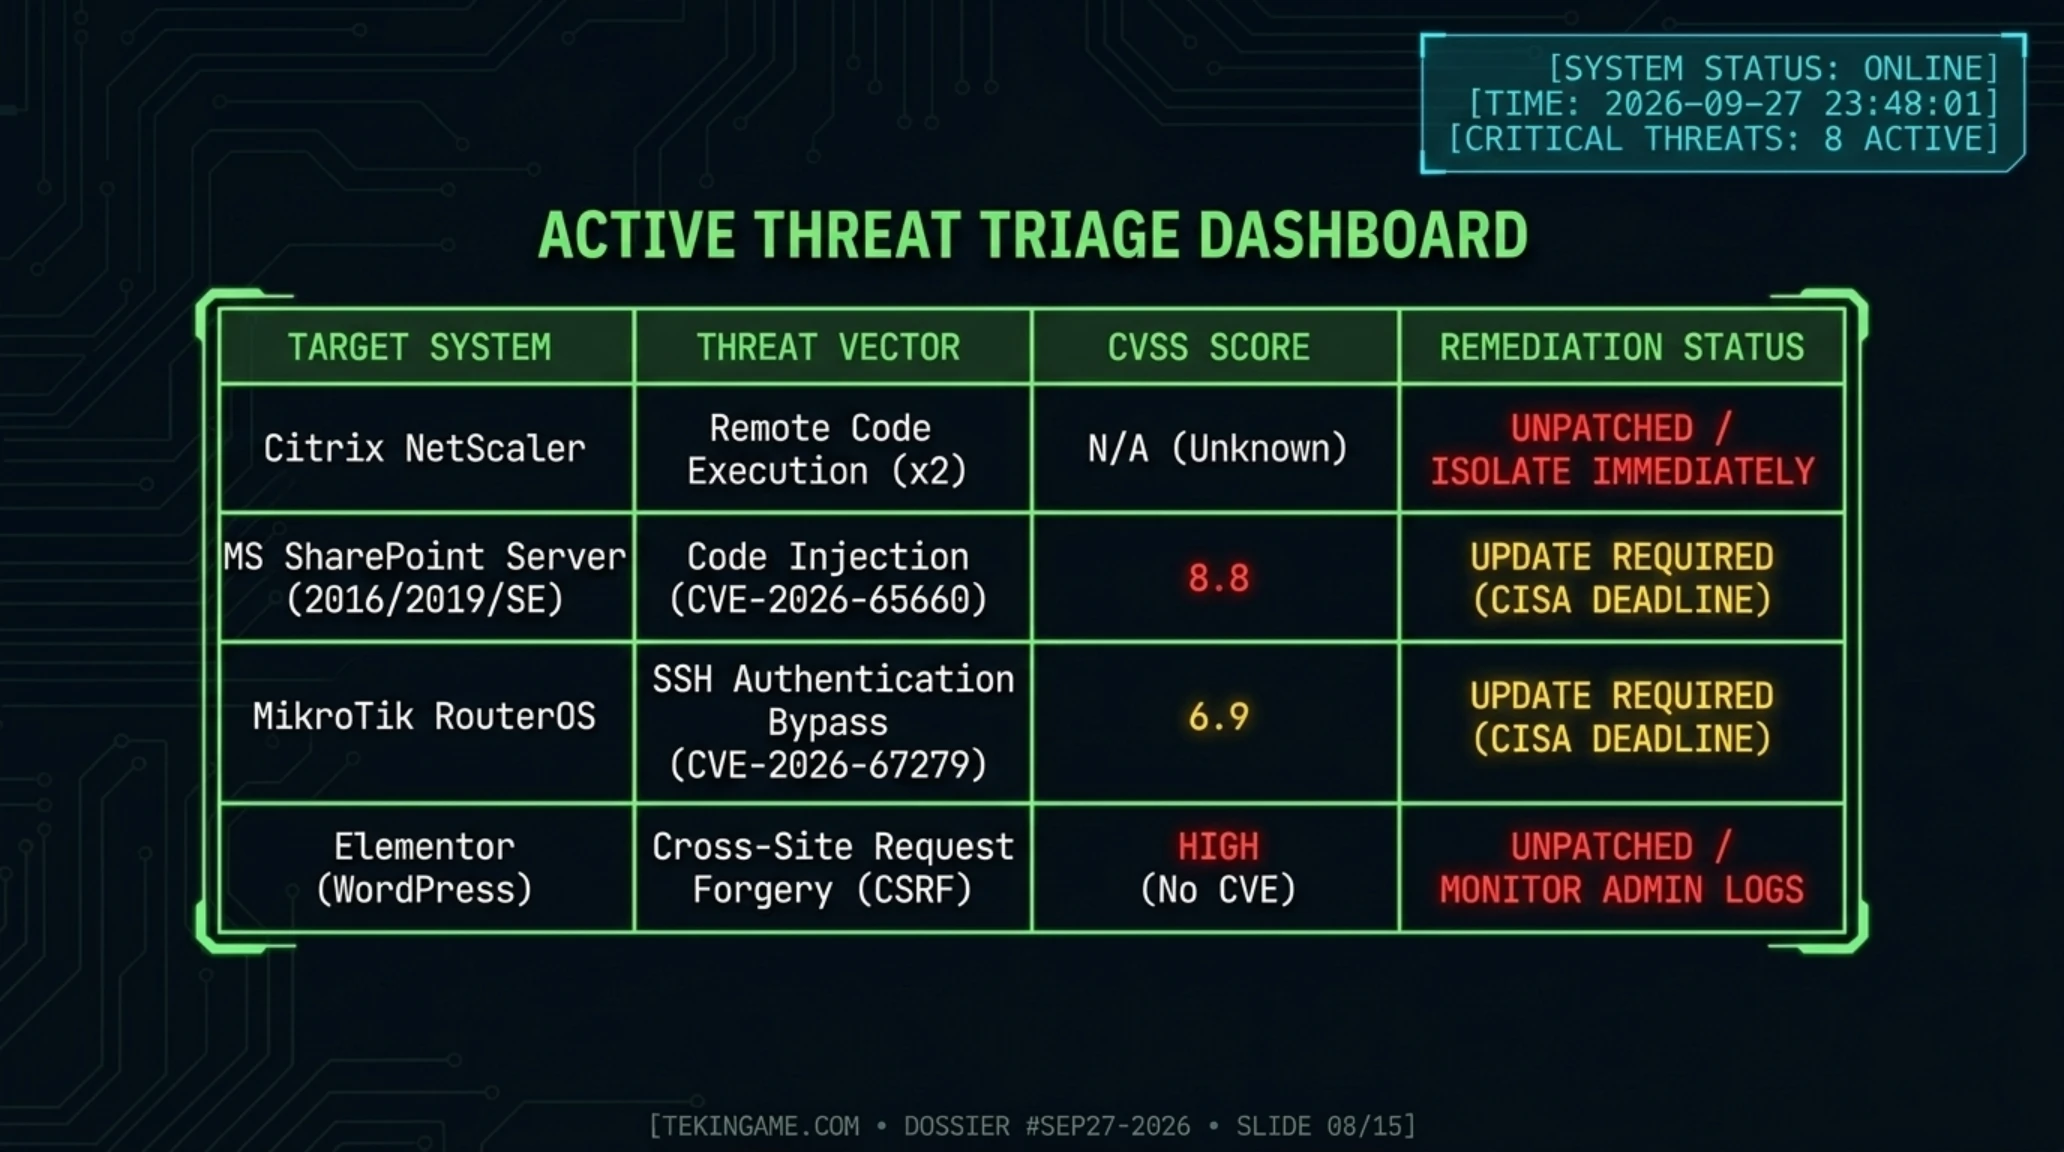
The first vulnerability, CVE-2026-65660 with CVSS score 8.8, is a code injection flaw in Microsoft SharePoint Server affecting versions 2016, 2019, and Subscription Edition. This flaw allows an attacker with low-level access (authenticated user) to execute arbitrary code on the server.
The second vulnerability, CVE-2026-67279 with CVSS score 6.9, is an SSH protocol flaw in MikroTik RouterOS. This flaw allows an unauthorized attacker to bypass authentication, open session channels, and execute commands on the device.
What Is KEV and Why It Matters?
The KEV (Known Exploited Vulnerabilities) catalog is maintained by CISA and documents flaws that exhibit:
- Active exploitation: Documented weaponization in real-world attacks
- Operational risk: Direct vectors to compromise critical infrastructure
- Available remediation: Vendor-released security patches
Federal agencies are mandated to remediate these flaws within strict deadlines, and private organizations must treat them with identical urgency.
Remediation Deadlines and Enterprise Impact
Per CISA directives, federal organizations must remediate these two vulnerabilities by September 27–28. This exceptionally short deadline reflects the severity and operational urgency of the situation. While Microsoft previously released patches for SharePoint, extensive telemetry indicates that numerous enterprises have not yet applied the updates.
MikroTik has likewise published stable RouterOS firmware updates. However, with millions of edge MikroTik routing appliances deployed across global SMBs and regional internet providers, automated patch distribution remains fragmented.
Immediate Remediation Directives
- Immediately install patches for on-premise SharePoint Server instances
- Upgrade MikroTik RouterOS appliances to the latest stable release
- Exhaustively audit SSH access logs for anomalous session establishment
- Enforce strict IP access controls and firewall filtering over SSH ports
- Monitor SharePoint server execution environments for unusual payload generation
📚 Classified & Related Dossiers in TekinGame
If you wish to explore beyond this report and delve into cybernetic frontiers and autonomous AI architectures, do not miss these three exclusive deep-dives in the Tekin Garage:
Elementor CSRF Flaw Allows WordPress Admin Account Creation
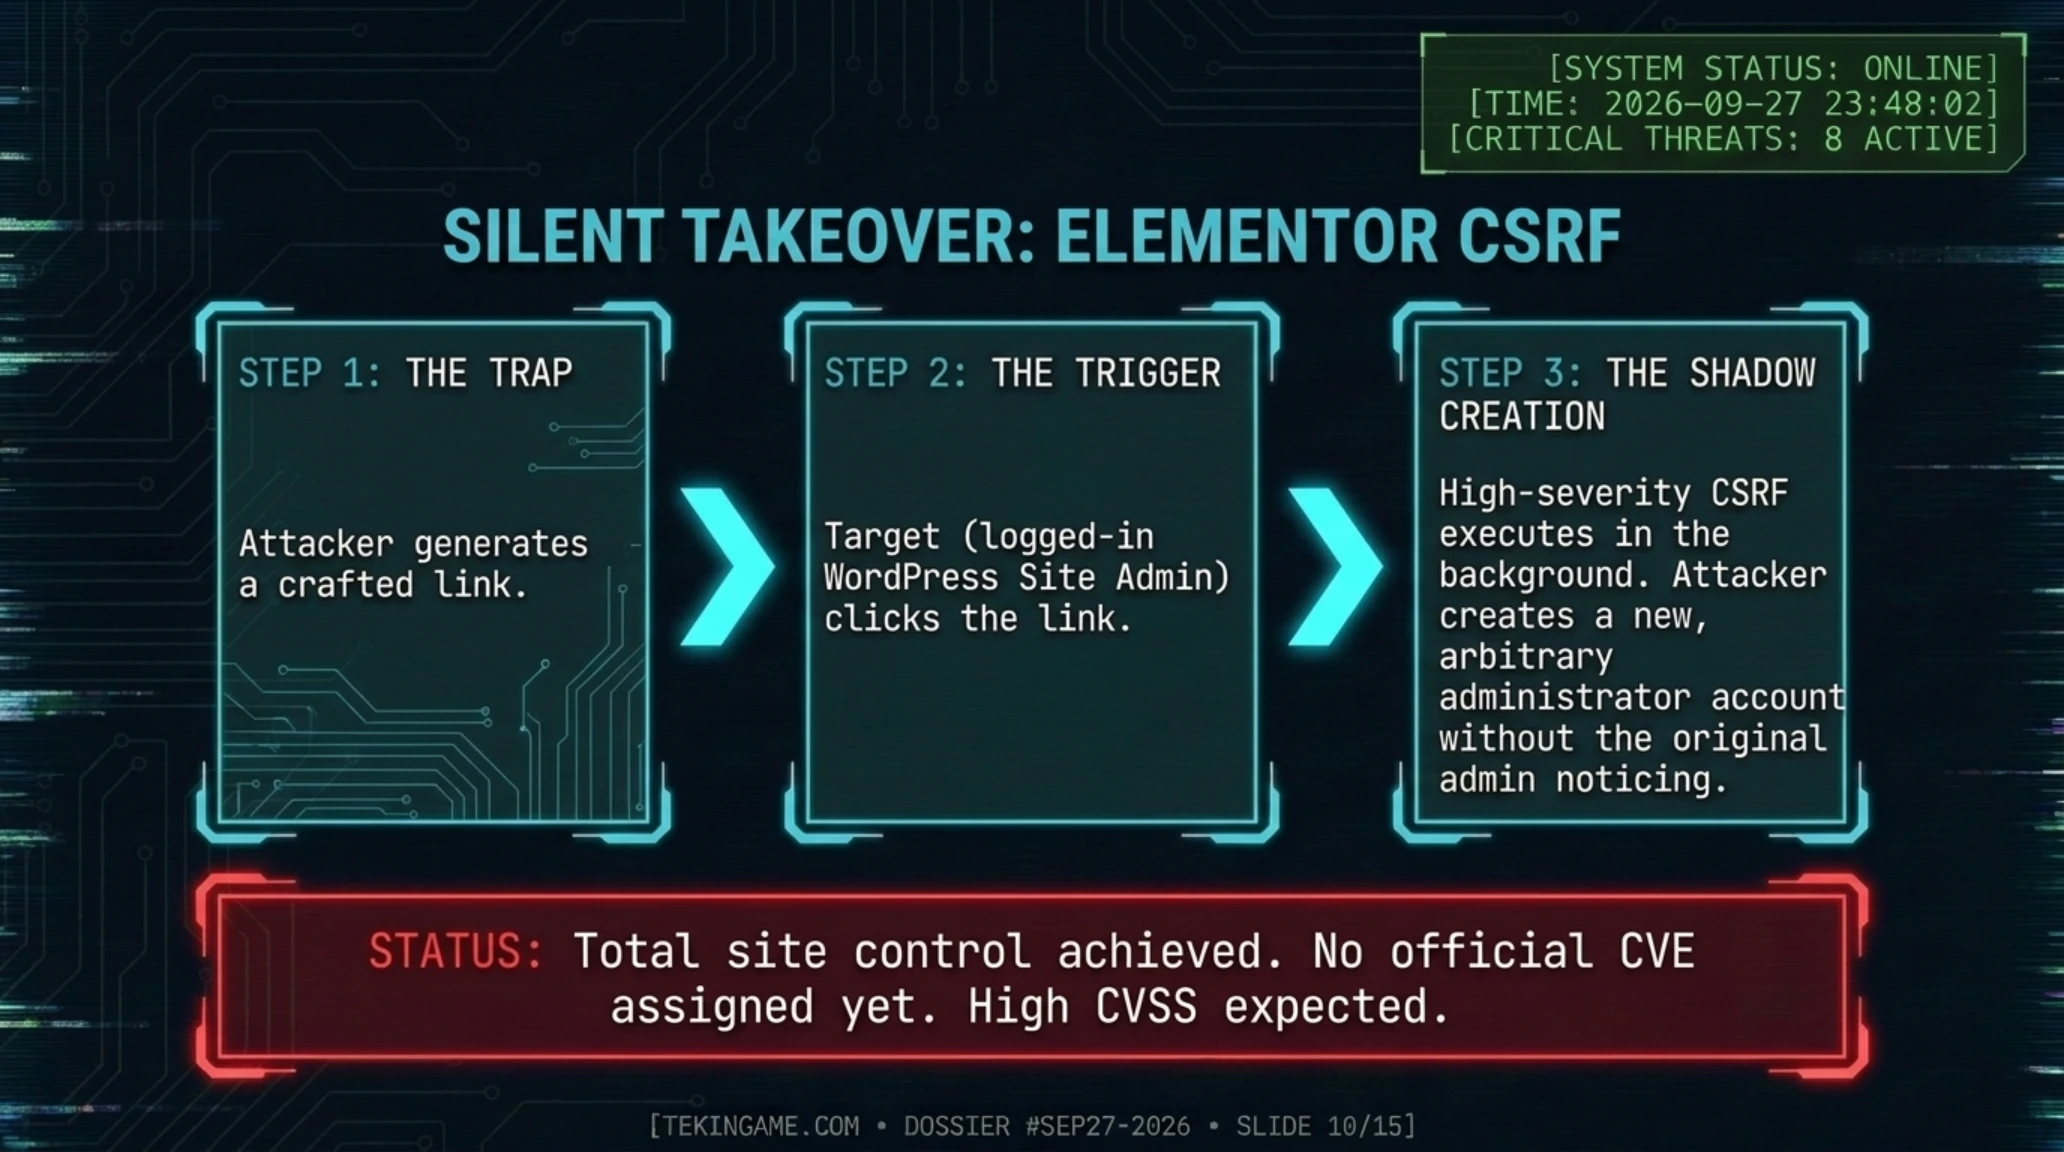
A high-severity Cross-Site Request Forgery (CSRF) vulnerability was discovered in Elementor Website Builder plugin for WordPress that could be exploited by an attacker to create arbitrary administrator accounts and gain complete control over the site.

This flaw has not yet received an official CVE but security researchers have assigned it a high CVSS score. The attack requires a site administrator to click on a crafted link while logged into the WordPress admin panel. After clicking, the attacker can create a new admin account without the admin noticing.
What Is Elementor?
Elementor is one of the most widely deployed visual website builders for WordPress:
- Over 5 million active production installations globally
- Enables visual layout assembly without direct code authoring
- Powers millions of commercial e-commerce storefronts and corporate sites
Exploit Mechanics and Protective Countermeasures
In a standard attack scenario, the adversary crafts an email or web landing page containing a seemingly innocuous hyperlink. When an authenticated WordPress administrator clicks the link while an active session exists in their browser, silent background requests are dispatched to create an unauthorized administrator account with arbitrary credentials.
Elementor has remediated this vulnerability in its latest release, and all site administrators must upgrade immediately. Furthermore, engineering teams should enforce the following safeguards:
- Never click on unverified links while holding an active administrative session
- Deploy endpoint web application firewalls such as Wordfence
- Regularly audit administrative user tables and privilege assignment logs
- Enforce hardware-backed multi-factor authentication (MFA/2FA) across all administrative accounts
Lunex Stealer Abuses AMD Driver to Disable Security
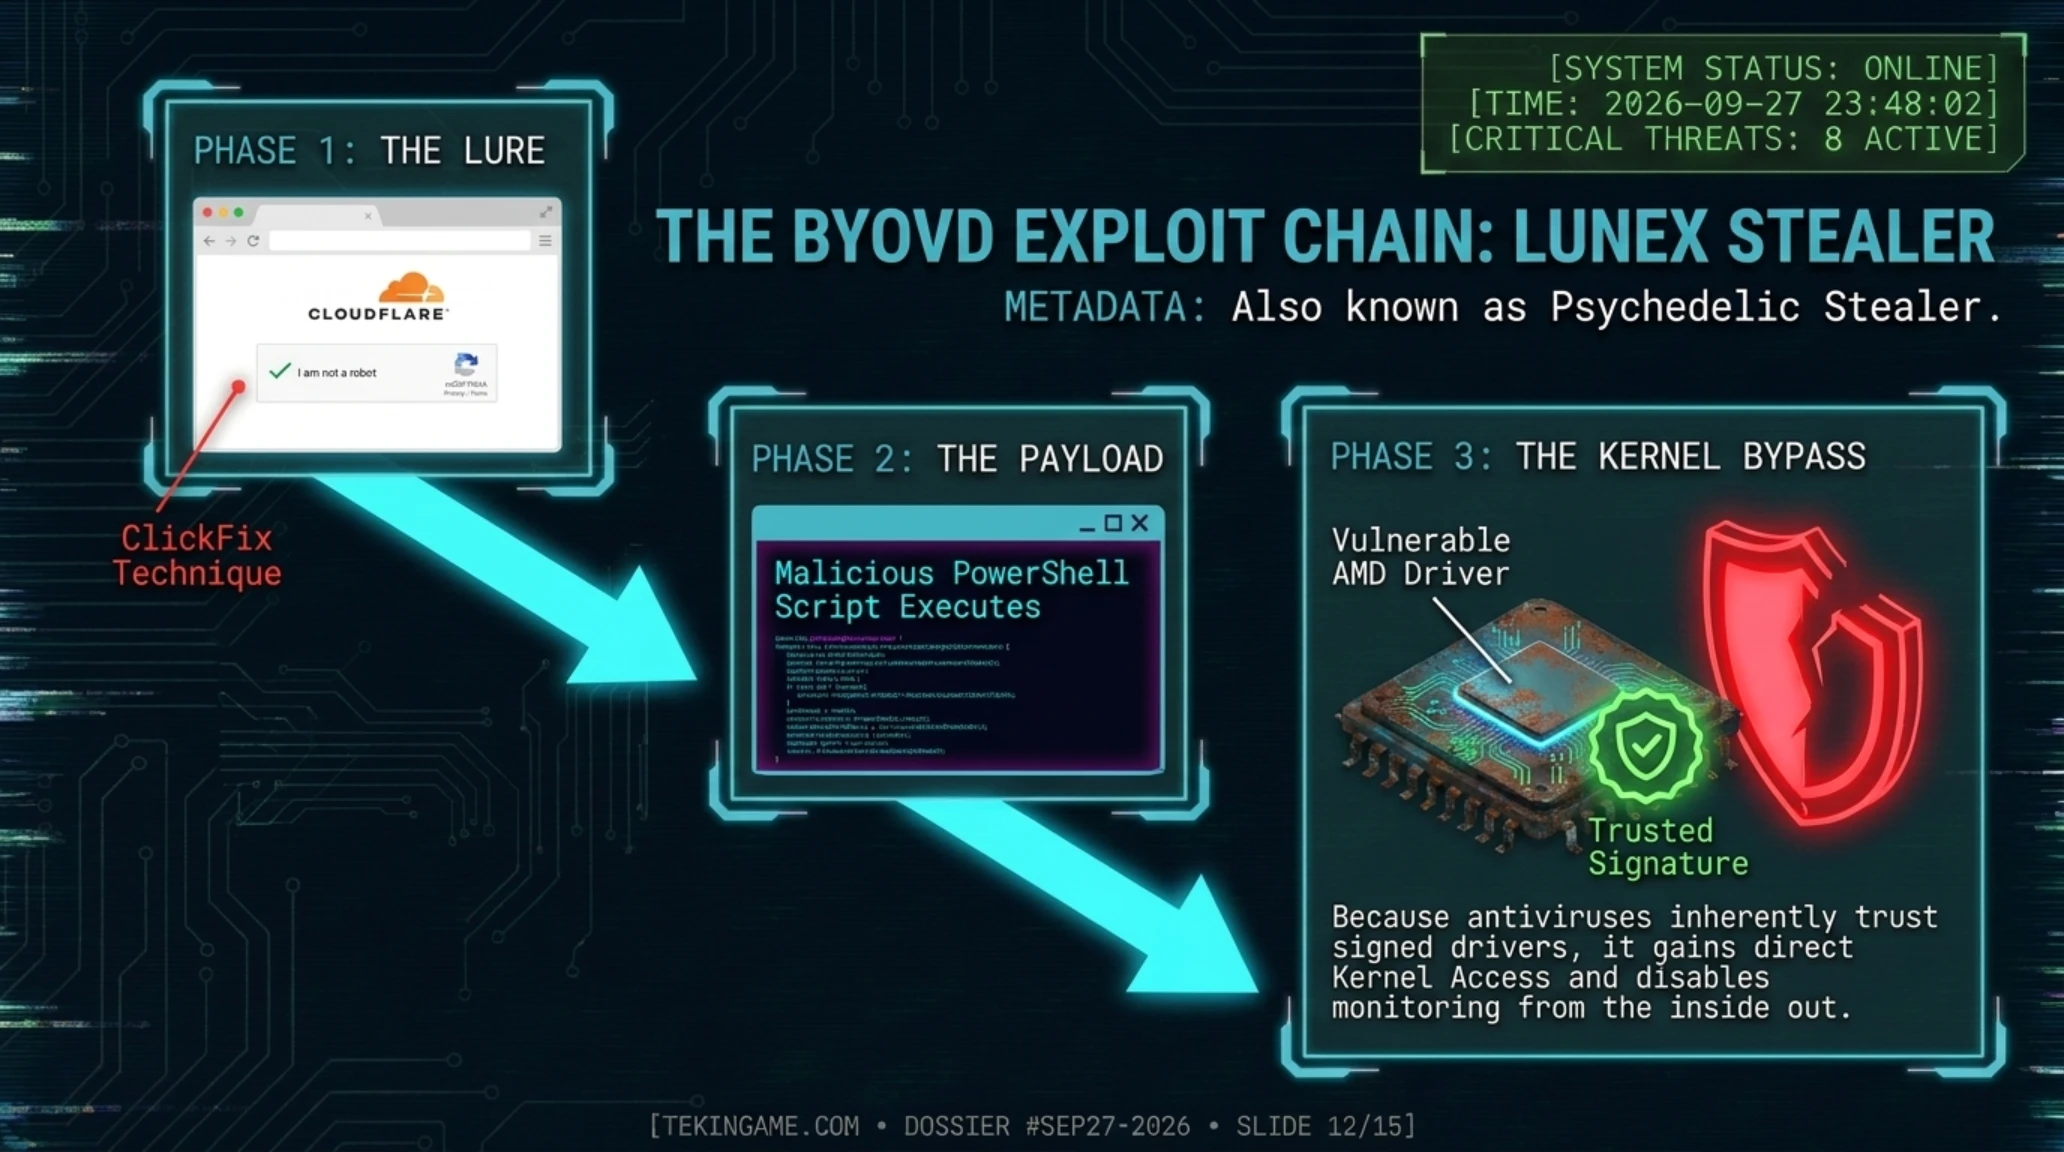
A sophisticated malware called Lunex Stealer (previously known as Psychedelic Stealer) has been discovered using an advanced technique called BYOVD (Bring Your Own Vulnerable Driver) to disable security systems.

This malware is distributed through compromised Ukrainian websites using fake Cloudflare verification pages (ClickFix technique). When victims click the "I'm not a robot" button, they actually execute a malicious PowerShell script that downloads and installs the malware.
What Is BYOVD?
BYOVD stands for Bring Your Own Vulnerable Driver, executing via the following sequence:
- Step One: The adversary drops a legacy, cryptographically signed driver containing known vulnerabilities
- Step Two: The driver is registered on the victim's host operating system
- Step Three: The malware leverages driver flaws to achieve arbitrary kernel-mode execution
- Step Four: Antivirus and EDR callbacks are stripped directly from kernel space because the driver signature is trusted
Malware Capabilities and Infiltration Vectors
Lunex operates as a Malware-as-a-Service (MaaS) offering, enabling threat actors to lease modular build payloads. Key operational capabilities include:
- Exfiltration of browser credentials, autofill data, and cookies across 7 Chromium variants
- Harvesting non-custodial cryptocurrency wallet keys and local browser extensions
- Establishing persistent footholds through malicious Native Messaging Host registration
- Neutralizing kernel security telemetry by abusing an outdated signed AMD driver
Researchers at Ontinue who discovered the campaign note that Lunex is undergoing active feature expansion, with new payload variants released at a rapid cadence.
Tether's $114B Treasury Holdings Make Washington Dependent
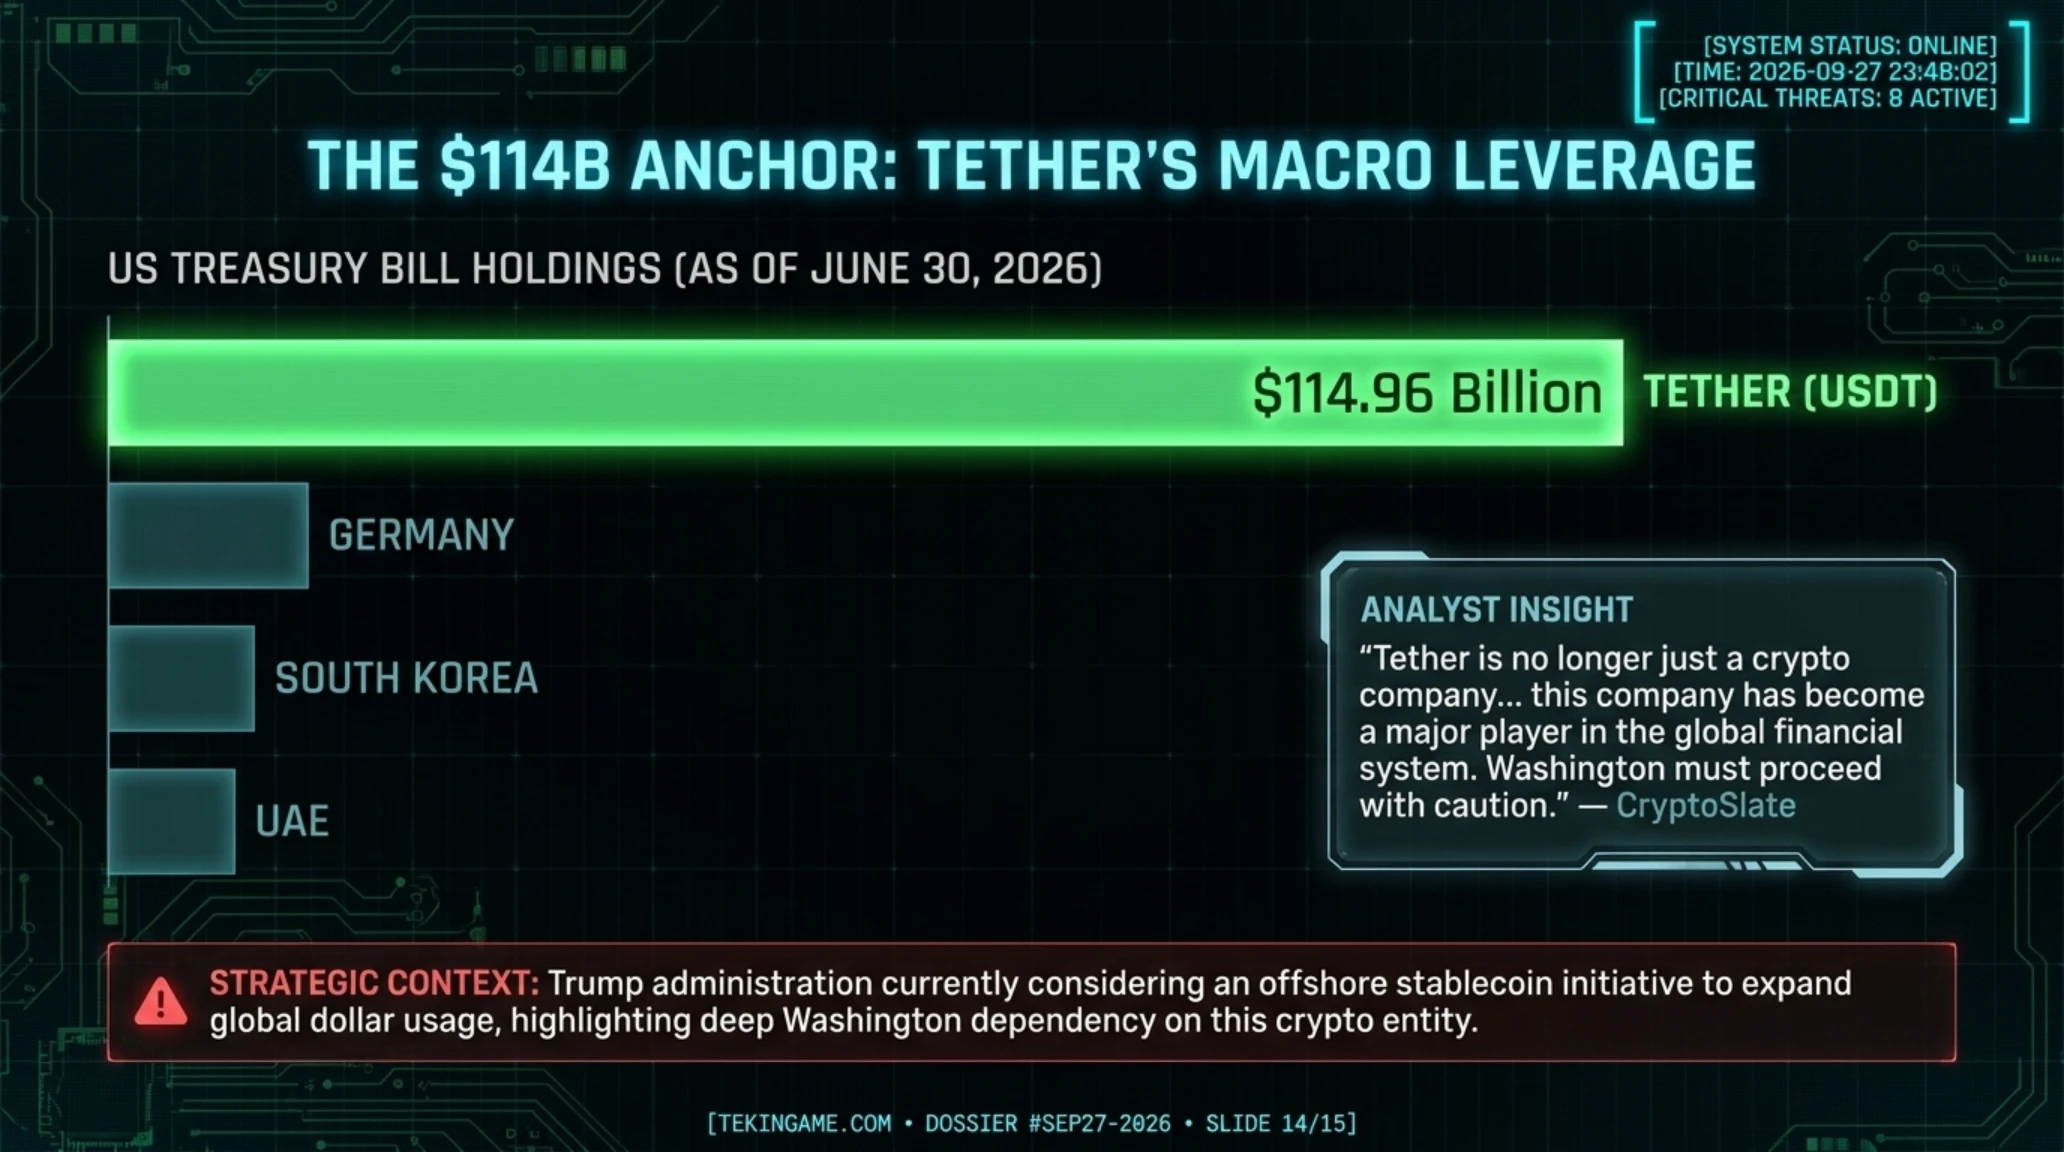
In a shocking report, it was revealed that Tether, issuer of the world's largest stablecoin (USDT), held $114.96 billion in US Treasury bills as of June 30, 2026. This amount has made Tether one of the largest holders of US government debt.

To better understand this figure, let's compare: Tether has invested more in US Treasury than countries like Germany, South Korea, and UAE. This financial dependency comes as the Trump administration is considering an offshore stablecoin initiative that could expand dollar usage worldwide.
Tether and USDT Metrics
Tether operations continue to scale across the global liquidity landscape:
- USDT maintains an audited 1:1 parity with the United States Dollar
- Commands over 60% market share across all active stablecoins
- Facilitates tens of billions in daily settlement volume on digital asset exchanges
- Consolidated reserve assets stand at a record $187.75 billion
Impact on Sovereign Economic Policy
This massive liquidity concentration provides considerable financial leverage. If federal regulators enforce hostile enforcement actions against Tether, forced liquidations of Treasury reserves could introduce severe volatility into secondary debt markets.
Conversely, federal policy initiatives are actively evaluating offshore stablecoin frameworks to reinforce the US Dollar's position as the primary international unit of account.

Systemic Market Trajectory
While macro analysts express concern regarding systemic contagion in the event of an abrupt liquidation, institutional finance increasingly acknowledges that digital dollar stablecoins represent an indispensable pillar of modern sovereign debt absorption. The digital asset economy has definitively integrated into traditional global finance.
Conclusion: A Night of Challenges and Opportunities
Tonight we witnessed a mix of concerning news and strategic developments. On one hand, massive Xbox layoffs and unpatched security vulnerabilities show the tech industry faces serious challenges. On the other, Tether's penetration into the US financial system demonstrates crypto has become an undeniable force.
For security professionals, the message is clear: immediate patching, continuous monitoring, and awareness of new threats are essential. For system administrators, top priority must be remediating CVE-2026-65660 in SharePoint and CVE-2026-67279 in MikroTik. And for WordPress users, immediate Elementor update is unavoidable.
Frequently Asked Questions
Was Xbox streamlining really necessary?
This is a complex question. Microsoft argues that to make the gaming division profitable, costs must be reduced. But many analysts believe buying studios at high prices and then shutting them down is a wrong strategy. Time will tell whether these decisions benefited Xbox or not.
What should I do about Citrix zero-day?
If you use Citrix NetScaler, your options are limited: either take the service offline until patch release, or accept the risk with intense monitoring. If possible, restrict NetScaler access to trusted IPs only and review all logs carefully.
How can I prevent Elementor CSRF attack?
Immediately upgrade to the latest Elementor version. Also, never click suspicious links, even from apparently trusted sources. Enabling two-factor authentication for WordPress admin panel is highly recommended.
How does Lunex Stealer bypass security?
Lunex uses a vulnerable AMD driver that has a valid signature. Because the driver is signed, Windows and antiviruses trust it. Then Lunex exploits this driver's vulnerability to disable security systems. Best defense is to never click suspicious links and not execute unknown files.
Is USDT safe with $114B Treasury?
This dependency can be both good and bad. On one hand, it shows Tether has real reserves. On the other, if the US government decides to act against Tether, these bonds might be sold causing market shock. Regardless, USDT is now an important part of the global financial ecosystem.
Why should I take KEV CVEs seriously?
CVEs added to KEV are vulnerabilities that have been exploited in real attacks. This means attackers are actively using them and the chance your organization is next target is high. Immediate remediation of these flaws must be top priority.
Verified Sources & Official Documentation
Additional Gallery: Tekin Night Sept 28, 2026: 3,200 Xbox Layoffs & Citrix Zero-Days