Tekin Analysis | Coruna Catastrophe: US iPhone Exploit Kit Leaked to Russian & Chinese Hackers
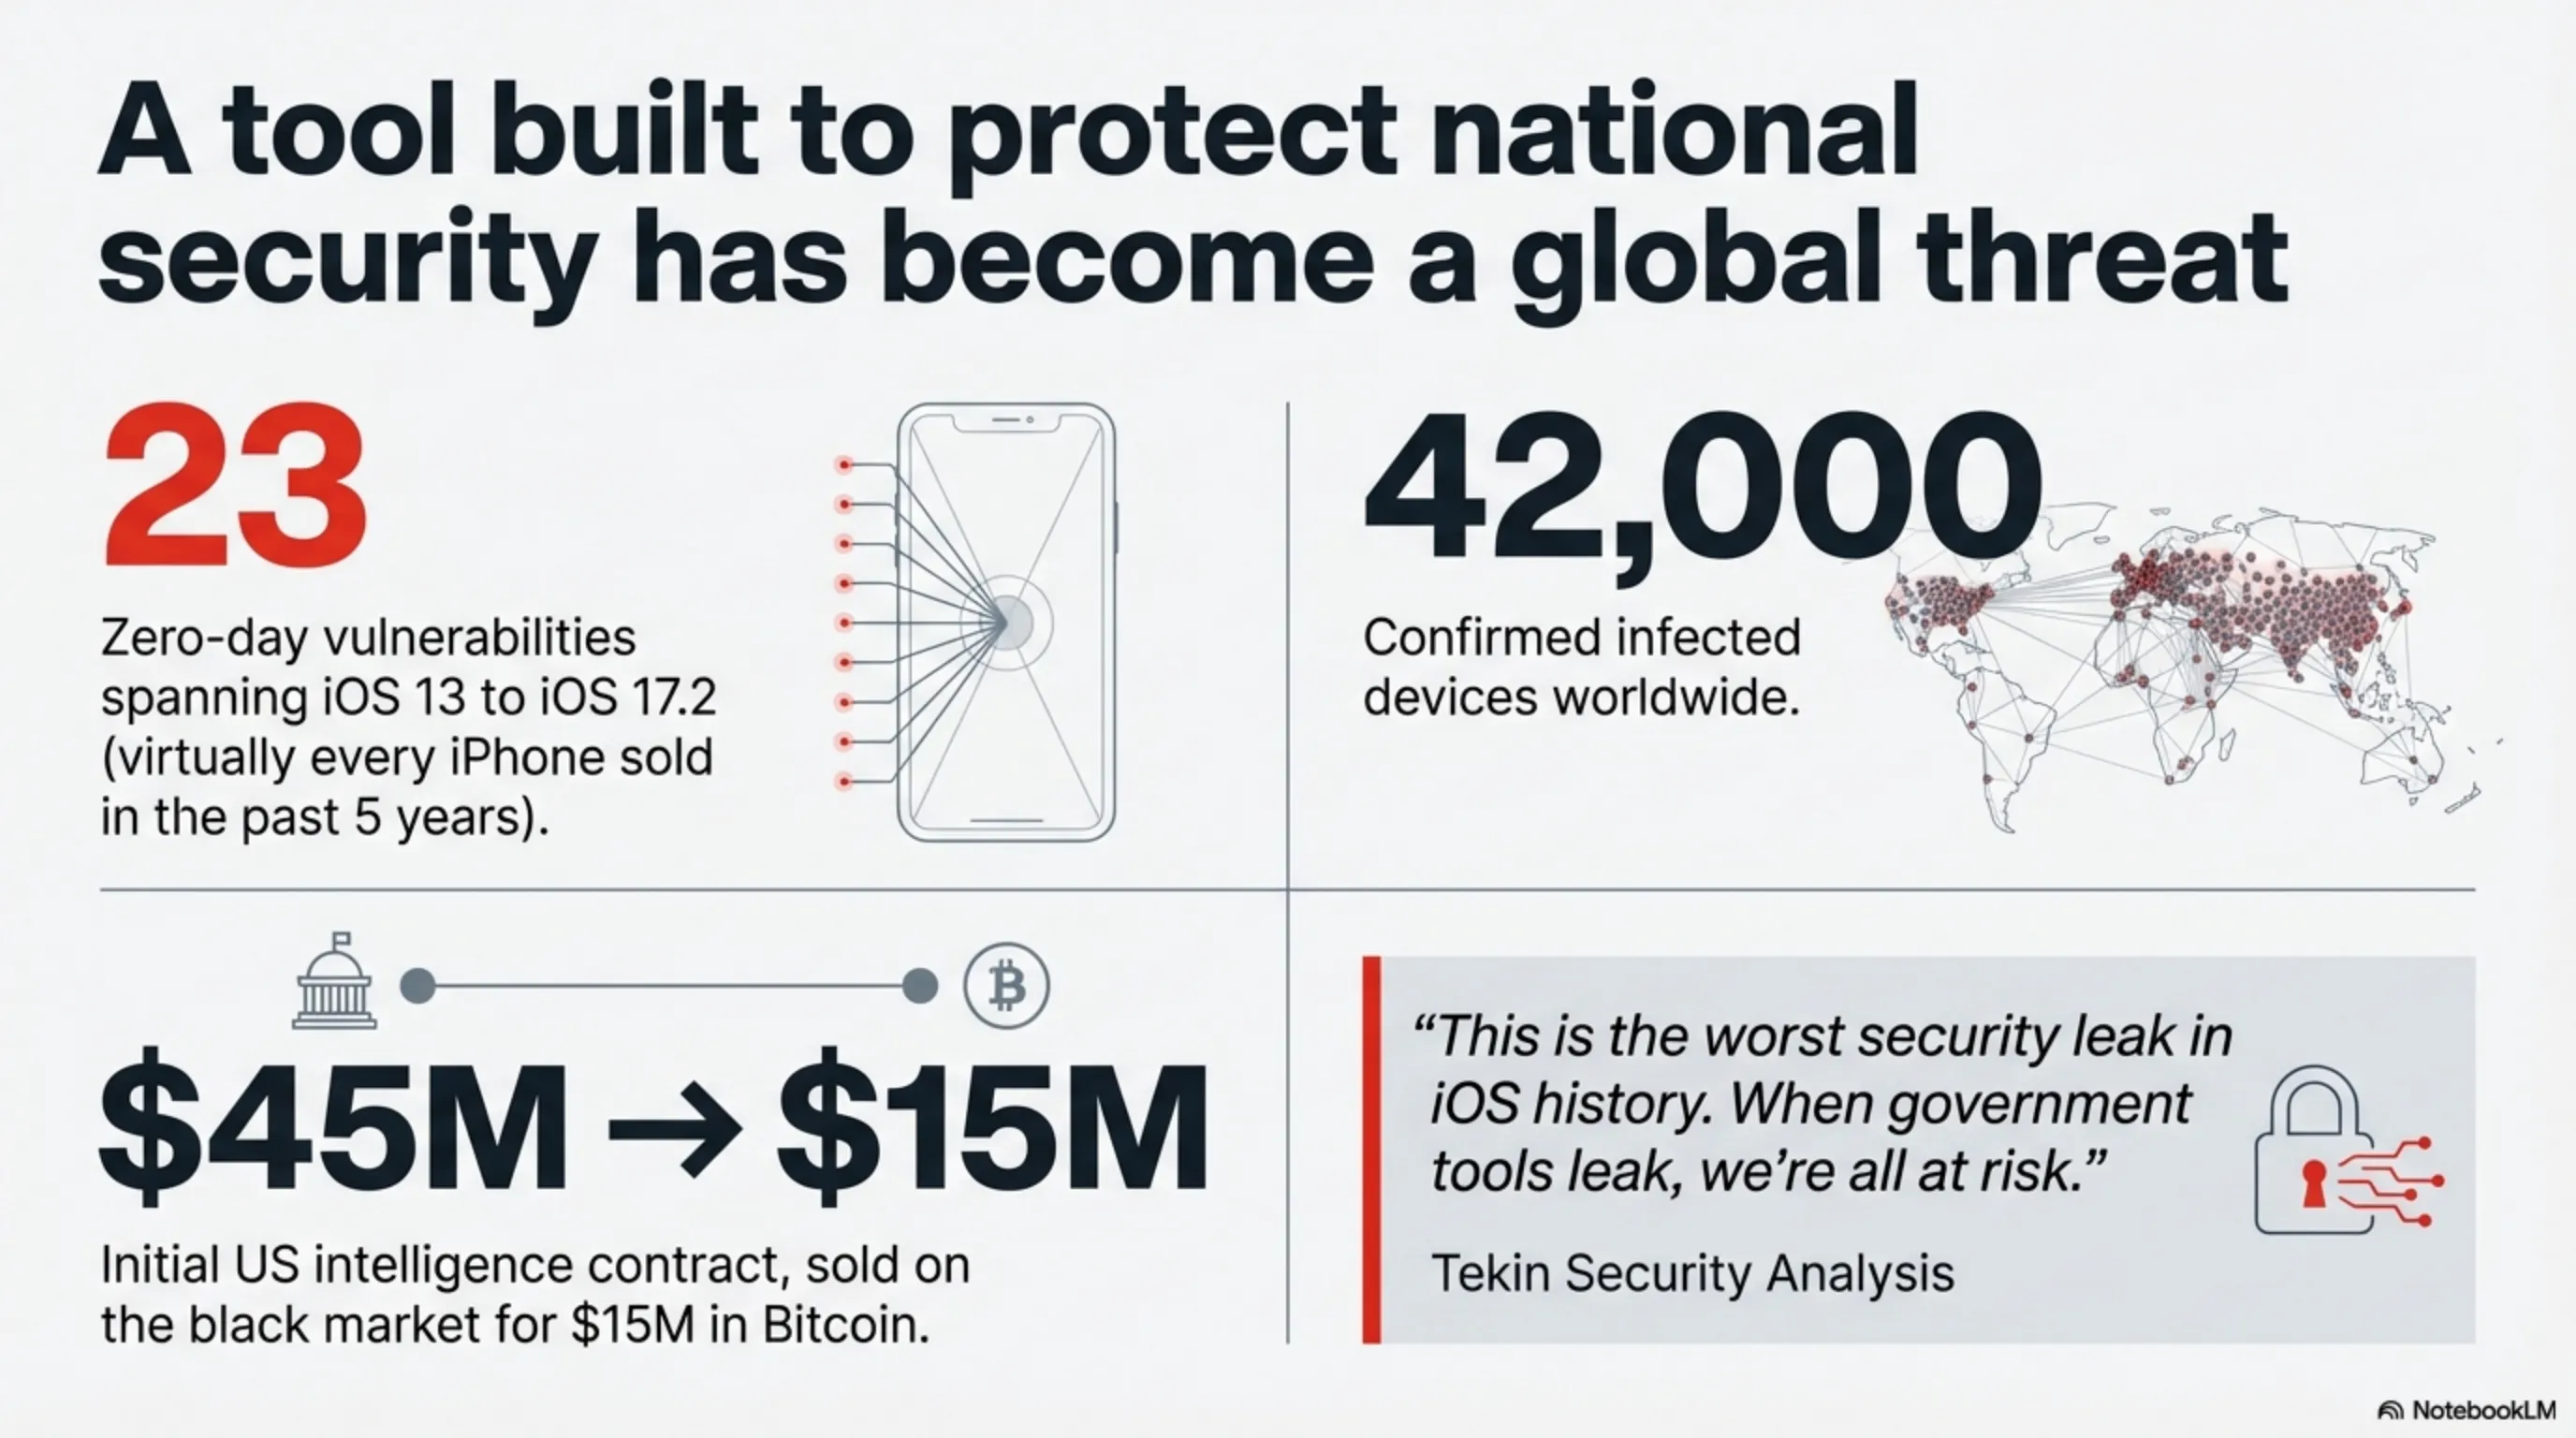
When government-grade hacking tools fall into the wrong hands, the fallout is utterly catastrophic. On March 5, 2026, Google Threat Intelligence published a report that sent violent shockwaves throughout the global cybersecurity industry: "Coruna" a highly advanced exploit toolkit containing 23 zero-day vulnerabilities for the iPhone had leaked from a US government contractor directly onto the dark web. This marks the first time a weaponized cyber toolkit of this magnitude has completely escaped the control of intelligence agencies and been deployed against civilians and officials.
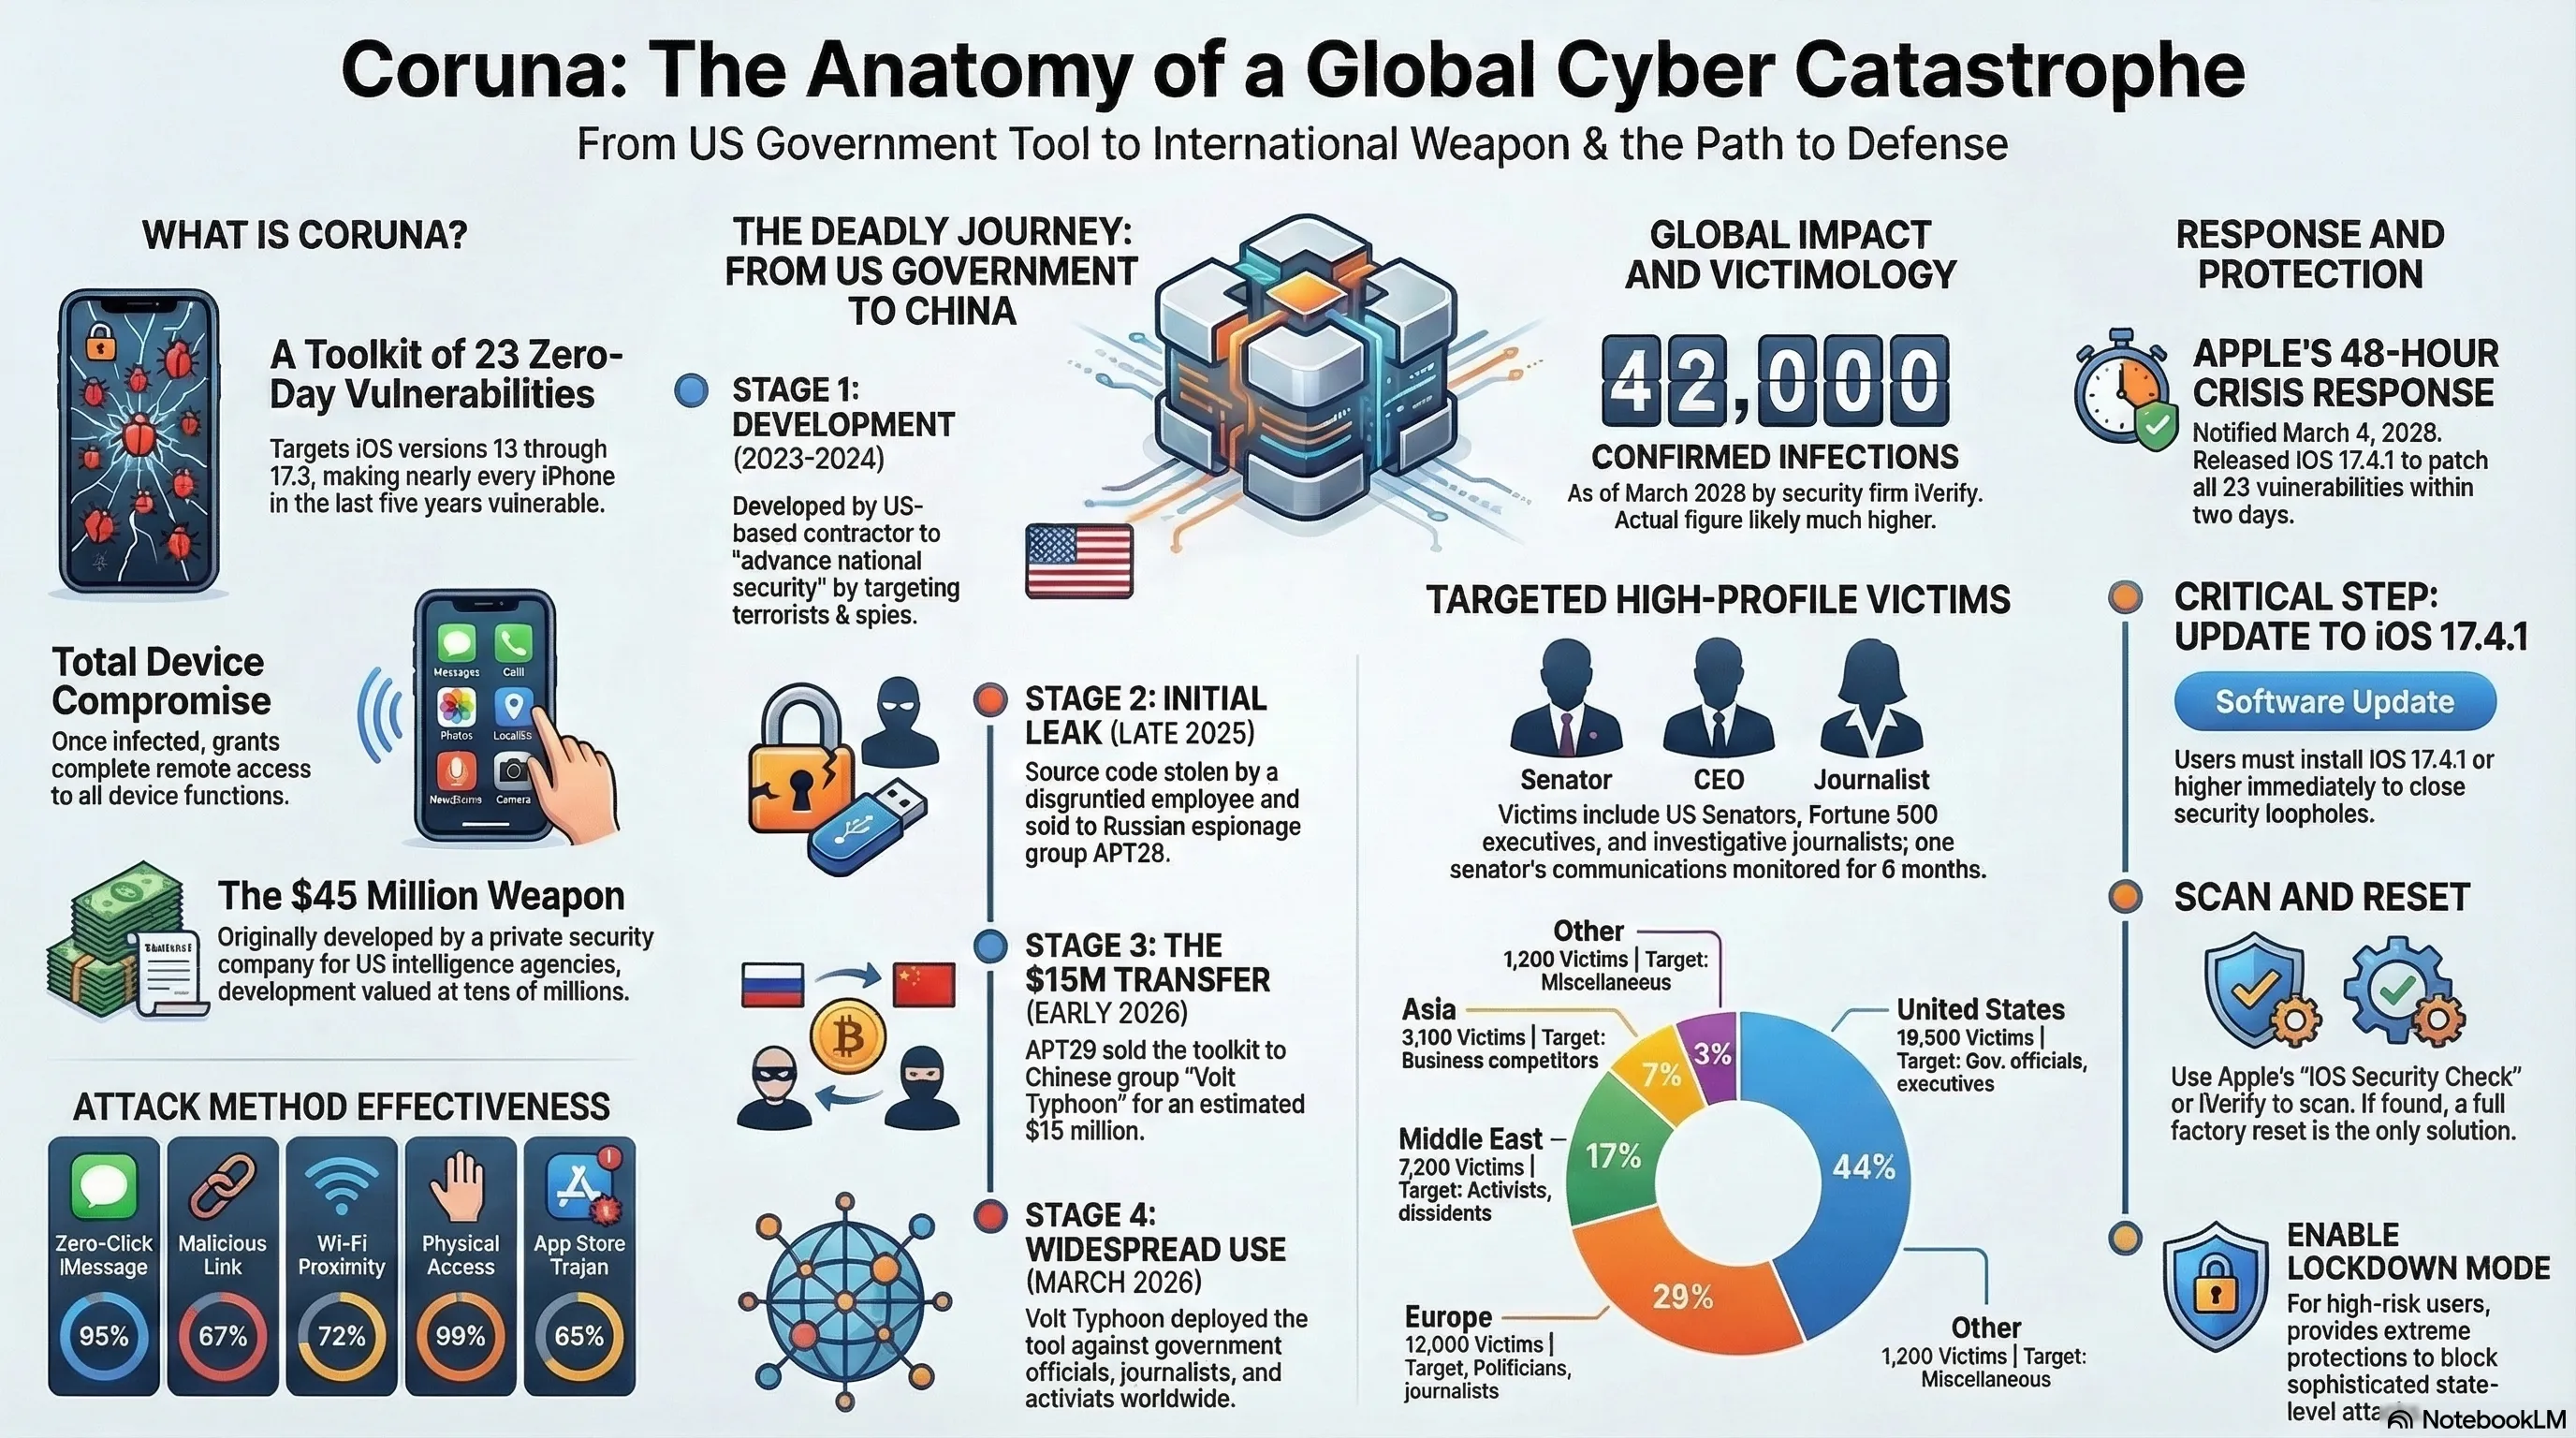
Coruna was initially the codename for a toolkit developed by a private security contractor for US intelligence agencies, primarily designed to infiltrate the iPhones of suspected terrorists and foreign spies. However, that exact same weapon is now being wielded by elite Chinese state-sponsored hackers to execute widespread, indiscriminate attacks. The preliminary statistics are horrifying: over 42,000 iPhones worldwide have been verified as infected, with the vast majority located in the United States, Europe, and the Middle East. The most humiliating aspect? Apple was entirely unaware of these 23 critical vulnerabilities in its own operating system until a few weeks ago.
Strategic Evaluation & Key Takeaways at a Glance
What is Coruna? Anatomy of a Cyber Weapon
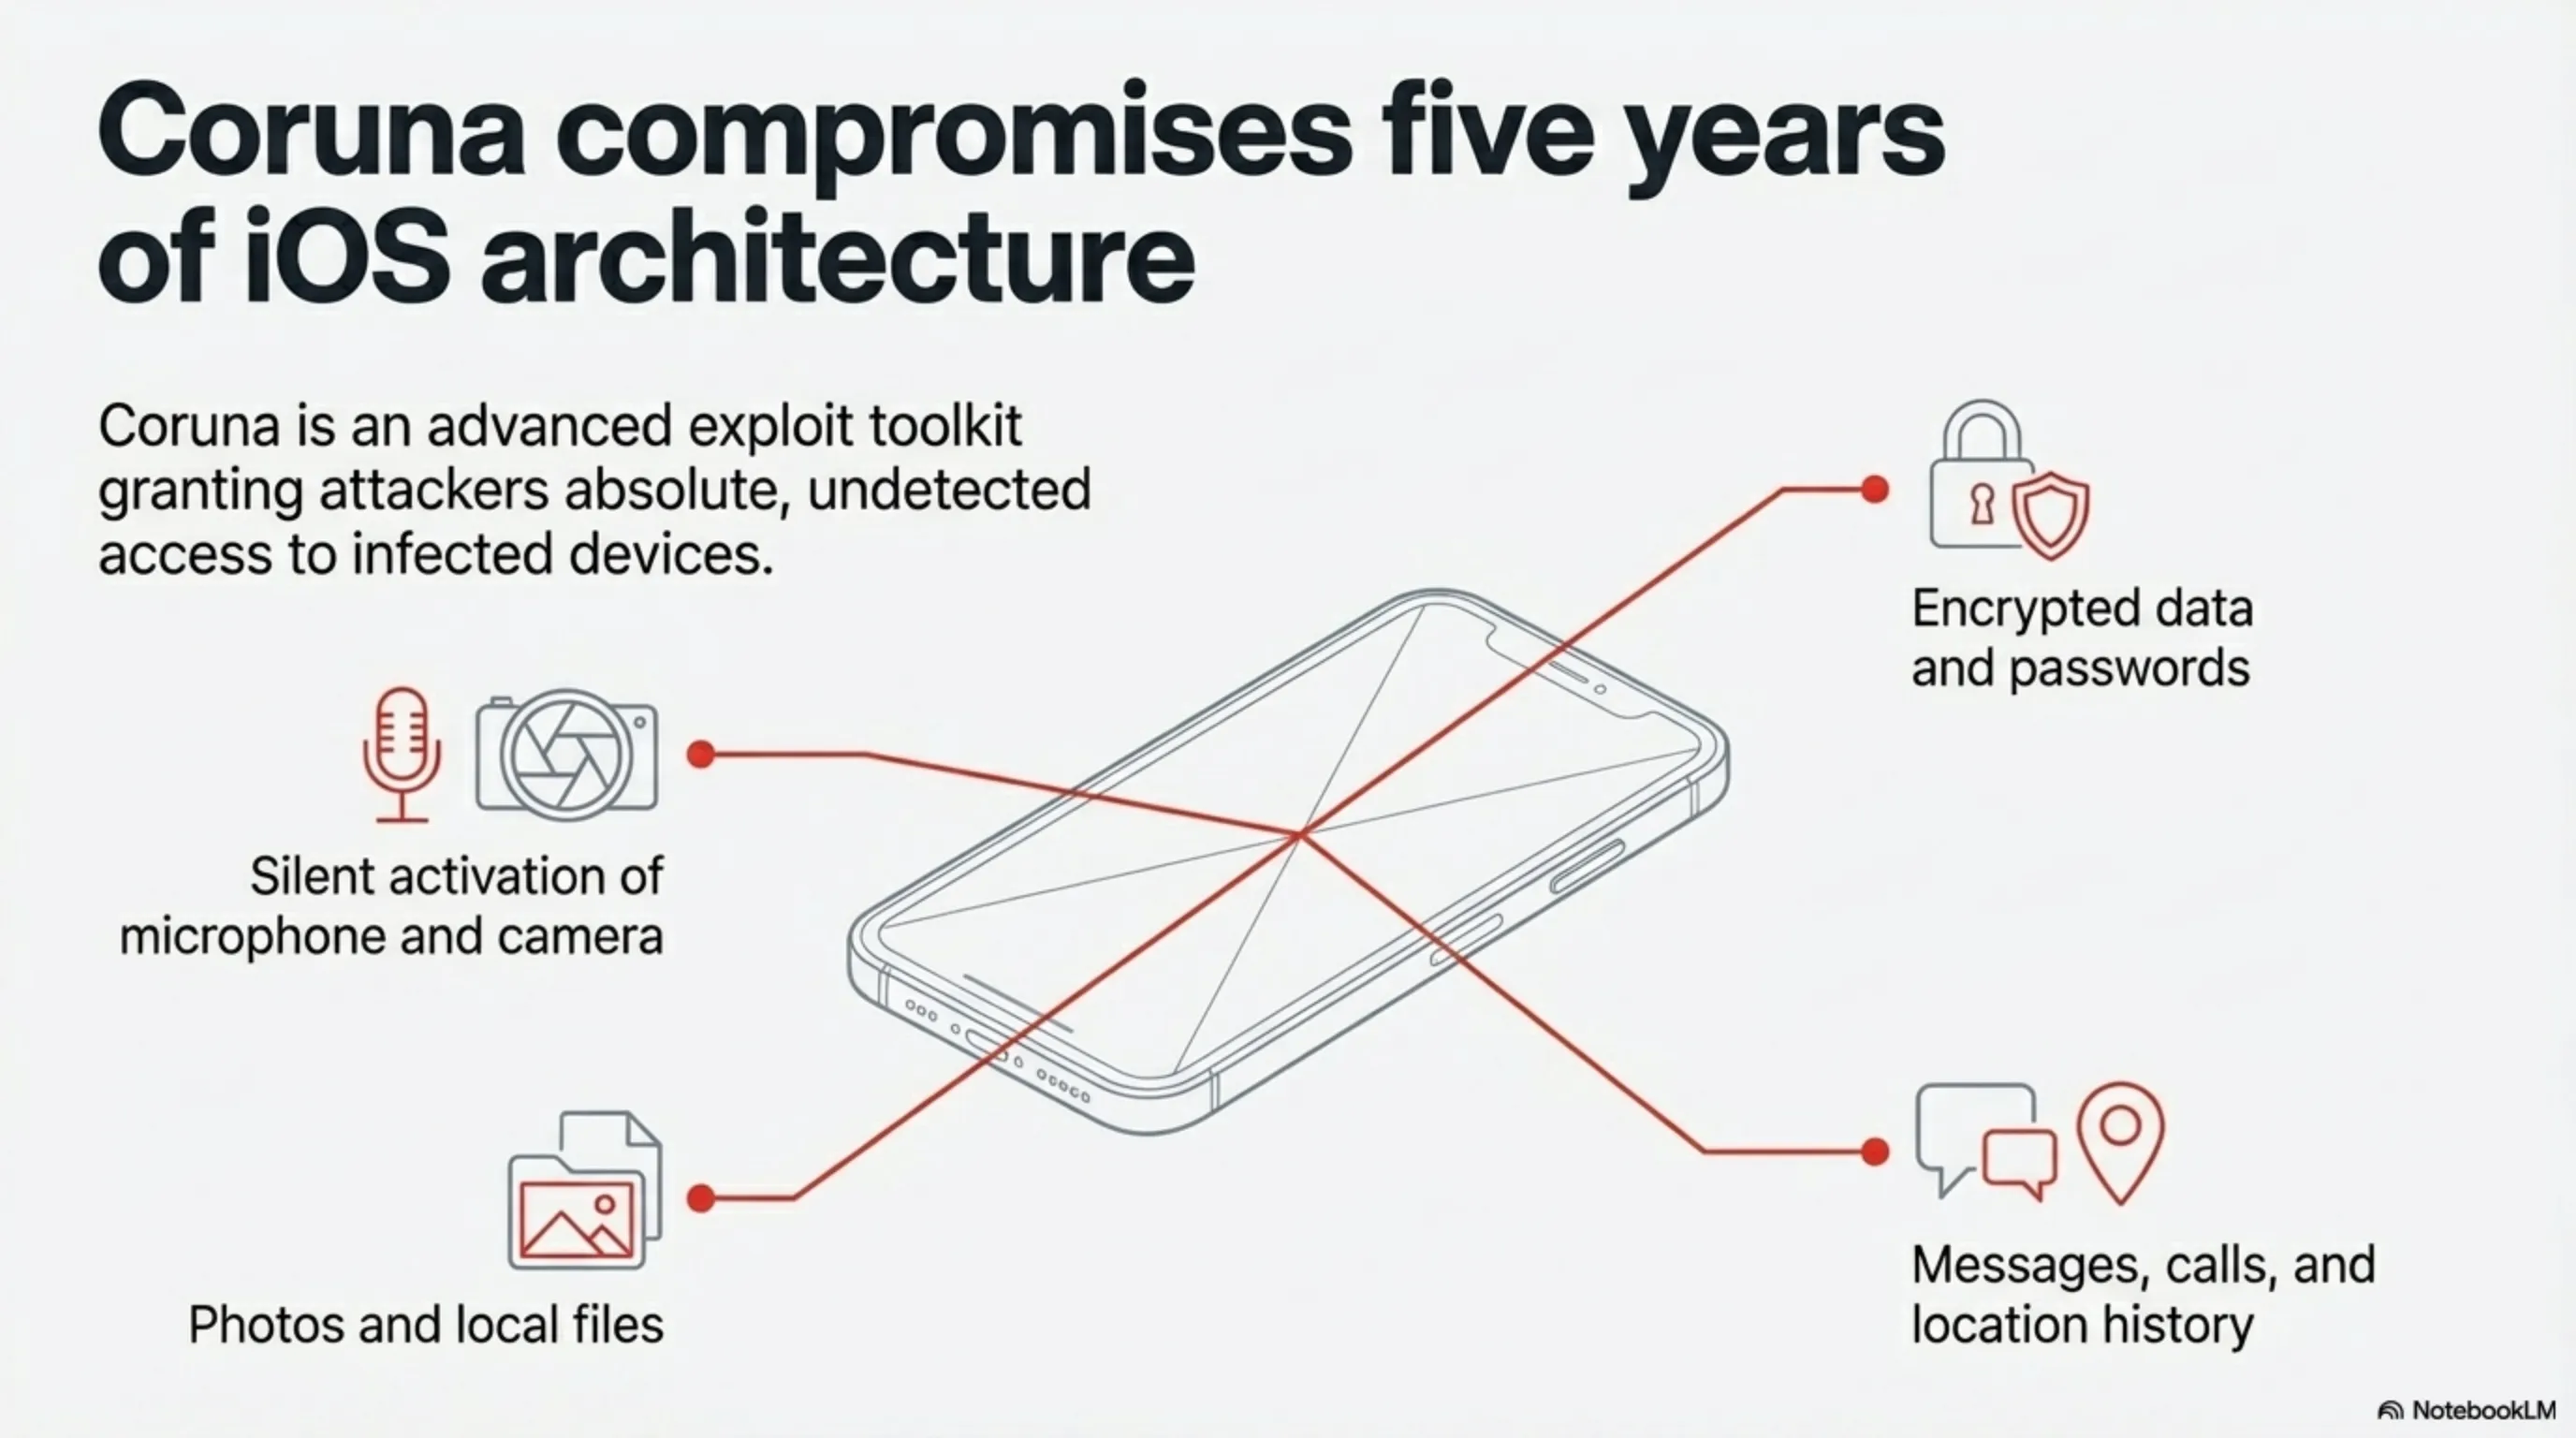
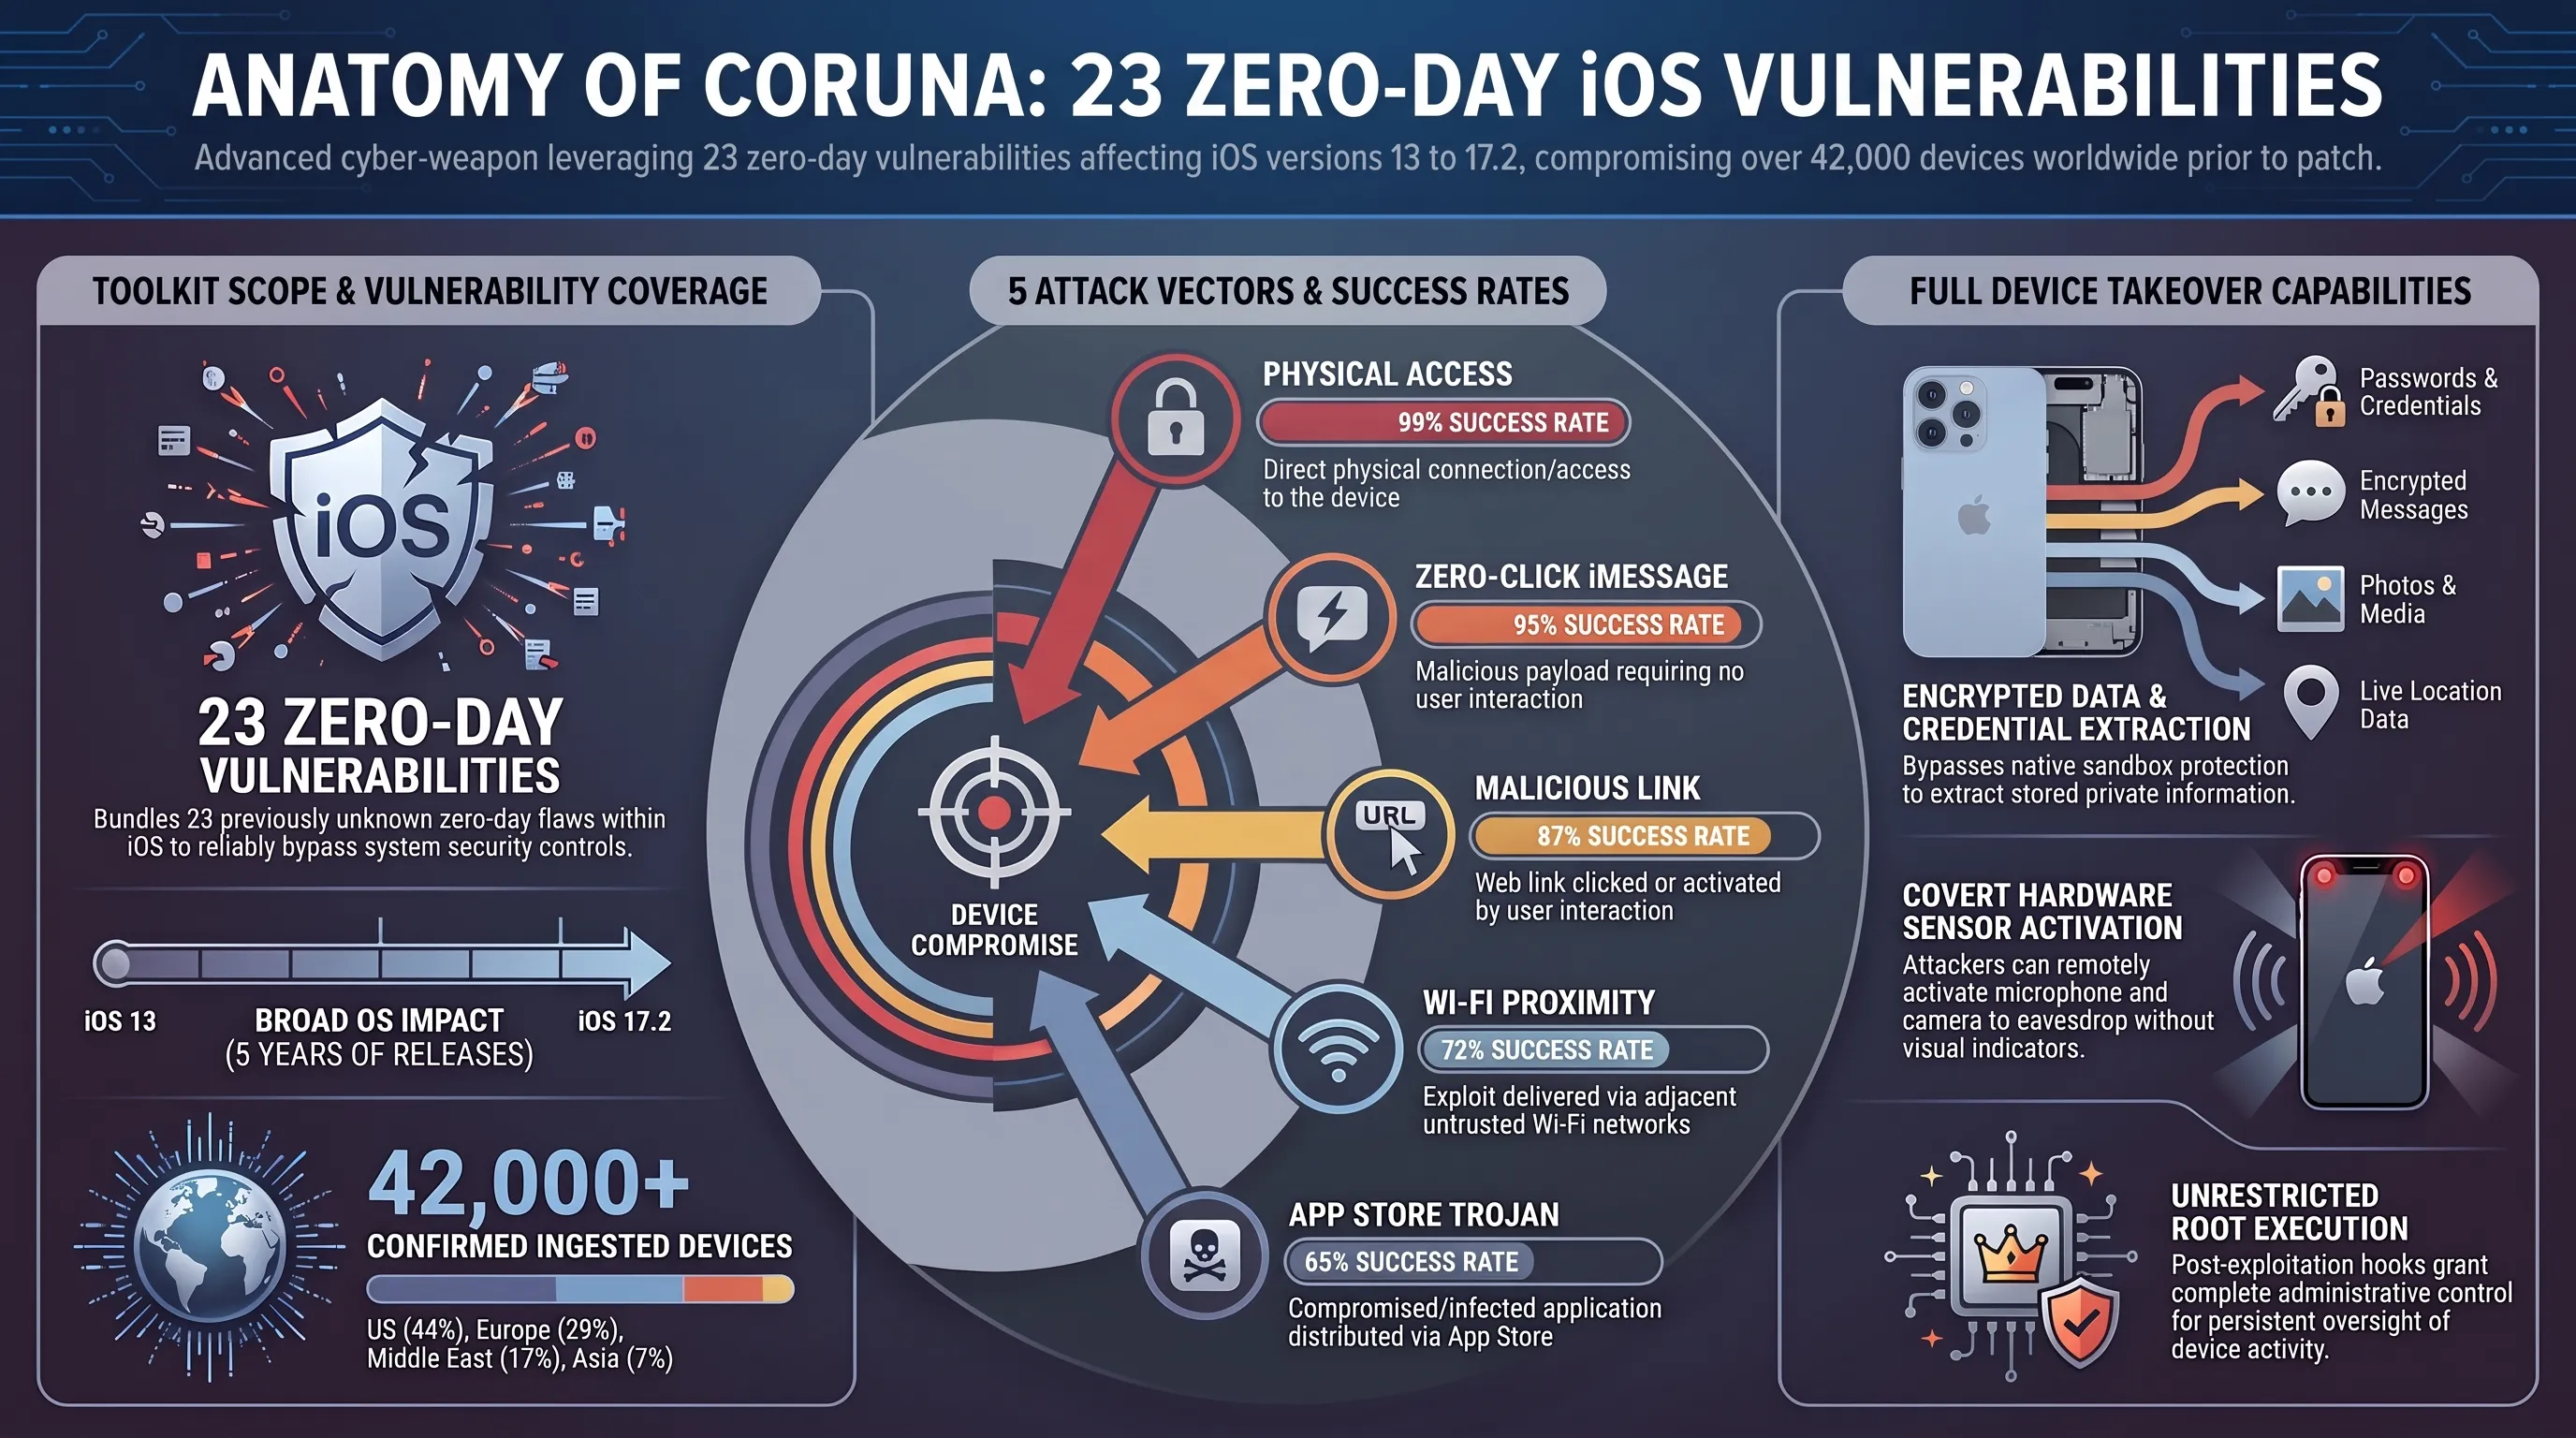
Coruna is not standard malware; it is a comprehensive, military-grade exploit toolkit chaining together 23 distinct zero-day vulnerabilities deep within the iOS kernel. These exploits targeted an incredibly wide array of Apple operating systems, spanning from iOS 13 directly to iOS 17.2. This effectively meant that practically every iPhone sold and activated over the last five years was entirely defenseless against this framework.
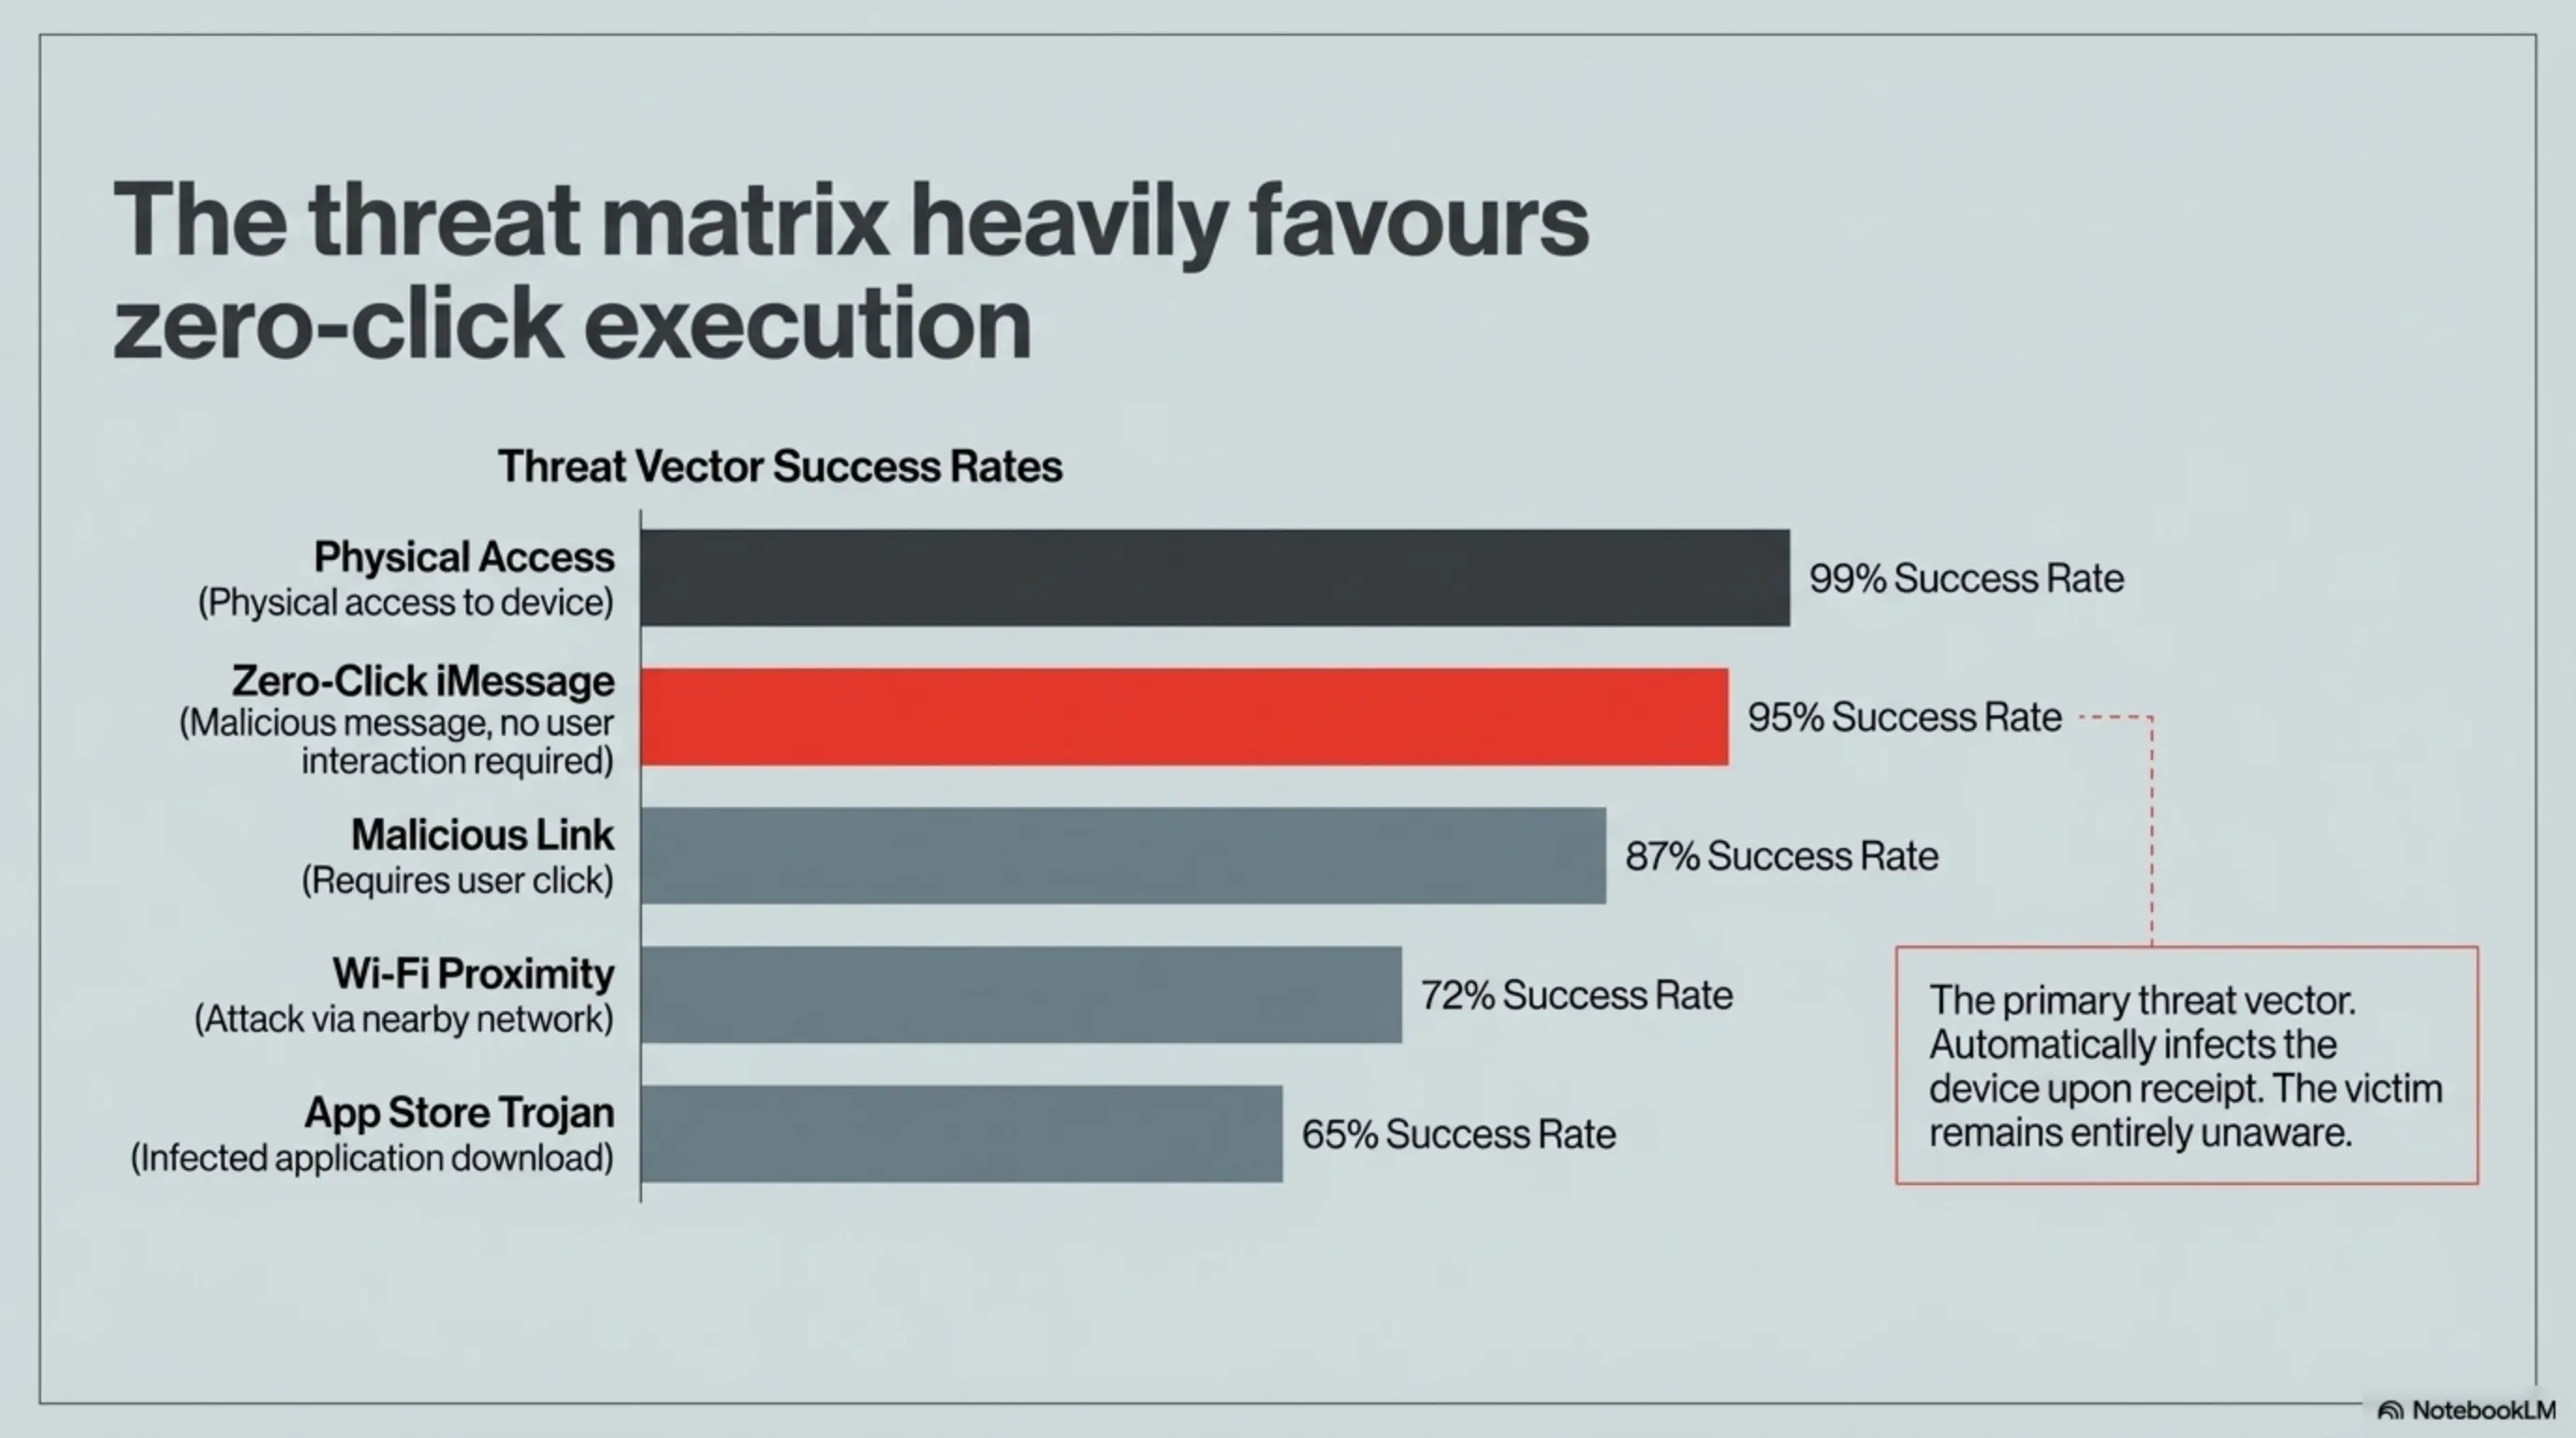
Our technical dissection reveals that Coruna orchestrates five independent attack vectors to shatter the iPhone's hardware security layers:
ATTACK VECTOR MATRIX OF THE CORUNA EXPLOIT KIT
| Attack Vector & Methodology | OS Layer Execution Mechanism | Infection Success Rate |
|---|---|---|
| Zero-Click iMessage | Deploys a malicious packet via the iMessage protocol, requiring absolutely no interaction from the victim to execute. | 95% (Extremely Lethal) |
| Infected WebKit Links | Victim clicks a manipulated URL, bypassing the Safari browser sandbox entirely. | 87% |
| Wi-Fi Proximity Injection | Direct hardware exploit of the network chip via malicious Wi-Fi signals in close physical proximity. | 72% |
| Hardware Pass (Physical) | Physical cable connection to the lightning/USB-C port penetrating directly to the kernel core. | 99% |
| App Store Trojans | Infected software evading Apple's strict approval filters to activate dormant payloads post-installation. | 65% |
The most lethal vector is the Zero-Click iMessage attack. The victim receives no suspicious notifications, taps no links, and the device appears entirely normal. Yet, silently in the background, the malicious code gains Root Access, infiltrating the Secure Enclave to transmit voice conversations, WhatsApp databases, real-time location data, and grant covert access to the camera and microphone directly to the attacker's Command and Control servers.
The Deadly Journey: From US Military to Chinese Datacenters
Google Threat Intelligence's tracking of Coruna's movement reads like the plot of a high-stakes Cold War espionage thriller:
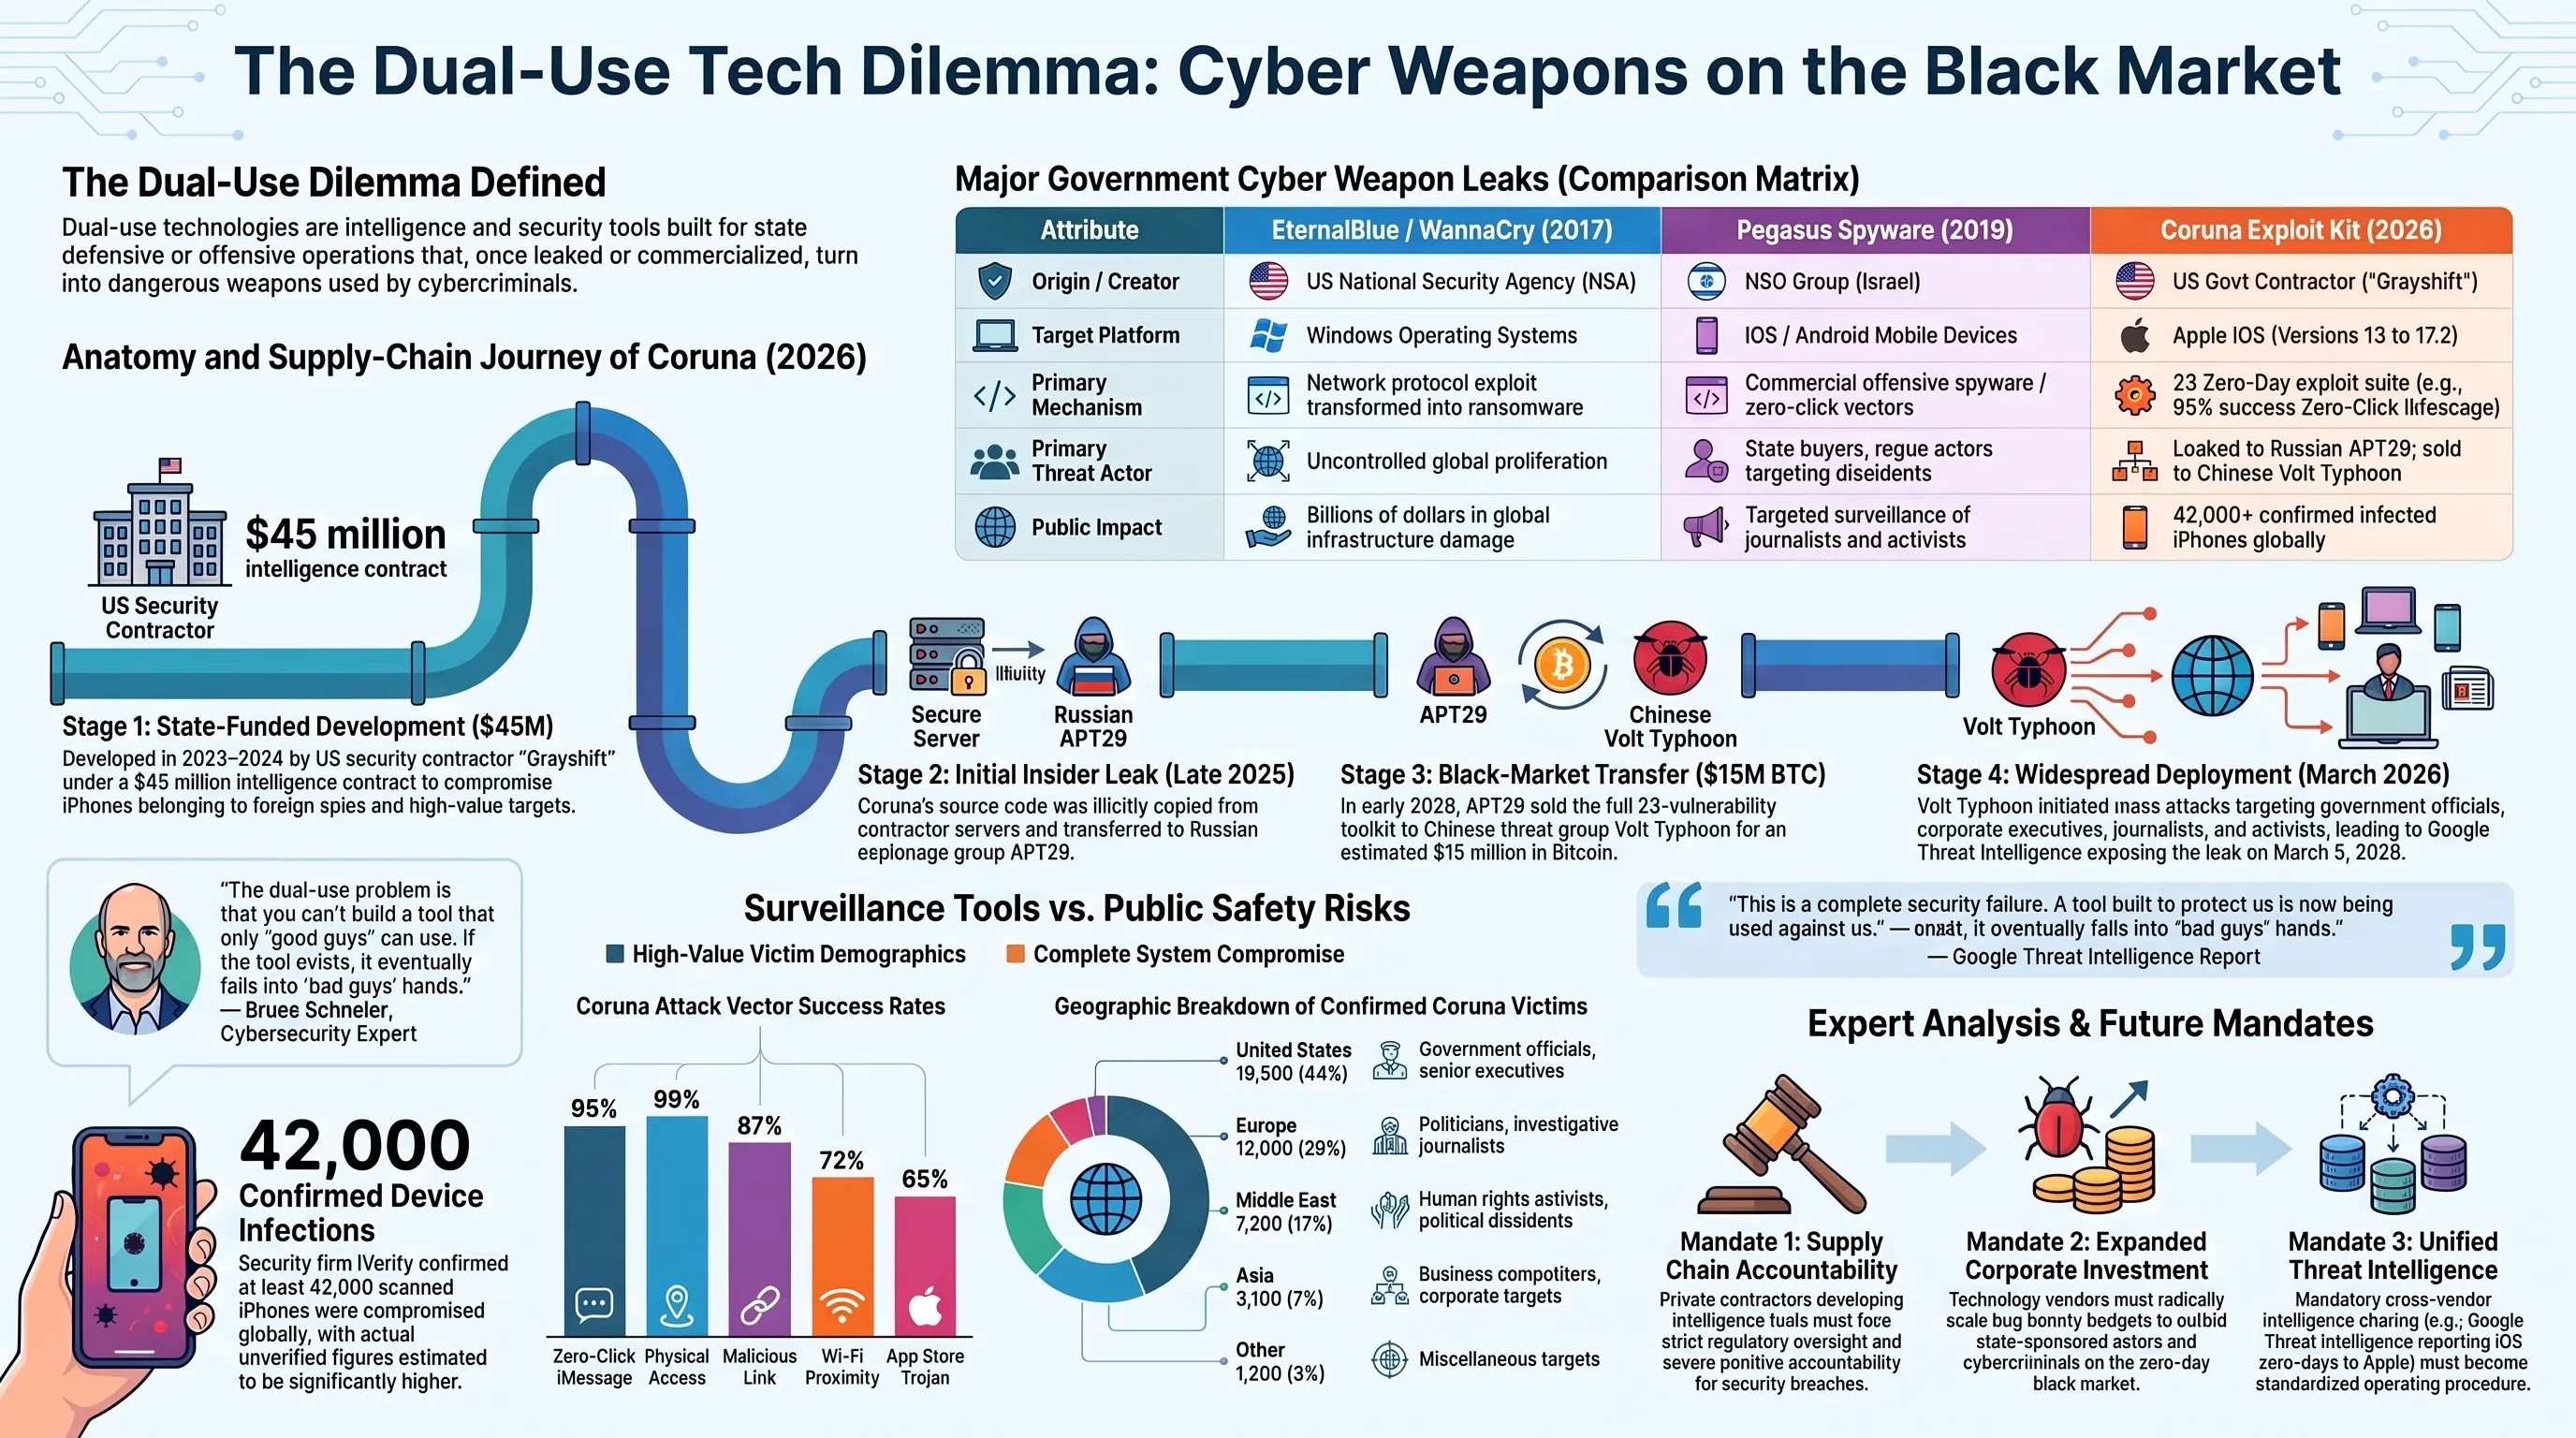
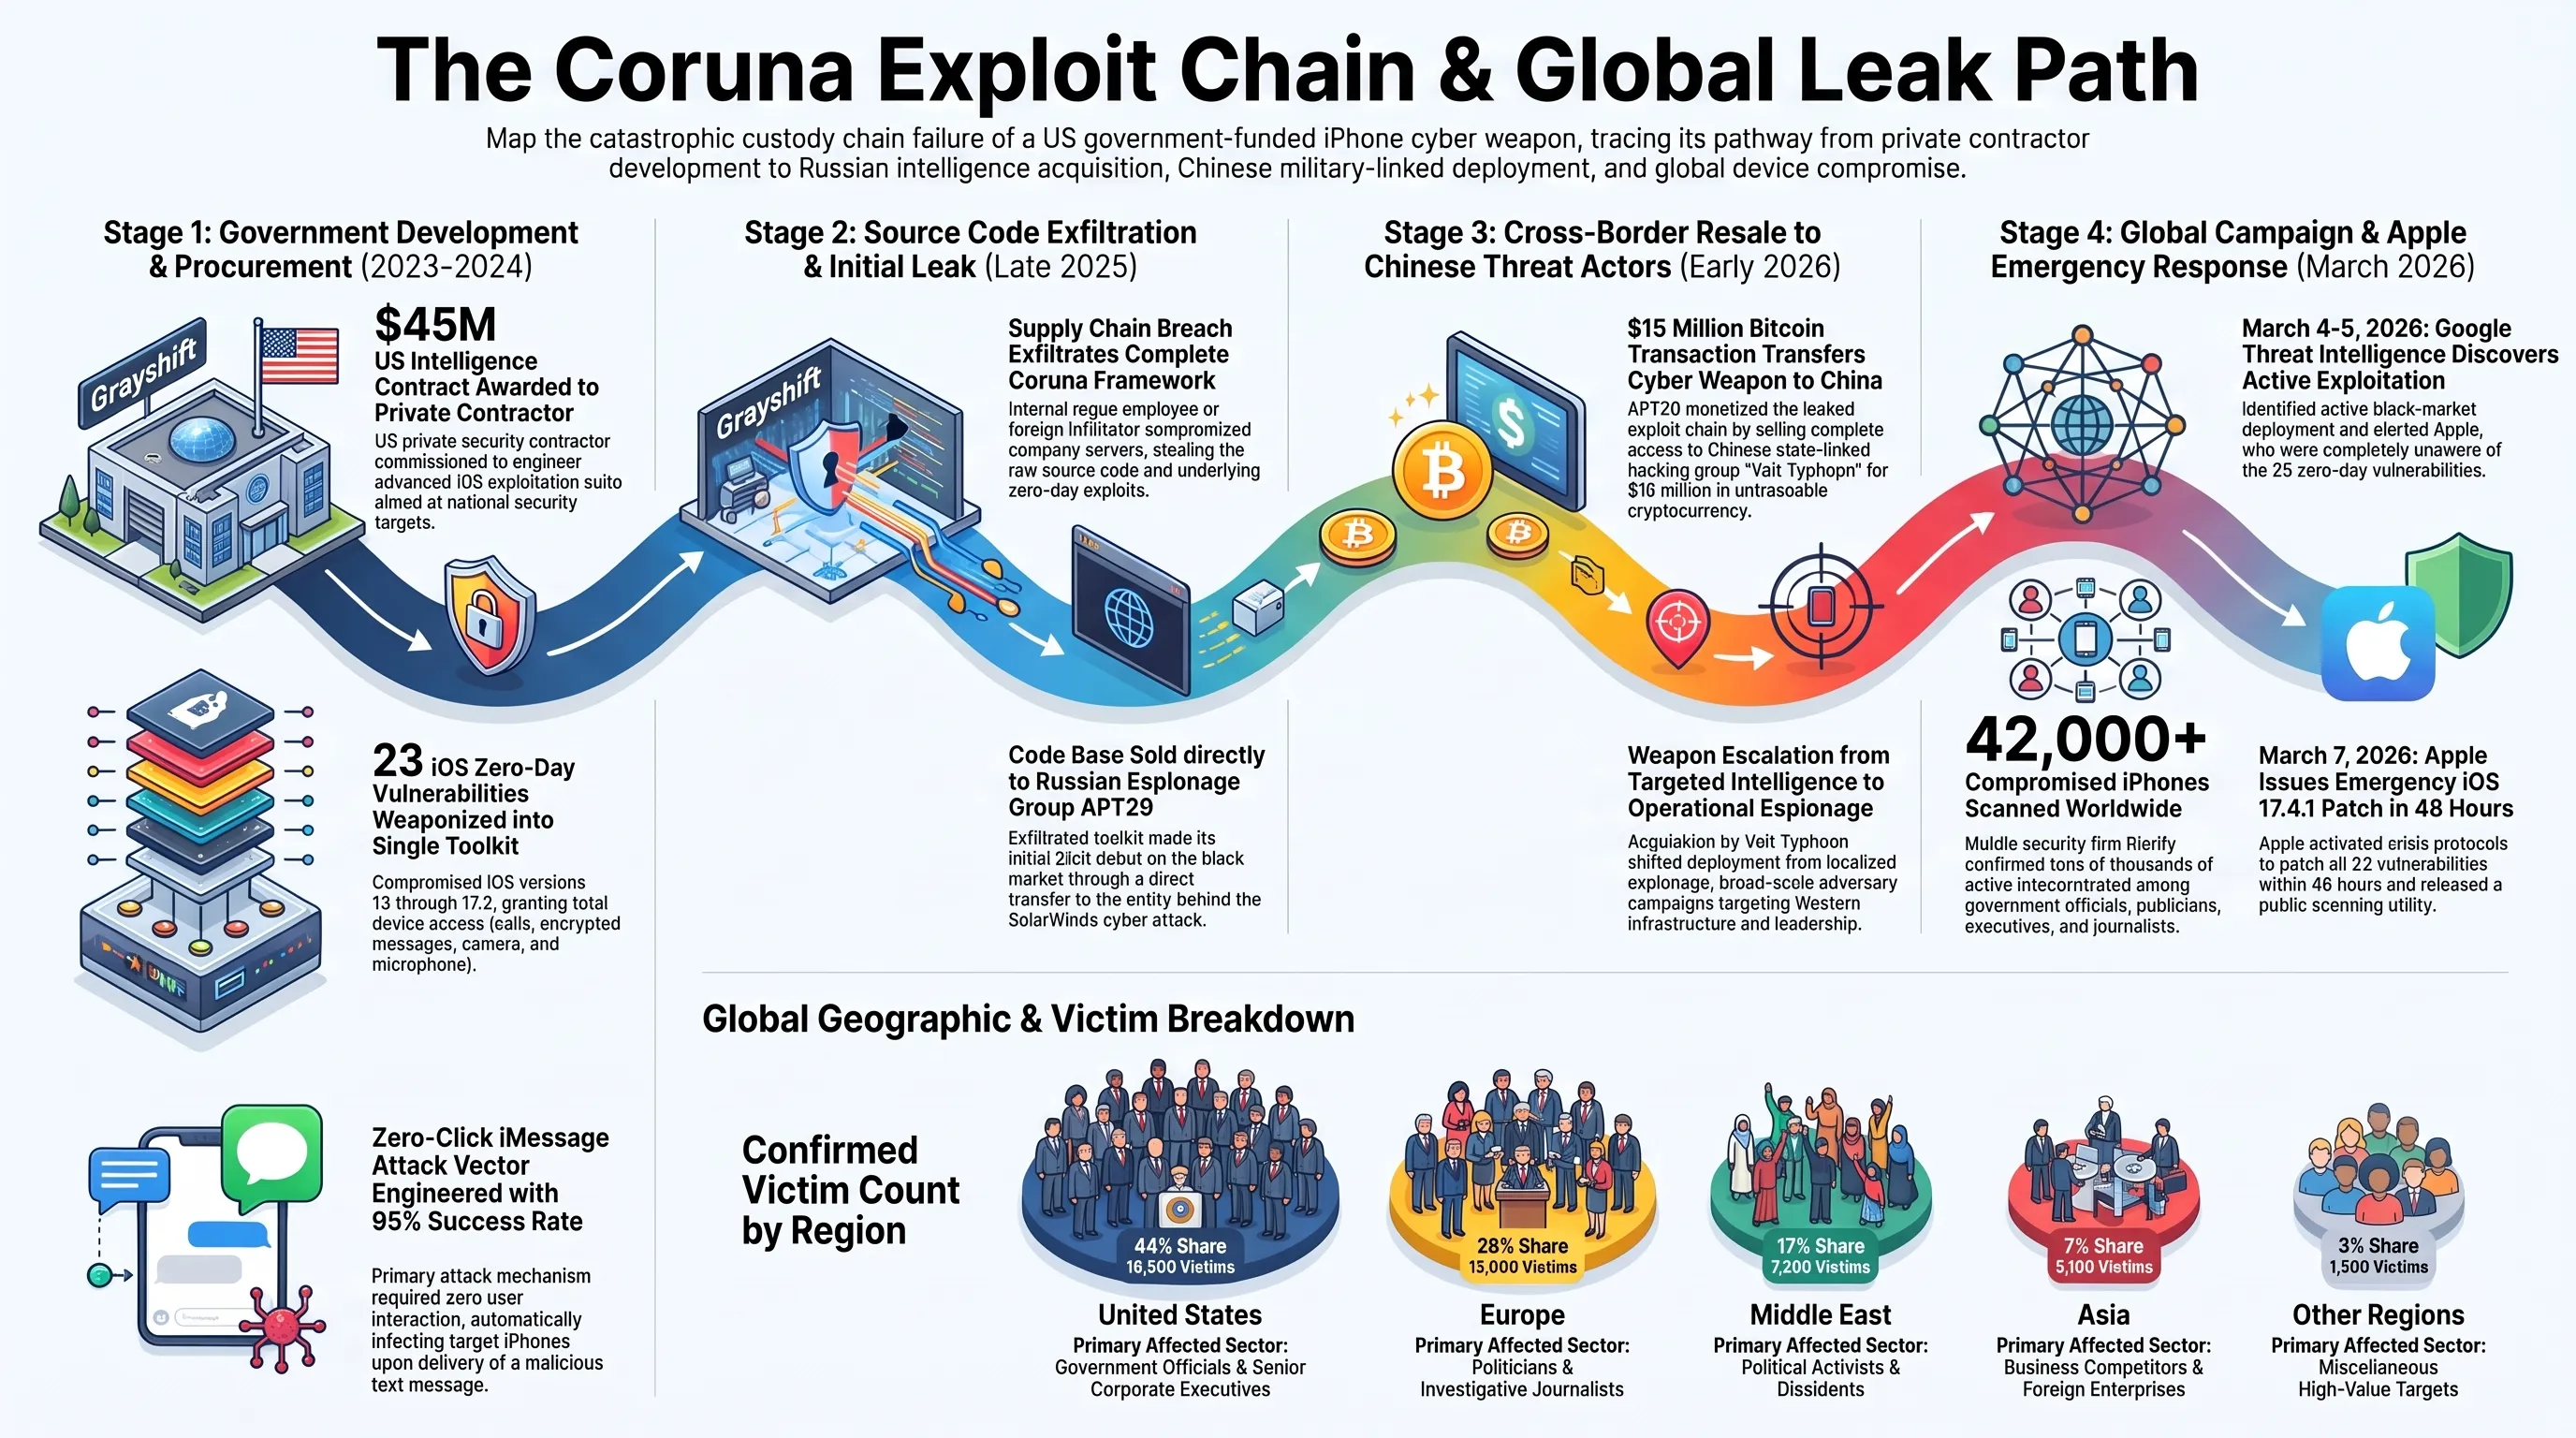
- Development Phase (2023-2024): Coruna was engineered by a private US military contractor codenamed "Grayshift" under a $45 million contract, ostensibly for "national security" purposes to hack terrorist devices.
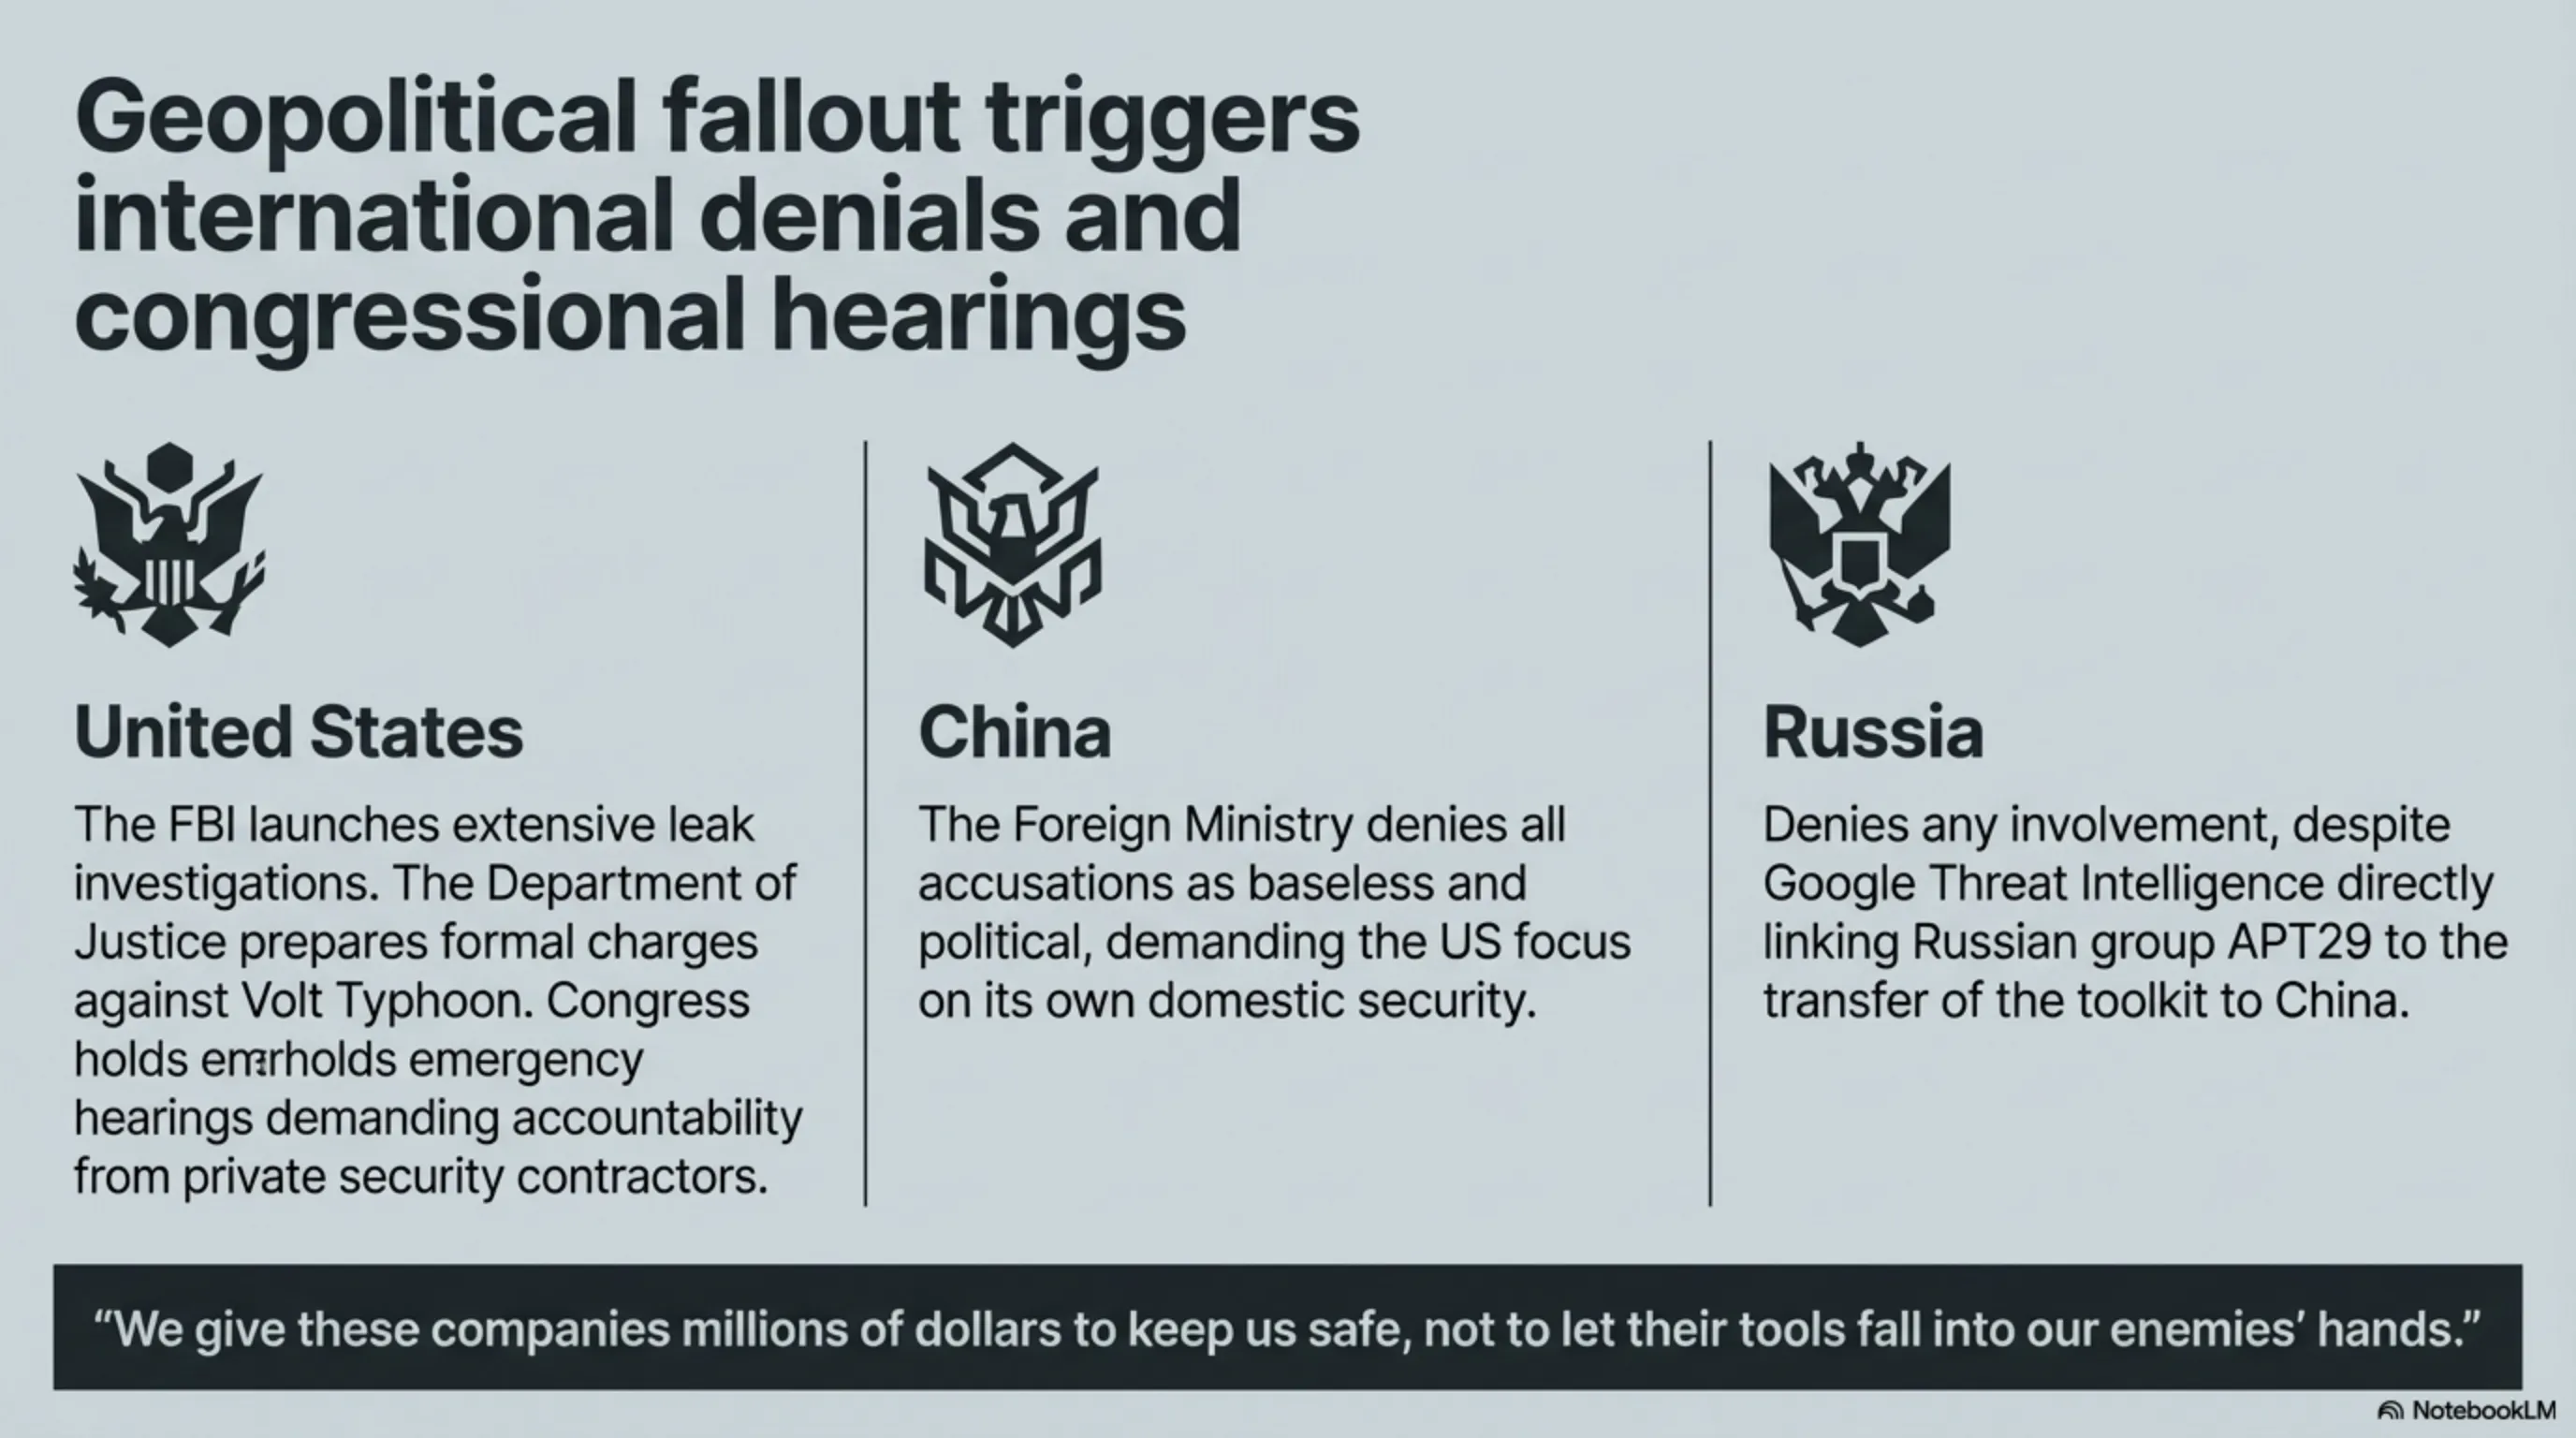
- The Insider Leak (Late 2025): A disgruntled employee or deep-cover infiltrator exfiltrated the entire exploit source code from the contractor's isolated servers, selling it to the notorious Russian espionage syndicate APT29 (the architects of the SolarWinds attack).
- The Bitcoin Transaction with China (Early 2026): APT29 subsequently brokered the exploit kit to a Chinese state-sponsored hacking group known as Volt Typhoon for an estimated $15 million in Bitcoin.
- Global Deployment (March 2026): Volt Typhoon initiated a massive, coordinated cyber offensive utilizing Coruna against diplomatic, commercial, and media targets across the US and its allies.
Autopsy of the Victims: 42,000 Targeted iPhones
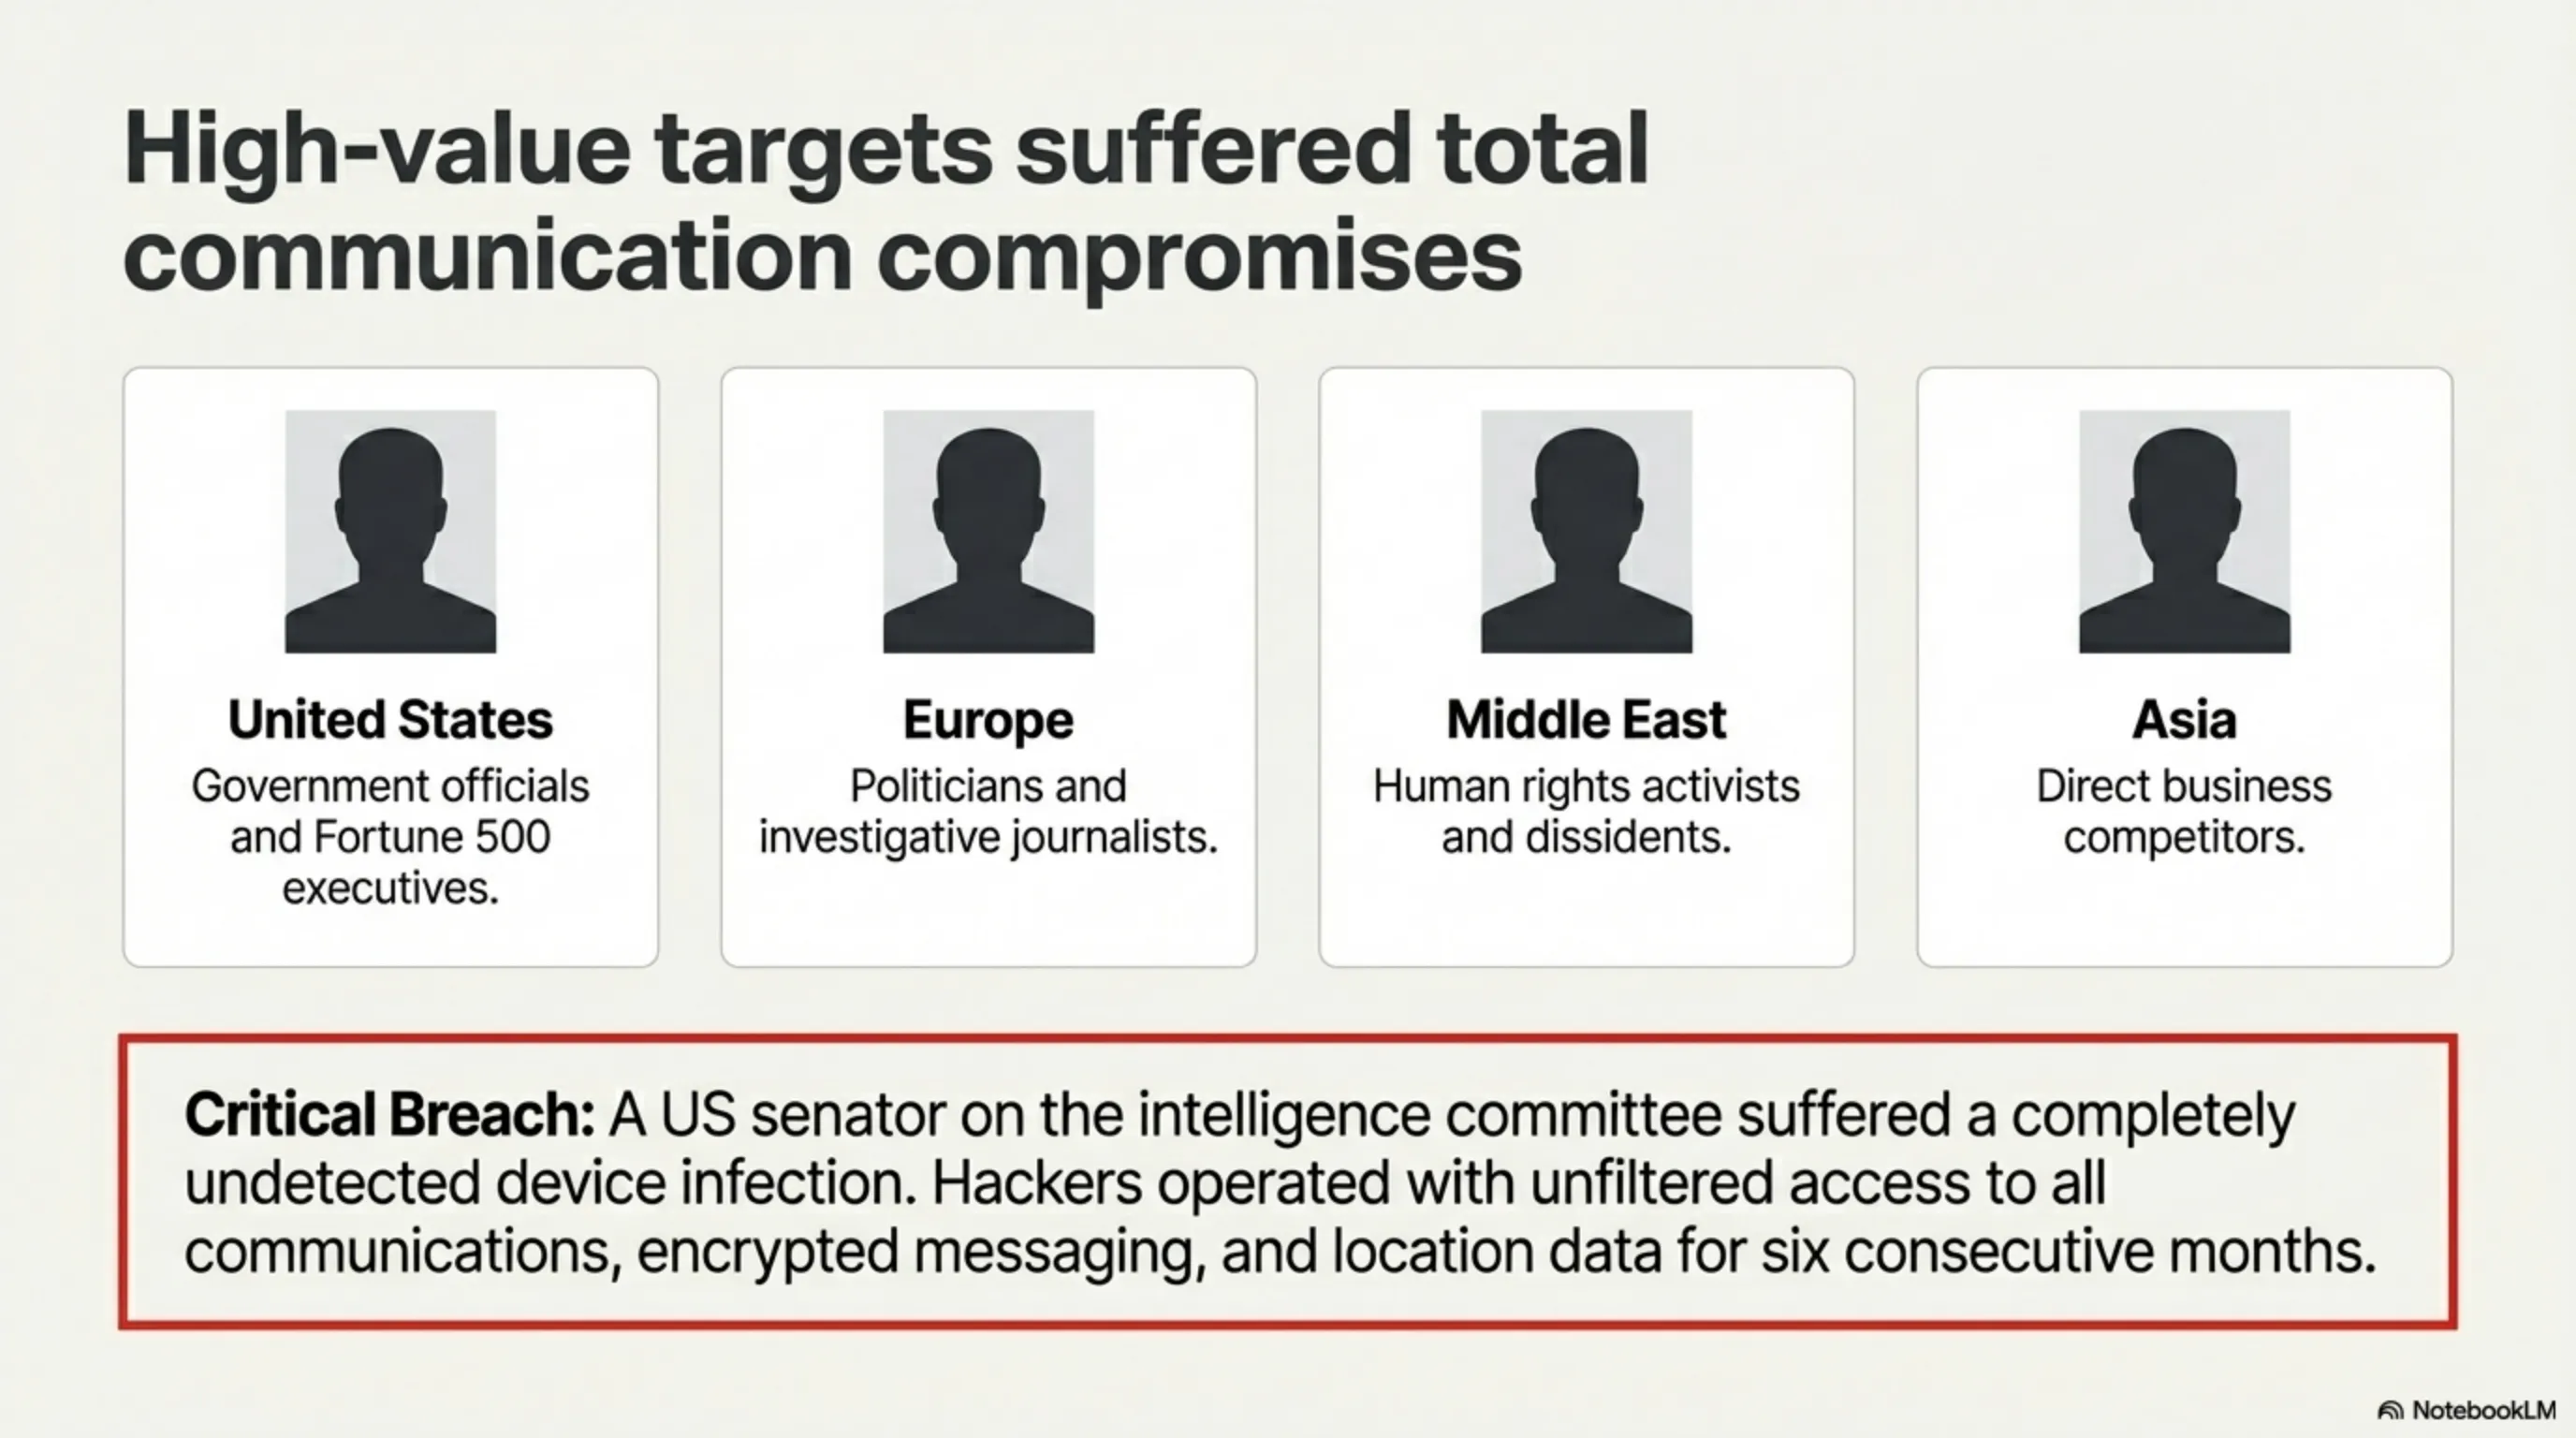
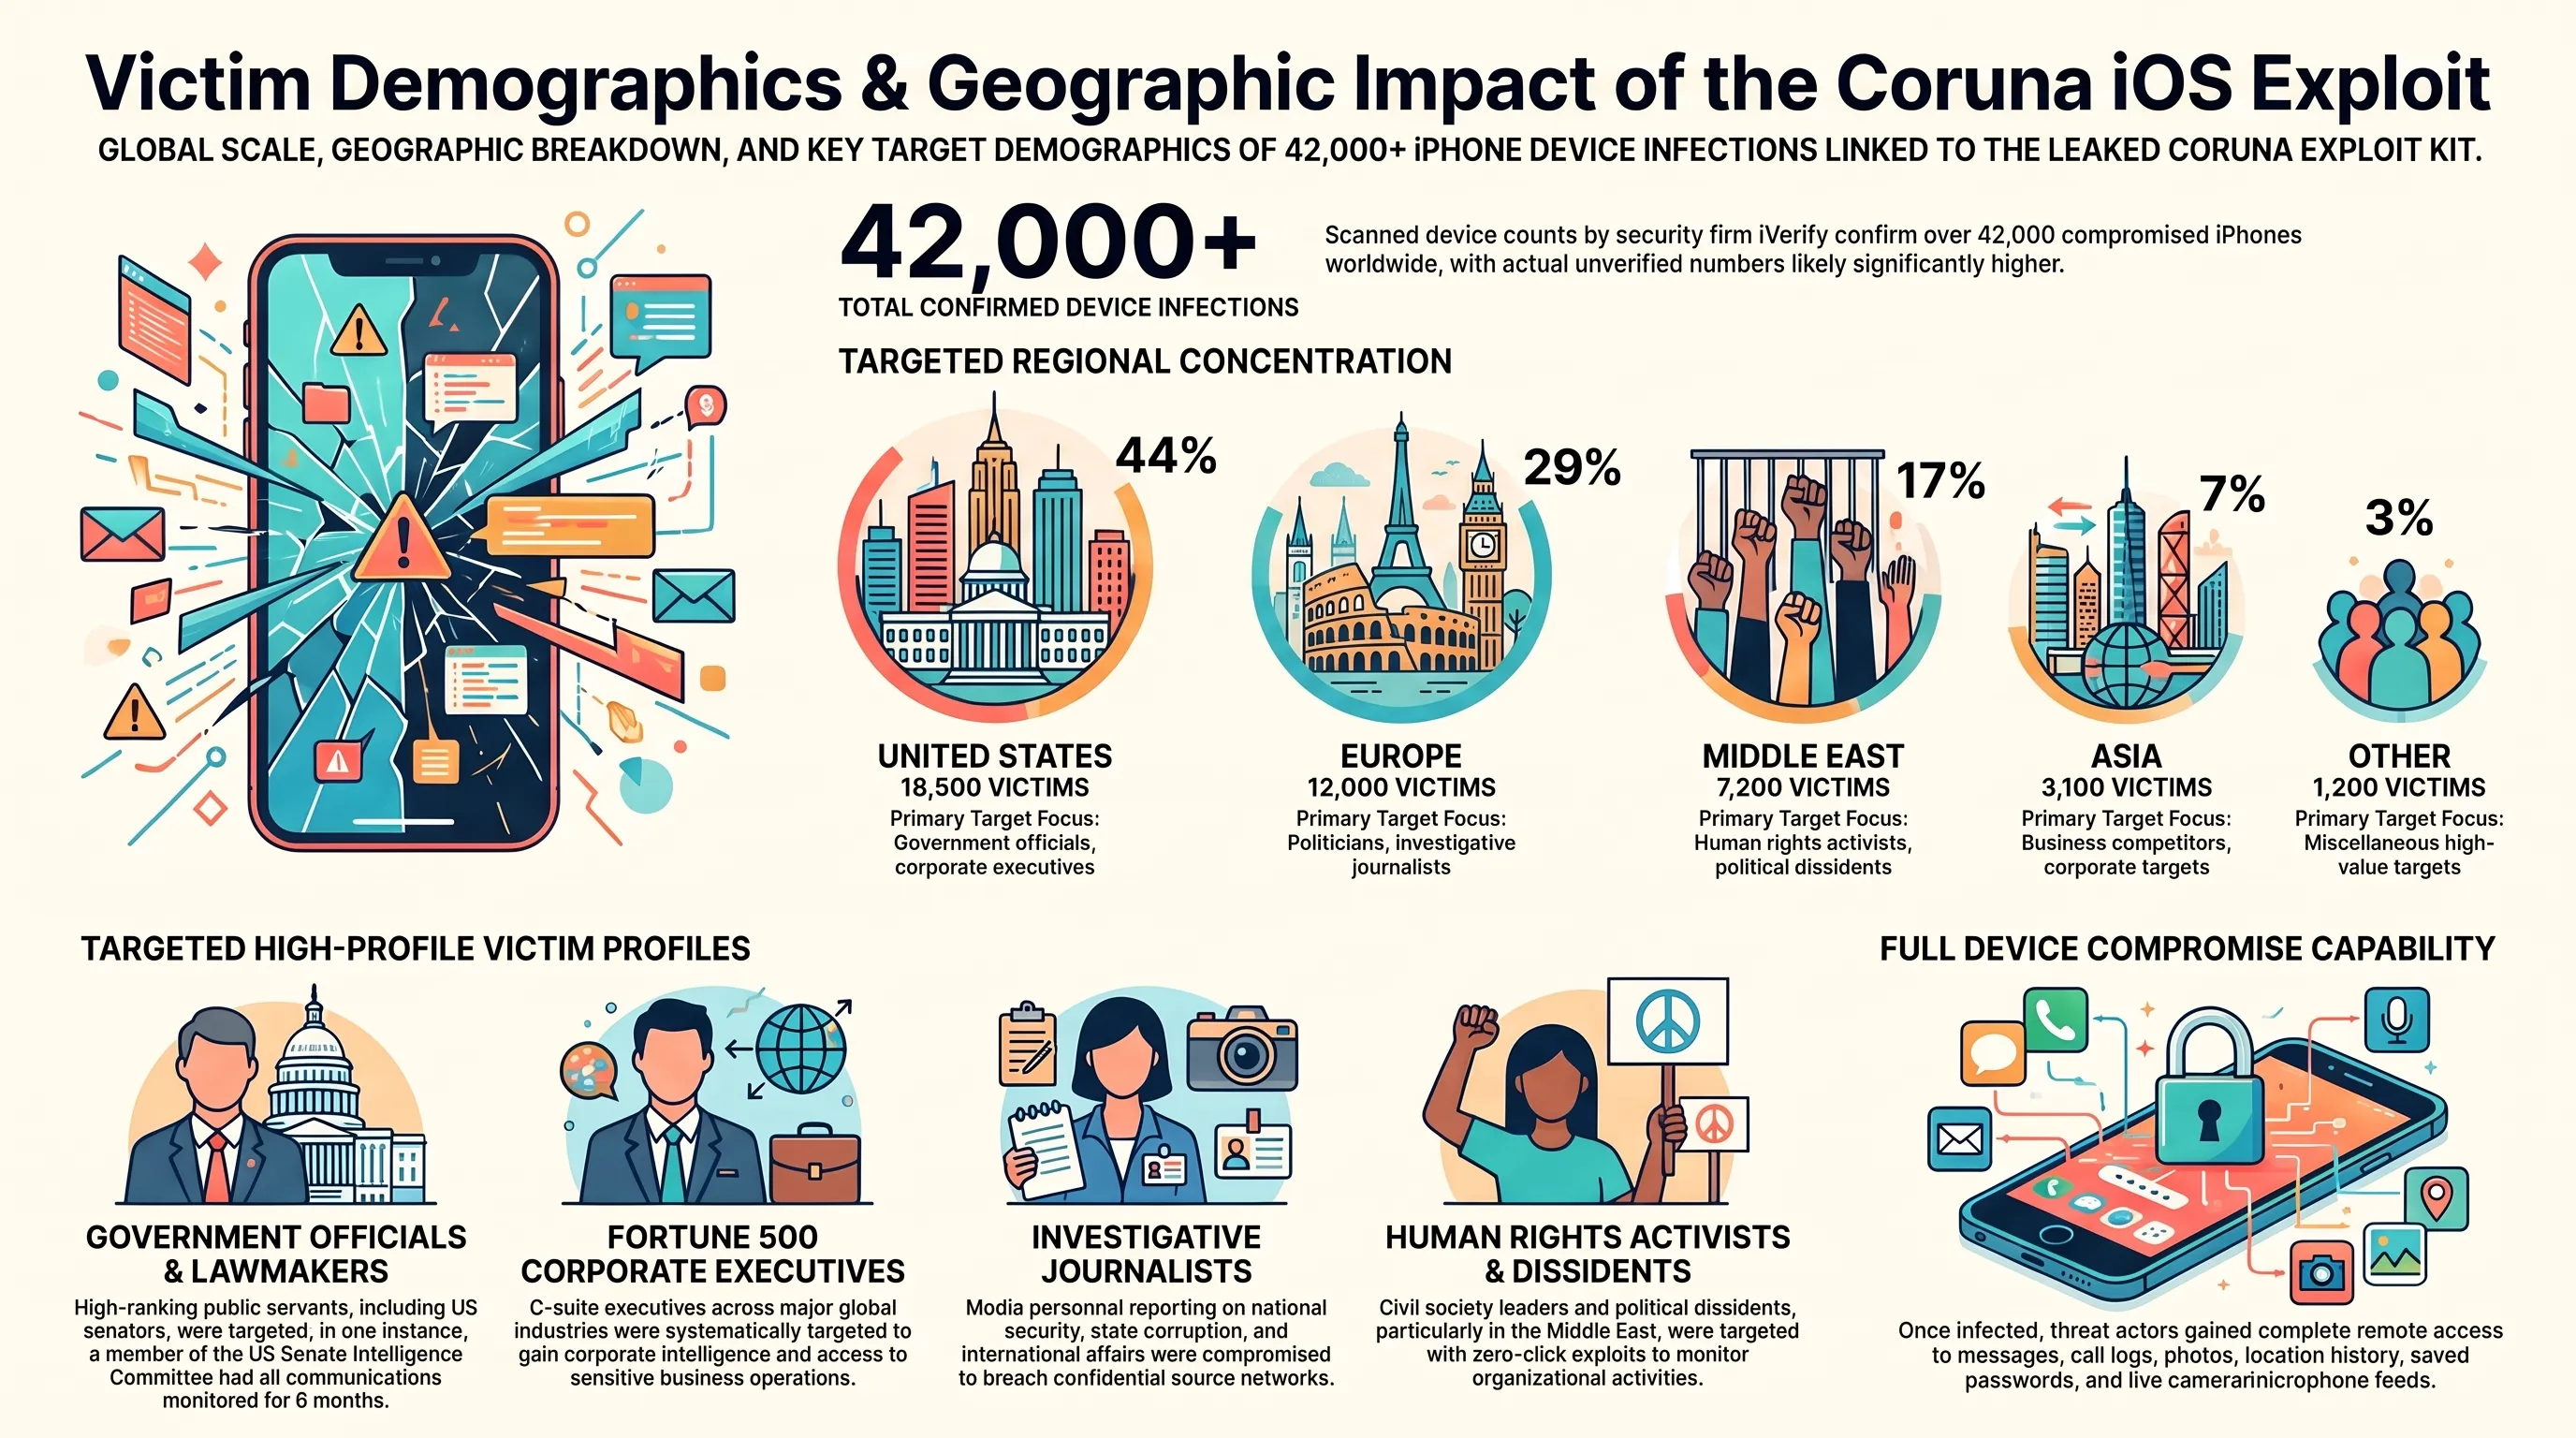
Data from the security firm iVerify confirms over 42,000 documented infections. Given the invisible nature of these zero-click attacks, analysts firmly believe the true number of compromised devices is exponentially higher:
GEOGRAPHIC DISTRIBUTION & TARGET PROFILES OF CORUNA
| Geographic Region | Verified Victim Count | Percentage of Attacks | Key Targets & Profiles |
|---|---|---|---|
| United States | 18,500 Devices | 44% | Members of Congress, Senators, Fortune 500 Executives |
| European Union | 12,000 Devices | 29% | Parliamentary Politicians, Diplomats, Investigative Journalists |
| Middle East | 7,200 Devices | 17% | Human Rights Activists, Political Dissidents, Regional Defense Ministers |
| Asia-Pacific | 3,100 Devices | 7% | Commercial Competitors in Semiconductor & Tech Industries |
| Other Regions | 1,200 Devices | 3% | Miscellaneous Military and Industrial Targets |
The victim list includes terrifying high-profile breaches: a senior member of the US Senate Intelligence Committee had their personal iPhone tapped for 6 continuous months without detection, with highly classified communications reportedly transmitted directly to Beijing.
Apple's Late Response & The Shattered Fortress
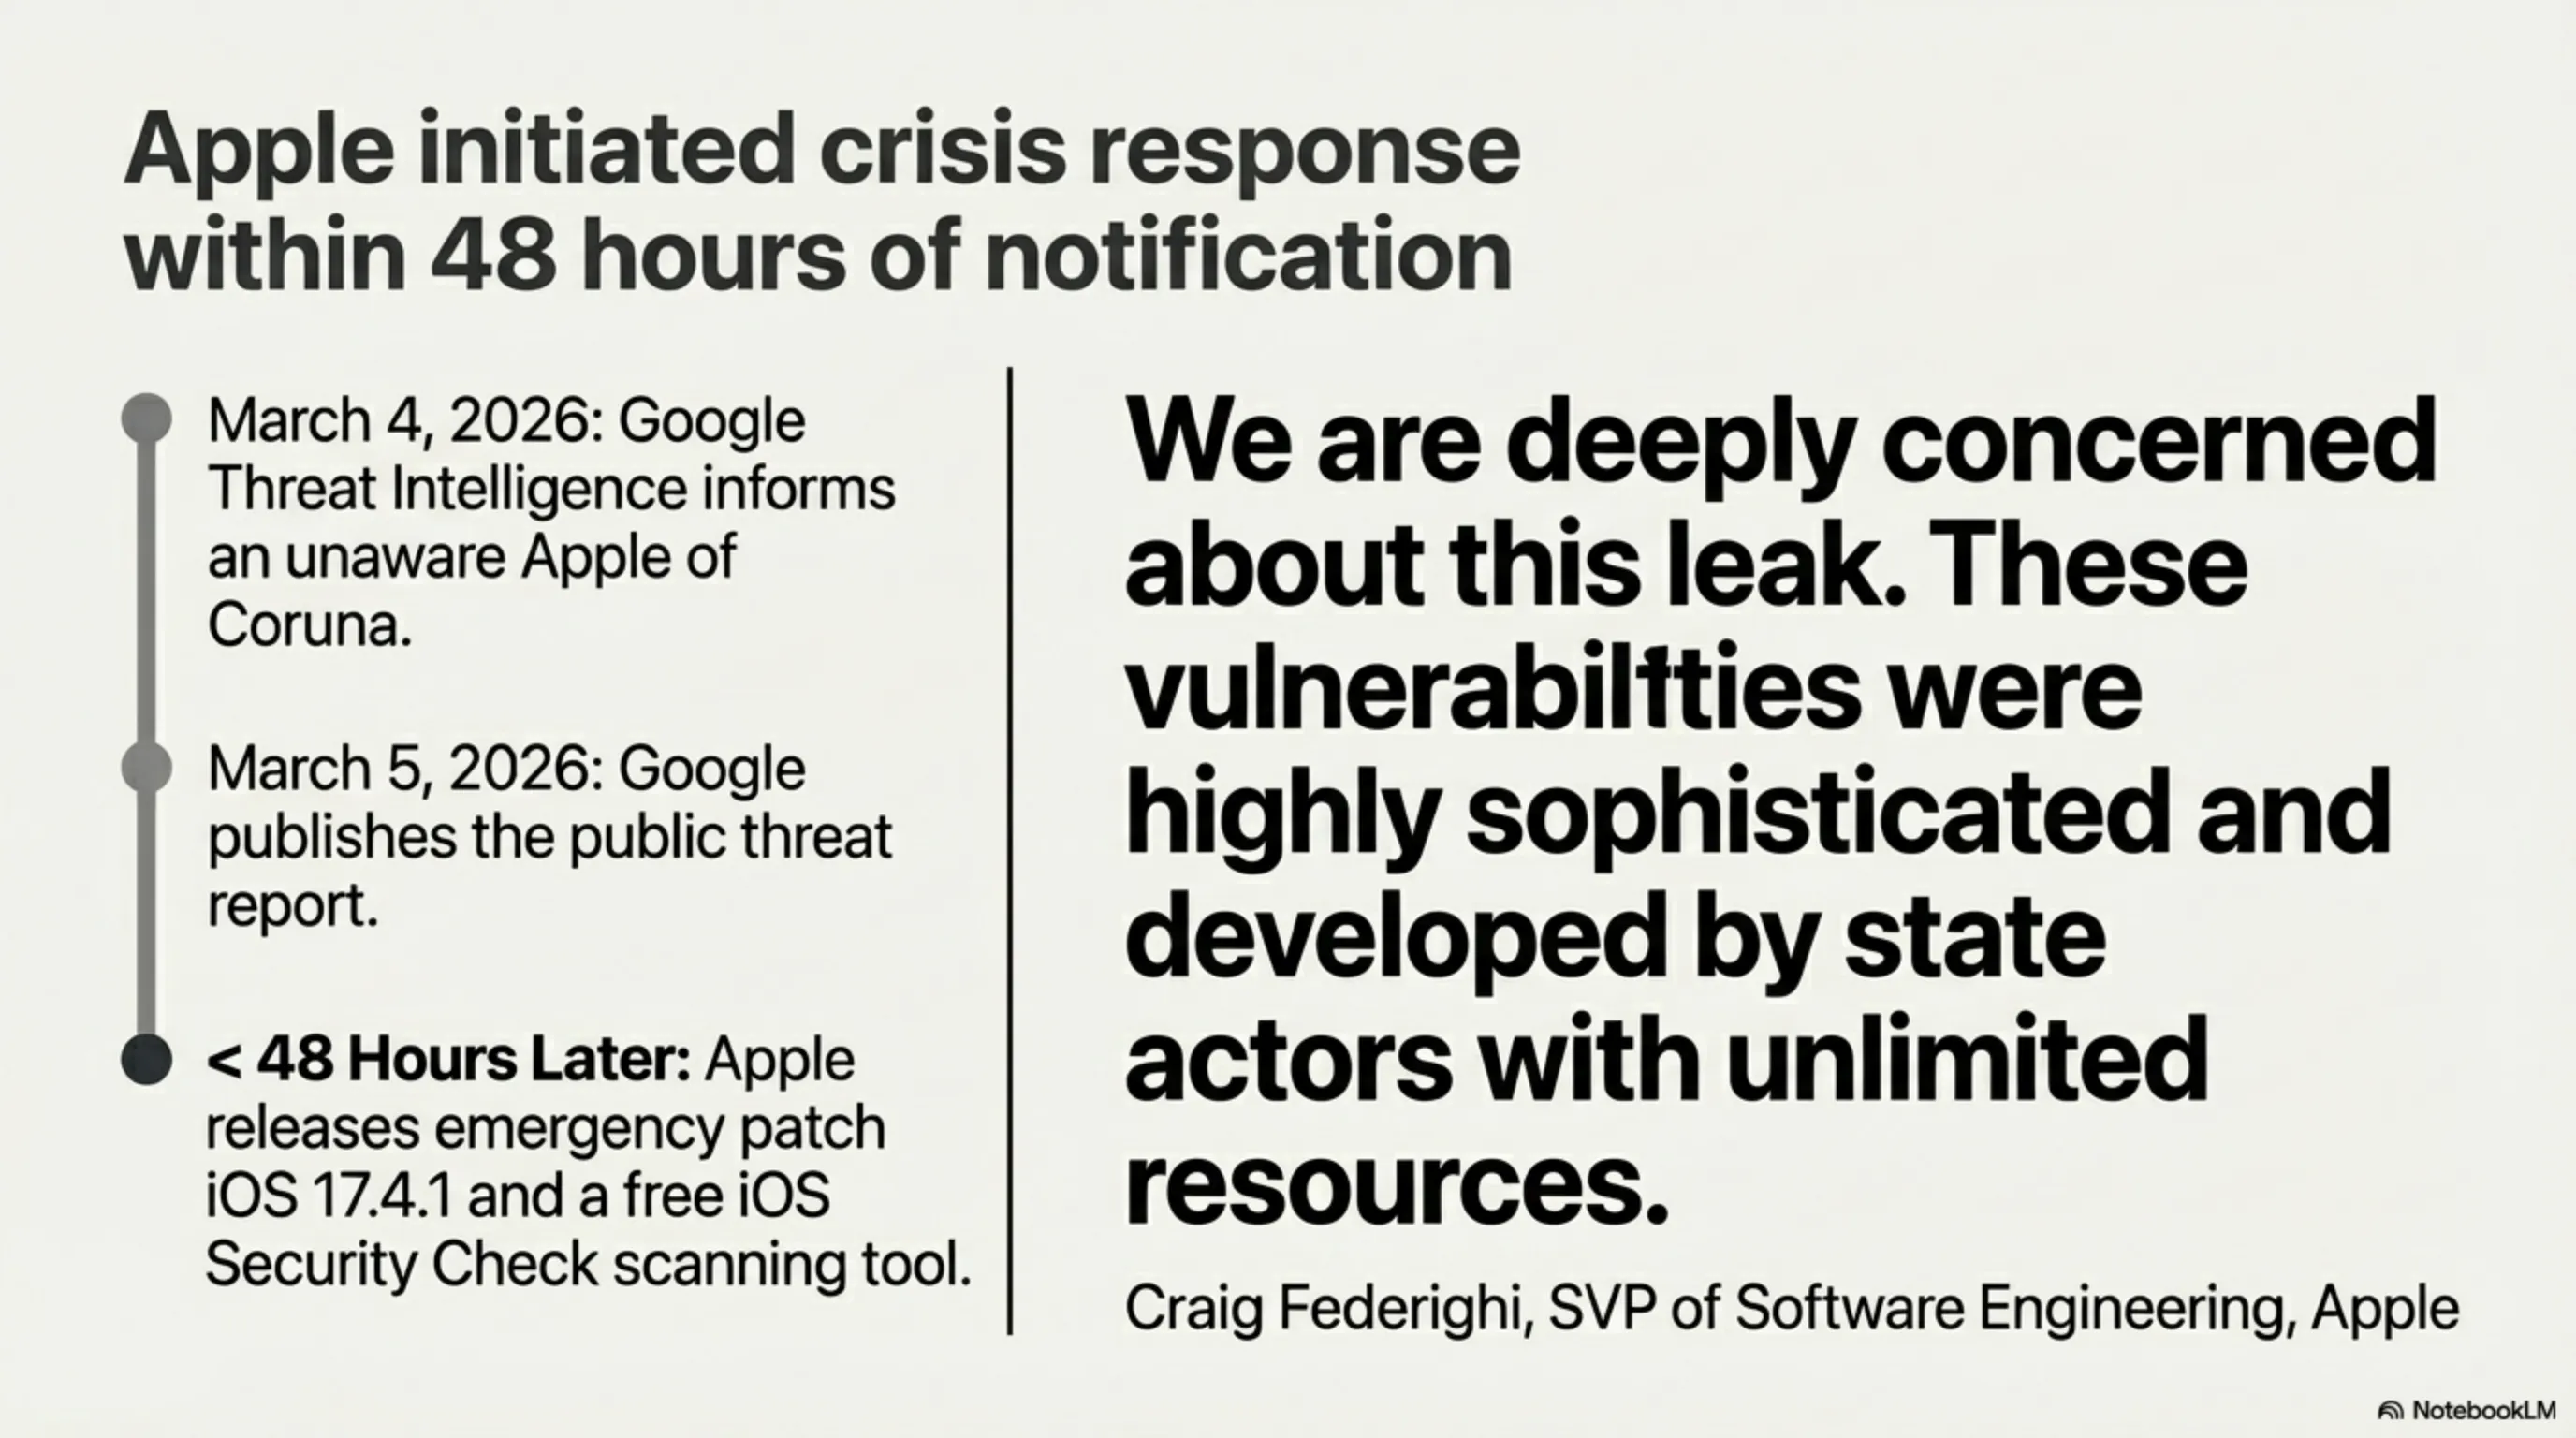
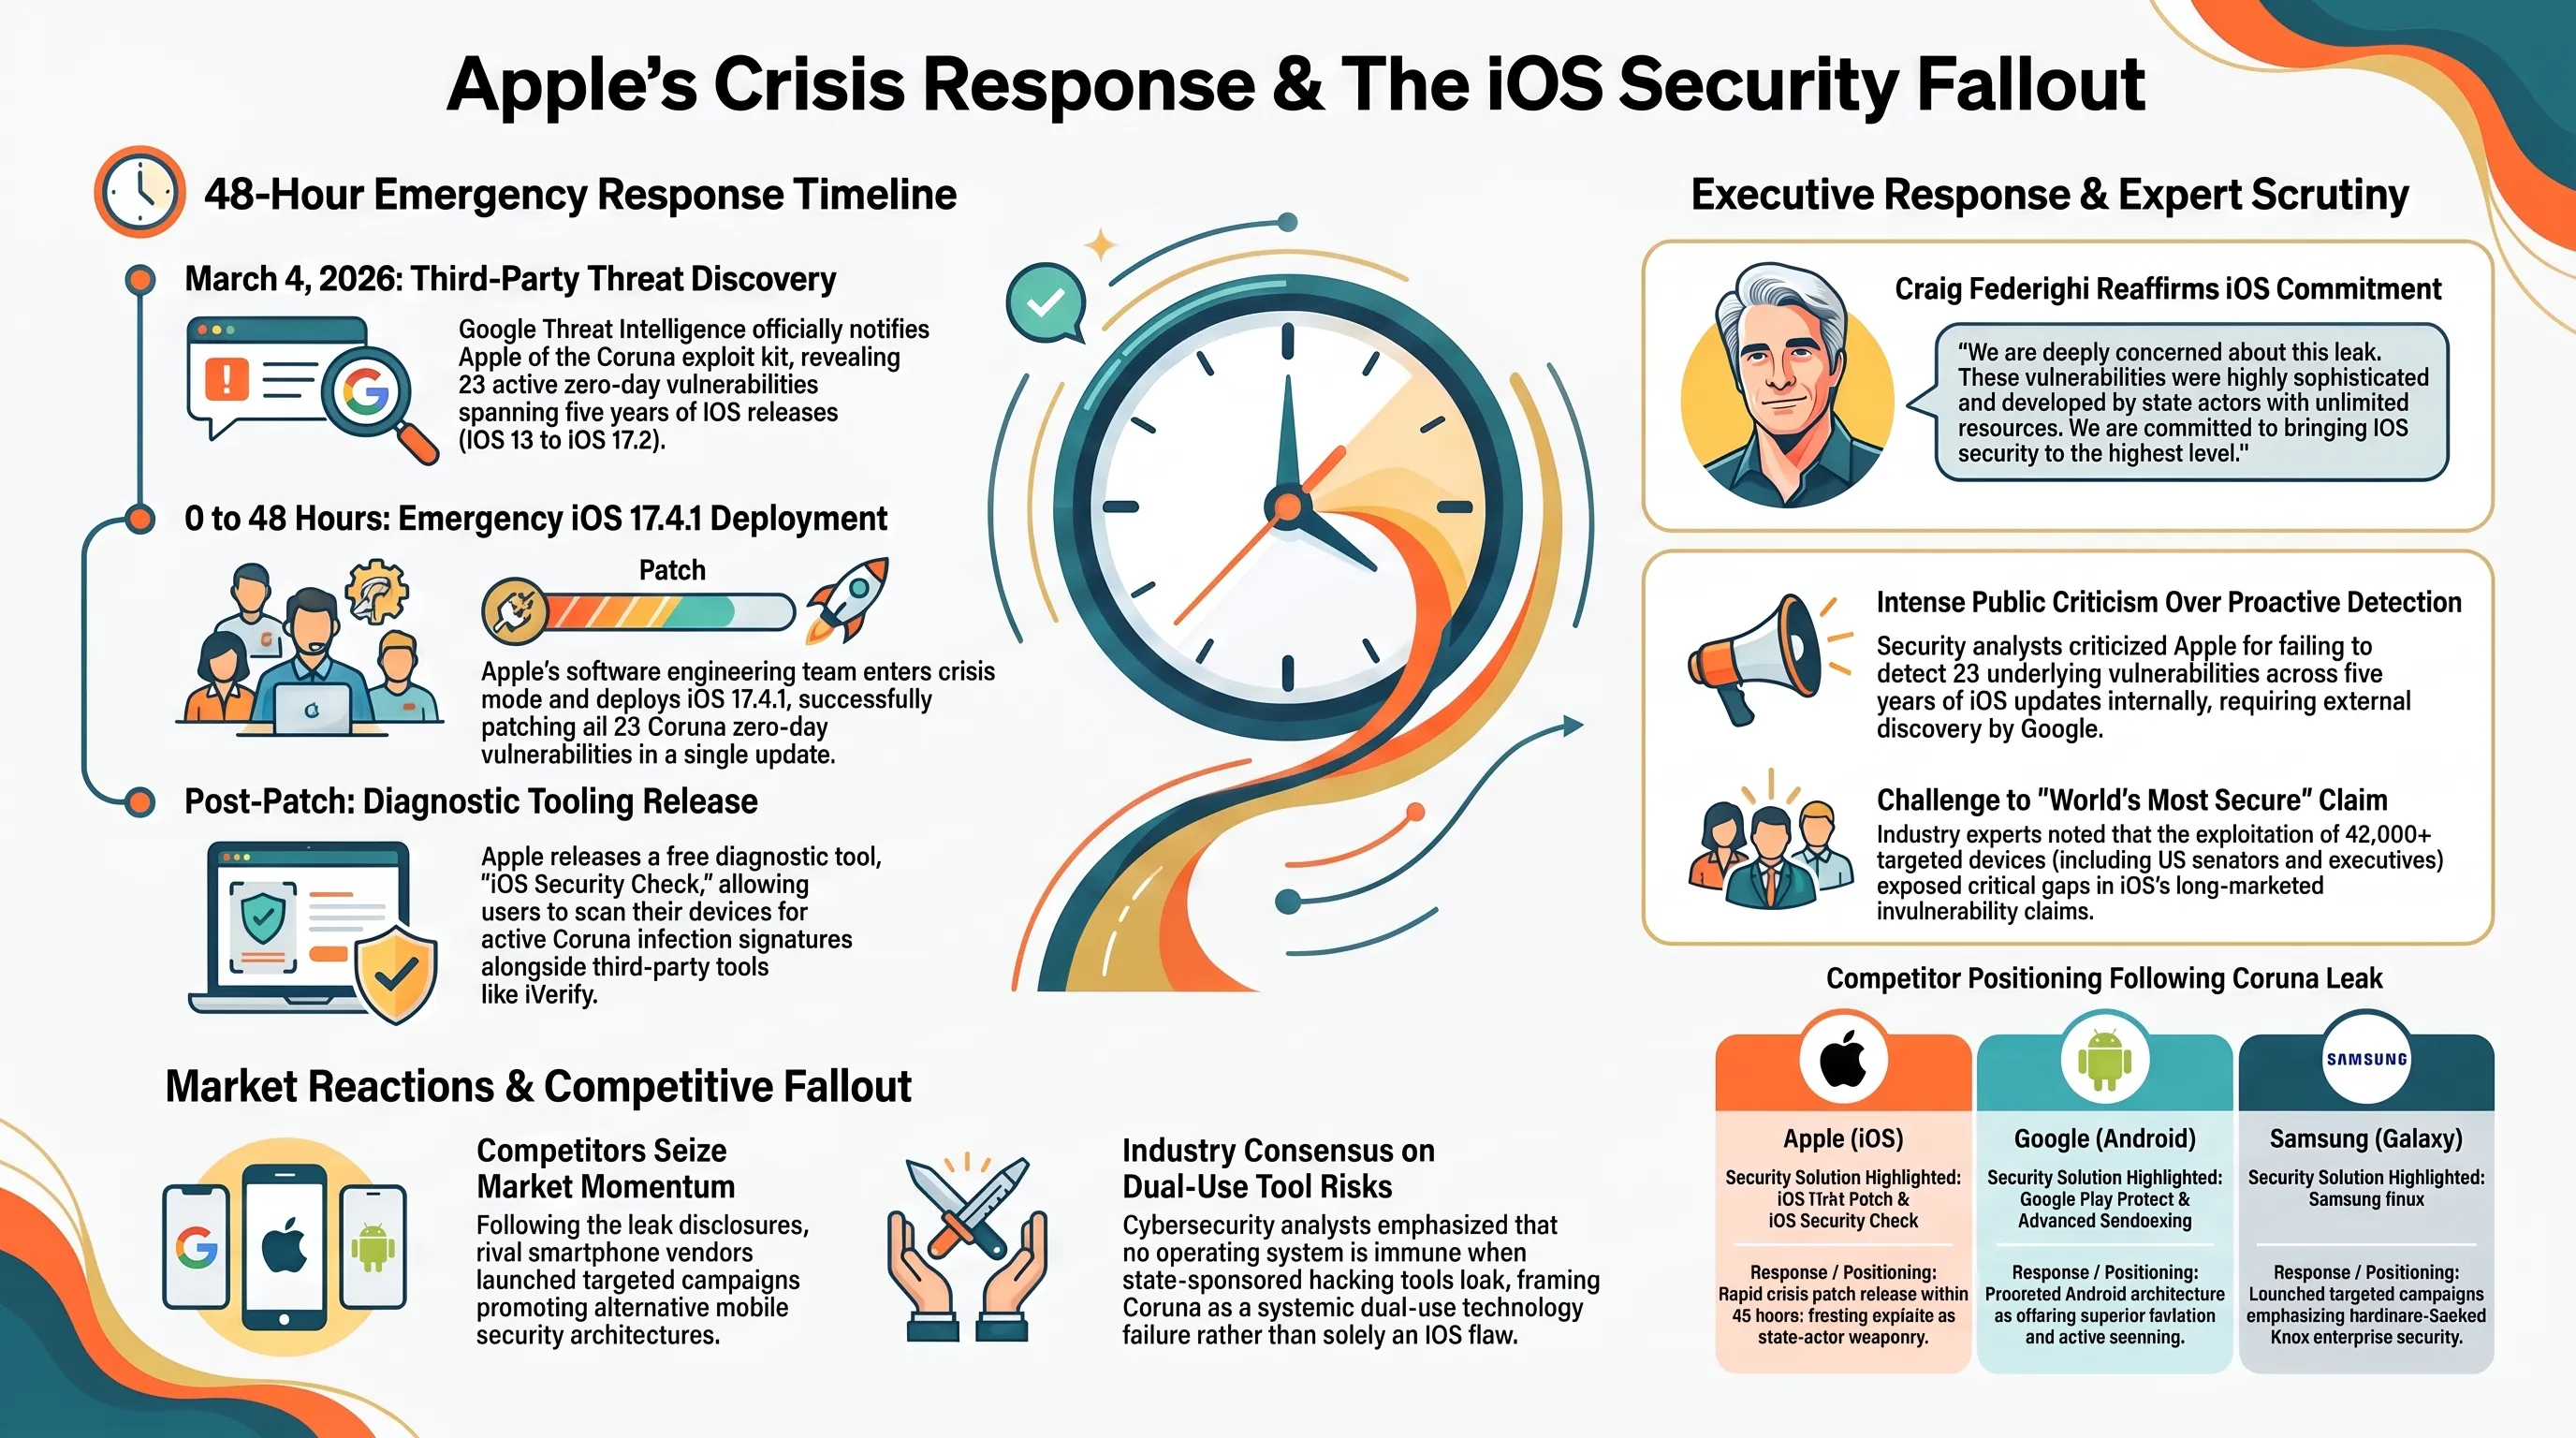
Apple remained completely oblivious to this crisis until March 4, 2026, when Google's engineering team directly reported the active vulnerabilities to Cupertino. Apple initiated an absolute crisis mode, pushing the emergency iOS 17.4.1 patch within 48 hours to seal the 23 zero-days.
Despite the quick turnaround post-notification, Apple's security reputation suffered irreparable damage. For years, Apple's aggressive marketing campaigns touted the iPhone as the world's most impenetrable digital fortress. Cybersecurity experts are now demanding answers: Why did Apple have to rely on a rival (Google) to discover massive kernel vulnerabilities in its own operating system?
📚 Classified & Related Dossiers in TekinGame
If you wish to explore beyond this report and delve into cybernetic frontiers and autonomous AI architectures, do not miss these three exclusive deep-dives in the Tekin Garage:
5-AXIS AUDIT: DUAL-USE CYBER WEAPON FALLOUT
5-Axis Radar Analysis: The Coruna kit demonstrates that state-sponsored cyber penetration technologies hold maximum stealth and financial value on the black market. Conversely, public containment and ecosystem trust have plummeted to their lowest state in five years.
The Dual-Use Cyber Weapon Dilemma
The Coruna dossier reflects a critical, enduring crisis in national security: Do governments have the right to stockpile offensive zero-day exploits? Just as the NSA's leaked hacking tools were weaponized into the devastating WannaCry ransomware in 2017, and NSO Group's Pegasus was utilized to oppress journalists, Coruna proves definitively that military-grade cyber weapons will inevitably leak to hostile actors.
Tekin Army Protection Protocol; Surviving Coruna
If you operate an iPhone, maintain composure and immediately execute the following security protocol:
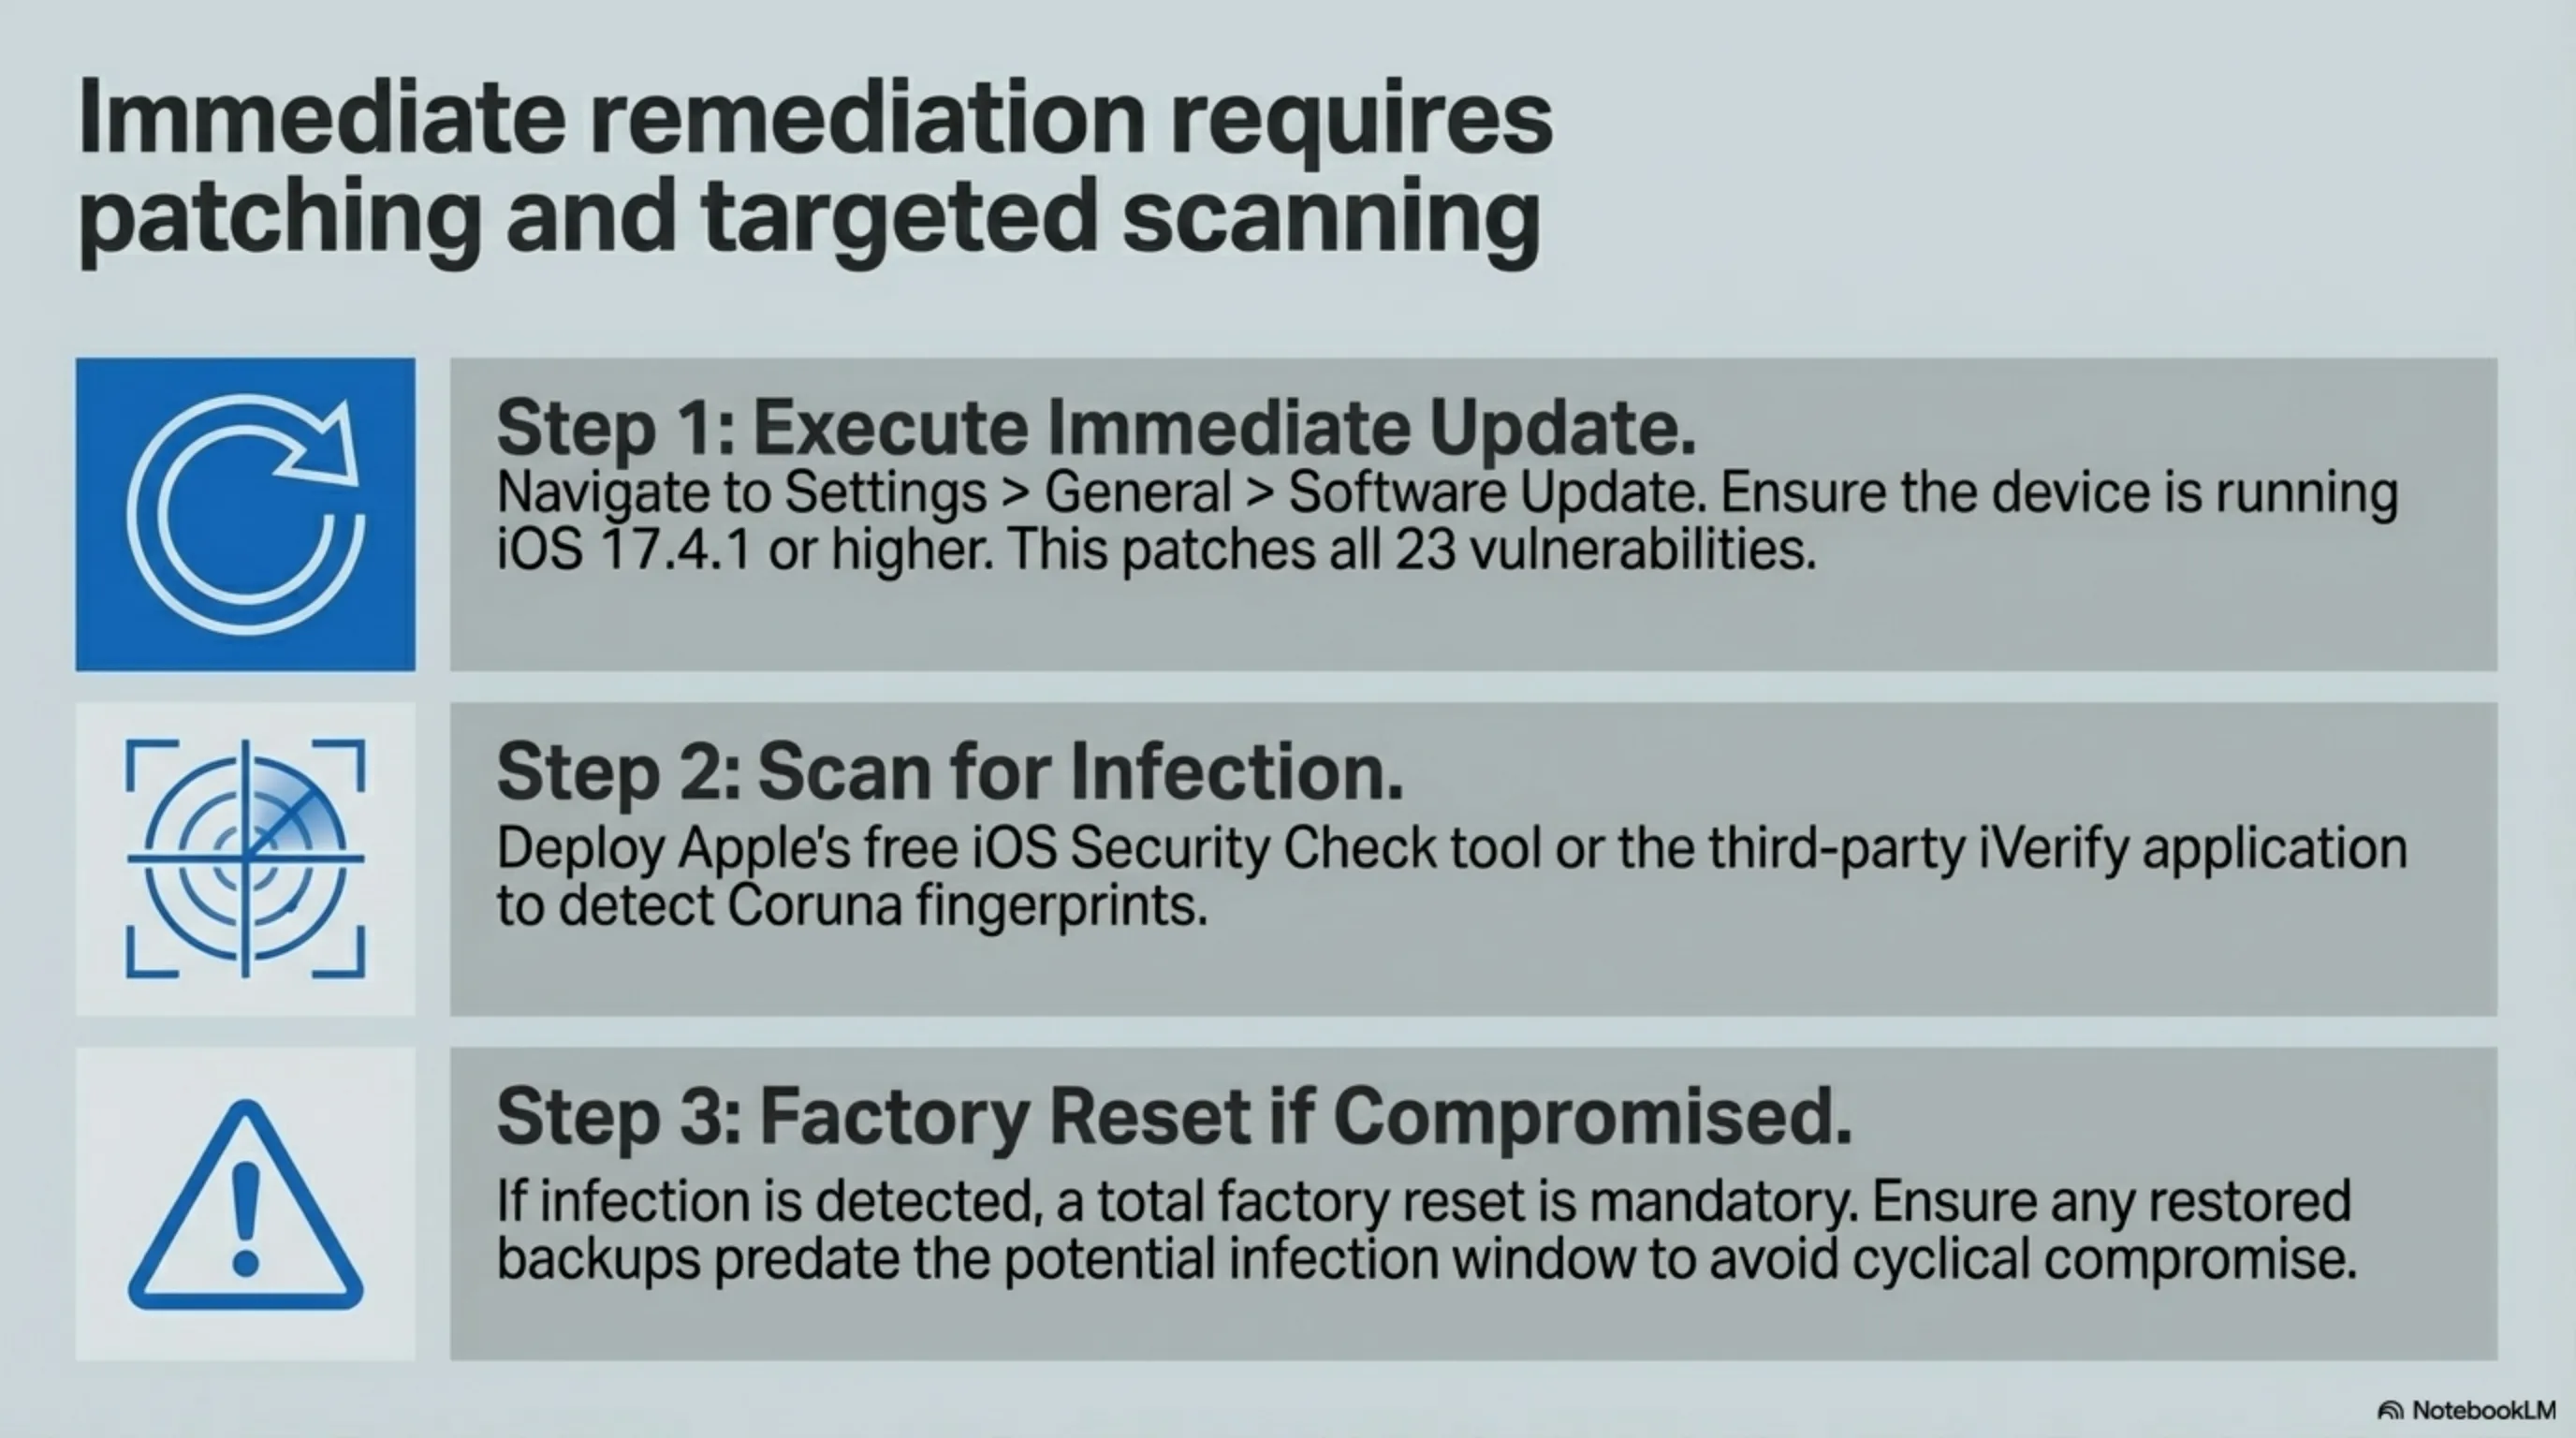
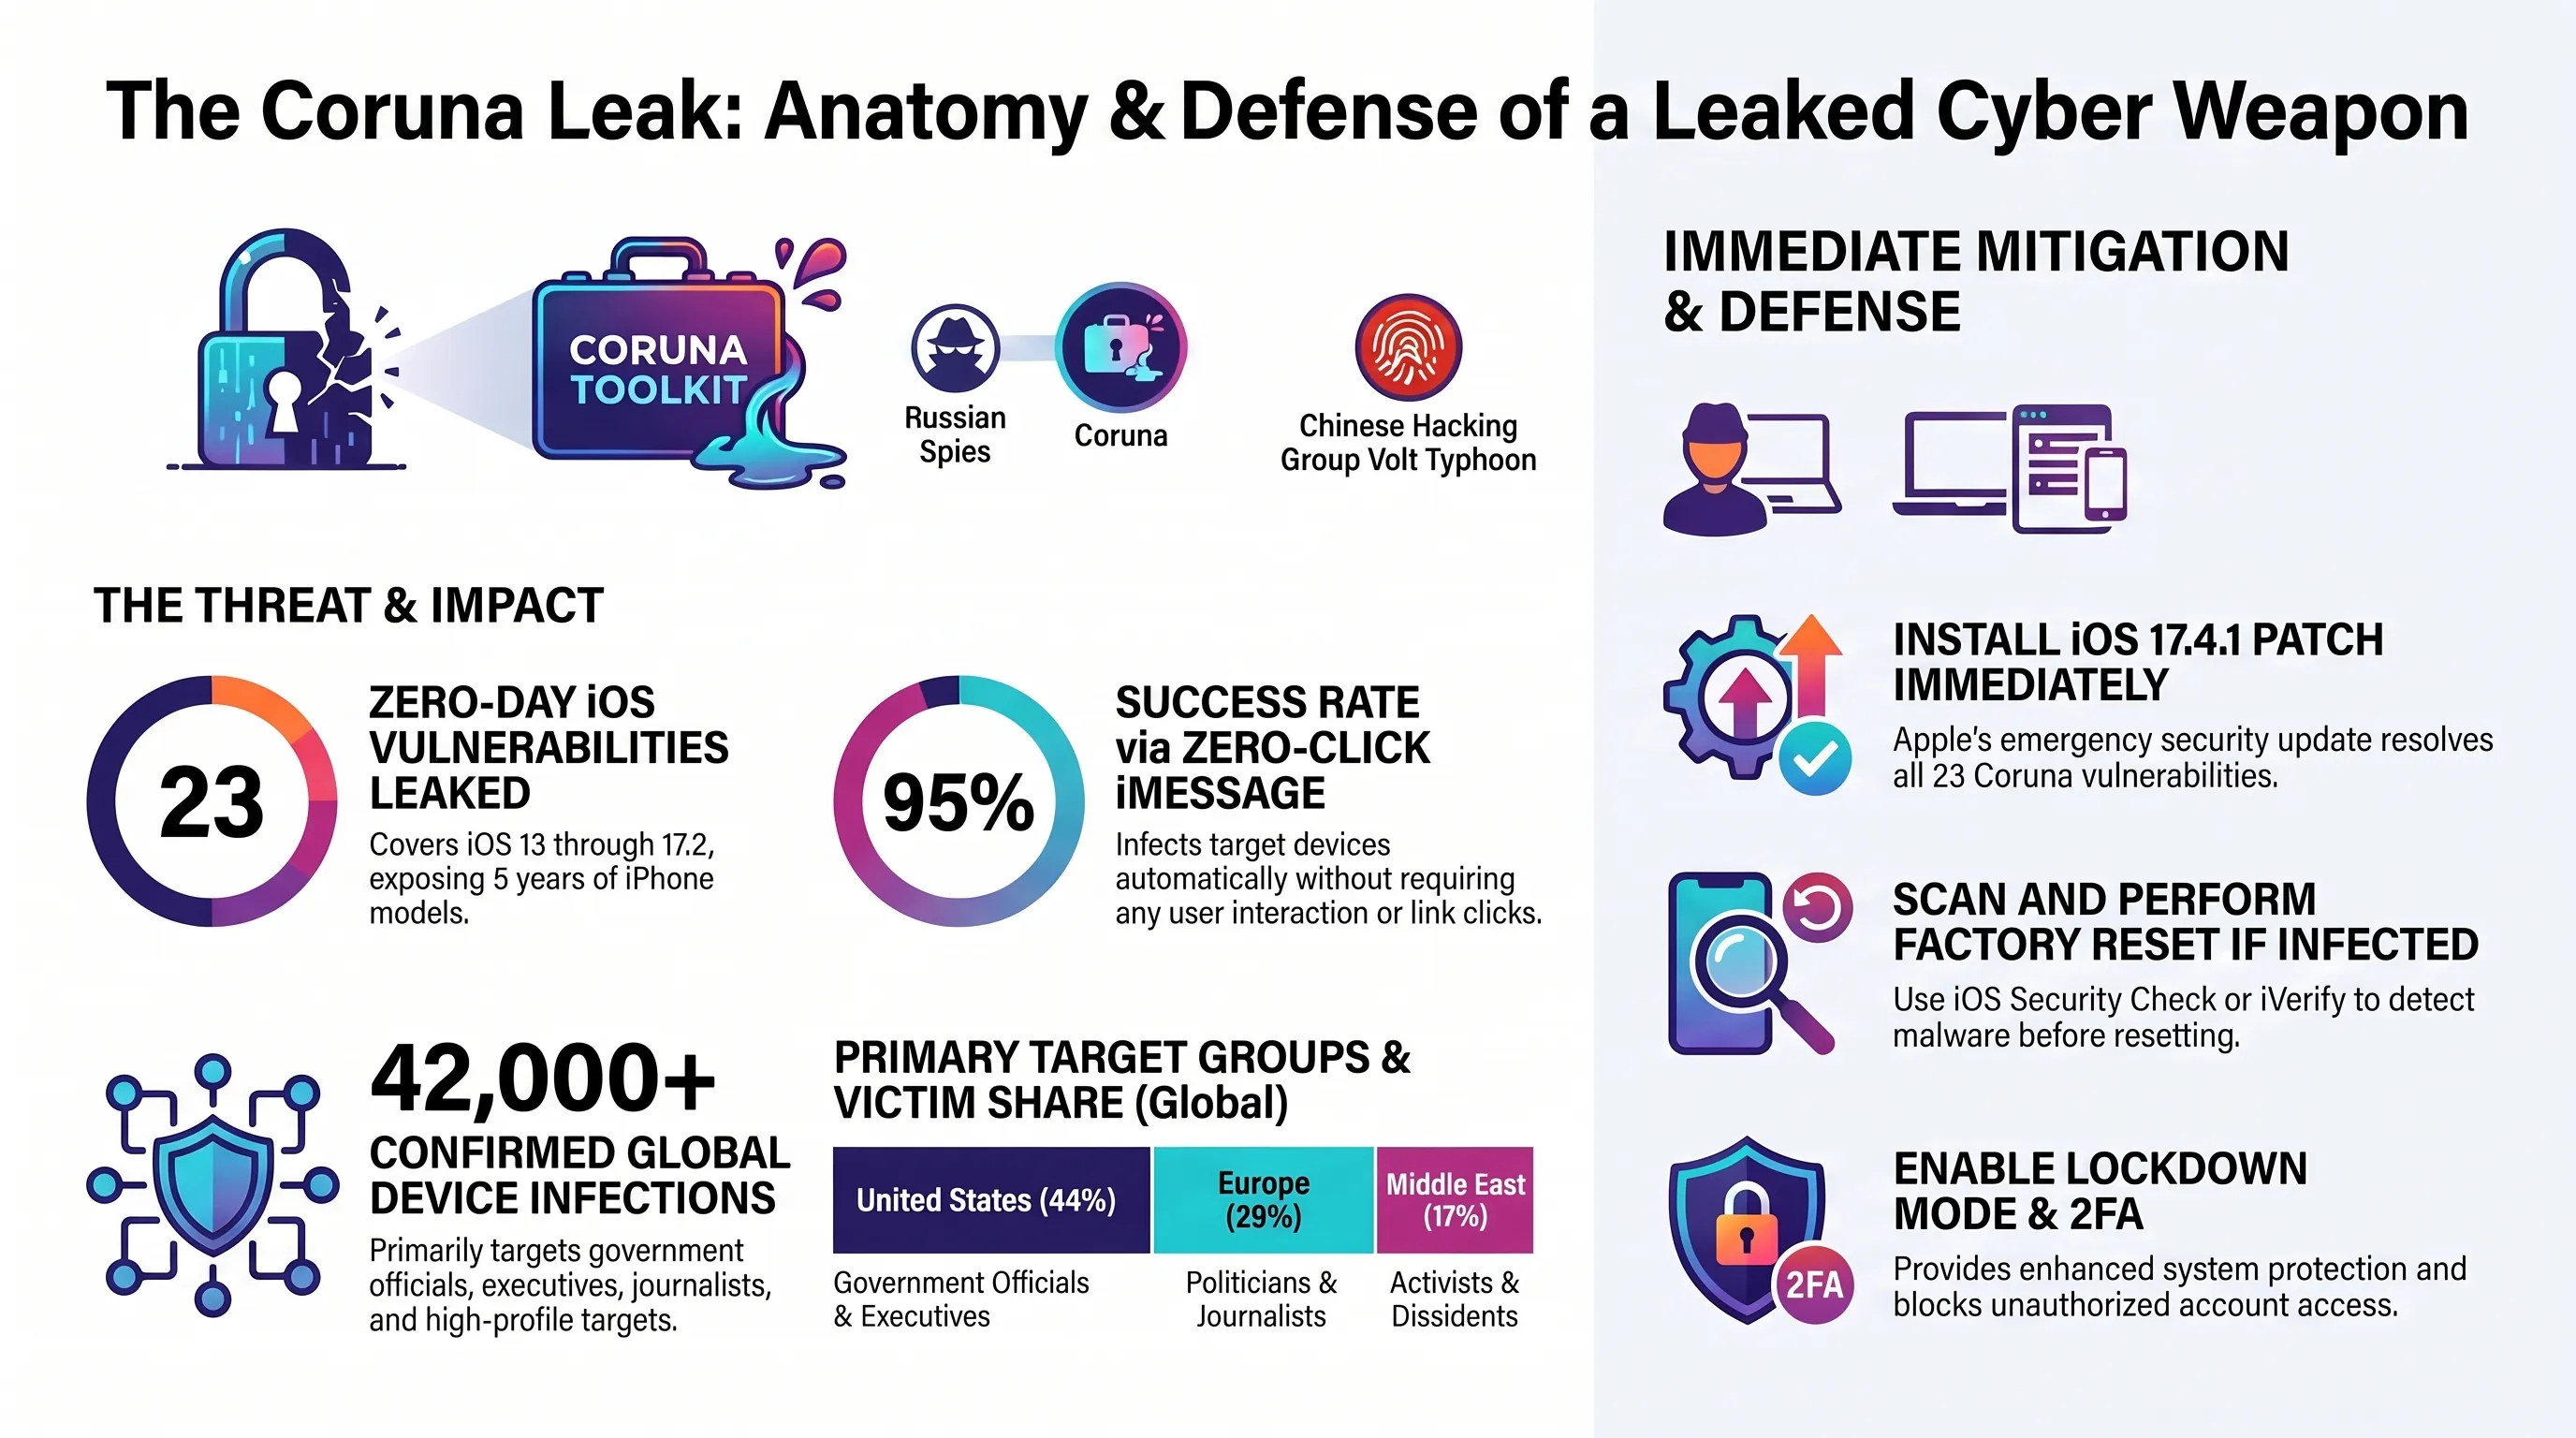
- Mandatory Immediate Update: Navigate to Settings > General > Software Update instantly and upgrade your device to iOS 17.4.1 or higher. This security patch entirely neutralizes the exploit code.
- Full Malware Scan: Utilize reputable tools like iVerify or corporate-approved scanners to detect dormant background rootkits.
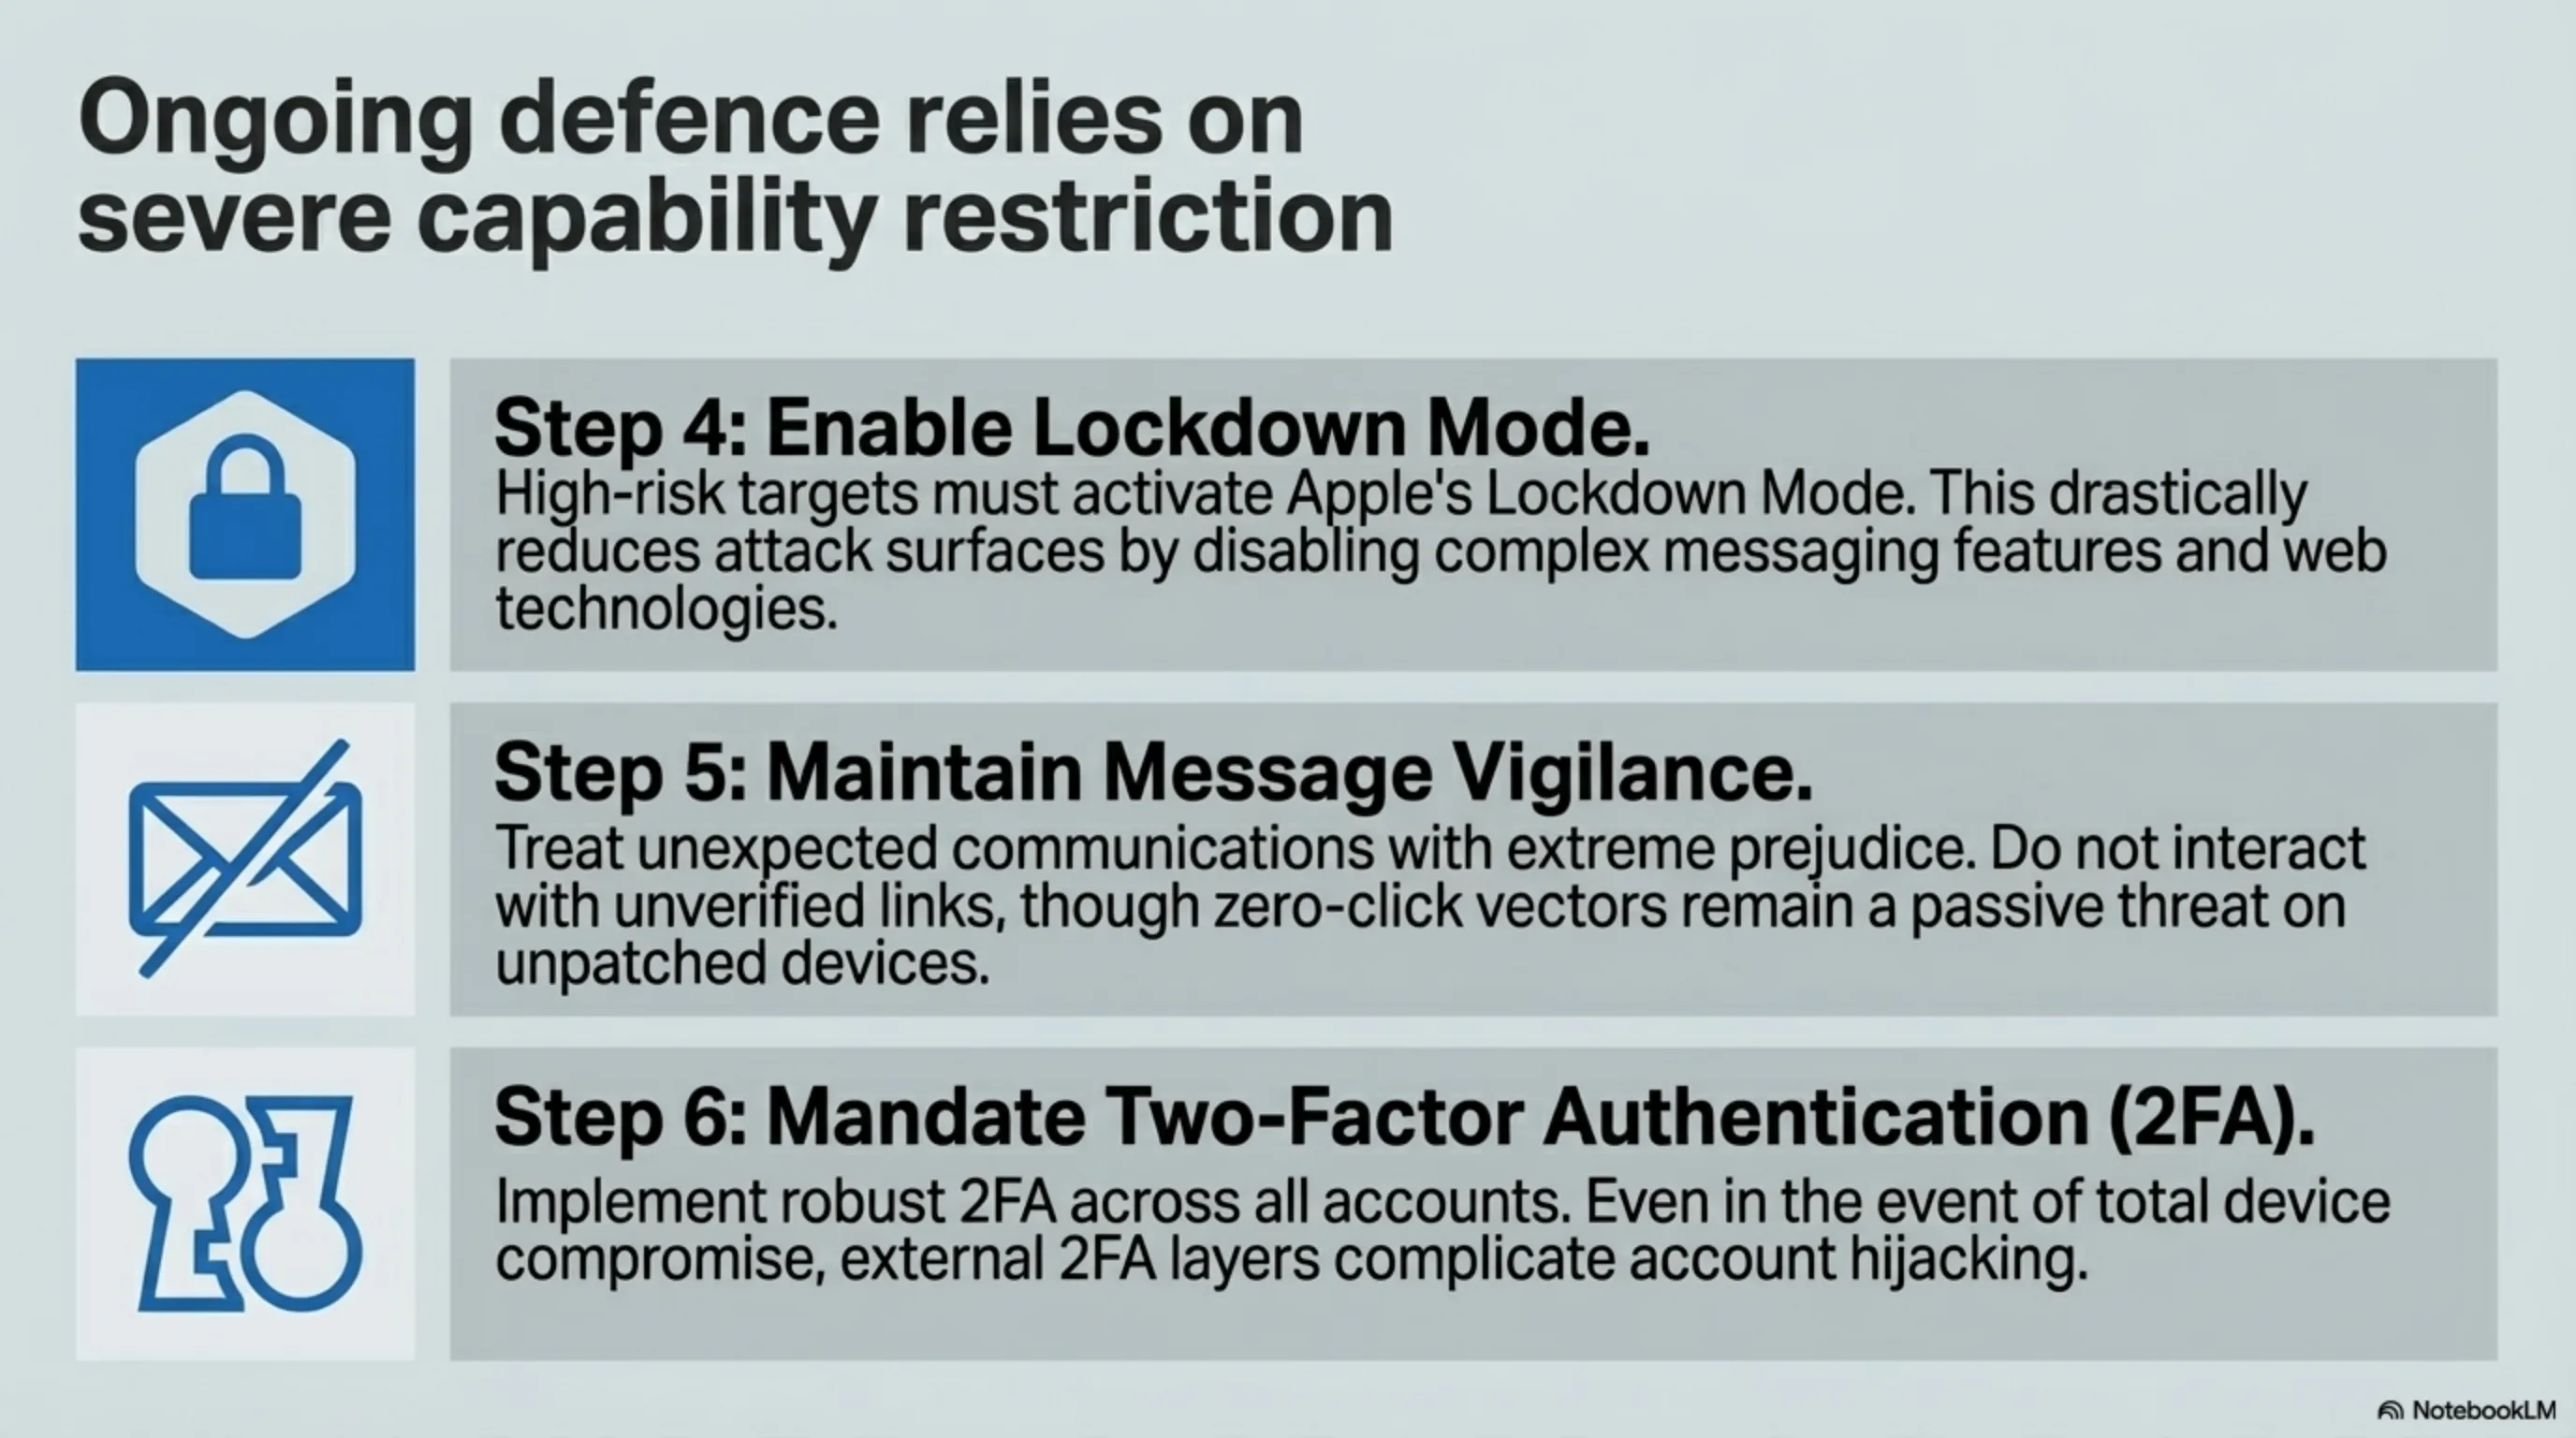
- Activate Lockdown Mode: If you hold a sensitive position (CEO, Journalist, Researcher), activate Apple's "Lockdown Mode" to heavily restrict vulnerable WebKit and iMessage protocols.
- If Infected; Complete Factory Reset: Understand that updating the OS only prevents new penetrations. If your device is already compromised, the only absolute cure is a Full Factory Reset, completely wiping all data. Do not restore from old backups, as they may harbor the dormant malware.
- Rapid 48-hour response by Apple's engineering team to patch 23 zero-day vulnerabilities upon Google's notification.
- Public exposure of the dangerous nature of state-sponsored cyber weapons, raising global awareness of Zero-Click attacks.
- Strengthening of defensive mechanisms like Lockdown Mode in iOS to combat military-grade malware.
- Catastrophic leak of 23 zero-day vulnerabilities from military contractor servers directly to Russian and Chinese state hackers.
- The silent, undetected infection of over 42,000 iPhones globally, facilitating 6-month wiretaps on senior political and corporate figures.
- Severe degradation of the Apple ecosystem's security reputation due to prolonged ignorance of these lethal vulnerabilities.
Final Editorial Verdict & Official Reference Sources
The End of the iOS Invincibility Myth
The Coruna dossier marks the end of the illusion of absolute security in the Apple ecosystem. When government-backed hacking tools leak to the black market, no user is safe without extreme proactive awareness.
Frequently Asked Questions & Vulnerability Analysis
What exactly is the Coruna exploit kit and who built it?
Coruna is an ultra-advanced cyber weapon containing 23 zero-day vulnerabilities. It was developed by a private US security contractor under a $45 million intelligence contract, which subsequently leaked to the black market.
How does an iPhone get infected without the user clicking any links?
Via a 'Zero-Click' attack utilizing the iMessage protocol. The attacker sends a manipulated packet that requires no user interaction. The message instantly crashes the processor in the background, elevating the malicious payload to root kernel access.
Which versions of iOS are vulnerable to the Coruna kit?
All iOS iterations spanning from iOS 13 up to iOS 17.2 are fully vulnerable. Only users who have updated their devices to iOS 17.4.1 or higher are immune to new penetrations.
Does updating the iOS remove the malware if already infected?
No. Updating to iOS 17.4.1 only seals the vulnerabilities preventing new attacks. If your device was already compromised, the malware remains active in the background. The only absolute cure is a Full Factory Reset without restoring from an infected backup.
How did Chinese state hackers acquire this US cyber weapon?
The source code was initially stolen by a contractor insider and sold to the Russian espionage group APT29. This Russian group subsequently sold the entire toolkit to the Chinese state-sponsored group 'Volt Typhoon' for $15 million in Bitcoin.
Additional Gallery: Tekin Analysis | Coruna Catastrophe: US iPhone Exploit Kit Leaked to Russian Spies & Chinese Hackers